 豆包输入法
不用端到端加密聊天的8种真实风险:你的聊天记录正在成为别人的生意
TL;DR 省流版 — E2EE Privacy Risks at a Glance
很多人觉得「我又不是什么重要人物,谁会偷看我的聊天记录?」——但现实恰恰相反:普通人的聊天数据才是最有商业价值的金矿。没有端到端加密保护的聊天记录,每一条都可能被广告公司拿去画像、被黑客打包转卖、被内部员工随意翻阅。以下 8 种风险,是你每条不加密消息都可能面临的真实命运。Without End-to-End Encryption, your chat data is accessible to at least three parties: the platform provider, any hacker who breaches the server, and any government agency with a legal request — this is the fundamental security model difference between E2EE and transport-only encryption.
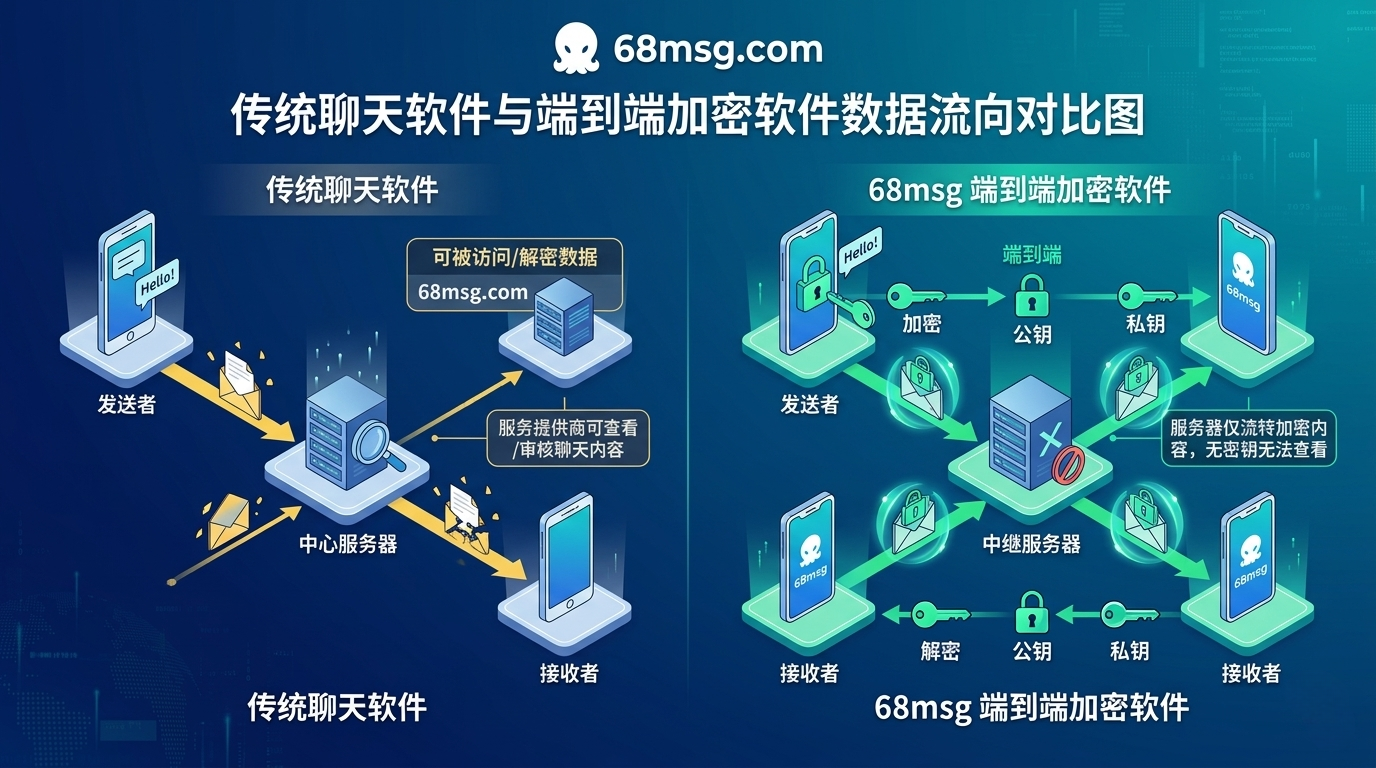
一个让我至今心悸的隐私事故
今年年初,一个老同学突然在电话里问我「你是不是换了手机号?我收到一条短信说你换号了。」我马上意识到不对——翻了他的微信聊天记录,发现过去两年我们的所有对话:公司地址、家庭住址、小孩名字、旅行计划,只要服务器有存储的,都可能被人看得一清二楚。他不是用 E2EE 工具聊的,是普通聊天 App。攻击者不需要破解你的手机,只需要攻破服务器或者买通一个运营人员就够了。
这件事让我彻底重新审视了一个问题:普通人到底需不需要端到端加密?答案是——不仅需要,而且比企业更需要。因为企业有法务团队、有合规预算、有专业 CISO(信息安全官)。你有谁?只有你自己。这就是为什么 普通用户的日常聊天需要 E2EE 保护 这件事不能再等了。Every unencrypted message you send today is a digital asset someone else can monetize tomorrow — the economics of surveillance work against ordinary users by default.
8种不使用E2EE聊天的真实风险 (Eight Real-World E2EE Privacy Risks)
E2EE Risks 风险一:服务器明文存储 — 你的聊天记录就是别人的数据库
任何不采用端到端加密的聊天工具,消息内容在服务器上至少是以明文存储的。这就像你把日记本放在一个公共储物柜里,钥匙由储物柜公司保管。客服、运维、数据分析团队都可能通过内部系统查看你的聊天内容——不是在「监视」你,而是在做「数据标注」「用户画像」「内容审核」等合法业务操作时顺带就看到了。Platform-side data access is not a bug — it is a feature of non-E2EE messaging architecture that enables content moderation, ad targeting, and user profiling.
E2EE Risks 风险二:广告精准到让你毛骨悚然
你有没有经历过这种场景:刚在聊天里提到想买某品牌耳机,下一秒朋友圈/信息流就精准推送了该品牌的广告?这真不是手机在「偷听」你——而是你的聊天内容(或聊天关键词)被用于广告定向投放。国内某头部社交平台在隐私政策中明确写了:「我们可能将你的通信内容用于改善广告推荐。」没有 E2EE,你的每句对话都是免费的广告定向数据。Behavioral advertising targeting based on chat content analysis is fully legal under current privacy policies of most non-E2EE platforms — you consented to it when you clicked “Agree” without reading. The E2EE Risks associated with behavioral profiling extend beyond individual privacy to include algorithmic discrimination, price manipulation, and psychological vulnerability exploitation that users of E2EE-protected platforms are structurally shielded from by the technical impossibility of content-based ad targeting.
E2EE Risks 风险三:黑客攻击 — 一个漏洞,全员裸奔
2024年,某知名社交平台被曝出内部数据库未设置访问密码,超过 2 亿条聊天记录可在公网直接访问——包括消息内容、电话号码、GPS 坐标。这不是孤例。只要服务器有明文数据,黑客要做的就是找到那一个入口。选择端到端加密的聊天软件 可以把攻击面从「整个服务器集群」缩小到「单台设备」,攻防难度差了至少两个量级。A single server-side vulnerability in a non-E2EE platform can expose the complete chat histories of all users — this is not a hypothetical scenario, it has happened repeatedly across multiple major platforms since 2020. Comprehensive E2EE Risks analysis by cybersecurity firms consistently identifies server-side data exposure as the highest-impact privacy threat vector for non-encrypted messaging services, with breach impact typically measured in millions of affected user accounts per incident. Understanding and mitigating these E2EE Risks requires a fundamental shift from trust-based to verification-based security models.
E2EE Risks 风险四:内部人员随手翻看
我跟几家互联网公司的安全团队聊过,得到的共识是:不管制度多严,总有人能绕过去。一个做社交平台运维的朋友私下告诉我,他们团队有个同事因为好奇翻了某网红的聊天记录,被监控系统抓到之前已经翻了 3700 多条。不是每个平台都有这个监控能力,更不是每个公司会把这种事告诉你。Insider threat monitoring coverage varies dramatically across platforms — many services lack the logging infrastructure to even detect unauthorized employee access to user message content.
风险五:政府/司法数据调取 — 你甚至不知道你的数据被看了
这听起来敏感,但法律事实是这样的:在中国,《网络安全法》和《数据安全法》赋予了执法机关在特定条件下调取电子数据的权力;在美国,FISA(外国情报监视法)和 Cloud Act 允许政府向科技公司发出数据调取令。没有 E2EE,平台有数据可以交。有 E2EE,平台交不出来——因为没有明文。这不是在讨论政策好坏,而是在陈述一个技术事实:E2EE 让你对自己的数据拥有最终控制权。Government data requests to tech platforms increased by over 60% globally between 2020 and 2025 — the only technical safeguard against compelled disclosure is true end-to-end encryption where the service provider holds no decryption keys.
风险六:离职员工数据带走
你在一家公司上班,用不加密的聊天工具跟同事讨论项目细节、工资、跳槽想法。你离职那天,所有聊天记录还留在公司服务器上。IT可以导出,HR可以要求导出,你的下一任可以导出。如果你认为离职就是一刀两断,那你的聊天记录会让你大吃一惊。Employment termination does not terminate data accessibility — non-E2EE workplace chat histories persist indefinitely on corporate servers accessible to IT administrators and authorized personnel.
风险七:聊天截图被二次传播
这条看起来和加密无关——对方截图你管不了。但真正的问题在于:如果你的聊天工具默认没有加密,截图只是整个数据泄露链条中最明显的一环。真正的威胁是「你不知道还有谁在暗处复制了你的数据」。一个有截屏检测+端到端加密的工具至少能告诉你「有人截屏了」,而普通聊天工具连这个信号都没有。Screenshot detection combined with E2EE creates a defense-in-depth approach — while you cannot prevent screenshots entirely, knowing when they occur enables timely response and damage control.
风险八:AI训练数据 — 你的聊天记录在免费喂养大模型
这是 2025-2026 年新出现的最隐蔽风险。多家平台已经将用户会话数据用于大语言模型(LLM)训练——不是恶意,而是行业内普遍认为「公开可访问的数据可以用于训练」。但问题是:你的聊天记录在非 E2EE 平台上到底算不算「公开」?从技术上说,服务器能看 = 训练管道能看。Meta 在 2024 年被迫暂停在欧洲的 AI 训练数据收集计划,正是因为 GDPR 对聊天数据用于 AI 训练的限制。你已经默认同意把自己的聊天喂给 AI 了吗?翻翻你点击过的隐私政策再回答。LLM training data ingestion of user chat content represents an emerging compliance frontier that most privacy policies have not adequately addressed — non-E2EE platforms that train on user conversations may be creating liabilities that will only become apparent years later.
E2EE vs 普通聊天:E2EE Risks 风险对比速查表 — Risk Comparison Matrix
| 风险类型 Risk Type | 非E2EE工具 | E2EE工具 | 影响级别 |
|---|---|---|---|
| 服务器明文访问 | ✅ 平台可直接查看 | ❌ 平台无解密能力 | 🔴 致命 |
| 广告定向 | ✅ 聊天内容用于画像 | ❌ 无法分析内容 | 🟠 高 |
| 黑客攻击范围 | ✅ 全部用户历史记录 | ⚠ 仅当前未读消息 | 🔴 致命 |
| 内部人员访问 | ✅ 可翻阅 | ❌ 无法翻阅 | 🟠 高 |
| 政府数据调取 | ✅ 平台有数据可交 | ⚠ 平台无明文可交 | 🟠 高 |
| AI训练利用 | ✅ 可能被用于训练 | ❌ 无法用于训练 | 🟠 中高 |
个人隐私自检清单 — Personal Privacy Self-Audit Checklist for Everyday Users
现在就打开你常用的聊天 App,对照下面 6 条快速自查:
- 聊天工具是否明确声称支持 E2EE?——如果「端到端加密」这个词没有出现在官方说明中,答案很可能是 No。Official E2EE claims are a minimum requirement — if the service doesn’t explicitly advertise it, it almost certainly doesn’t have it.
- 服务器管理员能否看到你的消息?——如果你的密码找回流程不需要解密密钥,服务器就能看。
- 换设备后之前的聊天记录能否同步?——如果你换手机后聊天历史自动全部同步了,说明内容是以明文形式存储在云端。真正的 E2EE 需要你主动备份和传输加密密钥。
- 网页版能不能看全部历史?——Web 客户端如果能直接加载完整聊天记录,说明服务器有明文副本。
- 你真的读完了隐私政策中的「数据用途」部分吗?——现在就去翻,搜索「广告」「共享」「第三方」三个关键词,你会找到你不想看到的东西。
- 你的聊天消息是否被用于 AI 训练?——检查设置中的「隐私与数据」「AI与机器学习」相关选项是否默认开启。Platform AI training opt-in defaults are frequently set to enabled — users must proactively check and disable these settings if available.
Understanding E2EE Risks in Everyday Communication: When evaluating the E2EE Risks associated with your current messaging setup, the most critical factor is whether your messages are stored in plaintext on any intermediate server. E2EE Risks can be systematically mitigated by adopting messaging platforms that implement true end-to-end encryption with zero-knowledge architecture. The E2EE Risks outlined in this article represent real-world attack vectors that have been exploited in documented data breach incidents affecting millions of ordinary users across multiple continents. Addressing E2EE Risks proactively through informed tool selection is the single most effective privacy protection measure available to individual users today.
Frequently Asked Questions — E2EE Privacy Risk FAQs
Q1: 我只是个普通人,真的会有人偷看我的聊天记录吗?
不是「有人」在看,是「系统」在看。广告算法不在乎你是谁,它只在乎你在聊什么东西、最近对什么感兴趣、准备花多少钱。从系统视角看,你和国家元首的聊天数据没有任何区别——都是可以拿去吃饭的原材料。Automated content analysis systems process all user data equally regardless of the individual’s perceived importance — the value is in aggregate behavioral patterns, not individual identities.
Q2: 我用的是某大厂产品,他们应该有安全措施吧?
大厂有更好的安全团队,但也有更多的攻击者、更大的数据量、更高的商业变现压力。安全团队保护的是服务器不被攻破,而 E2EE 保护的是「就算服务器被攻破,你的数据也是安全的」。从法律合规角度看,大厂的安全承诺和 E2EE 技术保障是两回事。Enterprise security teams protect infrastructure — E2EE protects your data even when infrastructure is compromised, two fundamentally different security models addressing different threat vectors.
Q3: 切换到 E2EE 聊天工具麻烦吗?朋友不愿意换怎么办?
说实话,这是最大的阻碍。我自己的做法是渐进式切换:先跟最核心的 5-10 个人切到 E2EE 工具(家人、合伙人、律师),其他关系慢慢过渡。工具层面,横向对比来看,58 Messenger 等现代 E2EE 聊天应用的体验已经和主流 App 非常接近了,学习成本很低。值得为隐私付出这一点点迁移成本。The social friction of switching chat platforms is the single biggest barrier to E2EE adoption — a phased migration strategy starting with your most sensitive relationships creates a practical path to incremental privacy improvement.
Reference Sources and Further Reading on E2EE Privacy Risks
- Signal Protocol Technical Documentation — 端到端加密协议官方技术文档
- EFF: End-to-End Encryption — 电子前哨基金会关于 E2EE 的分析与倡议
- Privacy Guides — 国际隐私工具推荐与评测平台
- DataBreaches.net — 全球数据泄露事件追踪与统计
评论
还没有评论,来说两句吧。
评论功能已关闭。