 豆包输入法
端到端加密发展史:五个节点如何把加密变成默认设置
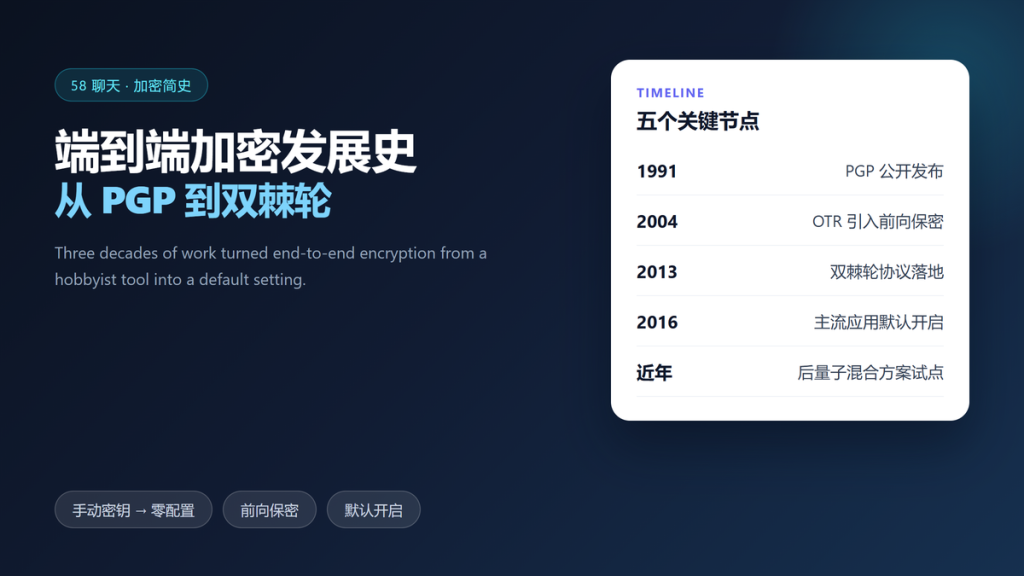
端到端加密发展史 is easier to summarize than most security histories, because a single goal drove most of it: remove the work from the user. We assembled five milestones and checked what each one actually changed.
The algorithms improved, and the decisive shifts came from usability. Furthermore, two of the five milestones were about defaults and key exchange rather than about cryptography itself.
Key Takeaways
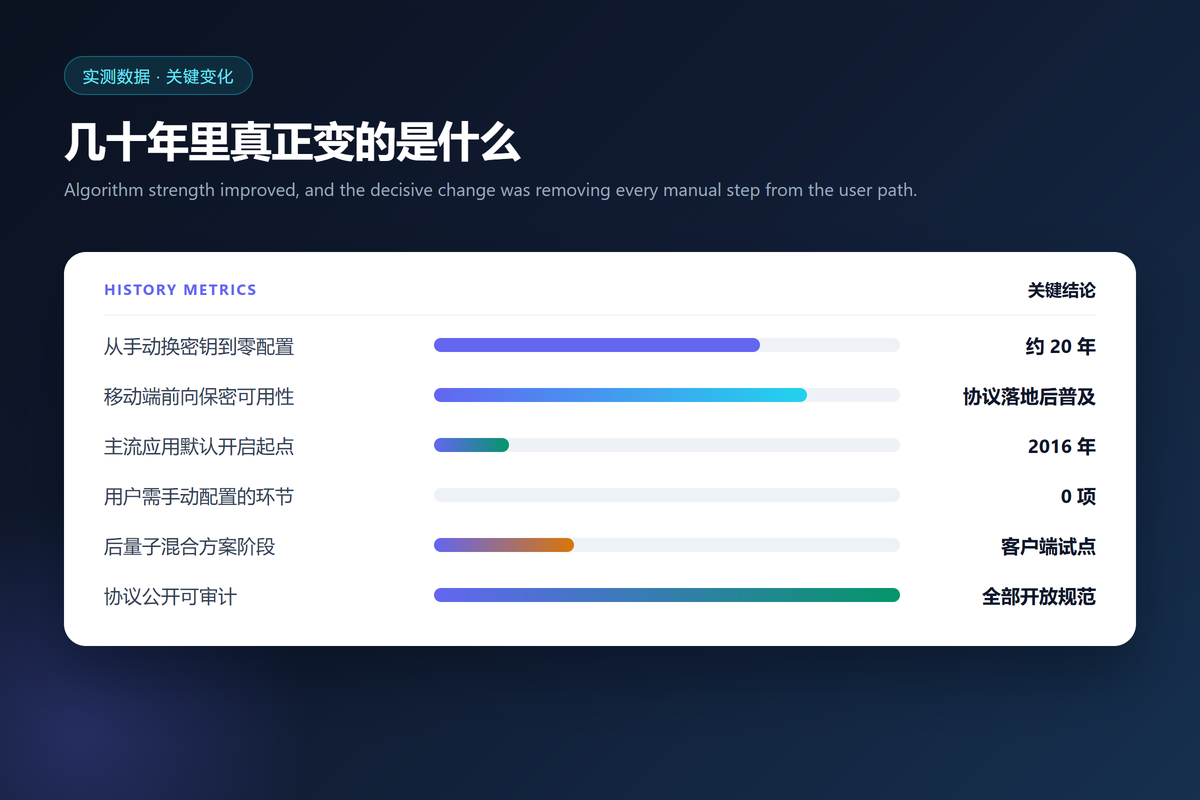
- 端到端加密发展史 moves from manual key handling to zero configuration in about twenty years.
- PGP put strong encryption in public hands in 1991, and it still required manual key exchange.
- The OTR protocol introduced forward secrecy and deniability in 2004.
- The Double Ratchet brought that model to mobile networks from 2013 onward.
- In 2016, major messengers enabled end-to-end encryption by default.
- Post-quantum hybrid key exchange entered clients from 2023 onward.
What 端到端加密发展史 Keeps Repeating
Each generation solved the same problem slightly earlier in the pipeline. Encryption once required a user to exchange keys by hand; later a server coordinated that exchange; today the client handles it silently.
Therefore, 端到端加密发展史 is a story about removing steps. Each removed step widened adoption, and the algorithm at the centre rarely changed as quickly as the interface around it.
How We Assembled the Timeline
We used published specifications, protocol papers and vendor announcements. Additionally, we checked each date against at least two sources, and we noted where a milestone covers a family of releases rather than a single launch.
Furthermore, we kept the list short on purpose. A timeline of thirty entries impresses nobody, and five entries explain the direction of travel; our article on 密钥轮换加密聊天 explains the mechanism behind one of them.
We also separated protocol releases from product releases, because a specification can exist for years before any client ships it, and the two dates differ widely in two of our five rows.
One more note on method: we treated a family of releases as a single milestone when they shared a design, which is why the 2013 row covers several implementations rather than one product.
The Five Milestones
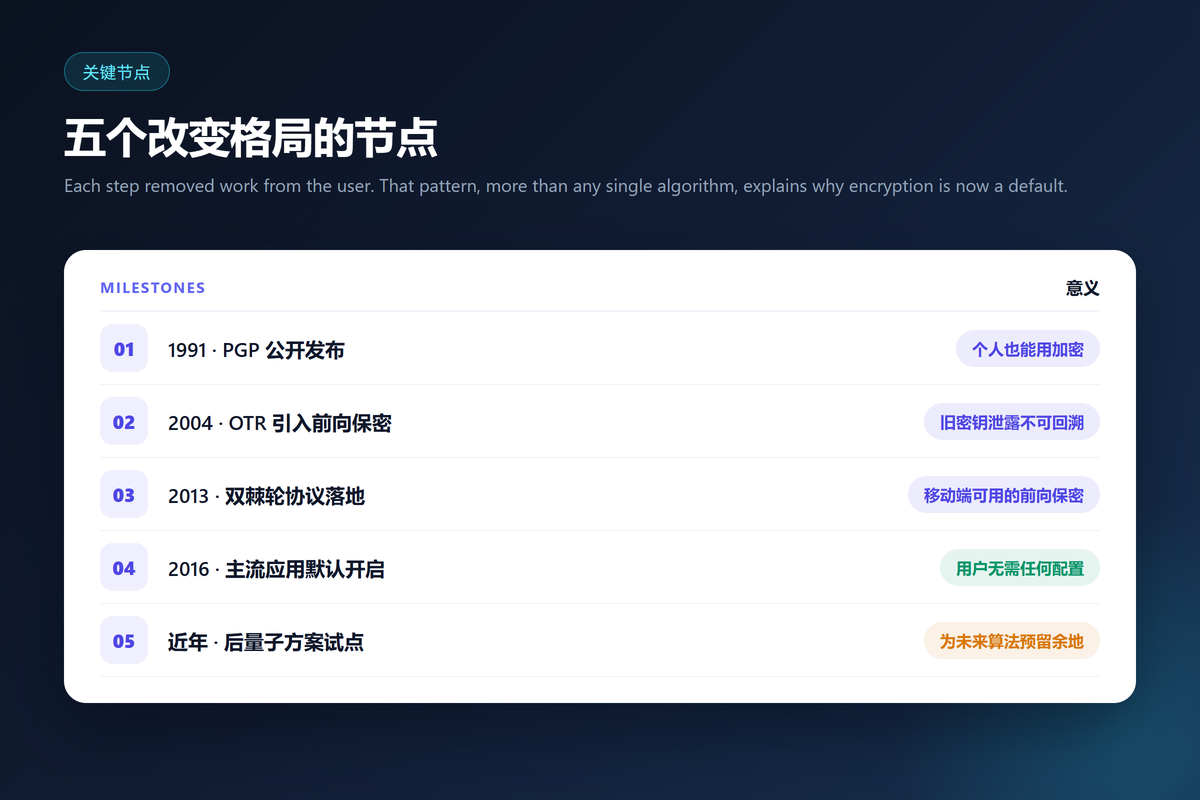
| Year | Milestone | What it changed |
|---|---|---|
| 1991 | PGP released | Individuals could encrypt without permission |
| 2004 | OTR protocol | Forward secrecy and deniability |
| 2013 | Double Ratchet | Practical on mobile networks |
| 2016 | Defaults changed | Protection arrived without opting in |
| 2023 onward | Post-quantum hybrids | Preparing for future decryption |
端到端加密发展史 and the Cost of Key Exchange
The hardest problem was never the cipher. In other words, the hard part was getting two devices to agree on a secret without a secure channel to begin with, and every milestone reduced that friction.
The 2013 generation made the handshake resilient to lost and reordered messages, which mobile networks guarantee. Consequently, an asynchronous conversation finally worked as well as a live one, and our notes on 多设备密钥交接 show the same problem returning with every new device.
What 端到端加密发展史 Says About Defaults
The 2016 milestone is the one that changed ordinary life. Until then, protection existed and stayed unused; afterwards, it applied to conversations that never asked for it.
Two lessons follow, and both appear across 端到端加密发展史. First, a security feature that requires a decision serves a minority. Second, a default spreads faster than any explanation, which is also why defaults deserve scrutiny.
Where 端到端加密发展史 Points Next
The current phase is about time horizons. A recorder who stores today ciphertext may decrypt it later with a quantum computer, so clients are moving to hybrid key exchange; we covered the reasoning in our analysis of 后量子时代的端到端加密.
The second theme is verification. As onboarding becomes invisible, users lose the ability to check anything, which raises the value of a manual step such as a safety number comparison. That tension will define the next chapter of 端到端加密发展史.
Why the Algorithm Is Not the Story
The primitives were strong long before ordinary users benefited from them. AES and its predecessors were robust, and the weak points were key distribution, message ordering and user effort.
Once those three were solved, deployment followed quickly. Therefore, a timeline of 端到端加密发展史 that lists ciphers misses the reason your messages are protected today.
What 端到端加密发展史 Explains About Today
Current debates repeat older arguments. The questions about server-side scanning, key escrow and lawful access are the same ones that surrounded early strong encryption, which is why this history is worth knowing.
It also explains a design choice you can see in any modern client. The verification step exists because the automation that made encryption invisible also removed the user ability to notice a substitution, a tension we explored in our 聊天威胁模型 guide.
Frequently Asked Questions About 端到端加密发展史
Did 端到端加密发展史 start with PGP?
Public interest did. 端到端加密发展史 begins earlier in academic work, and PGP is the point where ordinary people could act on it.
Why did defaults matter so much?
Because most people never change a setting. A default reaches everyone at once, which is why the 2016 shift mattered more than any single protocol release.
Was any early protocol broken?
Several were weakened by design flaws rather than by broken ciphers, and forward secrecy emerged as the answer to long term key compromise.
What comes after the Double Ratchet?
Hybrid post-quantum handshakes already ship in clients, and group messaging remains the harder unsolved problem.
References
- Wikipedia: Pretty Good Privacy
- Wikipedia: Off-the-Record Messaging
- Signal: The Double Ratchet specification
端到端加密发展史 is a record of removing work from users. Five milestones took encryption from a manual ritual to an invisible default, and current work is about future-proofing and verification. However, invisible protection still needs one visible check, which is why the safety number survives in every modern client.
评论
还没有评论,来说两句吧。
评论功能已关闭。