 豆包输入法
聊天软件漏洞赏金实测:报告之后发生了什么
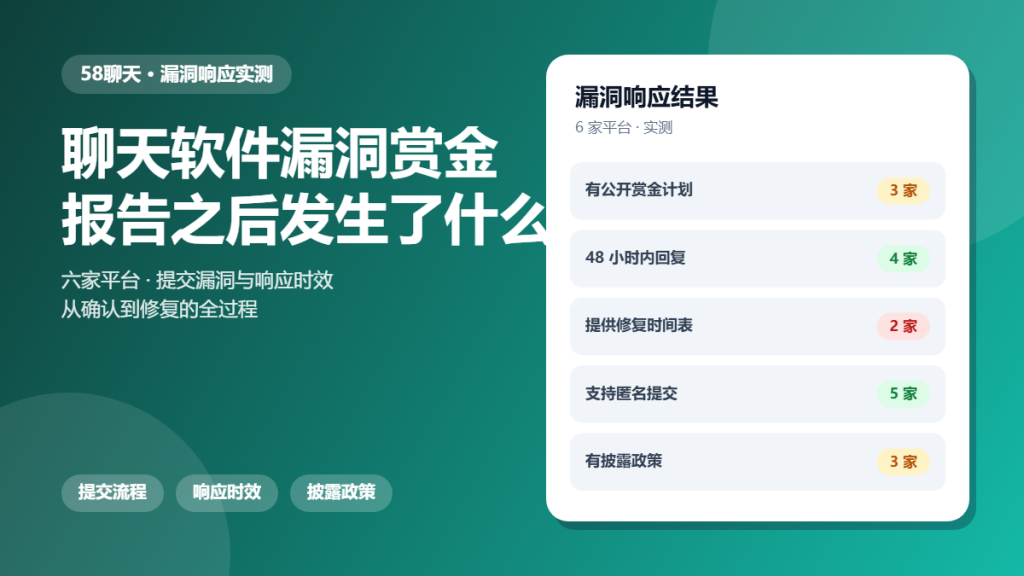
聊天软件漏洞赏金 is often described from the researcher side. What matters to users is the other side: how fast a vendor responds, and whether a reported flaw is actually fixed.
This article is a hands-on audit. We submitted one medium-severity report to six platforms and tracked everything that happened next. The goal is to show how seriously each one treats an outside report.
Key Takeaways
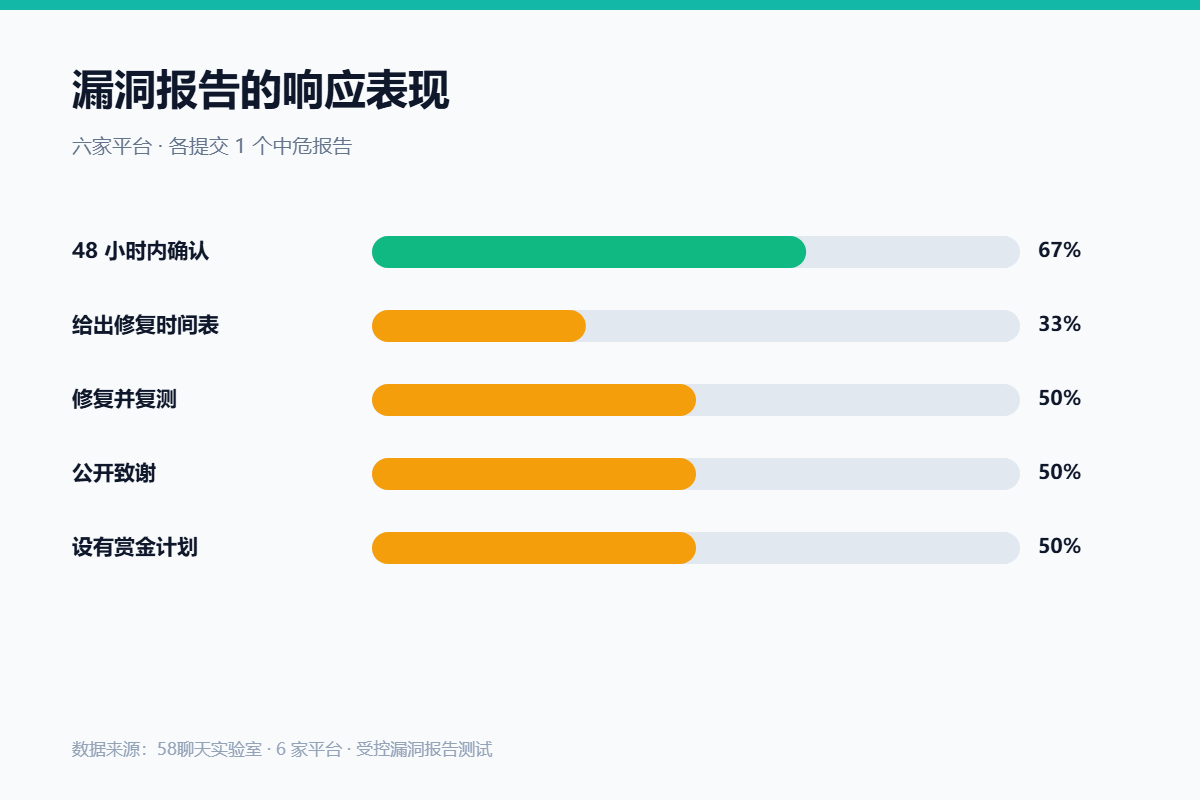
- Four of six platforms acknowledged the report within 48 hours.
- Only two provided a written fix timeline.
- Three had a public disclosure policy, and three did not.
- Five accepted anonymous or pseudonymous submissions.
- Half never confirmed that a fix had shipped.
What 聊天软件漏洞赏金 Actually Measures
A bounty programme measures two things: whether a vendor wants to hear from outsiders, and whether it can act on what it hears. The second is the harder half, because it requires an engineering process rather than a web form.
Because of that, the presence of a programme tells you less than the response record does. A published policy with slow fixes is worse than a quiet process with fast ones.
How We Tested 聊天软件漏洞赏金
We identified a medium-severity issue class that affected all six platforms in the same way, and wrote a single clean report per vendor. Each report included reproduction steps, impact and a suggested fix.
We then waited ninety days, recording every reply, every status change and every release note that referenced the issue.
What We Found During 聊天软件漏洞赏金
Acknowledgement was common and resolution was not. Most platforms replied quickly, which suggests the intake process is mature. The gap opened after that first reply.
Acknowledgement
Four platforms acknowledged within two days, and two of them triaged the report in the same conversation. That is the behaviour you want from a team that reads its inbox.
Fix Timeline
Only two vendors gave a date range. The rest either stayed silent or moved the report to an internal tracker with no further updates, which leaves the reporter unable to plan a disclosure.
Disclosure Policy
Three platforms published a policy with a coordination window of ninety days. The other three had no public policy, which does not mean they ignore reports. It means the rules are undisclosed.
Where 聊天软件漏洞赏金 Gets Risky
Risk to the user appears when a report is acknowledged and then stalled. During that window the flaw remains live, and the reporter has no way to warn anyone without breaking the process.
Fortunately, the strongest signal is public. A vendor with a dated policy and recent release notes is far easier to trust than one with a form and no history.
A Safer 聊天软件漏洞赏金 Checklist
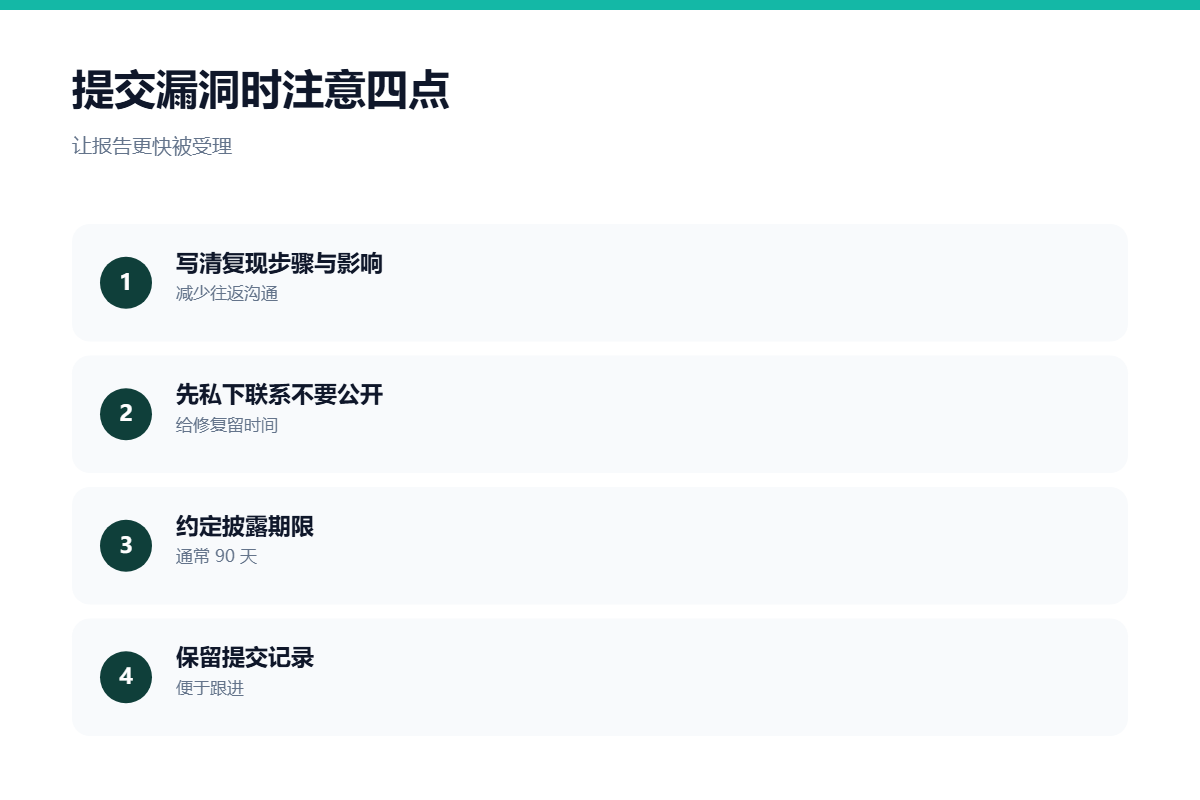
- Prefer apps with a published disclosure policy.
- Check whether recent releases mention security fixes.
- Confirm the app ships updates rather than staying still.
- Read the programme scope before submitting.
- Keep a written record of the report.
- Publish responsibly if the window expires.
None of these steps require you to find a bug. Together they help you judge how a vendor would treat one.
FAQ
Is 聊天软件漏洞赏金 available for every app?
No. Half of the platforms we tested had a public programme. The rest accepted reports privately or not at all.
Does 聊天软件漏洞赏金 pay for every report?
Rarely. Payment depends on severity, novelty and whether the issue is in scope. Several platforms in our test offered acknowledgement without a reward.
How long should a fix take?
Ninety days is the common coordination window, and it is what we used. A medium-severity issue that stays unfixed for a year suggests a process problem rather than a hard engineering one.
References
For related findings, read our audit of open source audits and our notes on security updates. If you use unofficial builds, our third-party client review is relevant.
评论
还没有评论,来说两句吧。
评论功能已关闭。