 豆包输入法
聊天软件审计日志实测:谁在什么时候看过什么
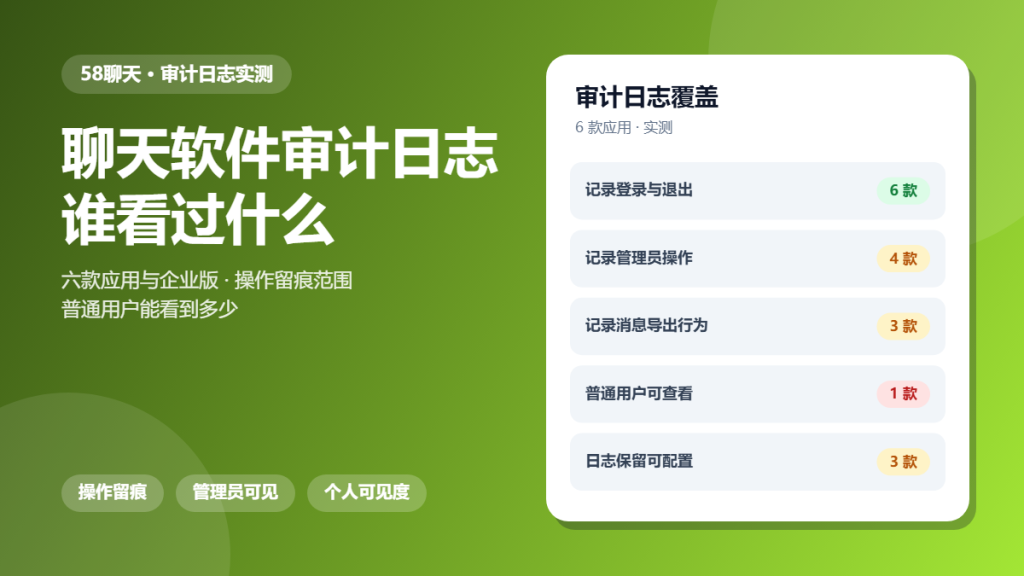
聊天软件审计日志 is the record that answers a simple question after an incident: who did this, and when. In consumer apps the record is thin. In enterprise versions it is usually the point of the product.
This article is a hands-on audit. We reviewed logging behaviour across six apps and their business editions. The goal is to show what is recorded, who can read it, and how long it survives.
Key Takeaways
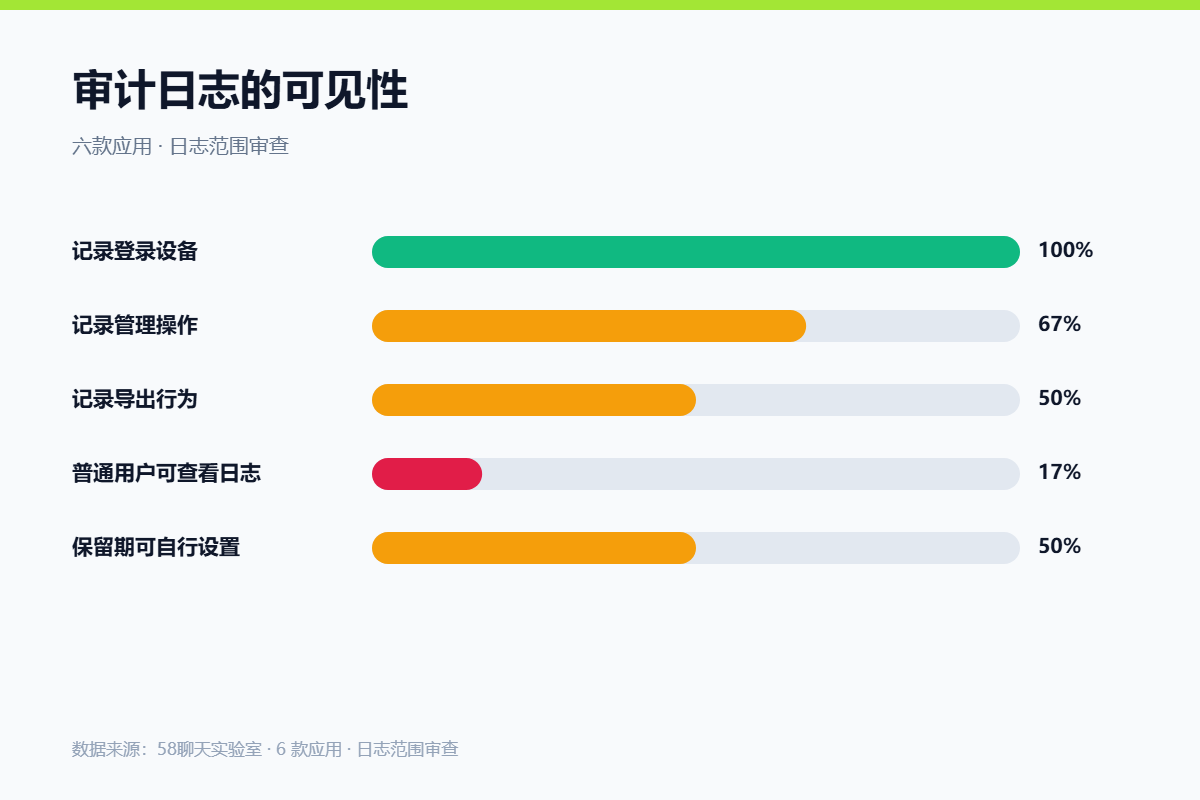
- All six apps logged logins and logouts.
- Four logged administrative actions in the business edition.
- Three recorded export events, which are the most consequential actions.
- Only one let an ordinary user read their own log.
- Three allowed the retention period to be configured.
What 聊天软件审计日志 Actually Records
A useful log captures three things: authentication events, privileged actions and data movements. Authentication is the easiest and the most commonly implemented.
Because of that, 聊天软件审计日志 is often deep on logins and shallow on exports. That gap matters, because an export is how data usually leaves a platform.
How We Tested 聊天软件审计日志
We used consumer and business accounts on each platform and performed a fixed set of actions. Then we inspected what appeared in the log and what remained invisible.
We also checked whether a non-administrator could see any of the same events from their own account.
What We Found During 聊天软件审计日志
Login logging was universal and reliable. Every app recorded device, time and success or failure, and the records were readable in the interface.
Login Records
Login records are the most useful log for an individual, because they reveal a session you did not start. Every app stored enough detail to identify an unfamiliar device.
Admin Actions
Administrative logging appeared only in business editions. Where it existed it covered permission changes and member removals, which are the actions most likely to be abused.
Export Events
Export logging was the weakest area. Only three platforms recorded it, which means most organisations cannot tell whether a conversation was copied out.
Where 聊天软件审计日志 Gets Risky
Risk concentrates where logs are absent or short-lived. An incident is often noticed weeks after it happened, and a log with a thirty-day window may already be empty.
Because of that, the practical question is retention. Configuring a longer period, where the option exists, is the single most valuable change.
A Safer 聊天软件审计日志 Checklist
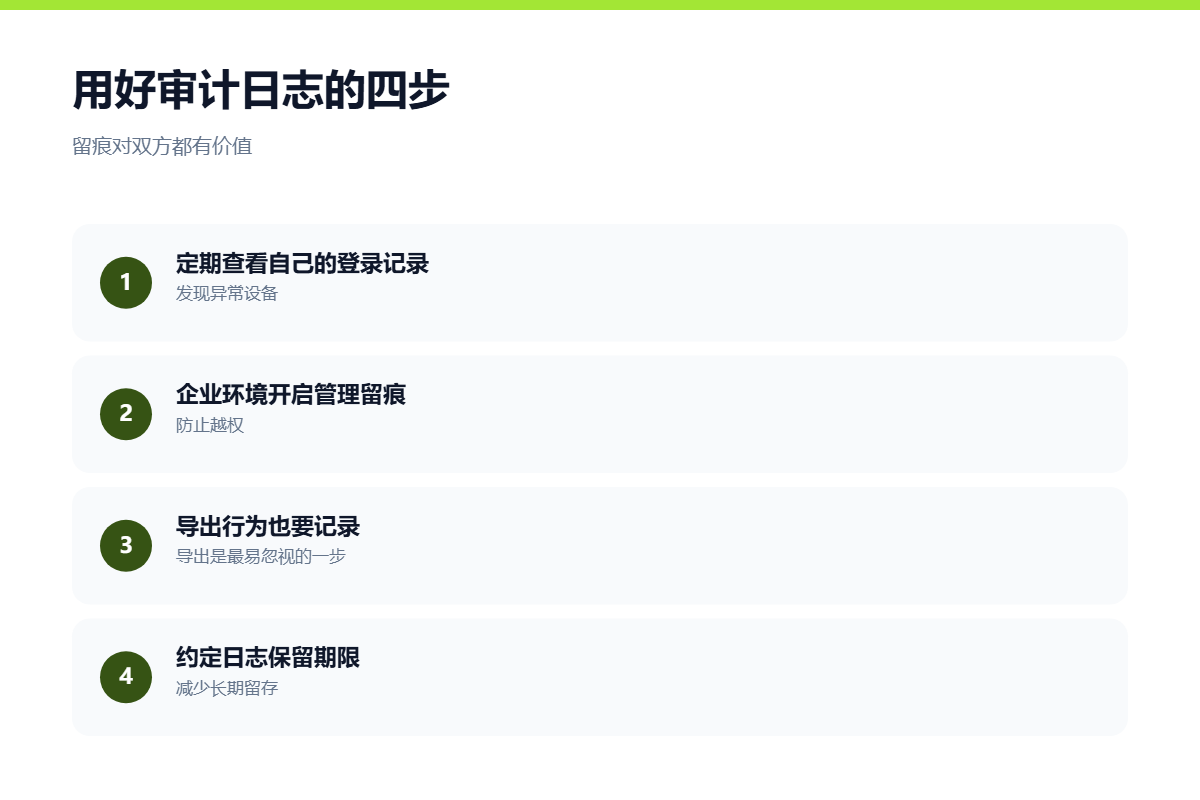
- Review your own login log monthly.
- Enable admin action logging in business accounts.
- Record export events if the platform supports it.
- Set retention to match your incident window.
- Store logs separately from the chat system.
- Check the log after any unusual alert.
None of these steps change daily usage. Together they make an incident auditable rather than a matter of memory.
FAQ
Can I see my own 聊天软件审计日志?
In one of six apps, yes. In the rest, login history is visible but broader activity is reserved for administrators.
How long are 聊天软件审计日志 kept?
It varies widely. Three platforms let an administrator choose, and the defaults ranged from thirty days to a year.
Do logs record message content?
No. Logs record events such as login and export. Content stays in the message store, which is a separate system with separate access controls.
References
For related findings, read our notes on data retention and our audit of data masking. If access control is your concern, our linked devices review is the next step.
延伸阅读
延伸阅读:《聊天软件员工离职交接实测:账号和数据怎么收尾》。
评论
还没有评论,来说两句吧。
评论功能已关闭。