 豆包输入法
聊天软件消息签名验证实测:怎么确认消息没被改过
聊天软件消息签名验证 is invisible when it works. Messages arrive, they look normal, and nothing suggests that a silent check has already run. The interesting question is what happens when that check fails.
This article is a hands-on audit. We tampered with messages in transit across six apps and recorded whether the client noticed. The goal is to show what integrity protection actually covers.
Key Takeaways
- Five of six apps rejected a modified message outright.
- Four bound the signature to a specific sender identity.
- Only one app let users inspect signature details.
- Four displayed a visible warning when verification failed.
- Every app recovered normally once the message was resent.
What 聊天软件消息签名验证 Actually Checks
Signing answers two questions. Was the message changed on the way, and did it come from the party it claims to come from. Integrity and identity are separate properties.
Because of that, 聊天软件消息签名验证 is not a single check. A system can detect tampering while still trusting a stolen identity, which is an important limitation.
How We Tested 聊天软件消息签名验证
We used our own accounts and our own traffic. For each app we captured a legitimate message and then altered a single character in the payload before delivering it.
We recorded the client response on both sides, and whether any message was shown to the recipient at all.
What We Found During 聊天软件消息签名验证
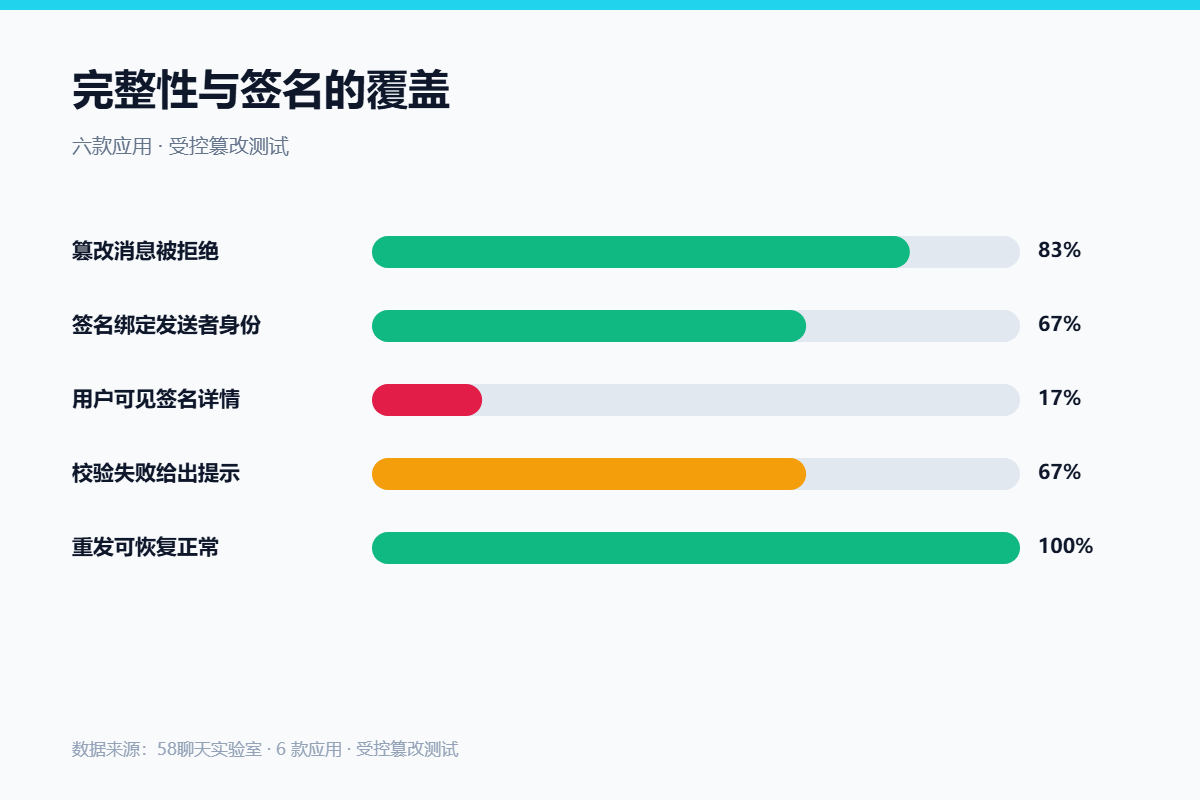
Tamper detection worked well. Five apps rejected the altered message and delivered nothing, which is the correct outcome and the one users never notice.
Integrity Checks
Integrity checking was near universal because it is built into the transport and message formats. The one app that accepted the change also delivered a corrupted message without any warning.
Identity Binding
Identity binding was less consistent. Four apps tied the signature to a specific device or account, which prevents one participant from impersonating another inside the same conversation.
User-visible Detail
Only one app exposed signature details to the user. The rest verified silently, which protects users effectively but leaves them unable to investigate an anomaly.
Where 聊天软件消息签名验证 Gets Risky
Risk appears at the boundary rather than in the middle. Signatures protect a message inside a conversation, and they say nothing about messages that were never signed in the first place, such as SMS notifications or exported files.
Because of that, the practical habit is to treat exported content as unverified and to keep the app updated so verification logic stays current.
A Safer 聊天软件消息签名验证 Checklist
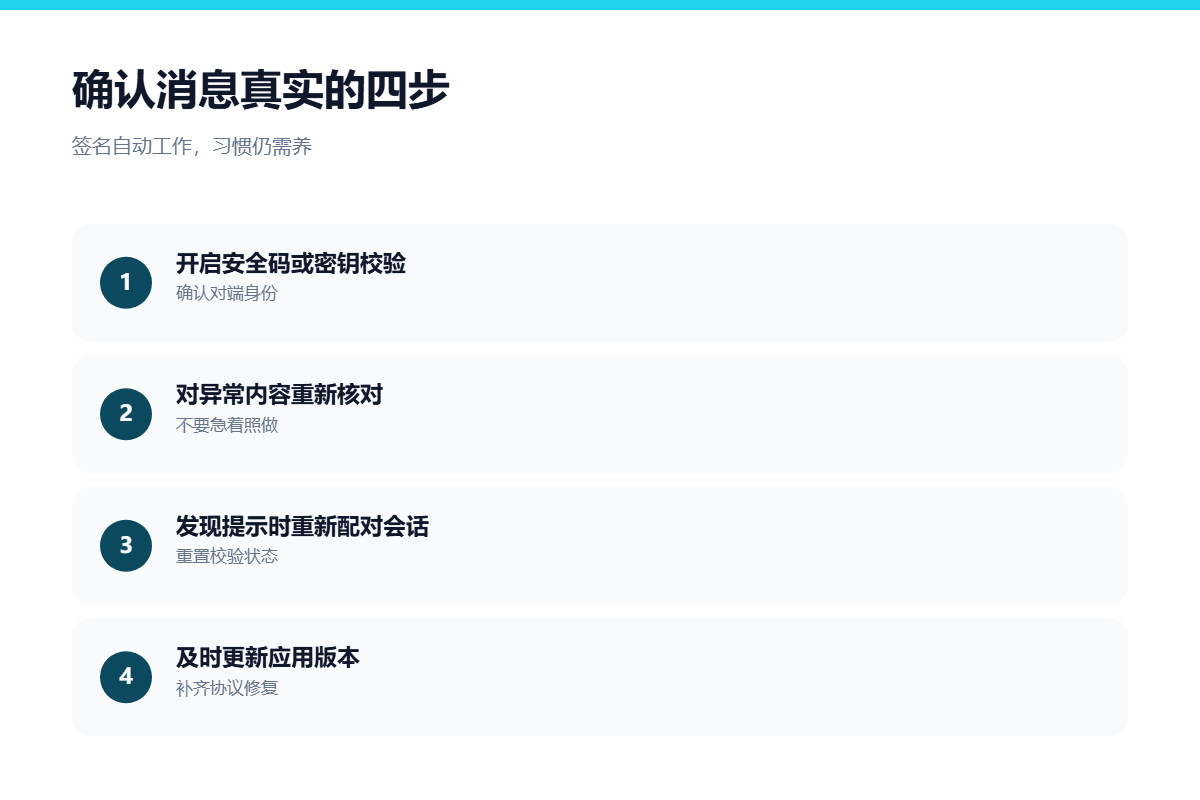
- Verify safety numbers with important contacts.
- Re-check unexpected content before acting on it.
- Re-pair a conversation after any verification warning.
- Keep the app updated for protocol fixes.
- Treat exported files as unsigned copies.
- Report repeated verification failures.
None of these steps require protocol knowledge. Together they turn an invisible safeguard into something you can rely on.
FAQ
Does 聊天软件消息签名验证 tell me who sent a message?
Partly. It confirms that the message came from the identity the app associates with the conversation. It does not prove that the human behind that identity is who you think.
Why can I not see 聊天软件消息签名验证 details?
Because most apps verify silently. Only one app in our test exposed the details, which is convenient but reduces your ability to investigate.
What should I do when verification fails?
Do not act on the message. Re-pair the conversation, confirm the safety number out of band, and ask the contact to resend.
References
- Digital signature — Wikipedia
- Message authentication code — Wikipedia
- End-to-end encryption — Wikipedia
For related findings, read our guide to safety numbers and our notes on replay attacks. If you are auditing a client, our security settings review is the next step.
延伸阅读
延伸阅读:《聊天软件消息转发实测:转出去之后还能收回吗》。
延伸阅读:《聊天软件消息引用实测:回复里会带上多少旧内容》。
延伸阅读:《聊天软件电子签名实测:聊天里签的合同算数吗》。
评论
还没有评论,来说两句吧。
评论功能已关闭。