 豆包输入法
聊天软件小程序隐私实测:小程序能拿到多少聊天数据
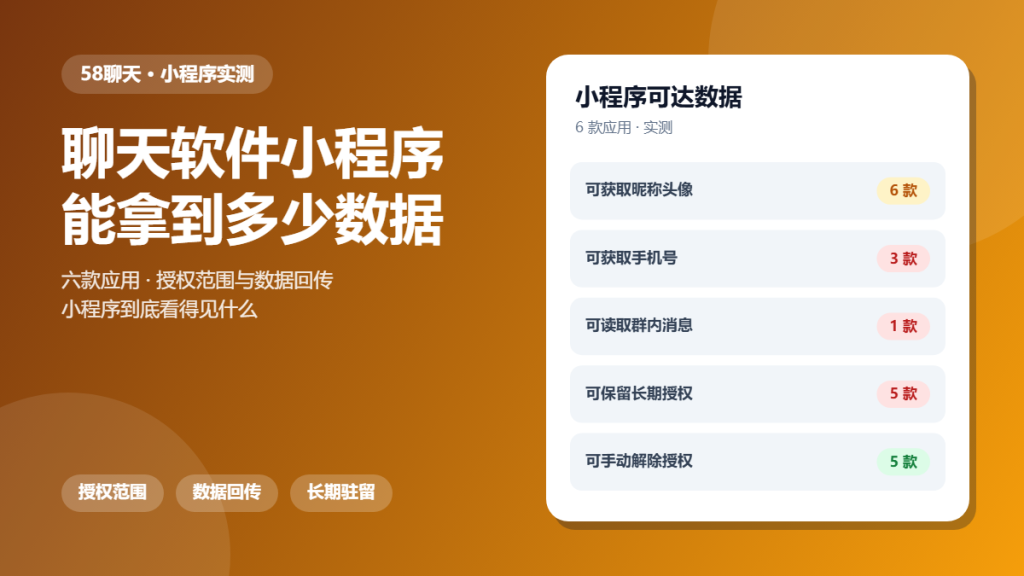
聊天软件小程序隐私 sits in a gap. A mini app is not quite a website and not quite an installed app, and its access rules are rarely explained in either place.
This article is a hands-on audit. We opened mini apps inside six chat clients and recorded what they requested and received. The goal is to show what an in-chat app can reach.
Key Takeaways
- All six mini apps requested a profile and an avatar.
- Three requested a phone number to function.
- One could read messages in the group where it was opened.
- Five retained the authorisation for a long period.
- Five allowed the authorisation to be revoked manually.
What 聊天软件小程序隐私 Actually Covers
A mini app runs inside the chat client and inherits a limited version of its context. It usually receives an identity, and in some platforms it can also read the conversation it was launched from.
Because of that, 聊天软件小程序隐私 depends on the platform rules as much as on the mini app itself. Two otherwise identical apps can receive very different data.
How We Tested 聊天软件小程序隐私
We opened a controlled mini app in each client, both from a personal chat and from a group. We recorded the consent screen, the data returned and what the app could read afterwards.
We then revoked the authorisation and checked whether access actually stopped.
What We Found During 聊天软件小程序隐私
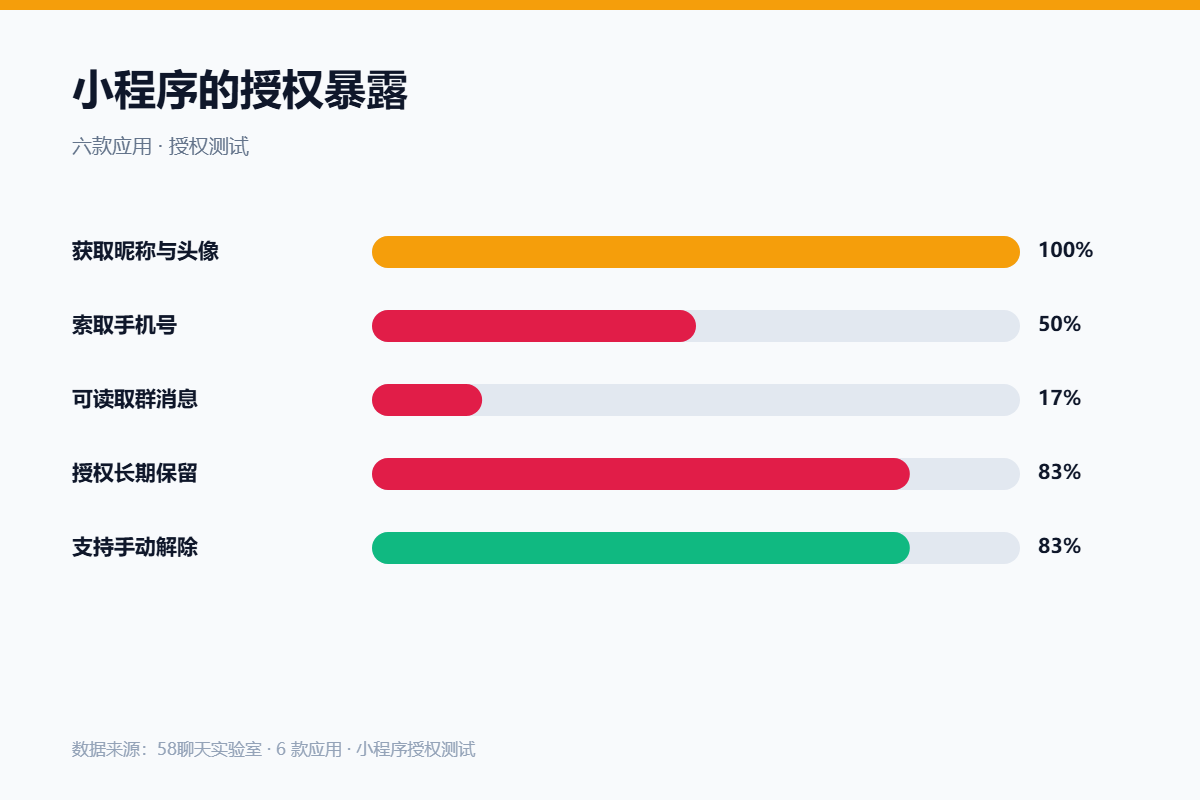
Identity data was universal. Every mini app received a nickname and an avatar, which is expected and also a stable link back to the account.
Requested Scopes
Scope requests were narrow on the surface. Three asked for a phone number despite having no feature that obviously needed one, which is the pattern worth questioning.
Data Returned
Returned data was modest in most cases. The exception was the application that could read group messages, which turns a small utility into a listener.
Authorisation Lifetime
Authorisation outlived the session. Five clients kept the grant until it was removed manually, which means a single use becomes a standing permission.
Where 聊天软件小程序隐私 Gets Risky
Risk concentrates in group contexts. A mini app opened in a group can often see who is present and, on one platform, what they said, which is a much larger scope than the same app opened privately.
Because of that, the practical habit is to open mini apps from a private chat and to revoke the access afterwards.
A Safer 聊天软件小程序隐私 Checklist
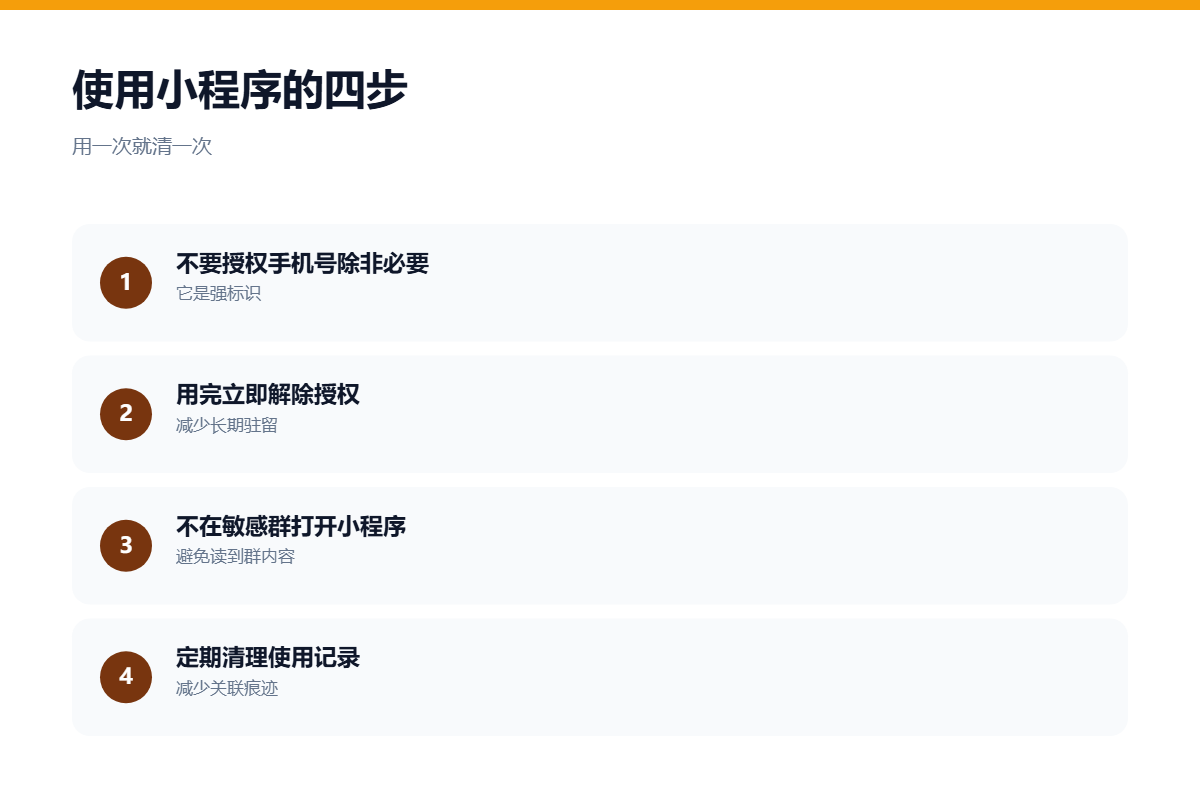
- Read the consent screen before approving.
- Refuse a phone number unless it is essential.
- Avoid opening mini apps inside sensitive groups.
- Revoke the authorisation after use.
- Review the authorised list periodically.
- Prefer mini apps from known publishers.
None of these steps prevent you using a mini app. Together they keep a quick utility from holding a permanent grant.
FAQ
Can a mini app read my chats in 聊天软件小程序隐私?
On one of six platforms it could read messages in the conversation it was opened from. Elsewhere the scope was limited to identity data.
How do I revoke 聊天软件小程序隐私 access?
From the authorised apps list in the client settings. In five clients the revocation took effect immediately and the mini app lost access.
Is a mini app the same as an installed app?
No. It runs inside the client with a narrower scope and it cannot access device permissions directly, which makes it safer by default and not harmless.
References
For related findings, read our audit of open interfaces and our notes on third-party sign-in. If permissions are your concern, our permissions audit is the next step.
评论
还没有评论,来说两句吧。
评论功能已关闭。