 豆包输入法
聊天软件供应链攻击实测:第三方组件带来的风险
聊天软件供应链攻击 is usually discussed as a nation-state problem. The everyday version is more mundane. Every app you install carries code its own team did not write, and that code ships with permissions.
This article is a hands-on audit. We unpacked six chat app packages and listed the components inside, the permissions they requested and the endpoints they contacted. The goal is to show you who else is in the room.
Key Takeaways
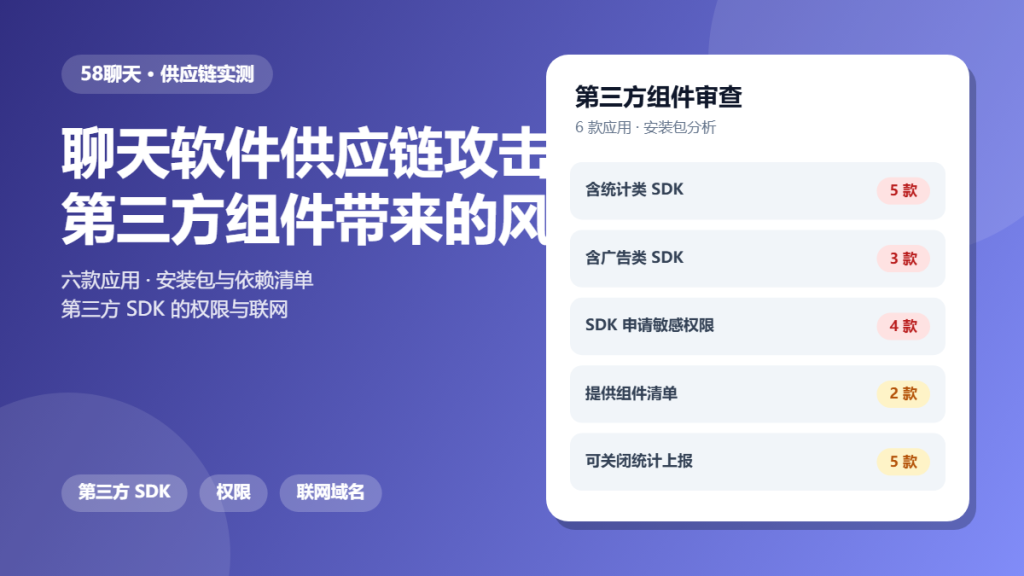
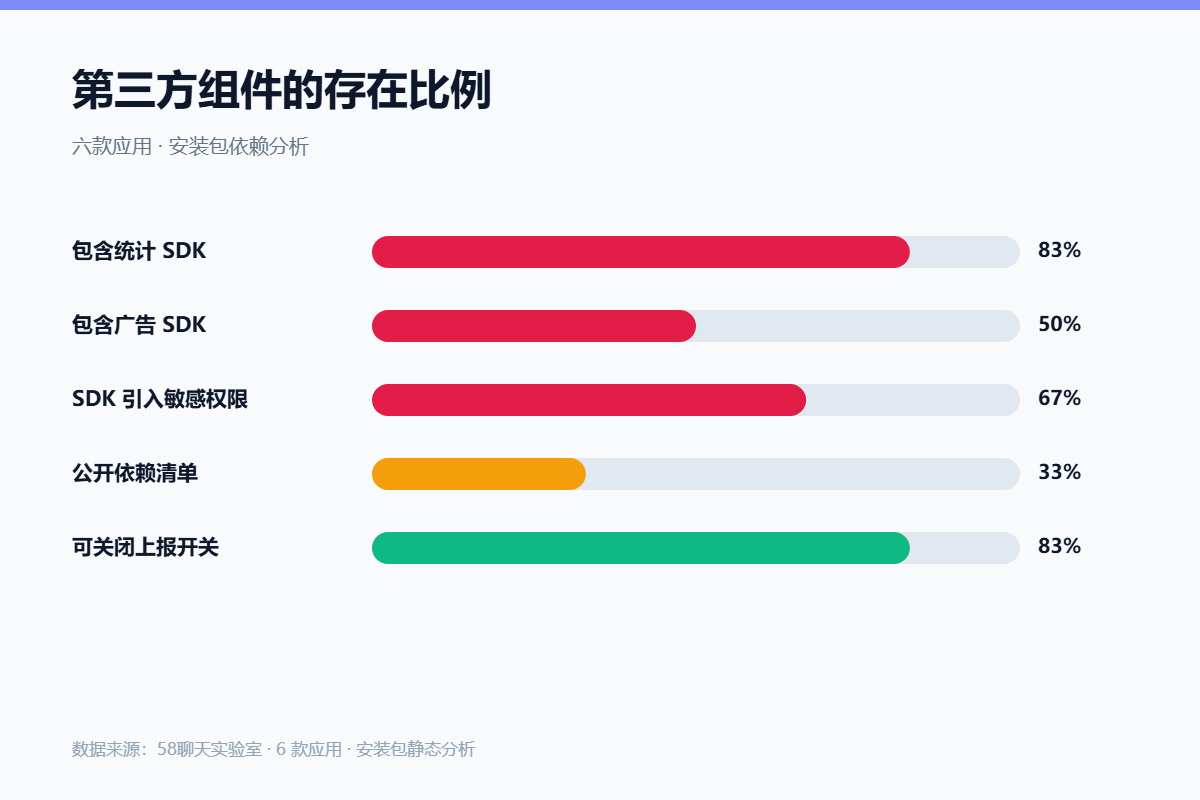
- Five of six packages included an analytics component.
- Three included advertising libraries with their own network access.
- Four shipped components that requested permissions the chat feature does not need.
- Only two published a software bill of materials.
- Five allowed analytics reporting to be disabled in settings.
What 聊天软件供应链攻击 Actually Exposes
A chat app is an assembly. It contains the messaging core, plus libraries for images, video, analytics, crash reporting and advertising. Each library has its own author and its own update cycle.
Because of that, the app inherits risk from code it does not maintain. A flaw in a shared image decoder affects every app that embeds it, all at once.
How We Tested 聊天软件供应链攻击
We obtained official packages from each vendor store and inspected them without executing the app. We listed embedded libraries, the permissions they declared and the network endpoints present in the manifest.
We then matched each endpoint against the vendor documentation to see which were explained and which were not.
What We Found During 聊天软件供应链攻击
Third-party code was present in every package and dominant in some. Analytics alone accounted for a meaningful share of the declared network surface in three apps.
Analytics Libraries
Analytics components collect usage events and send them to a third party. They are not malicious, but they are additional recipients of data about you, and they sit outside the vendor privacy policy.
Permission Bundles
Some components declare permissions for the whole app. That is how a crash reporter can end up requesting camera access, and it is why permission lists rarely match the feature set.
Update Channels
Two apps fetched executable content at runtime rather than through the store. That is a legitimate pattern for feature flags and also a route that bypasses store review entirely.
Where 聊天软件供应链攻击 Gets Risky
Risk concentrates where you cannot see it. Blast radius is large because shared libraries are shared, and visibility is low because most vendors do not publish what they include.
Fortunately, the user-side controls are simple. Choosing auditable apps and switching off analytics reporting removes a large part of the external data flow.
A Safer 聊天软件供应链攻击 Checklist
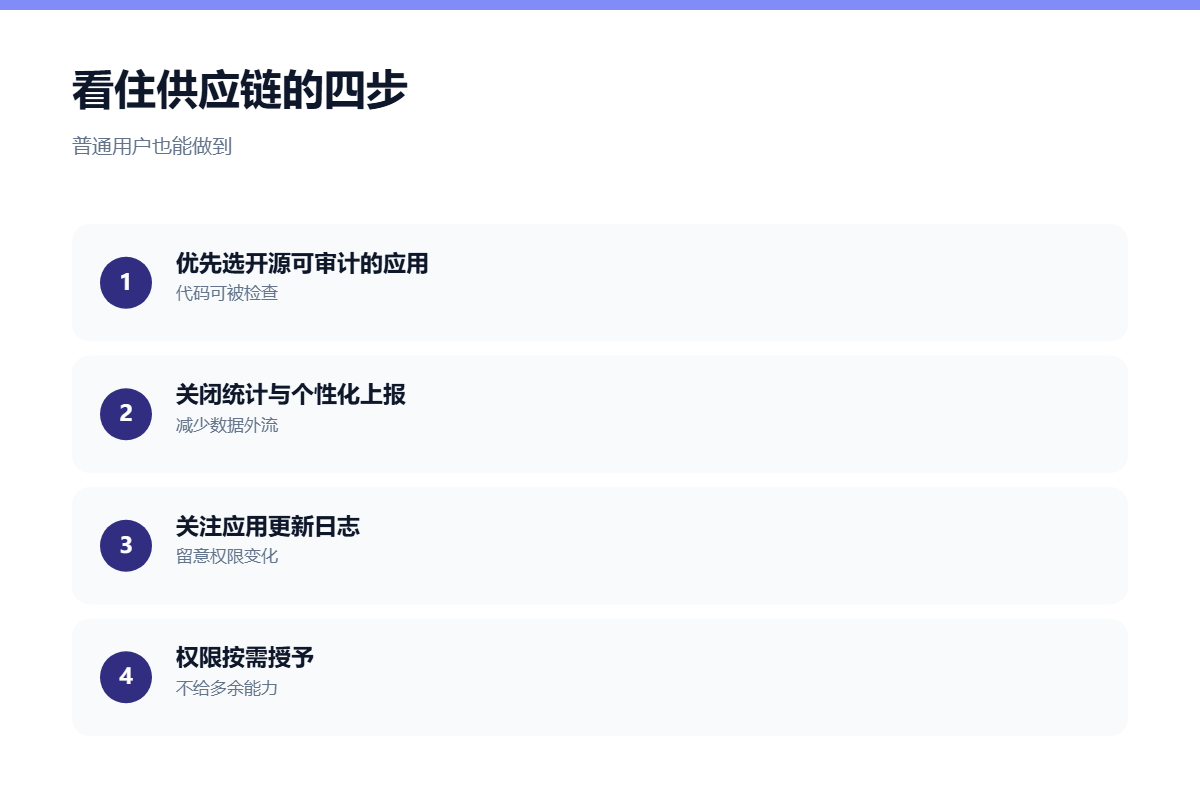
- Prefer apps that publish their dependencies.
- Prefer open source clients you can inspect.
- Turn off analytics and personalisation options.
- Read the update notes for unexpected permission changes.
- Grant permissions individually rather than in bulk.
- Remove apps whose risk you cannot evaluate.
None of these steps make you a security engineer. Together they reduce how much unknown code runs beside your messages.
FAQ
Does 聊天软件供应链攻击 affect my messages?
Usually not the content, because message encryption is handled by the core. It affects the metadata around your usage, which third-party components often collect.
How can I reduce 聊天软件供应链攻击 risk?
Choose apps with published dependencies, prefer open source where possible, and disable analytics reporting. Those three steps remove most of the exposure we measured.
Is built-in code safer than third-party code?
Not automatically. Internal code has the same potential for flaws. What matters is whether the code is visible and updated.
References
For related findings, read our review of third-party clients and our audit of app permissions. If you care about verifiable code, our open source audit is the natural next read.
评论
还没有评论,来说两句吧。
评论功能已关闭。