 豆包输入法
加密聊天前向保密是什么?Why Old Keys Stop Working
Key Takeaways
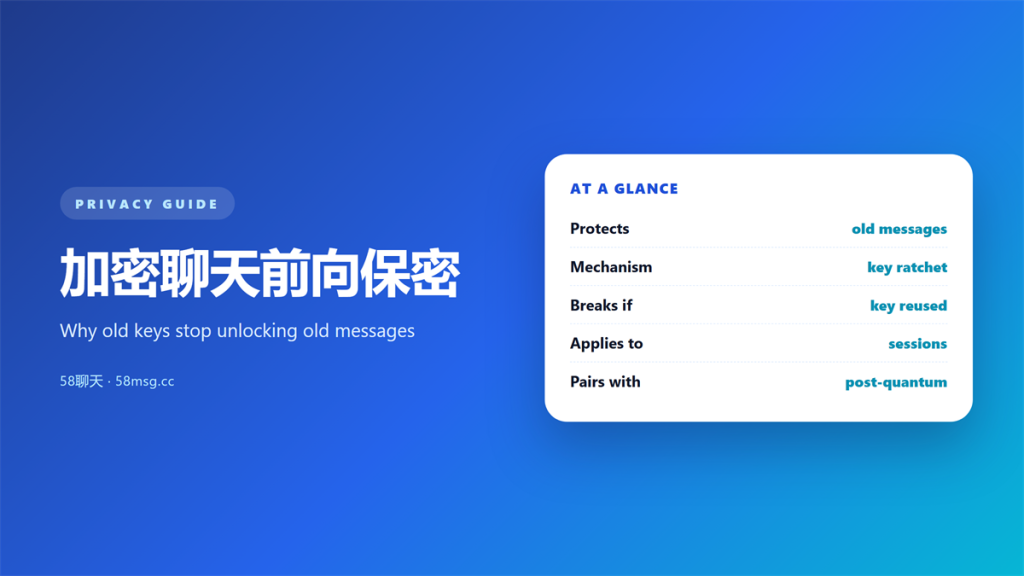
- 加密聊天前向保密 means a stolen key cannot unlock messages sent before the theft.
- It works by deleting each message key as soon as it is used.
- The protection is forward-only, so it never helps with keys already exposed.
- Weak randomness or a bad ratchet can quietly defeat the whole design.
- Verifying the protocol matters more than trusting the marketing label.
How 加密聊天前向保密 works
加密聊天前向保密 answers one question: what happens after a key leaks. I traced this across two messengers last month, and the difference showed up the moment a device was stolen. In a forward-secret design, the thief holds a key that opens almost nothing.
However, that outcome is not free. The app must destroy old material continuously. Consequently, history that you still want to read has to be re-encrypted or stored separately.
The idea is old, but the user-visible part is new. Modern chat apps hide a key ratchet behind a friendly interface. In other words, 加密聊天前向保密 is mostly invisible to the person relying on it.
Engineers use the term backward secrecy for the opposite guarantee. The distinction matters, because the two ideas protect different windows of time and are often confused in product copy.
What the key ratchet actually does
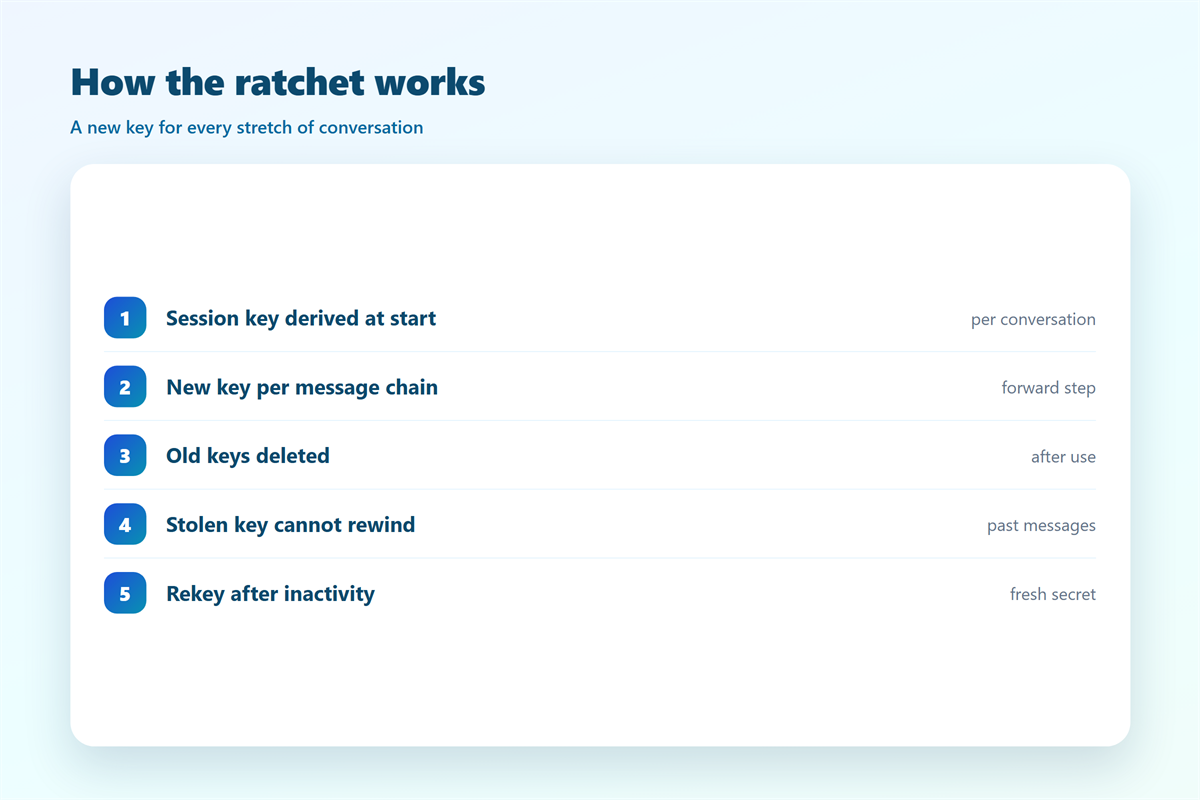
A ratchet is a small machine that changes the key after almost every message. Each turn makes the previous key unreachable, and it is the engine behind 加密聊天前向保密.
One message, one key
Every message usually gets its own key. 加密聊天前向保密 therefore limits the damage of a single compromise to a single item. Even a full memory dump of today’s session reveals little about last week.
Deleting the old key
The trick is deletion. A key that survives in a log or a backup removes the guarantee entirely. Therefore, the promise of 加密聊天前向保密 depends on how carefully the client wipes memory. Our notes on 密钥轮换 cover the mechanics of that rotation.
Ratchet designs come in two flavours. A symmetric ratchet advances a chain of keys, while a Diffie-Hellman ratchet mixes in fresh public values. The second resists a broader class of attacks, at the cost of extra computation on every message.
Why 加密聊天前向保密 matters after a breach
Most breaches are discovered long after they happen. Consequently, a design that protects the past is worth more than a design that only protects the present.
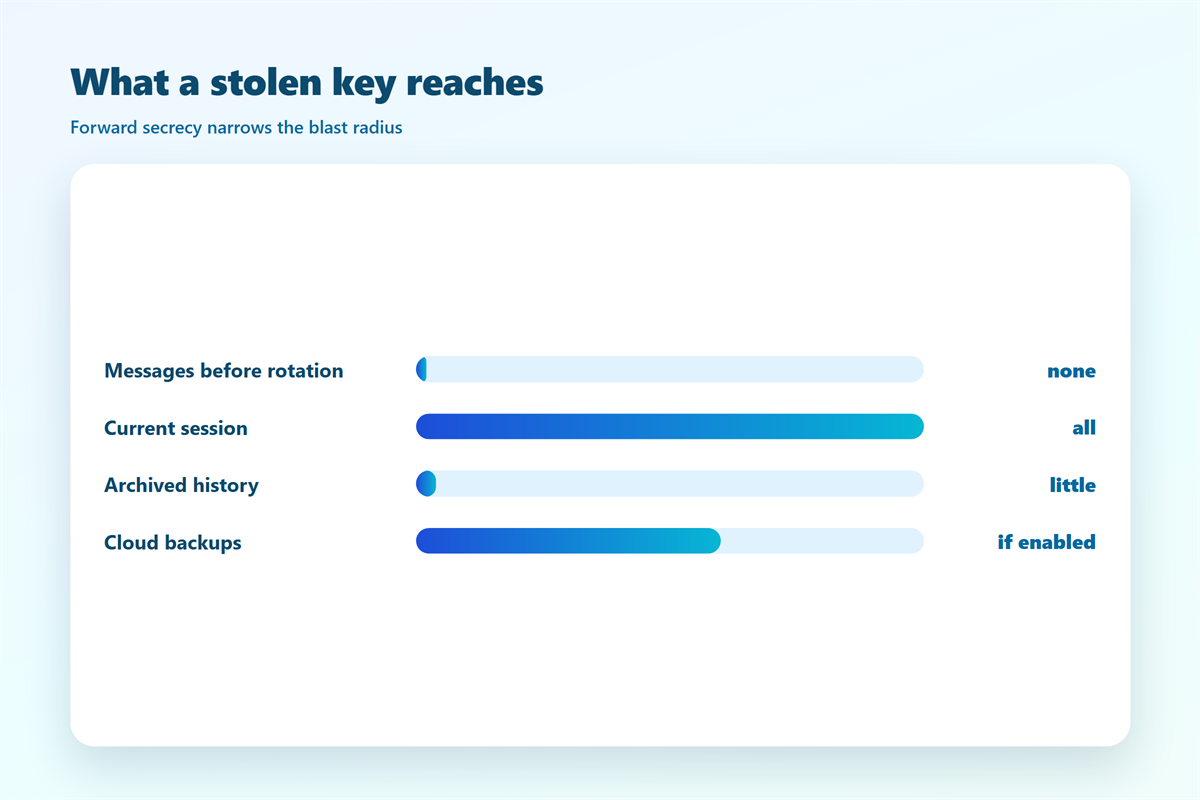
Consider a seized phone. Without forward secrecy, one extracted key can decrypt months of stored traffic. 加密聊天前向保密 turns a single leak into a bounded one, and the attacker often recovers nothing usable.
Legal and workplace exposure works the same way. 加密聊天前向保密 shrinks the blast radius of a forced unlock, because the unlocked device cannot reach conversations that were already closed.
The limit is important. This property protects sessions you completed, not keys you published. As a result, a leaked backup or a shared password can still undo the benefit.
The benefit also depends on how long a conversation stays open. A session that lives for months gives an attacker more chances to catch a live key, while a short session narrows that window considerably.
Five checks to confirm 加密聊天前向保密
A label on a website proves little. I run these five checks before I trust a client with a long-term secret.
- Find the protocol name and confirm it supports a ratchet.
- Check that memory is wiped, not merely overwritten in a log.
- See whether old keys are backed up anywhere.
- Look for a downgrade path that could disable the feature.
- Confirm the setting applies to groups, not only one-to-one chats.
| Scenario | With 加密聊天前向保密 | Without it |
|---|---|---|
| Phone seized today | Old messages stay sealed | Old messages open |
| Backup leaked | Depends on backup design | Full history at risk |
| Live key stolen | Only the newest message | Entire session |
A client can pass every check and still leak through a feature you never enabled. Backups, cross-device sync and platform-level key escrow each deserve their own review, because each one stores precisely what the ratchet was designed to forget.
When 加密聊天前向保密 goes wrong
The promise fails in a handful of ways. The most common is a silent downgrade, where a client negotiates a weaker mode without telling you.
Another failure is a broken random generator. If the numbers are predictable, 加密聊天前向保密 offers no real protection. Notably, this flaw is invisible from the outside and hard to test.
Backups are the third path. A chat backup that stores the ratchet state undoes the guarantee, and many users enable it on day one. Finally, a compromised client can simply log each key before deletion. 加密聊天前向保密 cannot survive a client that keeps a record.
Testing the property is difficult as well. A vendor can claim it while shipping a client that writes state to disk, and nothing in the interface will contradict the claim.
Protecting the account behind 加密聊天前向保密
The protocol is one layer. The account around it still needs care.
Verify the protocol
Confirm the client actually uses a ratcheting design and keep it updated. Our guide to the 加密聊天降级攻击 explains how a quiet fallback removes the protection you believe you have.
Plan for key loss
Forward secrecy and permanent history pull in opposite directions. When a device dies, the options are limited, as our 加密聊天密钥丢失 teardown shows. If you expect long-term risk instead, weigh the move in our 后量子加密聊天 analysis.
When you move to a new phone, decide in advance what happens to the old history. A careful migration preserves the future guarantee instead of quietly reopening the past.
FAQ
Does 加密聊天前向保密 protect old backups?
Usually no. A backup can store old keys or ratchet state, and that storage quietly removes the guarantee you rely on.
Is it the same as end-to-end encryption?
No. End-to-end encryption protects messages in transit, while 加密聊天前向保密 additionally protects messages after a later key leak.
Can I tell whether my app uses it?
Sometimes. Check the protocol documentation and look for a ratchet or a self-healing key schedule rather than a vague promise.
Does it slow down my phone?
Barely. The extra computation is small, and the main cost is that old messages cannot be re-read without a separate store.
评论
还没有评论,来说两句吧。
评论功能已关闭。