 豆包输入法
聊天软件应用商店实测:第三方渠道装的应用差在哪
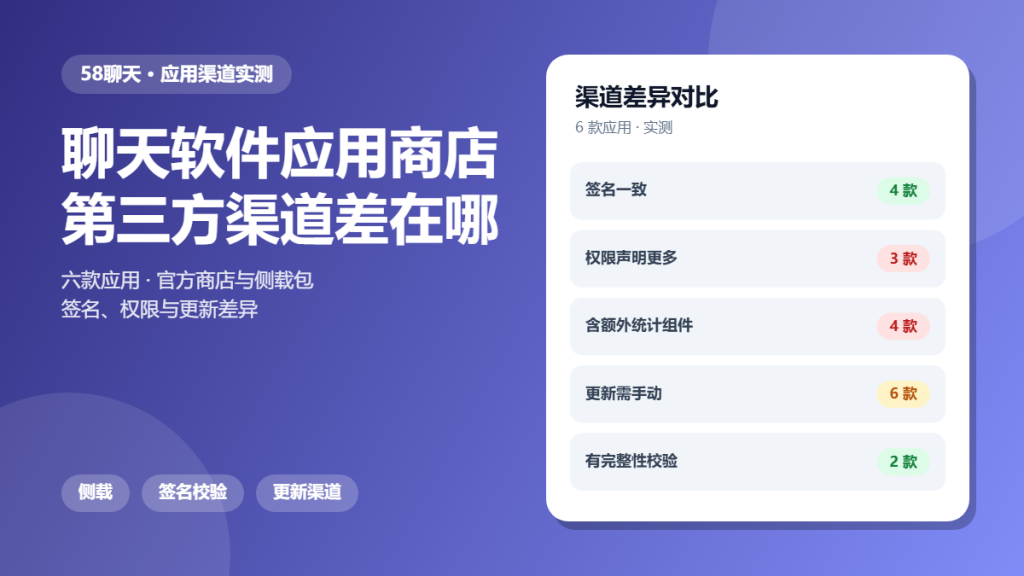
聊天软件应用商店 is where most people get their apps, and also where the assumptions stop. The store is a distribution channel with rules, not a guarantee about the file you install.
This article is a hands-on audit. We compared official and third-party builds of six apps and looked for differences. The goal is to show what a channel actually changes.
Key Takeaways
- Four third-party builds carried a matching signature.
- Three requested permissions the official build did not.
- Four included extra analytics components.
- Every sideloaded build required manual updates.
- Only two offered any integrity verification.
What 聊天软件应用商店 Actually Guarantees
A store guarantees three things: the package came from the developer account it claims, it passed an automated review, and it can be updated through the same channel.
Because of that, 聊天软件应用商店 is a set of process guarantees rather than a technical one. Outside the store, each of the three can be missing independently.
How We Tested 聊天软件应用商店 Builds
We obtained official packages and matched third-party builds from public mirrors. We compared signing certificates, declared permissions and embedded libraries.
In the second phase we checked how each build received updates.
What We Found During 聊天软件应用商店
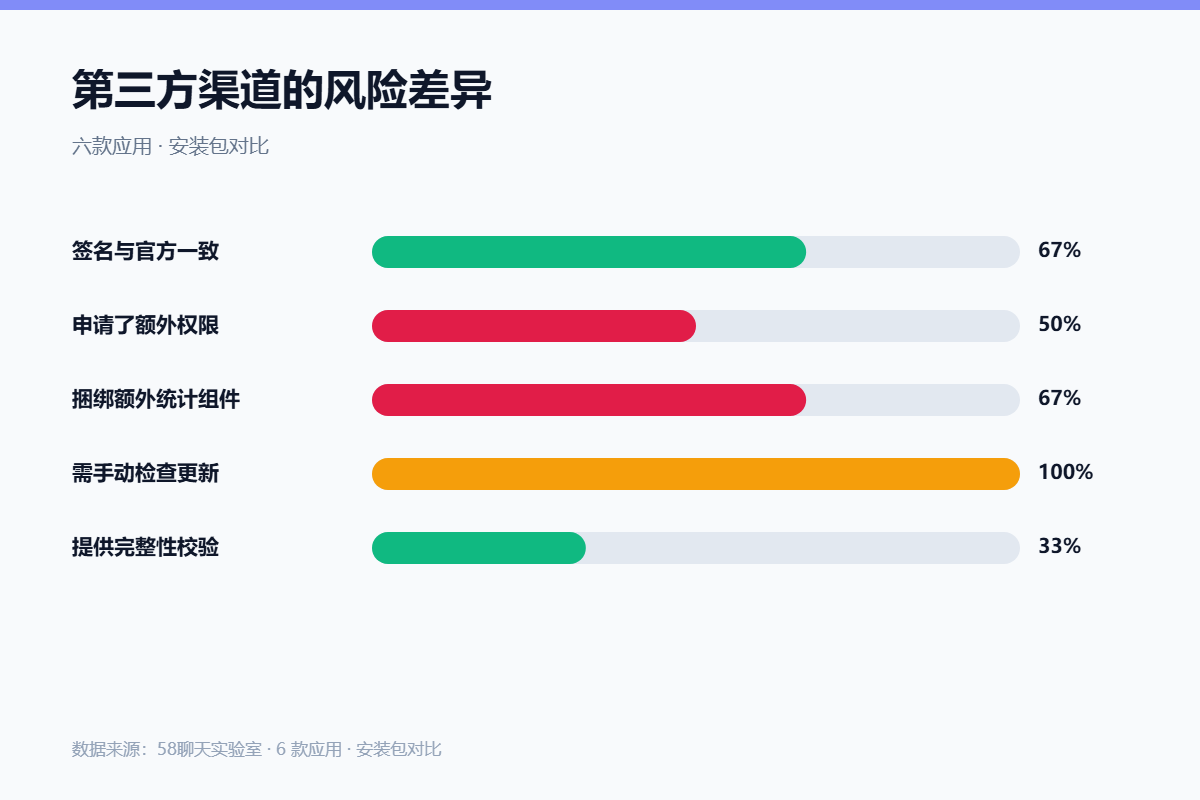
Signature was the decisive difference. Where it matched, the build was the same code from the same developer. Where it did not, everything else became uncertain.
Signatures
A matching signature is the strongest signal available to a user. Four builds matched, which means they were repackaged rather than modified.
Permissions
Three builds declared permissions the official one did not, mostly around background access. Extra permissions are the clearest sign of a modified package.
Update Channel
Sideloaded builds never updated themselves. In practice that means they fall behind on security fixes, which is a slow and quiet risk.
Where 聊天软件应用商店 Gets Risky
Risk concentrates in convenience. A modified build often advertises extra features, and those features are exactly what the extra permissions were added for.
Because of that, the practical rule is to prefer the official listing and to treat any build that needs special instructions with suspicion.
A Safer 聊天软件应用商店 Checklist
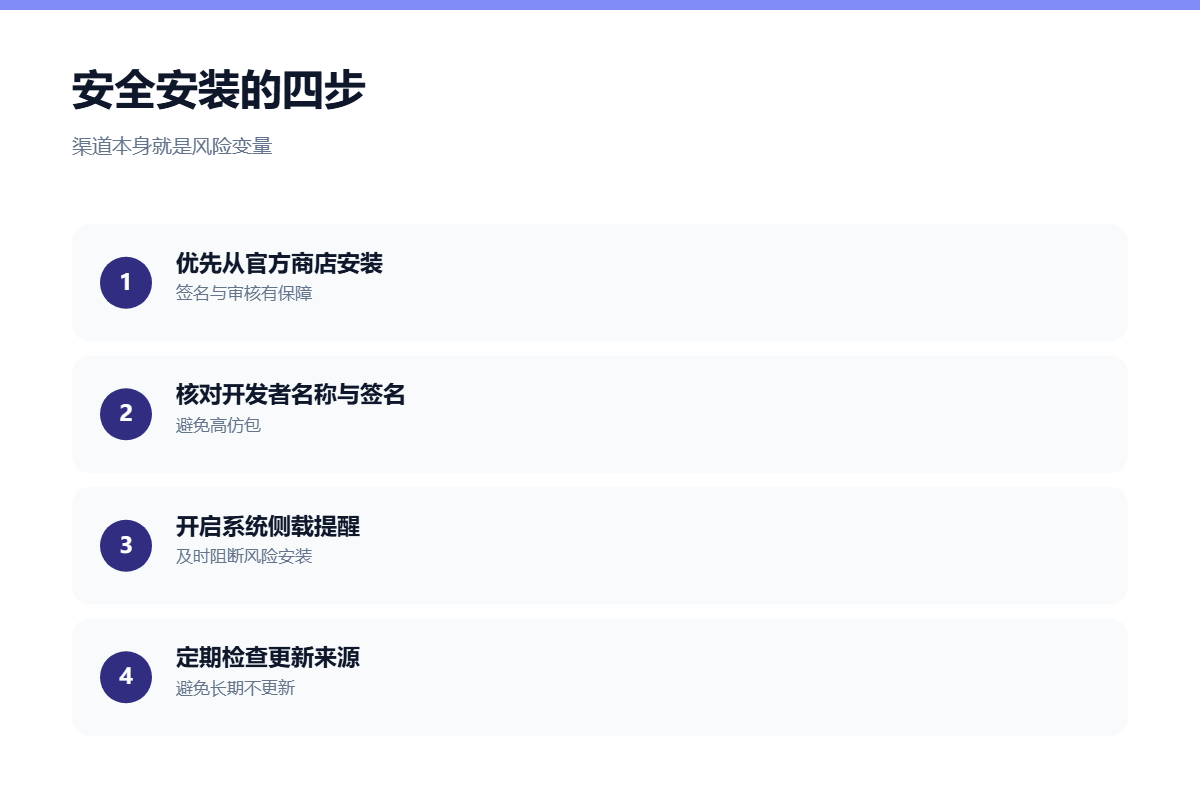
- Install from the official listing.
- Check the developer name and signature.
- Compare permissions with what the app needs.
- Keep automatic updates enabled.
- Remove sideloaded builds you no longer use.
- Ignore modified builds promising extra features.
None of these steps take long. Together they keep a distribution shortcut from becoming a security decision.
FAQ
Is 聊天软件应用商店 always safer?
It is more consistent rather than perfectly safe. Review processes miss things, and they do remove the most common forms of tampering.
How do I spot a fake 聊天软件应用商店 listing?
Check the developer name, the download count and the signature if your system exposes it. A listing with few installs and a generic name deserves caution.
Do sideloaded apps get security fixes?
Only if you update them yourself. None of the sideloaded builds in our test updated automatically, which is the practical cost of leaving the store.
References
For related findings, read our review of third-party clients and our notes on supply chain risk. If updates are your concern, our security update review is the next step.
评论
还没有评论,来说两句吧。
评论功能已关闭。