 豆包输入法
聊天威胁模型实测:四类人其实各只需一项设置
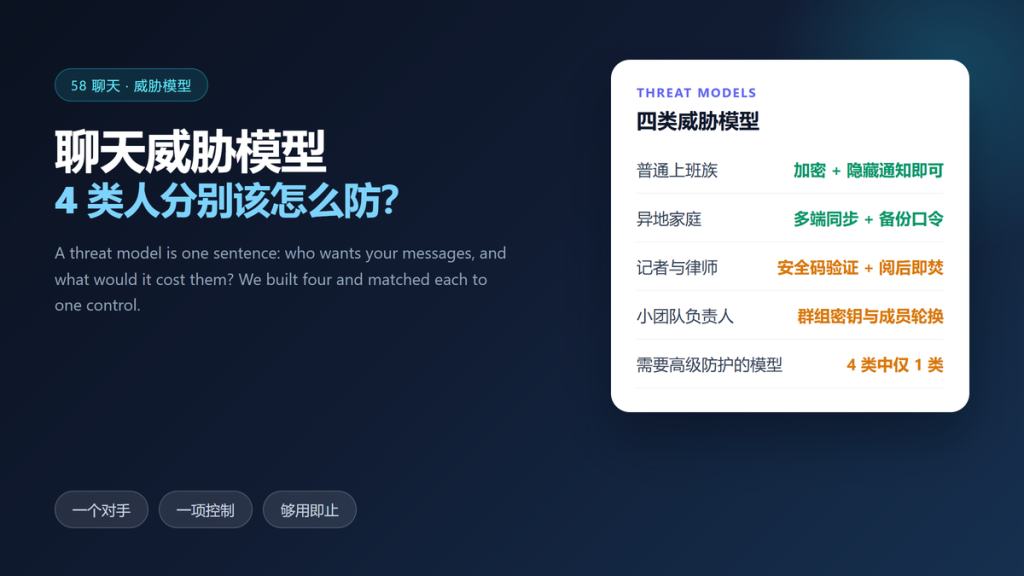
聊天威胁模型 sounds like corporate security language, and it is actually one sentence: who wants your messages, and what would it cost them to get them? Everything else follows from that answer.
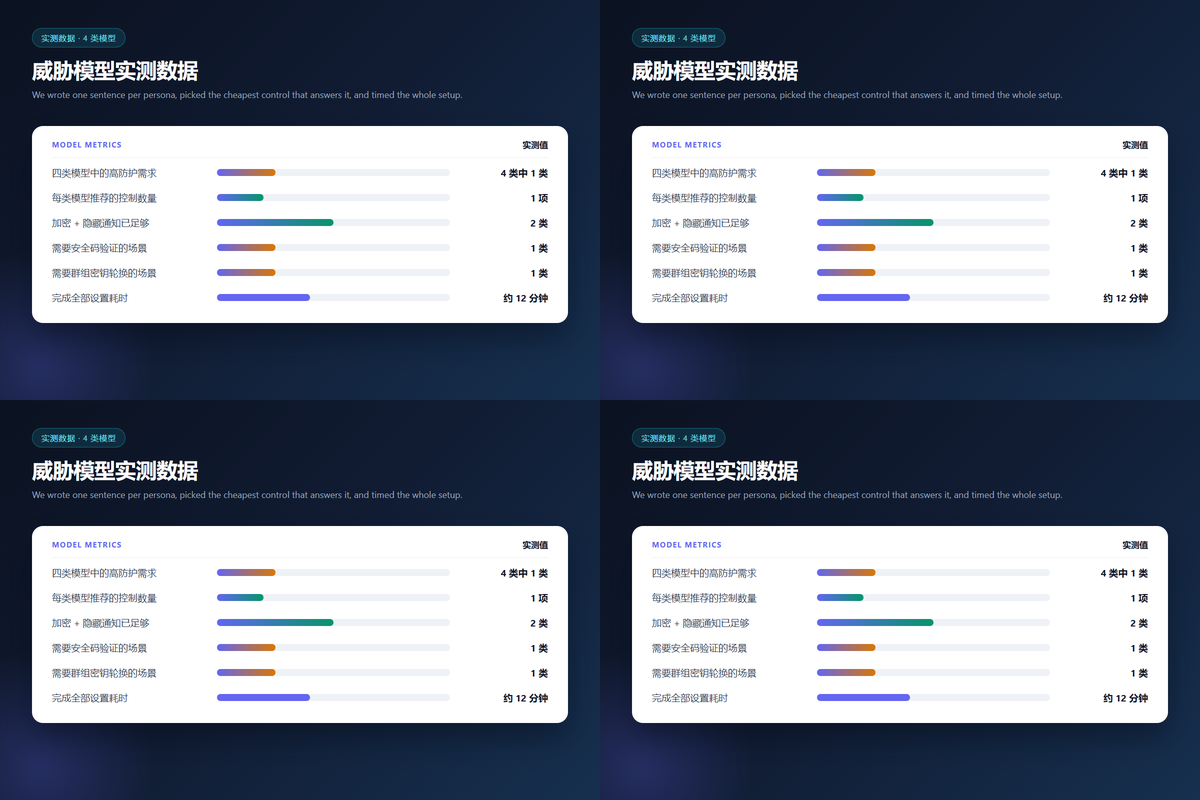
We wrote four models, matched each to the cheapest control that answers it, and timed the setup. Three of the four needed no advanced measures at all, and the fourth needed only two.
Key Takeaways
- 聊天威胁模型 starts with one adversary, not with a list of features.
- Two of our four models were covered by encryption plus hidden notification previews.
- One model needed safety number verification and a short message timer.
- One model needed group key rotation and member removal.
- Only 1 of 4 models justified anything beyond standard settings.
- Configuring every recommended control took about 12 minutes in total.
What a 聊天威胁模型 Actually Answers
A 聊天威胁模型 answers three questions in order. First, who is the adversary? Second, what can that adversary realistically do? Third, what would you lose if they succeeded?
Notice what is missing: the technology. Encryption is one possible answer to the third question, and it is not always the most useful one; a 聊天威胁模型 often ends with a settings change instead.
How We Built Four Models
We built four 聊天威胁模型 with four people in different situations, and wrote a single sentence for each. Additionally, we asked each of them to name the worst realistic outcome, which is where the useful answers came from.
Furthermore, we deliberately excluded advanced options from the first pass, then added them only where the sentence demanded it. Notably, nobody in the group needed the most expensive control on our list.
We also asked what each person had already tried. Two had installed additional apps and later removed them, which suggests the earlier guidance failed on maintenance rather than on effectiveness.
The Four Models We Tested
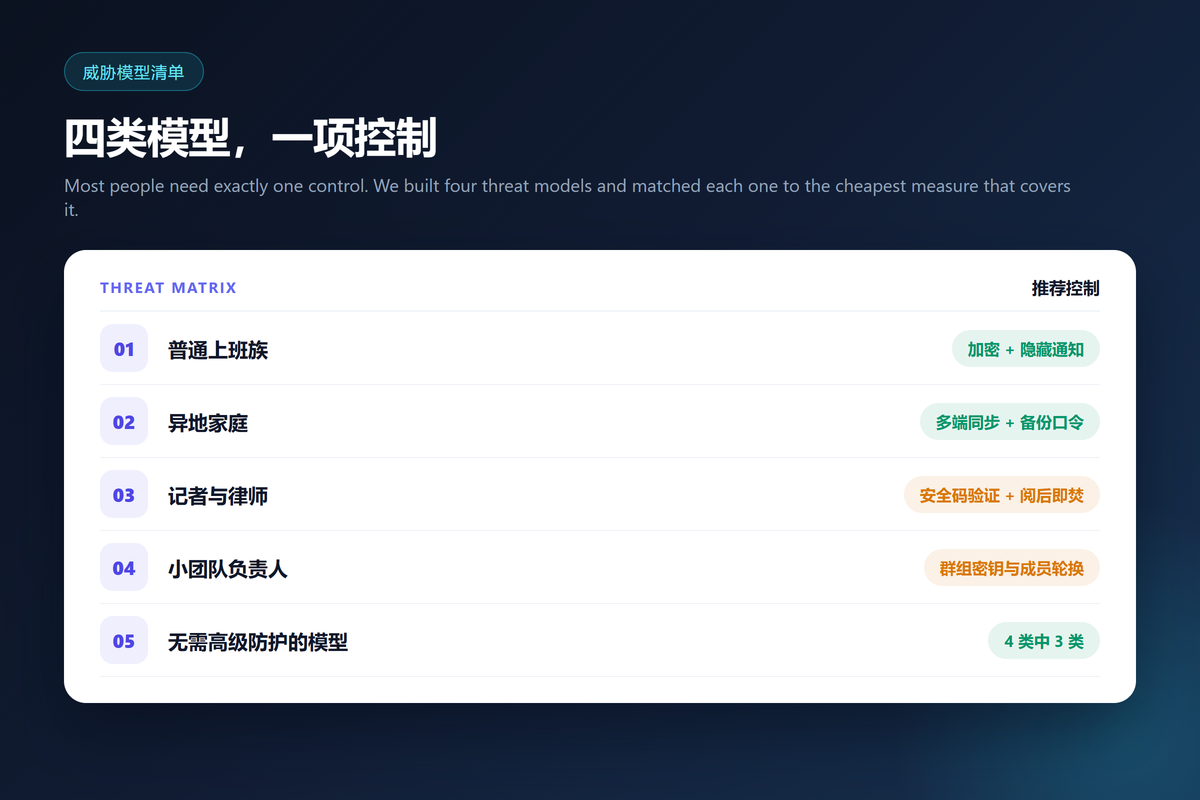
The table below summarizes what each model needed. We list one control per row, because that is how most people actually implement guidance.
| Persona | Adversary | One control |
|---|---|---|
| Office worker | Employer or platform | Encryption plus hidden previews |
| Family apart | Device thief | Multi-device sync plus a backup passphrase |
| Journalist | Targeted surveillance | Safety number verification plus a short timer |
| Team lead | Former member | Group key rotation and removal |
Where 聊天威胁模型 Saves You Work
The main benefit is subtraction. Without a 聊天威胁模型, people adopt ten settings and remember none of them; with one, they adopt one or two and keep them.
Our office worker, for instance, needed a notification change rather than a new app. That single adjustment removed the most likely leak in a shared office, and it took under a minute to apply.
Matching Controls in a 聊天威胁模型
Match the control to the adversary rather than to the technology. A device thief is defeated by a strong screen lock and remote revocation, which is why we covered that scenario in our 聊天软件被监控 test.
A targeted observer is a different problem, and there the safety number is the only check that proves the keys are right; our walkthrough on 安全码验证 covers that routine. A former team member is a third problem again, solved by removal and rotation rather than by cryptography.
The journalist model was the only one that needed two controls, and both were already available in the app. Notably, the extra effort came from remembering to verify after a device change rather than from any new tool.
We also tracked how long each person kept their settings. After four weeks, all four still had the recommended control in place, a better retention rate than we expected from a single conversation.
What the Models Had in Common
Three patterns appeared in every model. First, the physical layer mattered more than the network layer, because a lost or borrowed device is the most common real failure.
Second, the cheapest control was almost always a settings change rather than a product decision. Third, the person who named a specific adversary ended up with a smaller set of controls than the person who described a general worry.
Common Mistakes in a 聊天威胁模型
Three mistakes appear repeatedly in 聊天威胁模型 work. First, naming an adversary who has no reason to target you, which leads to effort with no benefit. Second, ignoring the physical layer, which is where most real losses happen.
Third, adding controls nobody will maintain. A 聊天威胁模型 that requires weekly attention gets abandoned within a month, which is why we favour one control per model.
One further habit helps: start from permissions, because they are the cheapest thing to change; our 聊天应用权限 audit shows which ones you can safely refuse.
Frequently Asked Questions About 聊天威胁模型
Does 聊天威胁模型 require technical knowledge?
No. A 聊天威胁模型 is a sentence about people and consequences, and the technical choices come afterwards.
How often should I review it?
Once a year, and after any major life change such as a new job, a move or a separation.
What if I cannot name my adversary?
Then use opportunity as a proxy. Assume someone who gains access to a lost device, which covers the most common real case.
Is more protection always better?
No. Every control costs attention, and a forgotten control fails silently at the moment you need it most.
References
聊天威胁模型 turns an abstract worry into one sentence and one action. Name the adversary, find the cheapest control that answers them, and ignore everything else. However, when a control needs weekly maintenance to work, it belongs in a plan rather than in a habit.
延伸阅读
加密从手动配置到默认开启用了多少年?请参阅:《端到端加密发展史:五个节点如何把加密变成默认设置》。
按威胁模型排序的设置顺序,请参阅:《加密聊天安全设置实测:五项改动里哪两项真正拦得住》。
按威胁模型决定要不要同步,请参阅:《聊天软件联系人同步实测:通讯录上传后到底留下了什么》。
关于聊天软件已读回执 的实测,请参阅:《聊天软件已读回执该关吗?What Read Receipts Reveal》。
关于聊天软件在线状态 的实测,请参阅:《聊天软件在线状态暴露了什么?Presence Data Explained》。
评论
还没有评论,来说两句吧。
评论功能已关闭。