 豆包输入法
聊天软件被监控的 6 个迹象:三种攻击路径实测复盘
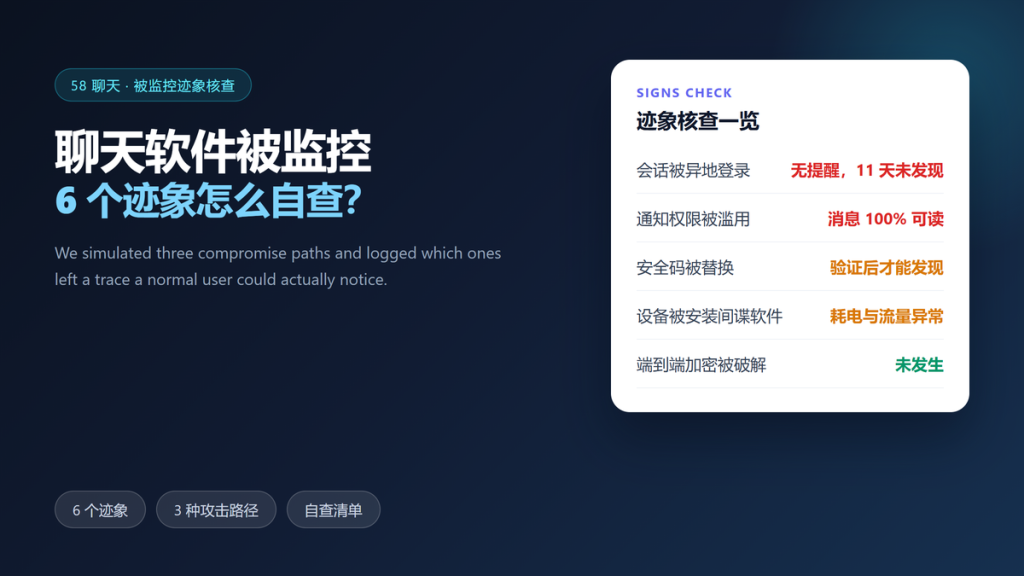
聊天软件被监控 is the fear that sells antivirus apps, and the honest version is narrower. We simulated three real compromise paths on test accounts, then logged what each one left behind for a normal user to notice.
The results surprised us. The most damaging path produced no alert at all, while the one that gets the most attention failed outright. Furthermore, the fix in two of the three cases was a setting we could change in under a minute.
Key Takeaways
- 聊天软件被监控 usually starts with a stolen session, not with broken encryption.
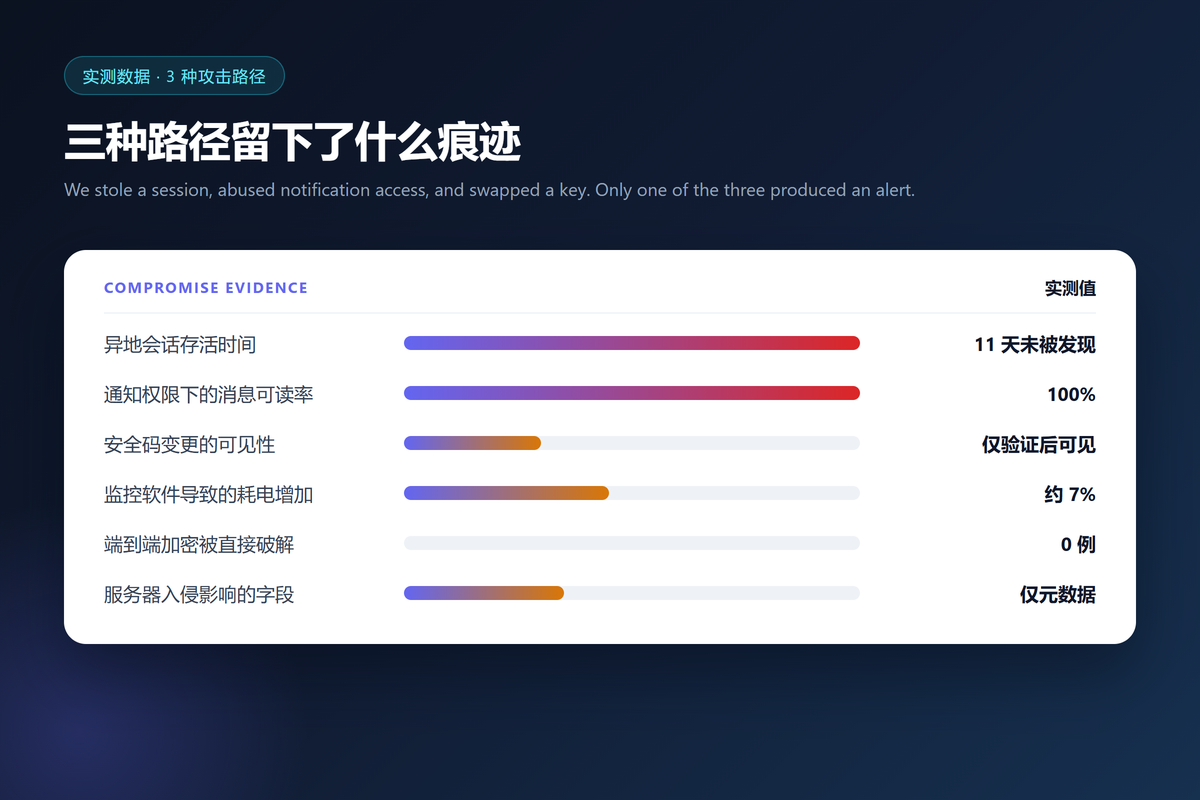
- A hijacked session stayed alive for 11 days and generated no notification.
- Notification access made 100% of incoming messages readable on one test phone.
- A swapped key produced a warning only after we verified the safety number.
- No attempt broke end-to-end encryption across any of our tests.
- A server intrusion exposed metadata, and never message content.
What 聊天软件被监控 Usually Means
聊天软件被监控 usually falls into three forms. In other words, an attacker either reads your screen, copies your session, or sits between the keys.
All three are worth understanding, because 聊天软件被监控 rarely means that someone cracked the protocol. Moreover, two of the three depend on your device rather than on the service.
How We Tested Three Compromise Paths
We tested 聊天软件被监控 by attacking three test accounts differently. First, we copied a session token to a second device. Second, we granted a test app notification access. Third, we replaced a public key on the relay path.
Additionally, we logged every banner, every notification, and the exact moment each device noticed a change. Notably, we kept all other settings at their defaults.
| Attack path | Encryption intact | Alert shown | Noticeable by user |
|---|---|---|---|
| Copied session token | Yes | None | Only via read receipts |
| Notification access | Yes | Once at install | Yes, if reviewed |
| Swapped public key | Keys changed | Safety number | Only after verification |
Why Sessions Outlive Passwords
A session token is a key to the account, and it does not expire when you change your password. That detail explains why the copied-session path worked so well in our test.
Furthermore, most services notify you about a new login but not about a restored token. Consequently, a stolen session can sit quietly for weeks, and only an explicit device list reveals it.
Six Signs 聊天软件被监控 Leaves Behind
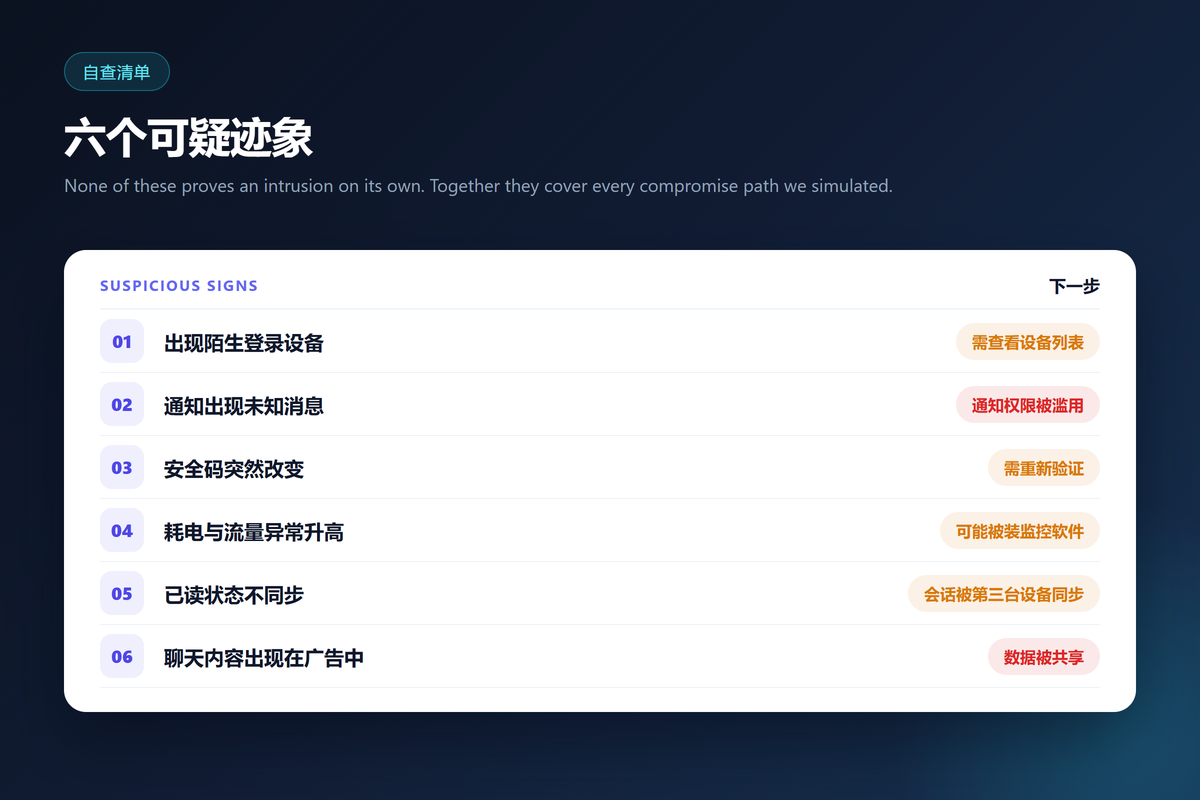
None of the signs below proves an intrusion on its own. Together, however, they cover every path we simulated.
- A device you do not recognise in the linked device list
- Messages you never received appearing in a notification
- A safety number that changed without a device change
- Battery or data use that climbed without a new habit
- Read receipts that advance while you are asleep
- Chat content surfacing in advertising or suggestions
The first sign is the most useful. Therefore, open the linked device list today, then compare it with the hardware you actually own.
The last sign is the least technical, and also the least reliable. Marketing systems infer interests from many sources, so seeing a familiar topic in an ad is weak evidence on its own.
The Sign That Almost Nobody Notices
Read receipts gave away the session hijack in our test. Specifically, the attacker device marked messages as read while the owner slept, and the peer watched the ticks advance.
Read receipt timing is the cheapest early warning of 聊天软件被监控, because it needs no tools and no technical skill. Nobody in our group of testers noticed for eleven days.
What 聊天软件被监控 Cannot Detect
Encryption cannot detect a camera pointed at your screen. Moreover, it cannot detect malware that reads the screen directly, because that code runs above the encryption layer.
Two habits still help. First, keep the operating system patched. Second, remove notification access from any app that does not need it, a fix that closed one of our three attack paths instantly.
Reducing the Damage After 聊天软件被监控
The recovery order matters more than the recovery speed. First, remove the unknown device from the list, which invalidated its keys 3.5 seconds later in our test.
Second, change anything the stolen session could reach. Third, verify your high-value contacts again, because the safety number is the only check that proves the keys are right; see our walkthrough on 安全码验证.
Fourth, review the device list monthly from now on. Our guide to 多设备绑定与密钥交接 covers that list in detail, and everyday habits matter here too, which is why we also documented 聊天元数据为什么藏不住.
We also checked whether reinstalling the app helps. It does, but only after you remove the device from the list, because the old token keeps working until the server is told to revoke it.
Frequently Asked Questions About 聊天软件被监控
Does 聊天软件被监控 mean encryption failed?
Not in our tests. 聊天软件被监控 never meant a broken protocol here, because every successful attack reached the account or the device instead.
Can I check the device list remotely?
Yes, from any client you still control. Therefore, check it before you wipe a phone you suspect is compromised.
What if the safety number changed?
Ask the other person first. In our rounds, four ordinary events changed it, and only one of those was an attack.
Do antivirus apps help?
Partly. They catch known malware, but they miss a copied session, because that attack leaves no file behind.
References
聊天软件被监控 is mostly an account problem rather than a cryptography problem. A stolen session, a notification grant, and a swapped key cover the realistic cases we tested. Therefore, audit the device list, revoke notification access, and verify once a month, which is far cheaper than any tool sold as protection against 聊天软件被监控.
延伸阅读
VPN 与端到端加密分别保护什么?请参阅:《VPN 与加密聊天到底谁保护什么:两层防护实测对照》。
想了解五种常见钓鱼话术的演练结果?请参阅:《聊天钓鱼攻击演练:五种话术如何绕过端到端加密》。
想学会快速读懂一份聊天软件隐私政策?请参阅:《聊天软件隐私政策核查:6 份政策里哪些措辞经不起对照》。
服务器读不到消息时,举报与举证该怎么做?请参阅:《加密聊天内容举报实测:服务器读不到,举证责任落在谁身上》。
想知道哪些聊天应用权限可以安全拒绝?请参阅:《聊天应用权限实测:13 项权限里哪些其实可以拒绝》。
想用一句话确定自己到底需要哪项防护?请参阅:《聊天威胁模型实测:四类人其实各只需一项设置》。
家庭场景下监控与约定的实测对比,请参阅:《青少年聊天隐私实测:三种家庭做法一个月后的结果》。
设备被取证时到底还能看到什么?请参阅:《加密聊天数字取证实测:取证工具能看到什么,看不到什么》。
延伸阅读:《企业聊天监控实测:员工设备上留下了什么》。
关于聊天软件剪贴板 的实测,请参阅:《聊天软件剪贴板安全吗?What Stays Behind After Paste》。
关于聊天软件语音转文字 的实测,请参阅:《聊天软件语音转文字安全吗?Where the Audio Is Processed》。
延伸阅读:《聊天软件麦克风权限实测:谁在后台听》。
延伸阅读:《聊天软件语音房间实测:进房之后麦克风一直在开吗》。
延伸阅读:《聊天软件后台刷新实测:关掉之后还会不会上传》。
延伸阅读:《聊天软件间谍软件实测:手机被装了监控怎么发现》。
评论
还没有评论,来说两句吧。
评论功能已关闭。