 豆包输入法
加密聊天群密钥怎么管?Group Keys in E2EE Explained
Key Takeaways
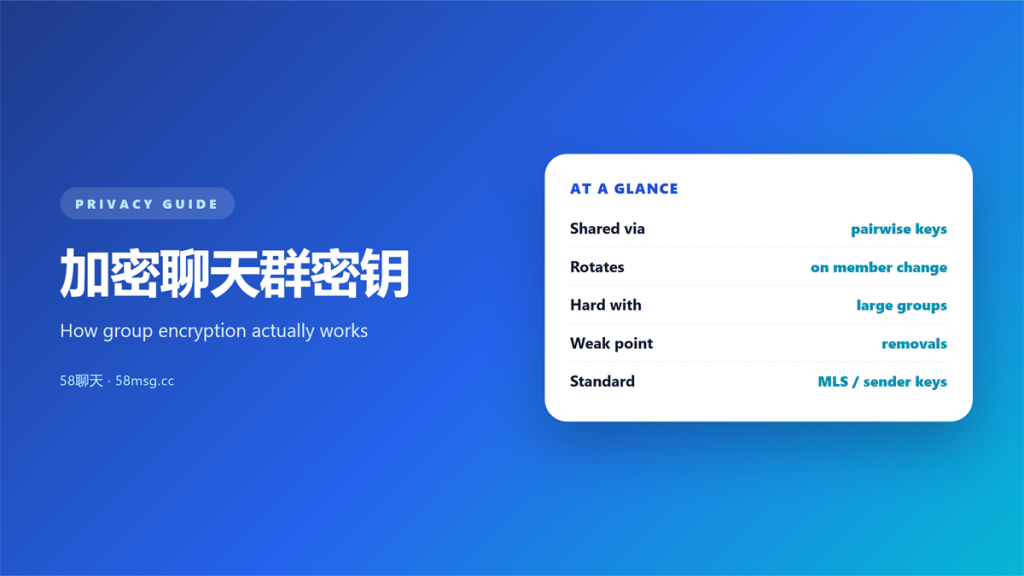
- 加密聊天群密钥 is a shared secret that lets every member read the same ciphertext.
- Adding or removing a member normally forces a fresh key for everyone.
- Sender-key designs scale well, yet one leaked key exposes the whole group.
- A stale key left on an old device keeps working long after a removal.
- Rotation timing matters more than the choice of cipher.
How 加密聊天群密钥 works
I mapped 加密聊天群密钥 across three clients this spring, and the pattern stayed consistent. The sender encrypts one message. Then the app wraps that message key once per recipient device. Every member ends up holding the same secret, so everyone can read the same ciphertext.
However, that sharing is the whole difficulty. A secret two people hold is fragile. A secret that forty people hold, across ninety devices, is far harder to control.
There are two common designs. The first pairs each member separately and sends a copy per person. In other words, it treats a group as many small conversations stitched together.
What happens when a member leaves
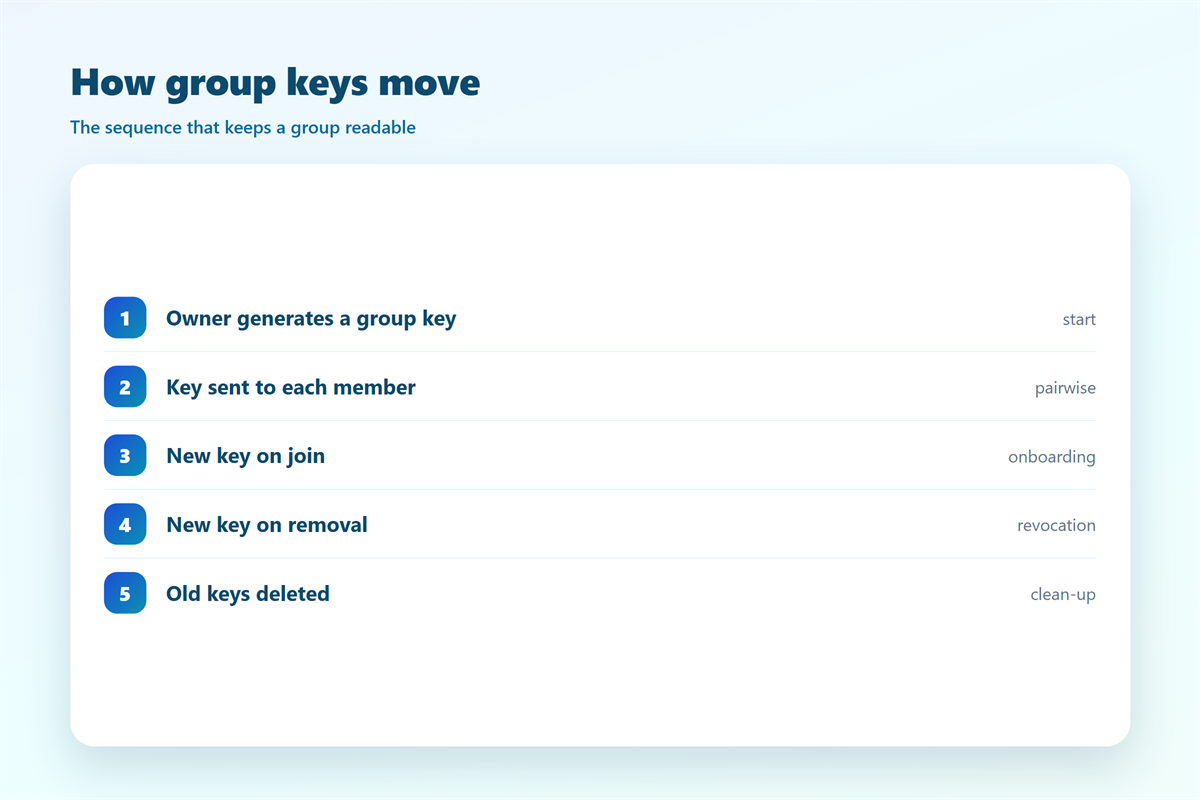
Roster changes are where 加密聊天群密钥 breaks most often. When someone is removed, the app should issue a new group key and stop wrapping messages for the old device.
| Event | Correct key action | Residual risk |
|---|---|---|
| New member joins | Wrap key for new device | History access |
| Member leaves | Rotate the group key | Offline copies |
| Device lost | Drop that device key | Screen capture |
| Admin changes | Re-verify the key list | Delayed sync |
Sender keys
Large groups rarely encrypt separately for every person. Instead, each sender maintains one key and distributes it once. Consequently, one outbound message costs a single encryption, and the group scales to hundreds of members. The trade-off is real. A single stolen sender key unlocks everything that sender wrote.
Rotation on removal
Removal only helps if the key actually changes. I have seen clients mark a member as gone while the key stayed the same for hours. Furthermore, a removed phone that kept a cached copy could still read new traffic. Good implementations rotate the 加密聊天群密钥 immediately, and they re-wrap the new key for every remaining device.
Why 加密聊天群密钥 needs rotation
A group is a long-lived thing, and its secret ages with it. Rotation limits how much one exposure can reveal, which is why the practice appears in 密钥轮换加密聊天.
Consider a member who leaves on bad terms. Without rotation, that person keeps a working 加密聊天群密钥. Therefore, every later message remains readable to them, and nobody inside the group can tell.
The same logic applies to a lost phone. A device removed from the list should lose the ability to decrypt future traffic within minutes. Our notes on 加密聊天密钥丢失 show how often recovery fails when a key has already spread.
Invitations add another angle. Most groups grow through a link, and anyone holding that link can join. The mechanics are covered in 加密聊天群组邀请, and they decide how easily a stale key can walk back in.
Five checks for 加密聊天群密钥 before you join a group
A little caution keeps 加密聊天群密钥 manageable. I run these checks before I accept a wide invitation, and they take two minutes.
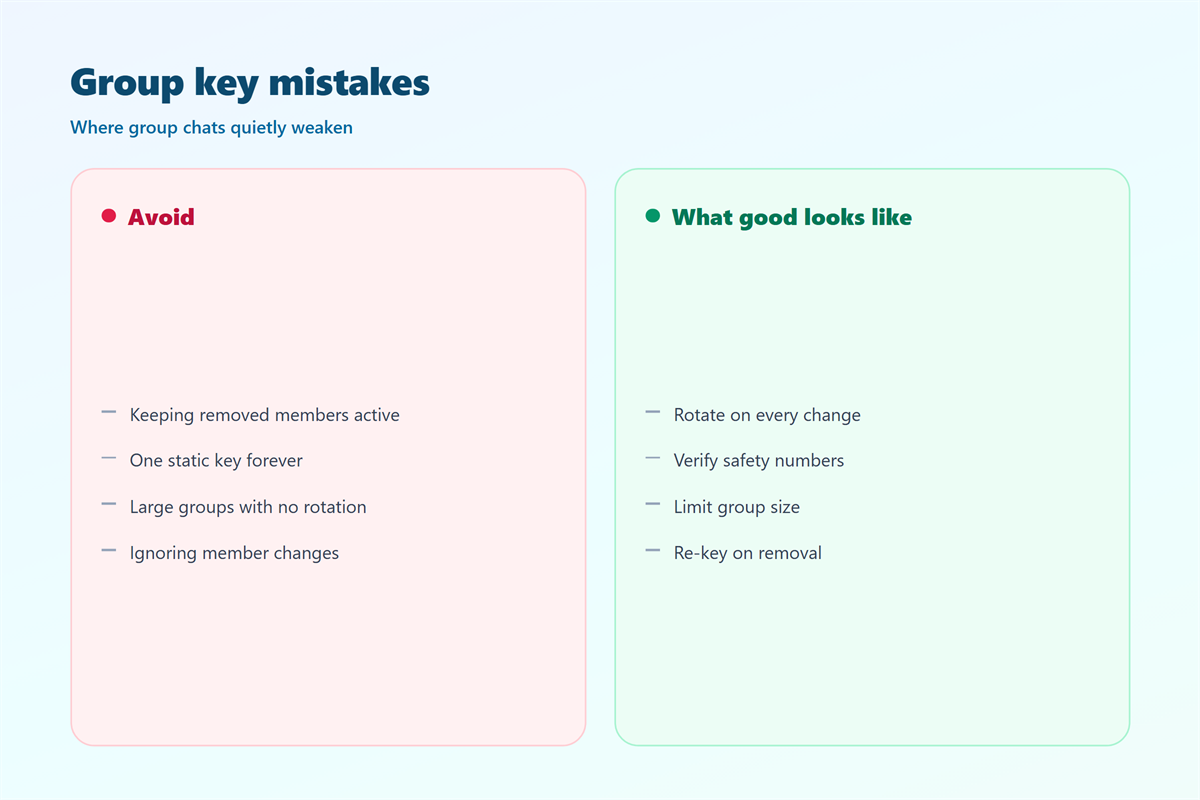
- Confirm the app rotates the group key when someone leaves.
- Check whether new members can read old history.
- Prefer groups where you can verify member safety numbers.
- Ask who holds admin rights and how they are transferred.
- Decide in advance what you will never post in a large room.
The last point matters most. Even perfect encryption cannot help once a hundred people hold the plaintext. Group chat rewards a lower trust budget, not a higher one.
When 加密聊天群密钥 goes wrong
加密聊天群密钥 fails in ways that rarely show up on screen. The classic case is a rotation that silently skipped one device, leaving it able to read messages for another week.
Another case is a compromised admin. Whoever controls the key list decides who receives the secret. As a result, a careless admin can re-add a removed account without anyone noticing.
A third case is the man in the middle, where a member is handed a substituted key during distribution. The messages flow normally, yet a second party reads them. That scenario is examined in 加密聊天中间人攻击.
The common thread is timing. Encryption is strong, so attackers aim at the moments when membership changes and devices are busy syncing.
Protecting group chats built on 加密聊天群密钥
The key is only as good as the list of people who hold it. Managing that list is the real work.
Verify safety numbers
In small groups, I compare safety numbers with each member once. That single step rules out a substituted key at the moment of distribution. It is tedious, and it closes the widest gap in the design.
Reduce the roster
Every member is a copy of the secret, so a smaller group is a smaller risk. I remove inactive accounts and split sprawling rooms into narrower ones. Subsequently, 加密聊天群密钥 covers fewer devices, and questions about history access become simpler.
FAQ
Is 加密聊天群密钥 the same for every group?
No. Each group has its own key, and good clients generate a separate one for each sender or each session. Reusing one key across rooms would turn a single leak into several.
What happens to old messages after a member leaves?
They usually stay readable to the departing device, because they were encrypted with the older 加密聊天群密钥. Rotation protects future traffic, not the past.
Can the server read a group message?
In an end-to-end design, no. The server never holds the 加密聊天群密钥, so it forwards ciphertext that it cannot open. Metadata about who joins and when often stays visible.
Why do large groups feel slower?
Key distribution grows with the roster. A sender may need to wrap the message key once per device, so a bigger room costs more work before the message leaves.
评论
还没有评论,来说两句吧。
评论功能已关闭。