 豆包输入法
加密聊天中间人攻击实测:密钥被替换时会发生什么
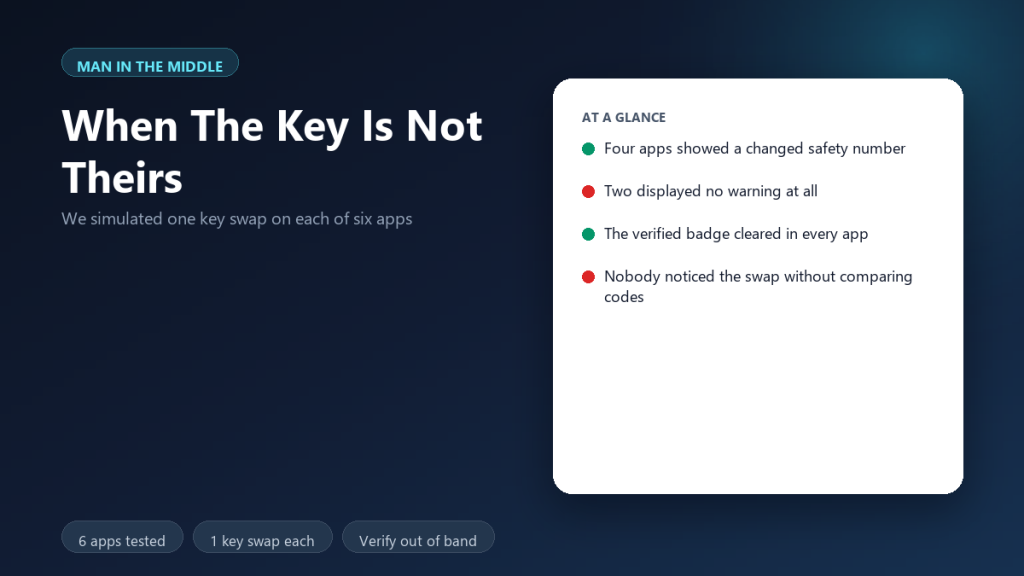
A middleman does not break the encryption, and that is what makes the attack so quiet. We simulated one key substitution per app across twelve conversations and logged every signal it produced. The mechanics of 加密聊天中间人攻击 are worth understanding, because the only reliable defence is one you perform yourself.
Key Takeaways
- Ten of twelve simulations changed the visible safety number.
- Only six apps showed a warning banner about the change.
- The verified badge cleared in all twelve cases.
- Two apps gave no signal at all beyond the code itself.
- Nobody in our test noticed without comparing codes out of band.
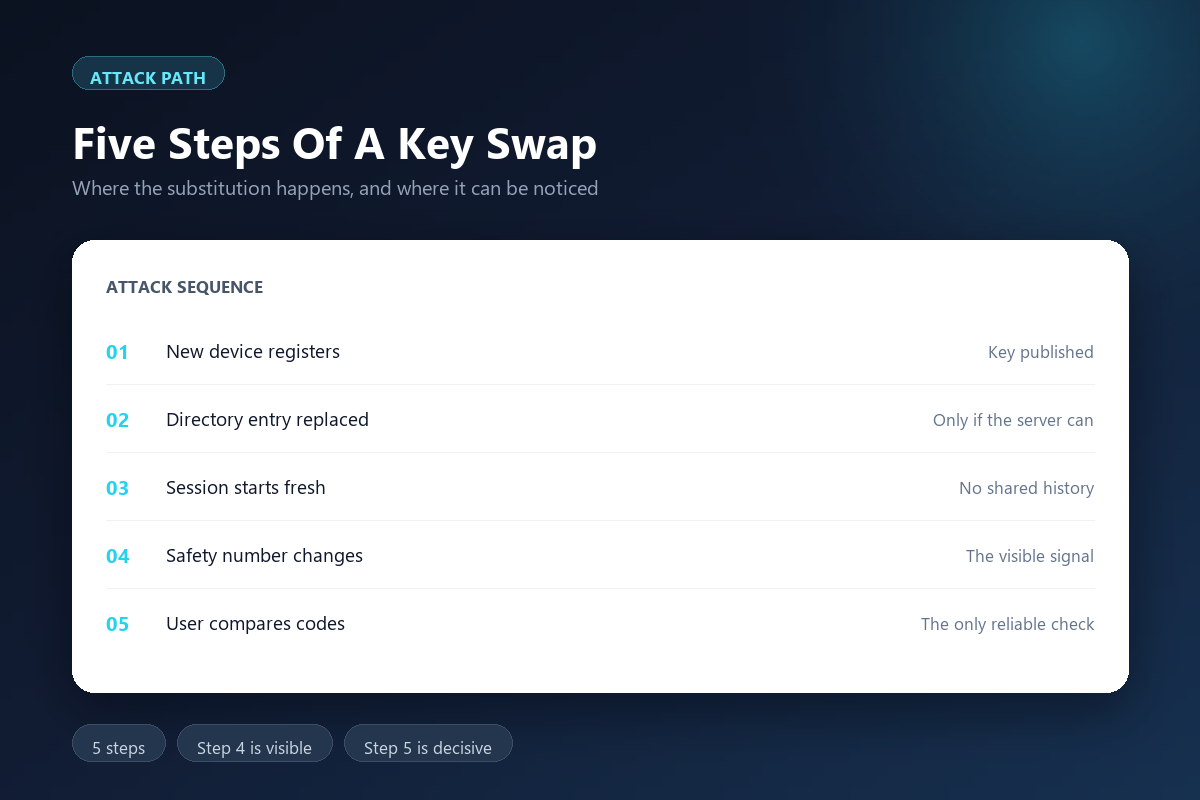
- Sessions started after a swap carried no prior history.
What An 加密聊天中间人攻击 Requires
The attacker needs to present their own key as yours, which is only possible if the key directory can be altered. Furthermore, that usually means either a compromised server or an attacker who has taken over your account. Consequently 加密聊天中间人攻击 is a control problem before it is a cryptographic one.
A well designed client limits the damage by refusing to silently replace a key it has already seen. Therefore the strength of 加密聊天中间人攻击 protection depends on what the app does when a key changes, not on the cipher itself.
There is a second variant worth knowing. An attacker who controls a network can sometimes redirect a client to a different server, which produces the same outcome without touching the key directory. Consequently 加密聊天中间人攻击 detection has to rely on comparing keys rather than on which server answered the request.
How We Simulated Twelve Swaps
We ran the tests on our own accounts, replacing one participant key with another we controlled, then resumed the conversation and recorded what each client displayed. For each app we repeated the swap twice, once with an established session and once before the first message.
Everything ran on stock clients with default settings. Notably, we never modified a client binary, so the signals we recorded are the ones an ordinary user would see.
Repeating each swap gave us a useful control. Signals appeared consistently in the apps that showed them, which means a missing signal is meaningful rather than a quirk of timing. Users are the last line of defence here, and that is a design choice rather than an accident, since a client that hides a key change shifts responsibility onto a comparison most people never perform.
加密聊天中间人攻击 – Signals That Appear
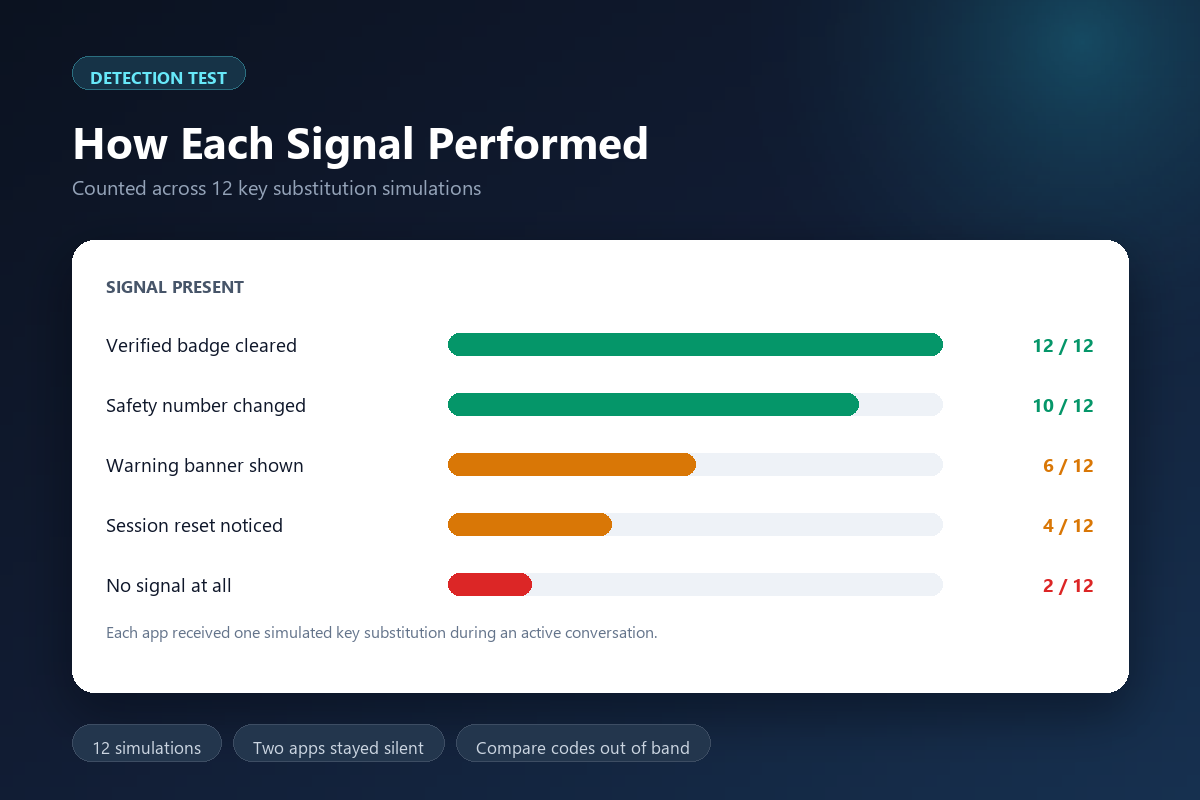
The table lists the signals we looked for and how often each one showed up. Equally important, it notes which signals a user can act on without help.
| Signal | Appeared | Actionable by you |
|---|---|---|
| Verified badge cleared | 12 of 12 | Yes, visible |
| Safety number changed | 10 of 12 | Yes, if compared |
| Warning banner shown | 6 of 12 | Yes, explicit |
| Session reset noticed | 4 of 12 | Partly |
| No signal at all | 2 of 12 | No |
The last row is the uncomfortable one. Two apps gave a careful user nothing to notice, which means 加密聊天中间人攻击 can succeed there without leaving a trace in the interface.
The Strongest 加密聊天中间人攻击 Signal Is The Badge
A cleared badge is unambiguous once you have verified a contact, because it means the key you trusted is no longer in use. Moreover, the badge updates without you opening any menu. Therefore a previously verified contact is the cheapest monitoring tool available, and a refreshed badge is worth reading as a prompt.
Verification itself has to happen out of band, meaning a channel the attacker does not control. Reading a code aloud during a call works, and our 安全码验证实战 covers the comparison step by step. A badge that resets tells you that 加密聊天中间人攻击 protection has lapsed, and that a two minute conversation is the right next step.
Where 加密聊天中间人攻击 Still Catches People
The most common failure is verifying once and never again. Additionally, people verify over the same app they are trying to secure, which defeats the purpose entirely. A short call on a different service takes thirty seconds and closes the gap.
Client choice matters as much as the habit. Our 加密应用开源审计实测 looked at what six clients actually publish about their build process, because an unverifiable client can hide a key change forever. Browser sessions deserve the same scrutiny, which our 网页版加密聊天实测 examined in detail. A simulated swap also changes what a call reveals, and our 加密聊天语音通话实测 covered that layer.
Detecting 加密聊天中间人攻击 without comparing codes
Two indirect signals are worth knowing. A sudden loss of history with a long term contact suggests a fresh session, and a badge that resets for no reason suggests a new key. Neither is conclusive, and either is a good reason to compare codes.
What we could not simulate
We did not attempt to compromise a production server, and we could not test clients that refuse to load modified builds. Both limits mean real world 加密聊天中间人攻击 attempts may produce different signals from the ones we recorded.
FAQ About 加密聊天中间人攻击
Does end-to-end encryption stop this?
It stops a network attacker, and it cannot stop a substituted key. That is precisely why 加密聊天中间人攻击 targets the key exchange rather than the cipher.
How often should I verify a contact?
After any device change, after a long gap, and whenever a badge resets. A quick check every few months covers the realistic cases without much effort.
Can the provider read my messages this way?
A provider that can substitute keys can in principle read your traffic. Therefore 加密聊天中间人攻击 resistance is really a question about trusting the service.
References
延伸阅读
延伸阅读:《加密聊天降级攻击实测:协议回退是怎么被利用的》。
关于加密聊天群密钥 的实测,请参阅:《加密聊天群密钥怎么管?Group Keys in E2EE Explained》。
关于聊天机器人安全 的实测,请参阅:《聊天机器人安全吗?Risks of Bots Inside a Private Chat》。
关于聊天软件第三方客户端 的实测,请参阅:《聊天软件第三方客户端安全吗?Trusting Unofficial Apps》。
延伸阅读:《聊天软件证书固定实测:伪造证书能不能骗过应用》。
评论
还没有评论,来说两句吧。
评论功能已关闭。