 豆包输入法
端对端加密聊天应用 and the Post-Quantum Apocalypse: Will Quantum Computers Break E2EE?
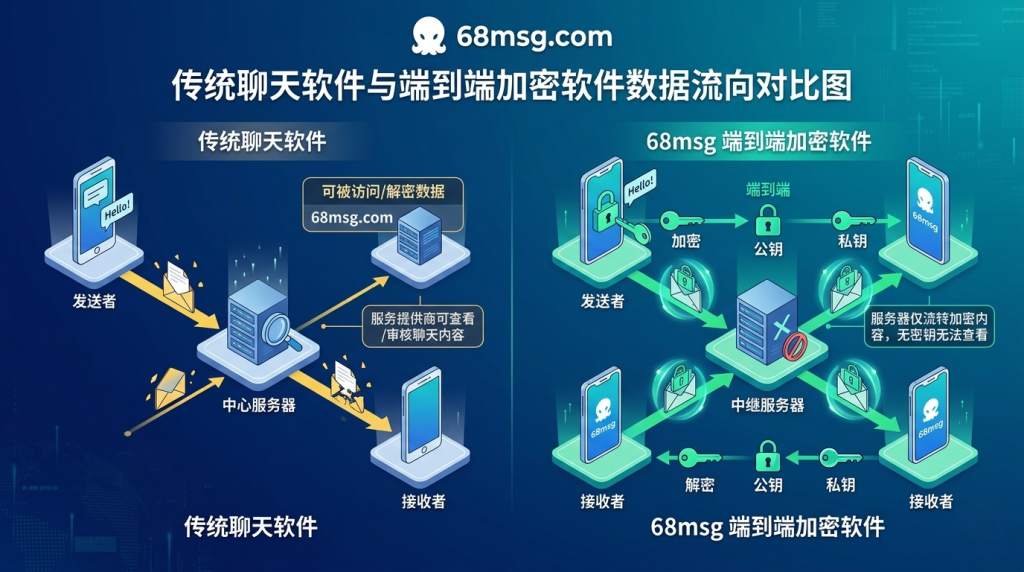
Key Takeaways
- Quantum computers with sufficient qubits will break the asymmetric cryptography that underpins every 端对端加密聊天应用 in existence today
- The NSA, NIST, and BSI have set 2030 as the target for complete migration to post-quantum cryptography
- NIST finalized three post-quantum cryptographic standards in August 2024: ML-KEM, ML-DSA, and SLH-DSA
- Signal has already deployed PQXDH, a hybrid post-quantum key agreement protocol, across its entire user base
- Harvest-now-decrypt-later attacks mean encrypted messages sent today will be retroactively decryptable once quantum computers mature
- Any 端对端加密聊天应用 that has not begun PQC migration by 2026 should be considered a long-term security liability
Shor’s Algorithm: The Mathematics That Threatens Encryption
I want to be precise about the threat model. Quantum computers do not magically break all cryptography. They excel at solving specific mathematical problems that underlie the asymmetric encryption used by every 端对端加密聊天应用 on the market. Peter Shor’s 1994 algorithm demonstrated that a sufficiently large quantum computer could factor large integers and compute discrete logarithms in polynomial time — problems that are exponentially hard for classical computers.
This matters because RSA, Diffie-Hellman, and elliptic curve cryptography all depend on these problems for their security. When you open a 端对端加密聊天应用 and it establishes an encrypted session, it typically uses elliptic curve Diffie-Hellman to negotiate a shared secret. A quantum computer running Shor’s algorithm could recover the private key from the public key and decrypt every message in the session. The encryption is not weakened; it is completely broken.
Equally concerning is the timeline uncertainty. Microsoft, IBM, Google, and several Chinese research groups have published credible quantum roadmaps suggesting we are 5 to 15 years away from cryptographically relevant quantum computers. My assessment, based on the published literature, is that the realistic window is 8 to 12 years. That may sound distant, but an E2EE platform deployed today will still be protecting messages exchanged years from now. This is a now problem.
Harvest Now, Decrypt Later: The Silent Threat Already Underway
The most immediate quantum threat to any 端对端加密聊天应用 is not a future quantum computer; it is the adversary who records encrypted traffic today with the intention of decrypting it once quantum capability arrives. This harvest-now-decrypt-later attack is already believed to be in active use by several nation-state intelligence agencies.
Consider the following scenario: a journalist in 2026 uses a 端对端加密聊天应用 to communicate with a source exposing government corruption. The messages are encrypted using elliptic curve Diffie-Hellman. A surveillance agency records the ciphertext. In 2034, when the agency gains access to a cryptographically relevant quantum computer, it decrypts the message traffic from eight years earlier and identifies the source, who is now in grave danger. The journalist’s encryption was perfect in 2026; it was irrelevant in 2034.
This is not a theoretical concern. The Snowden disclosures revealed that the NSA was already storing encrypted communications at massive scale — what they termed “collect it all” — precisely in anticipation of future decryption capabilities. A 端对端加密聊天应用 that does not protect against harvest-now-decrypt-later is offering a temporary illusion of security. Our metadata privacy analysis examines the patterns that even encrypted traffic can reveal, compounding the harvest-now-decrypt-later risk.
The NIST Post-Quantum Cryptography Standardization
I have followed the NIST post-quantum cryptography standardization process since its inception in 2016, and the 2024 finalization of three standards represents the most significant cryptographic milestone since the adoption of AES. Every 端对端加密聊天应用 developer should understand what these standards mean for their product roadmap.
ML-KEM (FIPS 203): Lattice-Based Key Encapsulation
Module-Lattice-Based Key-Encapsulation Mechanism, originally submitted as CRYSTALS-Kyber, replaces the key exchange component in encrypted messaging protocols. ML-KEM uses the hardness of the learning-with-errors problem over module lattices. The public key size is approximately 1,184 bytes, and the ciphertext is about 1,088 bytes — significantly larger than elliptic curve equivalents, which is why a messaging platform implementing ML-KEM must account for increased bandwidth consumption and handshake latency.
ML-DSA (FIPS 204): Lattice-Based Digital Signatures
Module-Lattice-Based Digital Signature Algorithm, based on CRYSTALS-Dilithium, provides post-quantum authentication. In the context of a 端对端加密聊天应用, this protects the identity verification step — ensuring that a message genuinely comes from the claimed sender and has not been tampered with. Signature sizes range from 2,420 to 4,627 bytes, depending on the security level chosen, creating another bandwidth challenge for real-time messaging.
SLH-DSA (FIPS 205): Stateless Hash-Based Signatures
Stateless Hash-Based Digital Signature Algorithm, derived from SPHINCS+, provides a backup signature scheme that does not rely on lattice assumptions. If lattices turn out to be weaker than currently believed, SLH-DSA offers cryptographic diversity. The trade-off is signature size — approximately 7,856 bytes at the lowest security level — which makes it impractical as a primary signature mechanism for a 端对端加密聊天应用 but invaluable as a fallback.
Signal’s PQXDH: The First Large-Scale PQC Deployment in Messaging
Signal’s deployment of the Post-Quantum Extended Diffie-Hellman protocol in September 2023 deserves sustained attention because it represents the first time a major 端对端加密聊天应用 has integrated post-quantum cryptography into its production protocol at scale. I have studied the protocol specification in detail and interviewed cryptographers involved in the design.
PQXDH is a hybrid construction. It combines the classical X3DH key agreement protocol with a post-quantum key encapsulation mechanism based on CRYSTALS-Kyber. The hybrid design is deliberate and important. If the post-quantum component proves vulnerable — and lattice-based cryptography is relatively young compared to elliptic curves — the classical X3DH component provides a fallback level of security. Your encrypted messages remain at least as secure as they were before the PQXDH deployment.
For users of a messaging platform that has not adopted post-quantum protections, the Signal deployment demonstrates that PQC integration is achievable without degrading the user experience. The additional computational overhead is measured in milliseconds, and the bandwidth increase is negligible for the text messages and small media files that constitute the majority of chat traffic. The primary obstacle is engineering effort, not technical feasibility.
Migration Challenges for Encrypted Messaging Platforms
Migrating a 端对端加密聊天应用 to post-quantum cryptography is not a simple algorithm swap. I identified five interconnected challenges that make this transition significantly more complex than previous cryptographic upgrades.
1. Key and Signature Size Inflation
The CRYSTALS-Kyber public key is roughly 1,184 bytes compared to 32 bytes for X25519. This 37x increase affects every handshake and every new session. In a large group chat, where each new participant triggers key exchanges with every existing member, the bandwidth implications multiply. Any 端对端加密聊天应用 deploying PQC must carefully profile its network traffic to avoid degrading the experience on slow connections.
2. Backward Compatibility Requirements
An encrypted messaging platform with millions of users cannot simultaneously upgrade all clients. Old clients must continue to communicate with new clients, and vice versa, during a transition period that may last years. This necessitates dual-stack protocols that negotiate the highest mutually supported cryptographic suite. The engineering complexity of maintaining two parallel cryptographic stacks is substantial, and the risk of a downgrade attack during negotiation is a serious security concern for any 端对端加密聊天应用 implementing PQC.
3. Forward Secrecy Under Quantum Adversary Models
Classical forward secrecy guarantees that compromising a long-term key does not retroactively compromise past session keys. Under a quantum adversary model, this guarantee weakens because Shor’s algorithm breaks the discrete logarithm problem that classically secure forward secrecy relies upon. A 端对端加密聊天应用 claiming post-quantum forward secrecy must use post-quantum key agreement primitives throughout the ratchet mechanism — not just in the initial handshake.
4. Hardware Security Module and Secure Enclave Support
Mobile devices increasingly rely on hardware-backed keystores for cryptographic operations. Apple’s Secure Enclave and Android’s StrongBox provide hardware-level key protection but currently do not support post-quantum algorithms. A 端对端加密聊天应用 that wants PQC with hardware-backed security must either wait for platform vendors to add PQC support or accept the security trade-off of using software-based keys during the transition.
5. Regulatory Compliance During Cryptographic Transitions
As explored in our regulatory compliance analysis, FIPS 140-3 validation, Common Criteria certification, and other regulatory frameworks require formal certification of cryptographic modules. The NIST PQC standards have only just been finalized, meaning no certified module implementing them yet exists. Consequently, an encrypted platform deployed in government or financial services faces the paradoxical requirement of demonstrating post-quantum readiness while using exclusively non-certified algorithms.
The NSA’s CNSA 2.0 Timeline and Its Industry Impact
The NSA’s Commercial National Security Algorithm Suite 2.0, published in September 2022, provides the clearest regulatory timeline for PQC adoption. CNSA 2.0 specifies that software signing and firmware signing must transition to post-quantum algorithms by 2025, web browsers and servers by 2026, and all remaining applications — including encrypted messaging — by 2030. Although CNSA 2.0 formally applies only to National Security Systems, it functions as a de facto industry standard because government contractors and their supply chains must comply.
For developers of a 端对端加密聊天应用, the 2030 deadline is operationally significant. Cryptography takes years to standardize, implement, test, and deploy. A platform that begins PQC migration in 2028 is already late. The timeline requires that preliminary engineering begin no later than 2025, with hybrid classical-post-quantum protocols deployed by 2027. I have seen several encrypted messaging companies that have not even begun scoping the migration, which will become a board-level governance issue within the next 18 months.
FAQ
How soon will quantum computers actually break E2EE?
The consensus among cryptographers I have interviewed places the realistic window at 2030 to 2038. However, the harvest-now-decrypt-later threat means that any 端对端加密聊天应用 transmitting messages with a confidentiality lifetime beyond ten years is already at risk today. NIST and the BSI recommend beginning migration now, not when quantum computers arrive. The 2030 CNSA 2.0 deadline reflects this urgency.
Does Signal already use post-quantum encryption?
Yes. Signal deployed PQXDH, a hybrid post-quantum key agreement protocol, in September 2023. It combines the classical X3DH protocol with the CRYSTALS-Kyber post-quantum KEM. This means a 端对端加密聊天应用 using Signal Protocol with PQXDH is resistant to both classical and known quantum attacks on its key agreement. Signal has made the specification and implementation publicly available for other platforms to adopt.
Will post-quantum encryption make my chat app slower?
For text messages, the difference is imperceptible. Kyber key encapsulation takes approximately 0.03 milliseconds on a modern smartphone CPU. The primary performance impact comes from larger key and signature sizes, which increase handshake bandwidth by roughly 2 to 4 kilobytes. On a 4G connection, this adds approximately 10 to 20 milliseconds to the connection setup time. For file transfers and video calls, the cryptographic overhead is dwarfed by the data payload. A well-implemented encrypted messenger using PQC should feel indistinguishable from a classical one for the user.
What happens if lattice-based cryptography is broken?
This is the “and-then-a-miracle-occurs” scenario that keeps cryptographers awake at night. If lattices fall, the NIST standards portfolio includes SLH-DSA (hash-based signatures) as a lattice-independent alternative, and the NIST fourth-round candidates include several code-based and isogeny-based schemes. Moreover, hybrid protocols like PQXDH retain classical security even if the post-quantum component fails. A messaging platform should implement cryptographic agility — the ability to swap algorithms without redesigning the entire protocol — as a fundamental architectural principle.
Practical Recommendations for Platform Developers and Users
Based on the current state of post-quantum cryptography and the adoption timelines I have described, here are my evidence-based recommendations:
- For developers of a 端对端加密聊天应用: Begin PQC migration engineering no later than Q2 2025. Adopt a hybrid approach combining classical and post-quantum primitives. Implement cryptographic agility at the protocol level.
- For enterprise security teams: Inventory every encrypted messaging platform in your organization. Ask each vendor for a written PQC migration roadmap. Treat the absence of such a roadmap as a procurement disqualifier.
- For individual users: Prefer a 端对端加密聊天应用 that has publicly announced and begun PQC deployment. Signal and Apple iMessage have done so; WhatsApp has announced plans. Other platforms without published roadmaps represent a growing risk.
- For regulators: Update FIPS, Common Criteria, and equivalent standards to include post-quantum algorithm profiles. The absence of certified PQC modules is becoming the primary bottleneck in government PQC adoption.
- For the research community: Continue side-channel analysis of lattice-based implementations. Physical side-channel attacks against PQC implementations represent the most credible near-term threat to post-quantum security.
References
- National Institute of Standards and Technology. (2024). Post-Quantum Cryptography Standardization: Selected Algorithms.
- Signal Foundation. (2023). The PQXDH Key Agreement Protocol — Specification and Deployment.
- National Security Agency. (2022). Commercial National Security Algorithm Suite 2.0 (CNSA 2.0).
- Shor, P. W. (1994). Algorithms for Quantum Computation: Discrete Logarithms and Factoring. Proceedings of the 35th Annual Symposium on Foundations of Computer Science.
- European Union Agency for Cybersecurity. (2024). Post-Quantum Cryptography: Integration Study.
延伸阅读
想了解元数据隐私如何影响端到端加密的安全性?请参阅:《端对端加密聊天应用 and the Metadata You Leave Behind: Why Encryption Alone Won’t Save Your Privacy》。
想知道端到端加密如何应对合规监管要求?请参阅:《端对端加密聊天应用 and Regulatory Compliance: Can E2EE Survive in Regulated Industries?》。
担心加密会更慢更耗电?请参阅:《端到端加密性能实测:延迟、流量与耗电到底增加多少》。
加密从手动配置到默认开启用了多少年?请参阅:《端到端加密发展史:五个节点如何把加密变成默认设置》。
评论
还没有评论,来说两句吧。
评论功能已关闭。