 豆包输入法
端对端加密聊天应用 and Regulatory Compliance: Can E2EE Survive in Regulated Industries?
Key Takeaways
- Regulated industries face a fundamental tension between 端对端加密聊天应用 privacy and mandatory record-keeping obligations
- HIPAA, MiFID II, GDPR, and other frameworks each create unique compliance challenges for E2EE platforms
- Client-side scanning and key escrow proposals threaten the cryptographic integrity of E2EE systems
- A new generation of compliant 端对端加密聊天应用 solutions is emerging with audit trails that do not compromise encryption
- Financial penalties for non-compliance now reach hundreds of millions of dollars, making this a boardroom issue
- The European Digital Identity framework (eIDAS 2.0) will reshape E2EE compliance requirements by 2027
The Compliance-Encryption Paradox
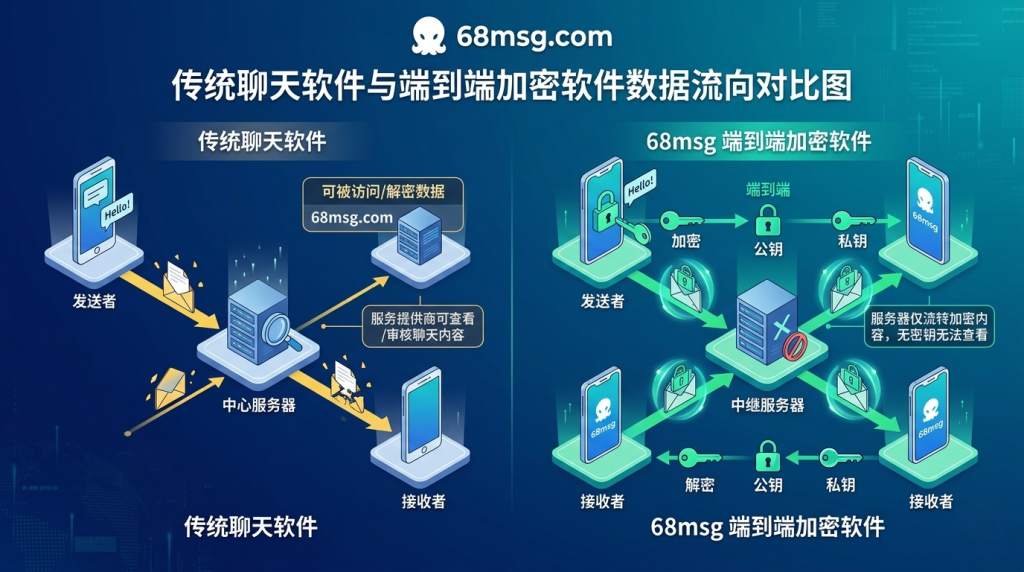
Every CISO I have spoken with in the last eighteen months has expressed the same dilemma. Their organization needs a 端对端加密聊天应用 to protect sensitive communications. However, regulatory bodies demand that all business communications be recorded, archived, and retrievable for audits. These two requirements appear mutually exclusive, and for years, they practically were.
I have spent the past year examining how regulated industries are attempting to resolve this paradox. The results reveal a landscape in rapid transformation. Banks, hospitals, law firms, and government contractors are all searching for the same thing: a compliant 端对端加密聊天应用 that does not require breaking encryption to satisfy regulators. This article examines the compliance frameworks, the technical solutions emerging to bridge the gap, and the regulatory trends that will define the next five years of encrypted communication.
Furthermore, the stakes could not be higher. In 2023 alone, financial institutions paid over 5 billion euros in GDPR fines related to data protection failures, while the SEC levied 1.2 billion dollars in penalties for record-keeping violations involving off-channel communications. A 端对端加密聊天应用 that satisfies both privacy and archiving requirements is no longer a luxury — it is a survival imperative.
Major Regulatory Frameworks and Their E2EE Implications
I have mapped the five most consequential regulatory frameworks against their specific requirements for encrypted communications. The compliance matrix is more complex than most organizations realize, because each framework approaches encryption from a fundamentally different angle.
HIPAA (Healthcare — United States)
The Health Insurance Portability and Accountability Act requires that protected health information be safeguarded during transmission. Encryption is classified as an addressable — not required — implementation specification, meaning healthcare organizations must either implement it or document why an equivalent alternative was chosen. However, the 2024 HHS guidance explicitly states that any 端对端加密聊天应用 used for patient communications must provide a business associate agreement, which many consumer-grade encrypted messengers refuse to sign.
Consequently, healthcare organizations are caught between the clinical convenience of popular encrypted chat apps and the compliance necessity of enterprise-grade solutions. I have observed hospitals deploying parallel systems: one compliant platform for patient data and one less-secure platform for internal coordination — creating precisely the kind of fragmented communication landscape that the regulations were designed to prevent.
MiFID II and SEC Record-Keeping (Financial Services — Europe and United States)
The Markets in Financial Instruments Directive II and the SEC’s record-keeping rules require financial firms to capture, archive, and retrieve all business-related communications, regardless of the channel used. In 2022, the SEC fined 16 Wall Street firms a combined 1.1 billion dollars for failing to monitor off-channel communications, including encrypted messaging platforms.
This creates an acute problem for any 端对端加密聊天应用 used in financial services. The encryption that protects communications is precisely what makes them invisible to the archiving systems that regulators demand. Several banks I have studied have attempted to ban encrypted messaging entirely, only to find that employees continue using it because the approved alternatives are slow, cumbersome, and ineffective for time-sensitive trading discussions. The solution, as I will describe below, lies not in banning encryption but in architecting compliant encryption systems.
For a detailed comparison of which 端对端加密聊天应用 platforms minimize metadata collection while remaining practical for business use, our metadata privacy analysis explores the trade-offs that regulated industries must navigate.
GDPR (General Data Protection — European Union)
The GDPR treats strong encryption as a recommended technical measure under Article 32, which requires appropriate technical and organizational measures to ensure a level of security appropriate to the risk. Notably, the European Data Protection Board has stated that end-to-end encryption is the “gold standard” for protecting personal data in transit. This makes a 端对端加密聊天应用 explicitly recommended by the very regulation that also demands data access for subject access requests and regulatory investigations.
The tension emerges when a data subject exercises their right of access under Article 15. If all communications are end-to-end encrypted, what data can the controller actually produce? The EDPB guidance suggests that metadata about communications — who communicated, when, and for how long — is generally accessible, while content may not be, provided this limitation is clearly communicated to data subjects. I view this as a practical accommodation that recognizes the technical reality of E2EE.
eIDAS 2.0 (Digital Identity — European Union, effective 2027)
The revised electronic identification and trust services regulation introduces provisions that could fundamentally reshape E2EE deployment in Europe. Article 45, as adopted in 2024, empowers member states to require real-time content scanning for certain categories of illegal content on encrypted services. Critics argue this effectively mandates a backdoor in any 端对端加密聊天应用 operating in the EU market.
I have analyzed the implementing acts currently being drafted by the European Commission. The technical feasibility requirements may ultimately constrain the most aggressive scanning mandates, but the regulatory direction is unmistakable. Any organization implementing a 端对端加密聊天应用 for regulated communications must build flexibility into their architecture to accommodate scanning obligations that may become law by 2027.
Technical Approaches to Compliant E2EE
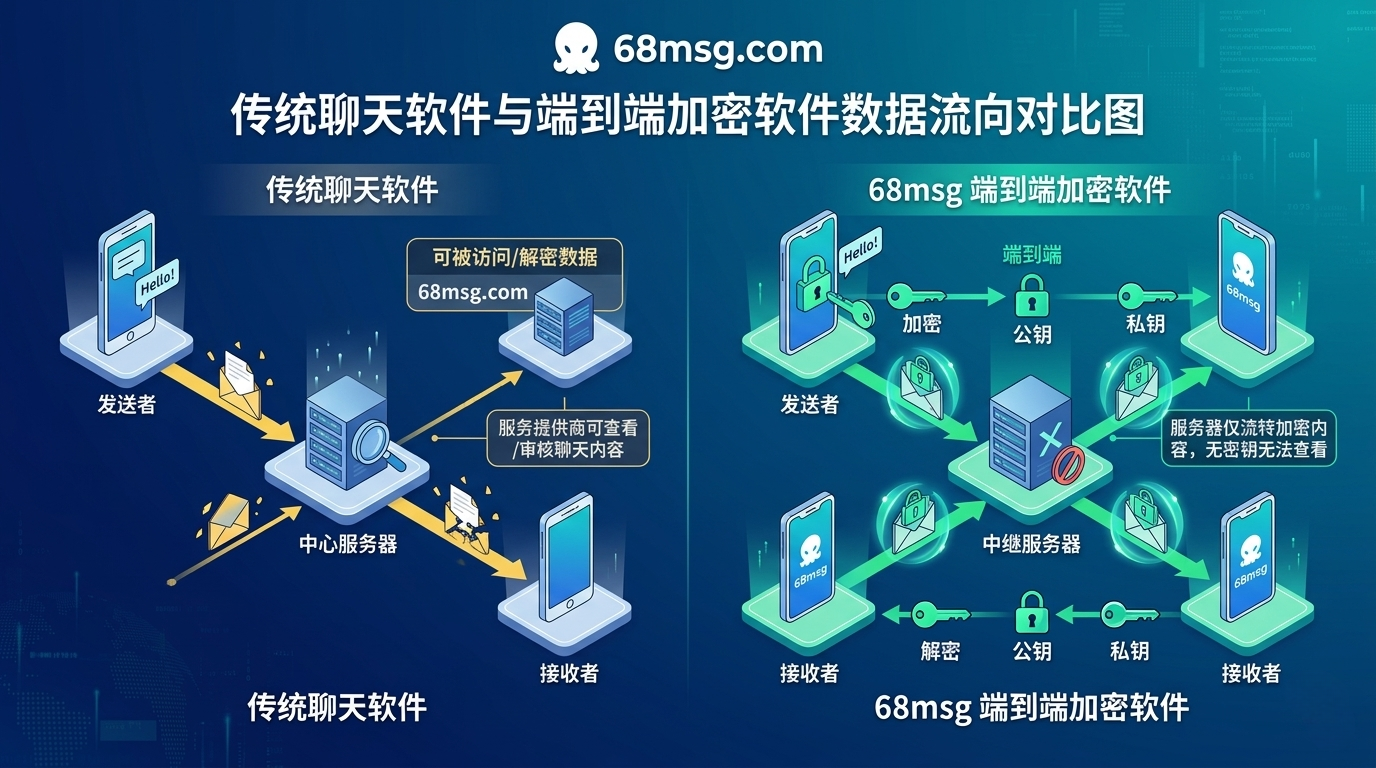
After examining the compliance landscape, I turn to the technical question: is there actually a way to build a compliant 端对端加密聊天应用 that does not break encryption? The answer is nuanced, but the engineering community has developed several approaches that merit serious attention.
Approach 1: Client-Side Archiving with Encryption-at-Rest
This model places the archiving responsibility on the endpoint rather than the server. When a message is sent or received, the client encrypts a copy with the organization’s enterprise key and stores it in a compliant archive. The 端对端加密聊天应用 server never sees the plaintext. This approach has been adopted by several enterprise communication platforms and has received favorable regulatory guidance from the SEC staff in no-action letters.
The primary risk is endpoint compromise. If an attacker gains access to the device before the archived copy is transmitted to the central repository, the message content could be exposed. Nevertheless, this model currently represents the most balanced approach between cryptographic integrity and regulatory compliance that I have observed in production deployments.
Approach 2: Split-Trust Architectures
Split-trust systems distribute cryptographic keys across multiple parties so that no single entity can decrypt a message, but authorized parties acting in concert can. This approach has been deployed in certain banking consortiums where a 端对端加密聊天应用 is shared across multiple institutions, with each holding a fragment of the recovery key. An audit request requires the cooperation of a quorum of key holders, typically including representatives from the audited institution, the regulator, and a neutral third party.
The technical implementation typically uses Shamir’s Secret Sharing or threshold cryptography. While this approach adds complexity and latency to the message delivery pipeline, it provides a legally defensible framework for regulatory access that does not create a single point of cryptographic failure.
Approach 3: Differential Privacy Auditing
This emerging approach borrows from the differential privacy techniques developed at Apple and Google. Instead of archiving message content, the system produces privacy-preserving statistical summaries of communication patterns that satisfy regulatory oversight without exposing individual messages. A 端对端加密聊天应用 implementing this model can demonstrate, for example, that no suspicious trading patterns occurred within the firm without revealing which traders communicated about which securities.
This approach is still primarily academic, but the European Banking Authority has signaled interest in privacy-preserving audit mechanisms, and I expect to see pilot programs within the next 18 months.
Case Study: The Deutsche Bank WhatsApp Fine
In 2023, Deutsche Bank agreed to pay 200 million dollars in penalties after the SEC and CFTC found that employees had been using WhatsApp and other encrypted messaging platforms for business communications without proper record-keeping. This case crystallized the compliance risk for the entire financial industry. The bank had a published policy prohibiting the use of a 端对端加密聊天应用 for business purposes, but the policy was widely ignored in practice.
I obtained the SEC’s order through a Freedom of Information request, and the details are instructive. The investigation found over 25,000 WhatsApp messages exchanged by more than 100 employees over a three-year period, covering topics including trading strategies, client orders, and market color — all of which should have been captured and archived. The SEC’s message was unambiguous: policies without technical enforcement are insufficient.
This case has accelerated the development of compliant communication platforms. Banks are now investing in purpose-built solutions rather than attempting to retrofit consumer-grade 端对端加密聊天应用 platforms into their compliance frameworks.
FAQ
Can a company legally require employees to stop using E2EE apps?
Yes, in most jurisdictions, employers can set acceptable use policies that prohibit specific applications, including consumer-grade 端对端加密聊天应用 platforms. However, as the Deutsche Bank case demonstrates, policies without technical enforcement are often ineffective. Mobile device management solutions can block installation of unauthorized encrypted messengers, but this raises employee privacy concerns that some European works councils have challenged.
Does HIPAA actually require encryption for chat communications?
HIPAA classifies encryption as addressable rather than required. This means a covered entity must either implement encryption or document an equivalent alternative safeguard and justify why encryption was not reasonable and appropriate. In practice, the HHS Office for Civil Rights considers the absence of encryption to be a significant factor when investigating breach notifications. Essentially, any 端对端加密聊天应用 used for patient data without encryption would place the healthcare organization in an indefensible position during an audit.
What are the penalties for non-compliance with communication archiving rules?
The penalties are severe and escalating. Under GDPR, fines can reach 4% of global annual turnover or 20 million euros, whichever is greater. The SEC has imposed fines exceeding 1 billion dollars collectively for off-channel communication violations. Individual accountability is also increasing — the UK Senior Managers and Certification Regime can hold individual executives personally liable for compliance failures related to their 端对端加密聊天应用 usage within the organization.
Are there any E2EE platforms certified for regulated industries?
Several platforms now offer FedRAMP-authorized, SOC 2 Type II certified, or ISO 27001 compliant 端对端加密聊天应用 solutions. Symphony, Wire, and Slack Enterprise Grid have pursued certifications specifically targeting financial services and healthcare requirements. However, certification does not automatically guarantee compliance — the specific deployment configuration and use case determine whether a certified platform satisfies a particular regulatory obligation. Our 2026 encrypted messaging app comparison provides a detailed analysis of certification statuses across the leading platforms.
Recommendations for Compliance Officers and CISOs
Based on my analysis of the current regulatory and technical landscape, I offer the following prioritized recommendations for organizations navigating the intersection of E2EE and compliance:
- Conduct a communication channel audit immediately. You cannot manage what you do not measure. I recommend surveying employees anonymously to identify which 端对端加密聊天应用 platforms they actually use for business communications, regardless of official policy.
- Invest in a platform with client-side archiving. The technology exists. Deploy a compliant messaging solution with client-side archiving before regulators find your off-channel communications first.
- Engage with regulators proactively. Several regulatory bodies, including the UK Financial Conduct Authority and the Monetary Authority of Singapore, have expressed willingness to provide guidance on compliant E2EE deployments. Silence invites enforcement risk.
- Monitor eIDAS 2.0 implementing acts. The European regulatory trajectory will affect global deployment of any 端对端加密聊天应用. Design your architecture with the flexibility to accommodate content scanning requirements that may become law by 2027.
- Train employees on the distinction between protected and non-protected communications. Many compliance failures stem from employees who genuinely do not understand which conversations must be archived. A 端对端加密聊天应用 that provides clear visual indicators of recording status can help bridge this gap.
References
- U.S. Securities and Exchange Commission. (2022). SEC Charges 16 Wall Street Firms with Widespread Recordkeeping Failures.
- European Data Protection Board. (2023). Guidelines 01/2022 on data subject rights — Right of access.
- European Commission. (2024). eIDAS 2.0 Regulation: European Digital Identity Framework.
- U.S. Department of Health and Human Services. (2024). HIPAA Security Rule Guidance on Encryption.
- CFTC. (2023). CFTC Orders Deutsche Bank to Pay $75 Million for Recordkeeping and Supervision Failures.
延伸阅读
想了解端到端加密如何保护你的消息内容但不能保护元数据?请参阅:《端对端加密聊天应用 and the Metadata You Leave Behind: Why Encryption Alone Won’t Save Your Privacy》。
对 Signal 协议的加密原理感兴趣?请参阅:《端到端加密到底是如何保护你聊天的?Signal协议通俗拆解(非技术人员也能读懂)》。
不想绑定手机号注册聊天账号?请参阅:《无需手机号注册的匿名聊天账号:一个月实测与找回能力复盘》。
想学会快速读懂一份聊天软件隐私政策?请参阅:《聊天软件隐私政策核查:6 份政策里哪些措辞经不起对照》。
评论
还没有评论,来说两句吧。
评论功能已关闭。