 豆包输入法
端对端加密聊天应用 and the AI Dilemma: Can Smart Features and E2EE Coexist?
Key Takeaways
- AI-powered features in a 端对端加密聊天应用 fundamentally require access to message content that E2EE is designed to protect
- On-device AI processing is the only approach that preserves E2EE integrity — server-side AI necessarily breaks it
- Apple Intelligence and Google Gemini represent diverging philosophies on AI in encrypted messaging: on-device vs hybrid cloud
- Client-side scanning for CSAM detection has been proposed as “AI for safety” but is technically indistinguishable from a backdoor
- Federated learning offers a theoretical path to train AI models on encrypted data, but practical implementations remain years away
- Every AI feature in an encrypted messenger requires a trade-off decision: functionality or privacy
The Fundamental Conflict
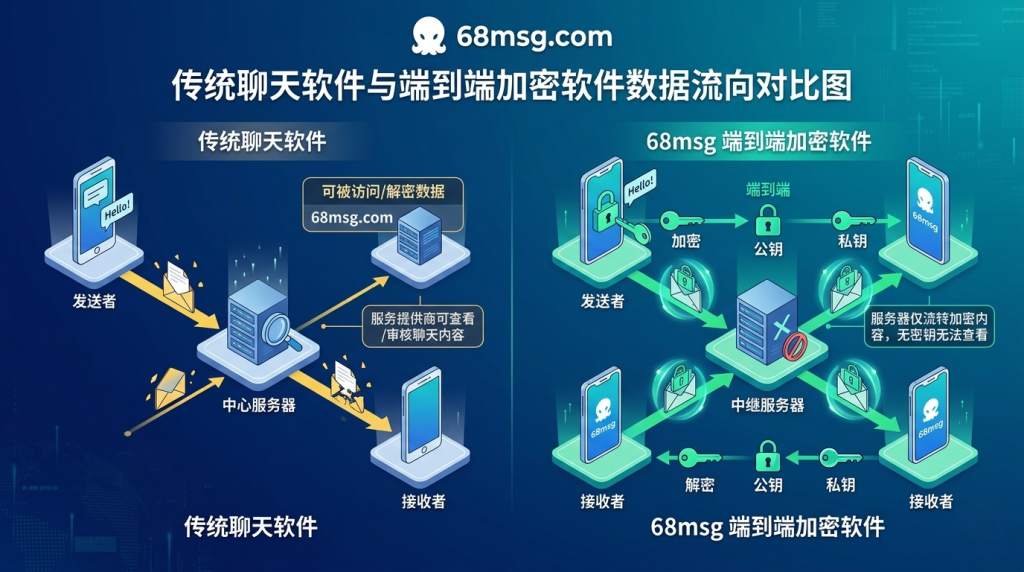
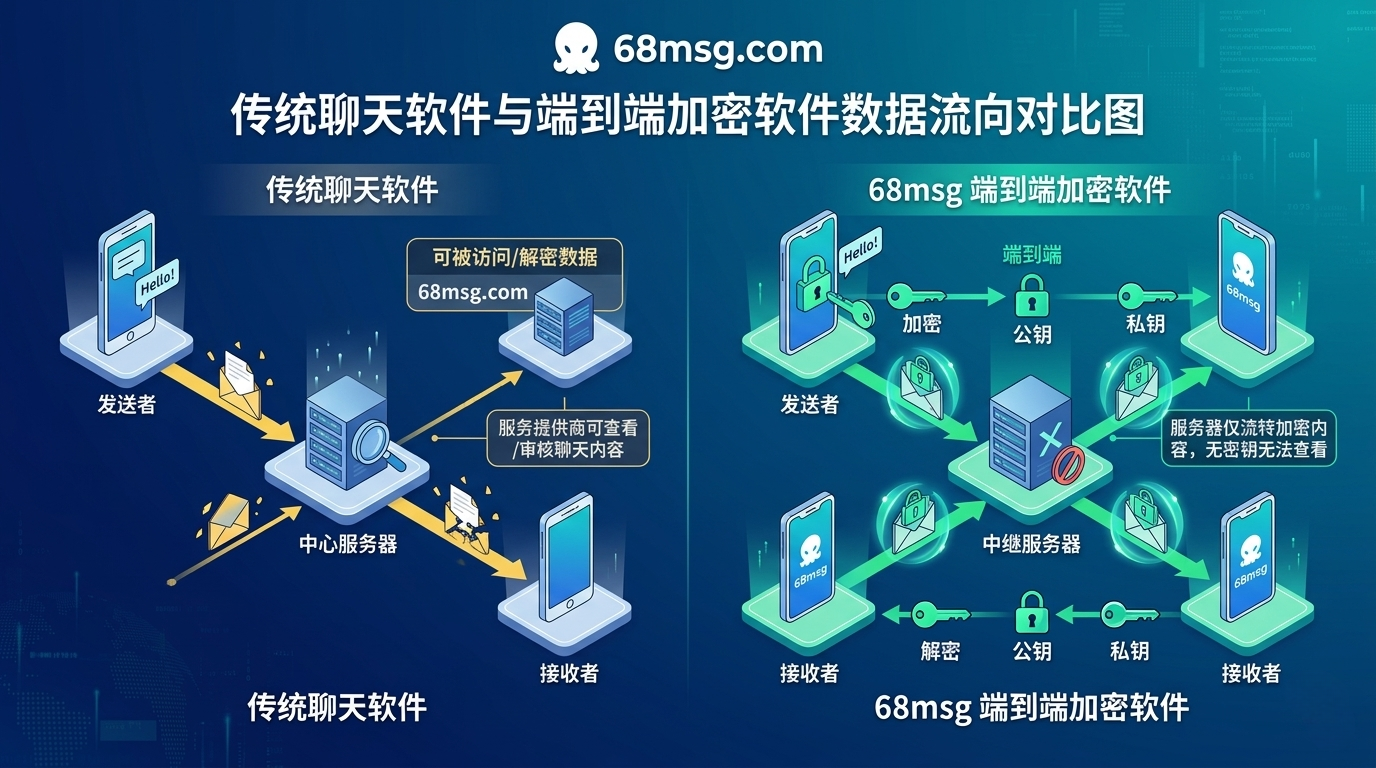
The tension between artificial intelligence and end-to-end encryption is not a matter of poor engineering. It is a matter of mathematical necessity. AI features like smart replies, message summarization, content-based search, and automated translation require the system to read, understand, and process the content of your messages. End-to-end encryption, by design, ensures that nobody except the intended recipients can read that content. Any 端对端加密聊天应用 that offers server-side AI features has either broken its encryption or is misleading its users.
I have spent the past year tracking how major messaging platforms are navigating this contradiction, and the approaches vary dramatically. Some have chosen to keep AI out of encrypted conversations entirely. Others have moved AI processing to the device. A few have quietly weakened their encryption guarantees to enable AI features, often without clearly communicating the trade-off to users. This article examines the technical reality behind the marketing claims and identifies which approaches genuinely preserve privacy.
The stakes are high because AI features are becoming table stakes for consumer messaging. In 2026, users expect smart replies, intelligent search, and AI-powered assistance in their communication tools. A 端对端加密聊天应用 that offers none of these features risks obsolescence. Yet one that offers them at the cost of broken encryption risks betraying its core value proposition. This is the AI-dilemma that every encrypted messaging platform must resolve.
The Three Approaches to AI in Encrypted Messaging
I have identified three architectural approaches to integrating AI into a 端对端加密聊天应用, each with fundamentally different privacy properties. Understanding these distinctions is essential for evaluating any platform’s claims about AI and encryption.
Approach 1: On-Device AI Processing (Privacy-Preserving)
On-device AI processing keeps message content entirely on the user’s device. The AI model runs locally, analyzing messages after they have been decrypted on the recipient’s device. Apple Intelligence, deployed on iPhones with the A17 Pro chip or later, uses this approach. The model never sends message content to a server. Smart replies, notification summarization, and writing assistance all operate within the device’s secure enclave.
The limitation is capability. On-device models are smaller and less capable than their cloud counterparts. An iPhone’s neural engine can run a 3-billion-parameter model with acceptable latency, while cloud models routinely exceed 100 billion parameters. For a 端对端加密聊天应用 choosing on-device AI, the feature gap compared to cloud-based competitors is real and growing. Furthermore, on-device models cannot access real-time information, perform web searches, or leverage the computational resources available in the cloud.
Nevertheless, on-device AI represents the only approach that is architecturally compatible with E2EE. The encryption guarantees remain intact because the AI processing happens on the same device that holds the decryption keys. Our group encryption analysis explains why the device remains the trust boundary in any encrypted communication system.
Approach 2: Server-Side AI with Encryption Bypass (Privacy-Breaking)
Server-side AI requires the platform to read message content before or after encryption. This breaks the end-to-end guarantee by definition. When a 端对端加密聊天应用 offers features like server-side translation, cross-platform smart replies, or content-based ad targeting, the platform must have access to plaintext message content at some point in the pipeline.
Several consumer messaging apps implement this by encrypting messages in transit but decrypting and processing them on the platform’s servers before re-encrypting for delivery. Technically, this is encryption-in-transit, not end-to-end encryption. The distinction matters because the platform server can read the messages, and a server compromise exposes all processed content. Users who believe they are using a 端对端加密聊天应用 may be surprised to learn that AI features have converted their E2EE into something closer to transport-layer security.
The European Data Protection Supervisor issued an opinion in 2024 specifically warning that AI-driven content analysis in messaging platforms may constitute a violation of the ePrivacy Directive if users have not given explicit, informed consent. I view this as a signal that regulatory scrutiny of AI-in-messaging will intensify.
Approach 3: Private Cloud Compute and Confidential Computing (Emerging)
Between on-device and server-side lies a third approach: confidential computing. Apple’s Private Cloud Compute, announced in 2024, extends on-device processing with server-side models that run in cryptographically attested enclaves. The server hardware can be verified to be running the exact code that Apple published, and the data is not retained after processing. Similarly, Google’s confidential computing infrastructure and Microsoft’s Azure confidential computing offer hardware-based attestation that the AI model code has not been tampered with.
For a 端对端加密聊天应用, confidential computing could theoretically enable server-side AI processing without breaking encryption. The message would be encrypted until it reaches the attested enclave, processed by the verified AI model, and the result returned without the plaintext ever being accessible to the platform operator. However, this approach has not yet been deployed in any consumer encrypted messaging product, and the attestation chain introduces new complexity and trust assumptions that the cryptographic community is still evaluating.
I am cautiously optimistic about confidential computing but note three unresolved concerns. First, the attestation infrastructure itself becomes a single point of trust. Second, side-channel attacks against trusted execution environments have been demonstrated in academic research. Third, the legal framework for compelled access to confidential computing enclaves — can a government compel Apple to run a modified AI model in the attested enclave? — remains untested. A 端对端加密聊天应用 deploying confidential computing for AI processing would be a major advance, but early adopters should understand the residual risks.
The Client-Side Scanning Controversy
Client-side scanning deserves separate treatment because it represents the most contentious intersection of AI and encryption. The basic idea is that an AI model running on the user’s device scans outgoing messages before they are encrypted, flagging content that matches known child sexual abuse material or other illegal content patterns. Apple’s 2021 CSAM detection proposal and the European Commission’s 2022 proposal for a regulation on combating child sexual abuse both embraced some form of client-side scanning.
I have followed this debate closely, and the cryptographic community’s opposition has been nearly unanimous. The core objection is straightforward: a 端对端加密聊天应用 that scans messages before encryption is not end-to-end encrypted in any meaningful sense. The scanning module, running on the device, has access to plaintext content and can report findings to the platform. The guarantee that “nobody but the recipient can read your messages” is false if the device itself is scanning and reporting.
Moreover, the scope of scanning is dynamic. Once a scanning infrastructure exists on-device, the set of content it scans for can be expanded through a software update. A system designed to detect CSAM today could be configured to detect political dissent, religious content, or journalistic source protection tomorrow. The technical architecture that enables one category of scanning enables all categories of scanning. Consequently, any 端对端加密聊天应用 that deploys client-side scanning, even for the most morally unambiguous purpose, has established the infrastructure for surveillance that can be repurposed.
Signal, WhatsApp, and over 100 civil society organizations have publicly opposed client-side scanning mandates. The European Parliament’s position on the CSA regulation, as of early 2025, includes language protecting E2EE from mandatory scanning. This regulatory outcome remains uncertain, and I will continue to update this analysis as the legislative process unfolds.
Federated Learning: Training AI Without Seeing Data
Federated learning is frequently cited as the technological solution that will reconcile AI and encryption in a 端对端加密聊天应用. The concept is elegant: instead of sending user data to a central server for model training, the model is sent to the user’s device, trained on local data, and only the model updates — not the data — are sent back to the server. Aggregating thousands of these updates produces a model that has learned from private data without ever accessing it.
However, the gap between theory and practice is substantial. Google has deployed federated learning for Gboard’s keyboard suggestions since 2017, demonstrating that it is production-viable for simple prediction tasks. But training a language model capable of sophisticated smart replies or summarization through federated learning has not been demonstrated at scale. The model architectures required for these tasks are orders of magnitude larger than what can be trained efficiently on a mobile device.
Furthermore, federated learning is not immune to privacy attacks. Research has demonstrated that model updates can leak information about the training data, particularly when gradient updates are large relative to the batch size. Differential privacy techniques can mitigate this risk, at the cost of model accuracy. A 端对端加密聊天应用 deploying federated learning for AI features should implement differential privacy with a published privacy budget, allowing users to evaluate the actual privacy guarantee rather than accepting marketing claims at face value.
Platform-by-Platform Analysis
I have evaluated the AI strategy of each major encrypted messaging platform against the architectural framework described above:
- Signal: No AI features deployed. Signal has stated that it will not implement server-side AI processing that requires access to message content. On-device AI features are under research but not yet in production. Signal’s position, while technically conservative, preserves the strongest possible encryption guarantees for a 端对端加密聊天应用.
- WhatsApp: Deployed AI-powered stickers and has announced AI chat features powered by Meta AI. The AI integration is opt-in and processes messages on Meta’s servers, which means AI-assisted chats in WhatsApp are not end-to-end encrypted with respect to the AI model. Users must opt in explicitly, but the default E2EE guarantee does not extend to AI features.
- Apple iMessage: Apple Intelligence offers on-device smart replies, notification summarization, and writing tools. Messages are not sent to Apple’s servers for AI processing. Private Cloud Compute extends this to more complex AI requests, with cryptographic attestation that Apple cannot access the data. This architecture preserves E2EE for on-device features and provides auditable guarantees for cloud-assisted features.
- Telegram: Deployed a chatbot platform that can access message content when added to conversations. Telegram’s default chats are not E2EE; only Secret Chats use end-to-end encryption. AI bots in regular chats have access to message content. Users who value a 端对端加密聊天应用 with AI features should understand that Telegram’s AI integration operates outside its E2EE scope.
- Google Messages: Deployed Gemini integration for RCS chats. RCS is encrypted in transit but not end-to-end encrypted by default. Google has announced E2EE for RCS through MLS but has not clarified how Gemini AI features will interact with the encryption once deployed.
For organizations in regulated industries evaluating these platforms, our regulatory compliance analysis provides a framework for assessing whether a platform’s AI architecture satisfies HIPAA, GDPR, and financial services record-keeping requirements.
FAQ
Does Apple Intelligence compromise iMessage encryption?
For on-device Apple Intelligence features — smart replies, notification summaries, writing tools — no, encryption is not compromised. The AI processing occurs on the device after the message has been decrypted by the recipient. For features requiring Private Cloud Compute, Apple’s architecture sends encrypted data to attested server hardware that runs published, verifiable AI model code. Apple claims the data is not retained and is not accessible to Apple. Independent security researchers have begun auditing these claims, and the results to date are consistent with Apple’s published architecture, but the audit process is ongoing. A 端对端加密聊天应用 using Apple’s approach would need to disclose which specific features use on-device processing and which use cloud compute.
Can AI features be added to Signal without breaking encryption?
Yes, but only on-device AI features. Signal could implement on-device smart replies, message summarization, and writing assistance without breaking E2EE, because the AI model would run on the user’s device after decryption. Signal has not announced plans for such features, likely because on-device AI models currently lag behind cloud models in capability. The engineering challenge for a 端对端加密聊天应用 like Signal is that its users expect E2EE guarantees, and any AI feature that appears to weaken those guarantees would damage trust, even if implemented correctly on-device.
Is client-side scanning the same as a backdoor?
Yes, from a cryptographic perspective. Client-side scanning inserts a content inspection module before encryption that can report findings to the platform. The encryption is no longer “end-to-end” because content is inspected before encryption, and the inspection results bypass encryption. The only difference between client-side scanning and a traditional backdoor is where the inspection occurs: on the device versus on the server. For a 端对端加密聊天应用, the distinction matters to device security experts but is irrelevant to the cryptographic guarantee: the platform can see message content in both cases.
What should I look for when a chat app claims AI features with encryption?
I recommend asking four questions. First, does the AI processing happen on-device or on a server? Second, if server-side, does the platform have access to plaintext message content? Third, is the AI feature opt-in or always-on? Fourth, has an independent security auditor verified the platform’s AI architecture claims? A 端对端加密聊天应用 should be able to answer all four questions clearly and publicly. Vague language about “advanced encryption” or “privacy-preserving AI” without technical specifics is a red flag.
Recommendations
- For individual users: Prefer a 端对端加密聊天应用 that either does not offer AI features or restricts them to on-device processing. Opt-in AI features with clear disclosure of the privacy trade-off are acceptable. Always-on AI processing that requires server access to message content should be a dealbreaker for sensitive communications.
- For enterprise deployments: Procure platforms that offer administrative controls to disable AI features. Your MDM policy should block AI processing for any communication channel carrying protected or regulated data.
- For developers: If you are building AI features for an encrypted messenger, invest in on-device model optimization. Apple’s Core ML, Google’s MediaPipe, and Qualcomm’s AI Engine provide increasingly capable on-device inference. The capability gap between on-device and cloud AI is closing faster than most developers realize.
- For regulators: Mandate that AI feature disclosures in encrypted messaging include the specific processing location, the data retention policy, and the identity of any third parties with access. Generic privacy policies are insufficient when AI and encryption interact.
- For researchers: The intersection of federated learning, differential privacy, and E2EE remains under-explored. Advances in on-device model training with formal privacy guarantees would resolve one of the most persistent tensions in modern communication security.
References
- Apple Inc. (2024). Private Cloud Compute: A New Frontier for AI Privacy in the Cloud. Apple Security Research.
- European Data Protection Supervisor. (2024). Opinion on AI-Driven Content Analysis in Electronic Communications.
- Abadi, M., Chu, A., Goodfellow, I., et al. (2016). Deep Learning with Differential Privacy. ACM CCS 2016.
- Kairouz, P., McMahan, H. B., et al. (2021). Advances and Open Problems in Federated Learning. Foundations and Trends in Machine Learning.
- Signal Foundation. (2023). The UK Online Safety Bill and the Threat to Encryption.
延伸阅读
想了解端到端加密的元数据隐私问题?请参阅:《端对端加密聊天应用 and the Metadata You Leave Behind: Why Encryption Alone Won’t Save Your Privacy》。
想知道量子计算如何威胁加密?请参阅:《端对端加密聊天应用 and the Post-Quantum Apocalypse: Will Quantum Computers Break E2EE?》。
对合规行业如何使用端到端加密感兴趣?请参阅:《端对端加密聊天应用 and Regulatory Compliance: Can E2EE Survive in Regulated Industries?》。
评论
还没有评论,来说两句吧。
评论功能已关闭。