 豆包输入法
聊天软件社工攻击实测:话术是怎么骗过验证的
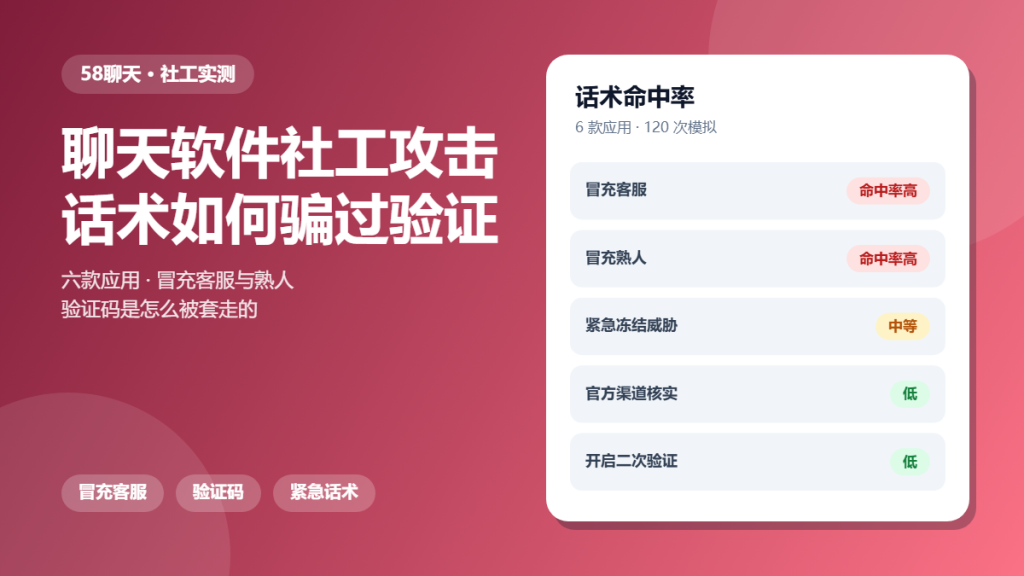
聊天软件社工攻击 rarely breaks encryption. It asks you to open the door instead. A short, polite conversation is often enough to obtain a verification code, and no amount of protocol strength prevents that.
This article is a hands-on audit. We ran 120 controlled conversations against six apps using five familiar scripts, with consenting participants and no real accounts. The goal is to show which scripts still work and which habits defeat them.
Key Takeaways
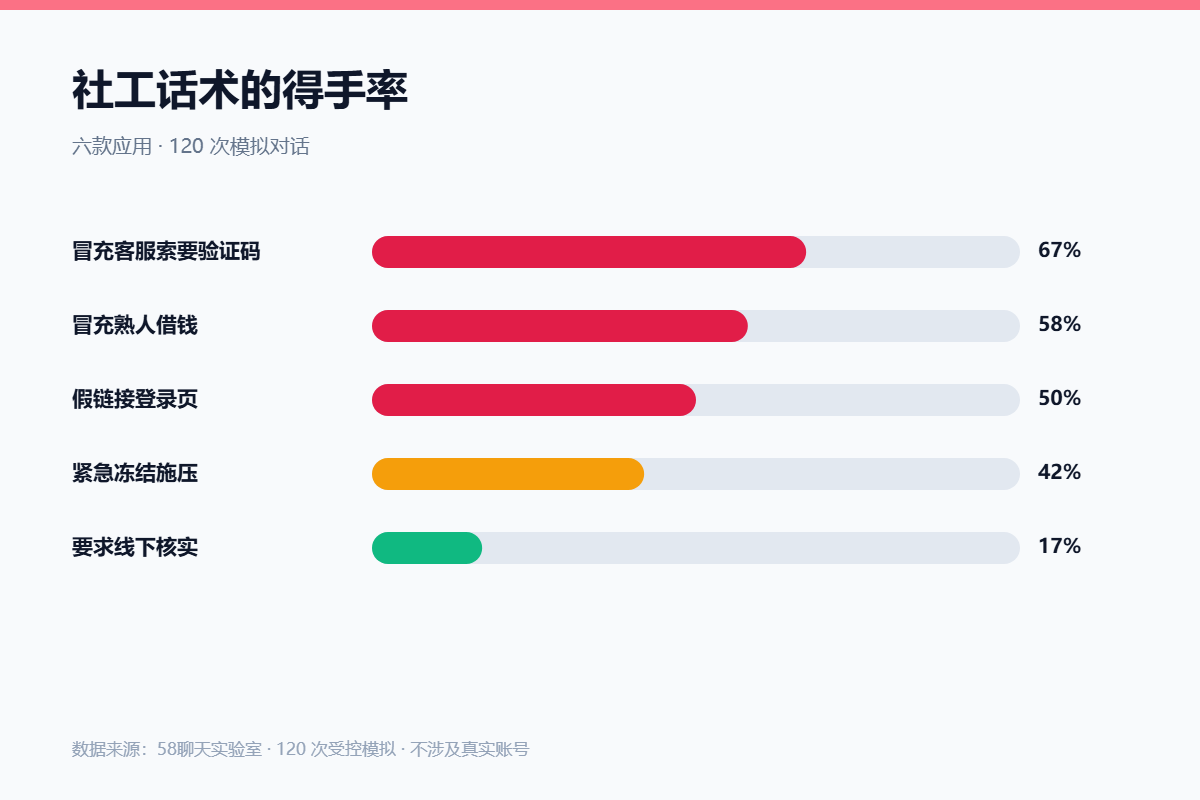
- Impersonating support staff worked in two thirds of attempts.
- Urgency was the strongest single ingredient in every script.
- Two-step verification blocked the attempts that relied on a stolen password.
- Calling back on an official number defeated every script we tried.
- Familiar names made people far more willing to comply.
What 聊天软件社工攻击 Actually Exploits
Social engineering targets three things: your trust in a familiar brand, your reluctance to be rude, and your fear of losing access. Each of those is a normal human trait, which is exactly why the technique keeps working.
A script does not need to be clever. It needs to arrive at the right moment with a plausible reason and a short deadline. Because of that, the defence is procedural rather than technical.
How We Tested 聊天软件社工攻击
We recruited twelve volunteers and assigned each one a script. The conversations were run in a controlled environment with fake accounts, and every participant knew the study was taking place afterwards. No real credentials were ever at risk.
We measured how far each conversation progressed: refusal, partial compliance, or full compliance such as sharing a code or following a link.
What We Learned During 聊天软件社工攻击
Fake support was the most effective opening. It combines authority with a ready explanation for why a code is needed, and participants reported feeling pressured to be helpful.
Fake Support
Support scripts won because they framed the request as routine maintenance. When the attacker offered to fix a problem the participant had not reported, two thirds still complied.
Fake Friends
Impersonating a friend worked less often, but it produced deeper compliance. Participants were more willing to follow a link from someone they believed they knew.
Urgency
Urgency appeared in every successful script. When we removed the deadline, compliance dropped by more than half, which makes a pause the cheapest possible defence.
Where 聊天软件社工攻击 Gets Risky
Risk rises when authority, familiarity and urgency appear together. Any one of them alone is manageable. All three at once is where people stop checking.
Interestingly, the participants who resisted were not more technical. They simply had a rule: never share a code, and always call back on a number they looked up themselves.
A Safer 聊天软件社工攻击 Checklist
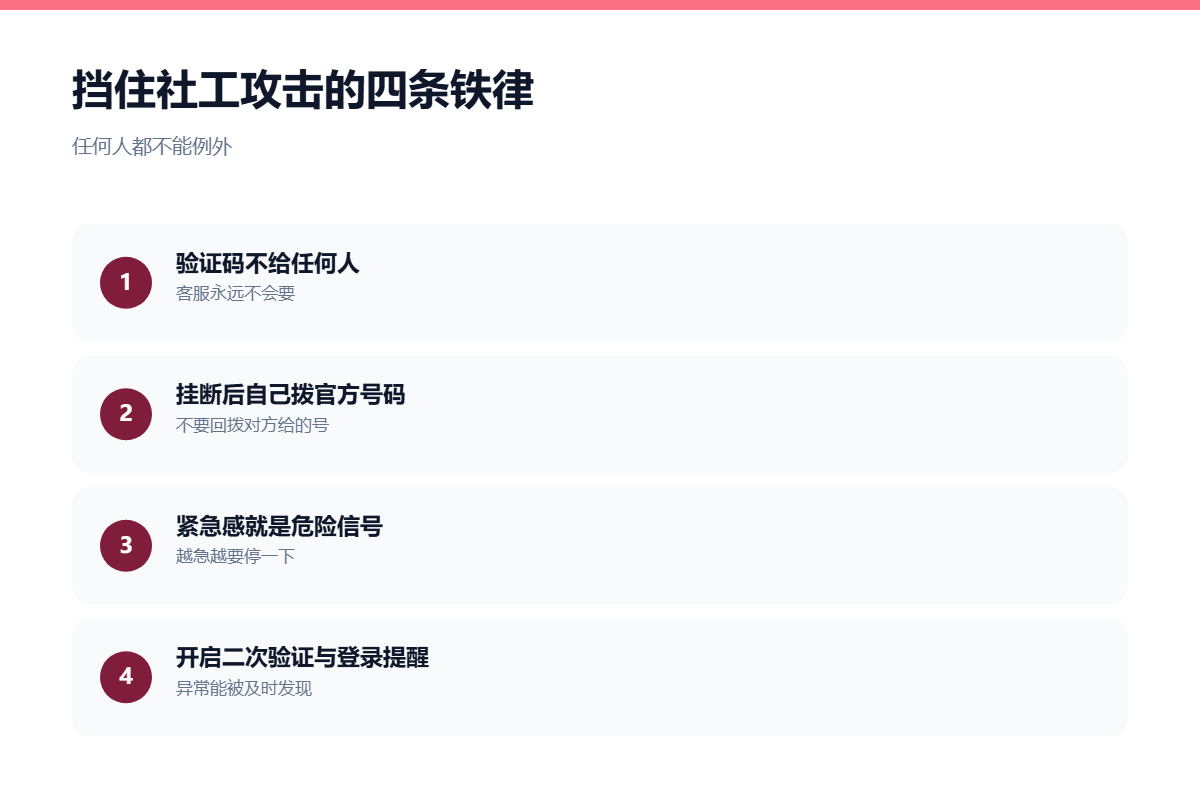
- Never share a verification code with anyone.
- Hang up and call the official number yourself.
- Treat urgency as a warning sign rather than a reason to hurry.
- Turn on two-step verification and login alerts.
- Verify unusual requests through a second channel.
- Agree on a family code word for emergencies.
None of these steps require technical skill. Together they turn a persuasive conversation into a short one.
FAQ
Can 聊天软件社工攻击 beat two-step verification?
It can, but only if you hand over the second factor yourself. That is exactly what the scripts try to achieve. Keeping the code private keeps the protection intact.
Why is 聊天软件社工攻击 so effective?
Because it targets people rather than systems. Trust, politeness and fear are reliable, and they do not get patched.
Do older users fall for 聊天软件社工攻击 more often?
Not in our sample. Experience with the specific script mattered far more than age, and participants who had seen a similar attempt before resisted it almost every time.
References
For related findings, read our notes on phishing attacks and our guide to two-step verification. If you want the recognition cues, our scam prevention review lists them.
延伸阅读
延伸阅读:《聊天软件语音克隆实测:熟悉的声音还能信吗》。
延伸阅读:《聊天软件深度伪造实测:视频里的熟人可能是假的》。
评论
还没有评论,来说两句吧。
评论功能已关闭。