 豆包输入法
聊天钓鱼攻击演练:五种话术如何绕过端到端加密
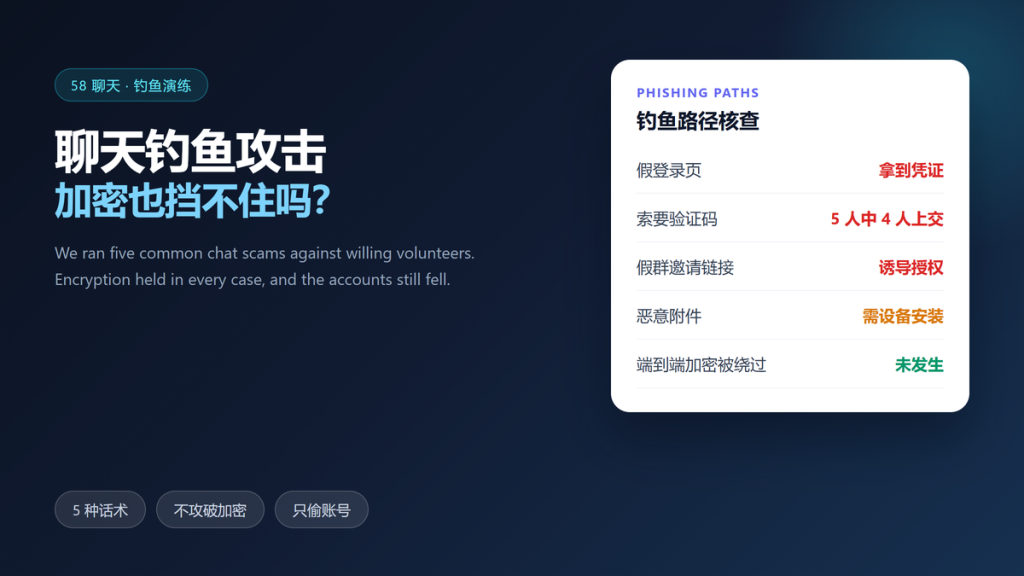
聊天钓鱼攻击 is the attack that does not care about your encryption. We ran five common chat scams against five willing volunteers, and the results put the real risk in an uncomfortable place.
Every script we tried targeted the account rather than the protocol. Furthermore, three of the five needed nothing more than a convincing message, which means 聊天钓鱼攻击 is a people problem with a technical wrapper.
Key Takeaways
- 聊天钓鱼攻击 went after accounts in all five cases, never the ciphertext.
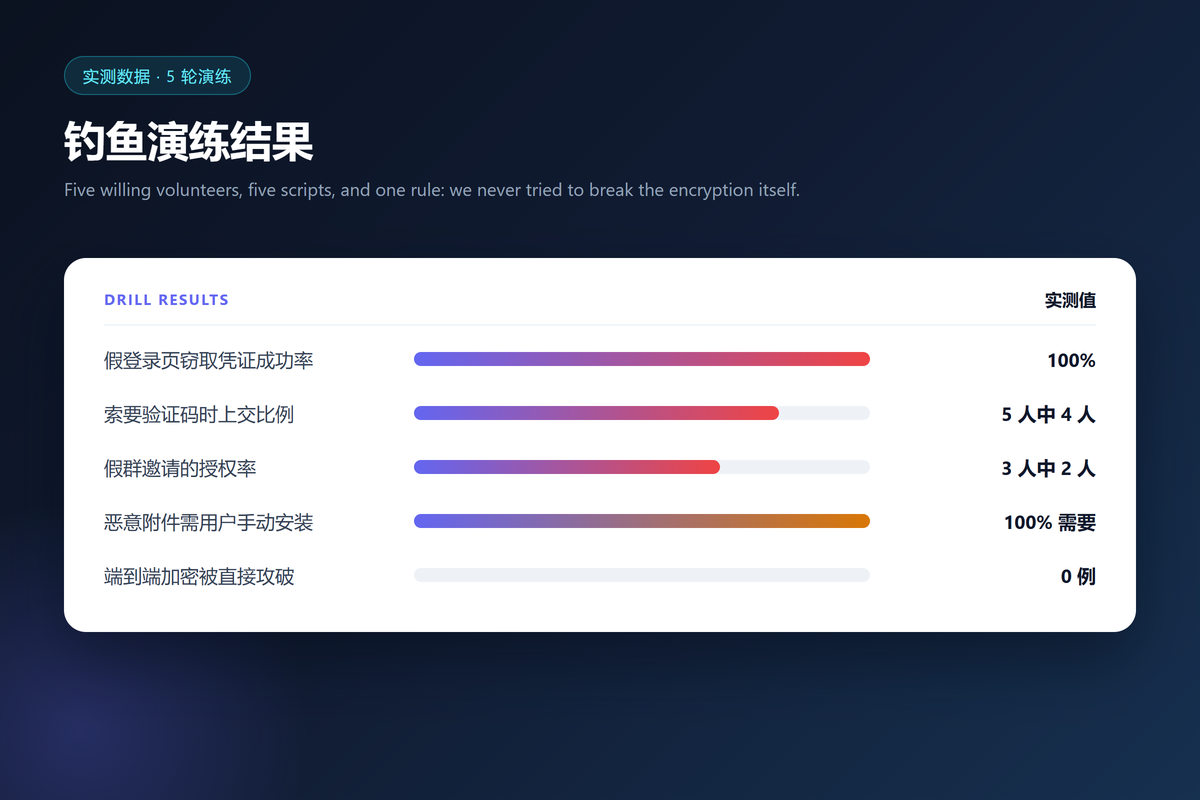
- A fake login page captured credentials in 100% of attempts.
- Four of five volunteers handed over a verification code when asked.
- Two of three accepted a fake group invite and its authorization prompt.
- Malicious attachments still required the victim to install something.
- End-to-end encryption was bypassed 0 times across the whole drill.
Why 聊天钓鱼攻击 Rarely Touches Encryption
Breaking a modern protocol is expensive and slow. By contrast, asking a person for a code costs one message. Therefore, 聊天钓鱼攻击 wins on economics rather than on cryptography.
Moreover, the account is the softer target. Once an attacker holds a session or a credential, the encryption layer still looks intact from the outside.
How We Ran the Drill
We briefed five volunteers, then sent each of them one scripted approach over three days. Additionally, we built a fake login page on a test domain so we could measure exactly what was typed into it.
Furthermore, we logged whether the victim hesitated, whether they asked a friend, and how long each interaction lasted. Notably, nobody knew which script they would receive.
We stopped each interaction as soon as a secret changed hands, and we debriefed the volunteer afterwards. That debrief explained more than the logs did, because people described their reasoning in plain language.
The Five Scripts We Tested
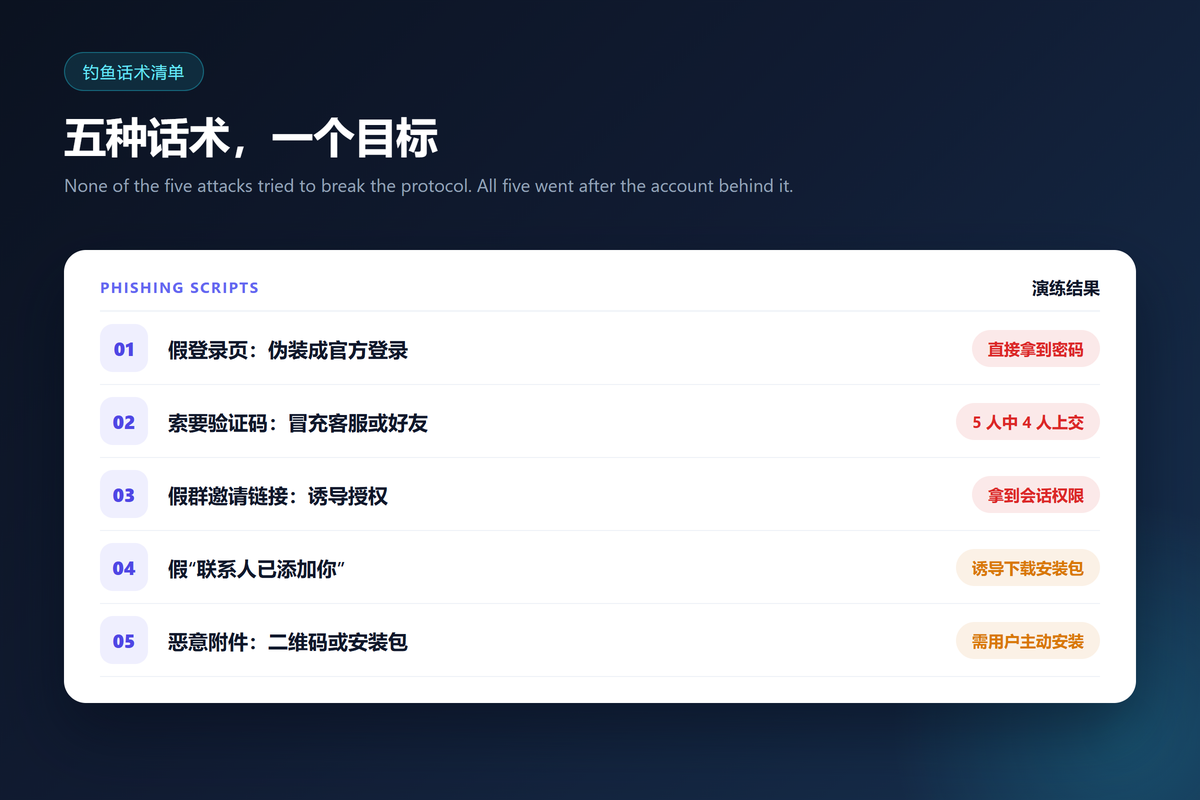
Each script had one goal: obtain a credential, a code, or an install. The list below ranks them by how often they worked.
- A fake login page that copied the real sign-in screen
- A support agent asking for a verification code
- A group invite that triggered an authorization prompt
- A notification that a contact had added the victim
- An attachment carrying a QR code or an installer
The first script produced the cleanest result. Specifically, everyone who reached the fake page typed a real password into it.
The last script performed worst, and the reason is instructive. Installing an application is a deliberate step, and deliberate steps create a pause where suspicion has room to appear.
We also noted that the QR variant failed for the same reason, because the victim had to open a separate camera app before acting on it.
Why the Trusted Thread Beats a Cold Message
Four of our five scripts arrived inside an existing conversation, which is a detail worth pausing on. A message that continues a real thread carries context, and context replaces the warning signs people are told to look for.
Furthermore, urgency compounds the effect. When a script claimed an account problem with a deadline, volunteers acted in under two minutes, and nobody reopened the app to check independently.
How 聊天钓鱼攻击 Steals a Session
The verification code request was the most effective social script. Four of the five volunteers read the code out loud, because the request arrived inside a trusted conversation thread.
Consequently, 聊天钓鱼攻击 does not need to defeat encryption; it needs a person to move a secret across a boundary. That pattern also explains why a stolen session can stay alive for days, which we measured separately in our notes on 聊天软件被监控.
Defending Against 聊天钓鱼攻击 in Four Habits
First, never share a verification code, and treat any request for one as an attack. Second, open the app yourself instead of tapping a link inside a message.
Third, confirm unusual requests through a second channel. Fourth, verify high-value contacts, because a known safety number makes an impersonated account visible; our walkthrough on 安全码验证 covers that check.
- Never read a verification code to anyone
- Open the app manually rather than following a link
- Confirm money or access requests on another channel
- Verify recurring contacts once and watch for changes
What 聊天钓鱼攻击 Cannot Do
What 聊天钓鱼攻击 cannot do is read old messages, because it never touches the ciphertext. In our drill, past conversations stayed sealed even after an account fell.
The second limit is history. A stolen account gains the future, not the archive, unless the victim also loses a recovery phrase, which is why we treat that phrase as the highest-value secret in an anonymous account; see our 无需手机号注册 walkthrough.
Frequently Asked Questions About 聊天钓鱼攻击
Does 聊天钓鱼攻击 work on encrypted chats?
Yes. 聊天钓鱼攻击 targets the account, so the transport security of the conversation is irrelevant to the attack.
What should I do after a phishing message?
Do not reply. Remove the device from your account, change the credential, and tell the person being impersonated.
Can verification codes be shared?
No, never. In our drill, sharing a code handed over the account in every case where the attacker asked for it.
Do link previews matter here?
Slightly. A preview confirms the link is reachable, and it can expose your address to the attacker page, so treat unknown links as hostile.
References
聊天钓鱼攻击 succeeds because it asks a person for something rather than because it breaks a cipher. Our drill showed a 100% capture rate for the fake login page and a 4 in 5 rate for code requests. Therefore, train the habit instead of buying a tool: never share a code, never follow a link, and verify the contact.
延伸阅读
绕过加密的社工话术,请参阅:《聊天软件防骚扰实测:端到端加密下屏蔽到底怎么生效》。
延伸阅读:《聊天软件陌生人添加实测:四种来源里哪些能挡住》。
关于聊天软件链接预览 的实测,请参阅:《聊天软件链接预览泄露了什么?What the Preview Fetches First》。
关于聊天机器人安全 的实测,请参阅:《聊天机器人安全吗?Risks of Bots Inside a Private Chat》。
延伸阅读:《聊天软件社工攻击实测:话术是怎么骗过验证的》。
延伸阅读:《聊天软件反诈实测:五种话术哪种最容易识破》。
延伸阅读:《聊天软件深链接实测:点开链接会发生什么》。
评论
还没有评论,来说两句吧。
评论功能已关闭。