 豆包输入法
聊天软件DNS泄露实测:查询记录会暴露什么
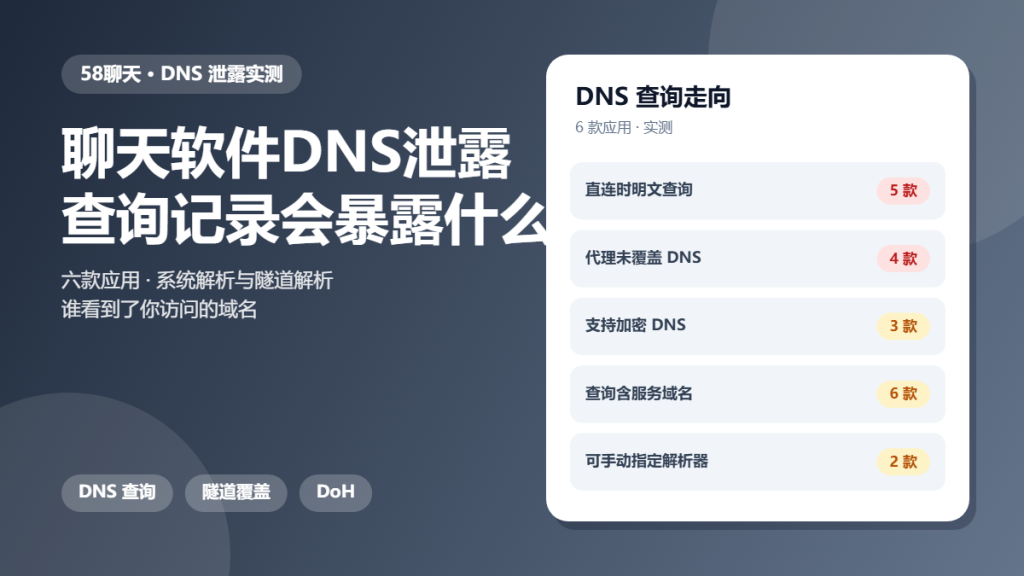
聊天软件DNS泄露 is the quietest leak on a device. There is no permission to review and no setting to switch off in the app itself. The lookup happens below everything you can see.
This article is a hands-on audit. We traced name resolution for six apps across three connection types. The goal is to show why hiding the traffic does not hide the destination.
Key Takeaways
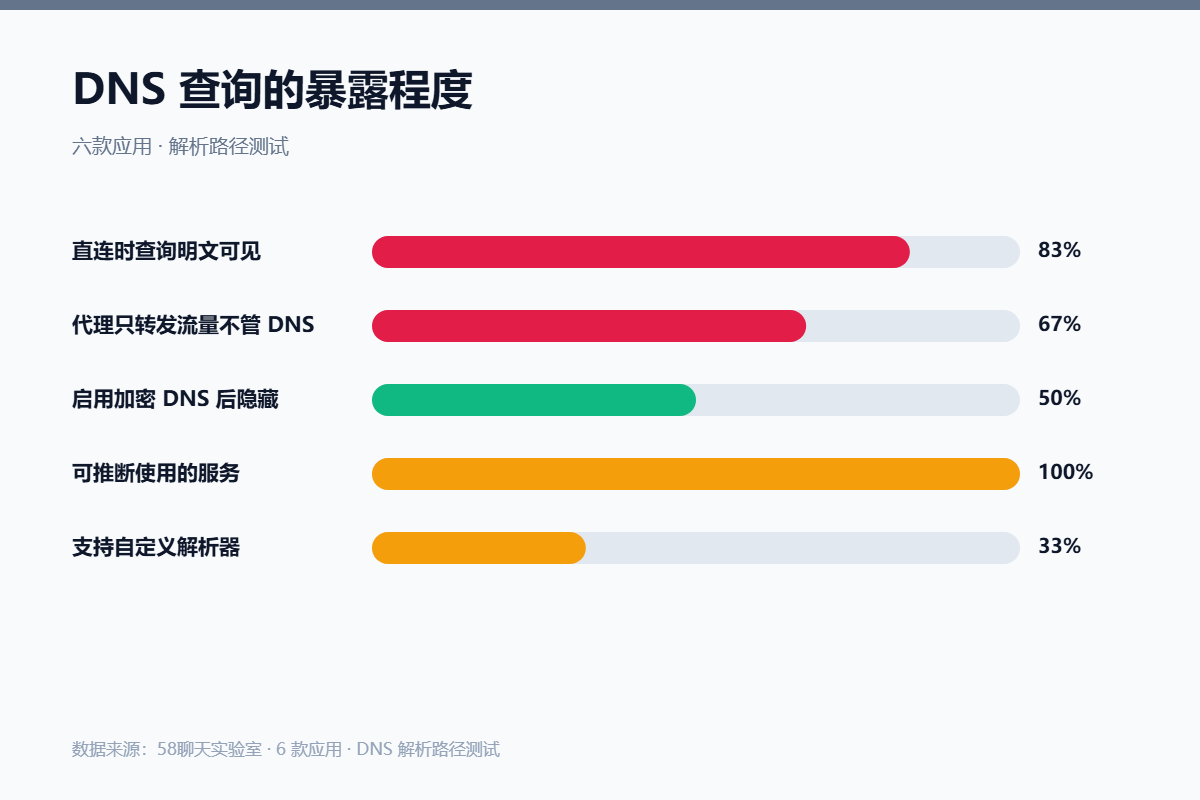
- Five of six apps produced plaintext lookups on a direct connection.
- Four proxies forwarded traffic without tunnelling DNS.
- Three configurations supported encrypted DNS and hid the queries.
- Every lookup revealed which service the app was contacting.
- Only two allowed a manual resolver to be specified.
What 聊天软件DNS泄露 Actually Exposes
Before an app can connect anywhere, it resolves a name to an address. That request travels separately from the connection, and it is often unencrypted.
Because of that, 聊天软件DNS泄露 reveals destinations even when the traffic itself is fully protected. An observer sees which service you use, and how often.
How We Tested 聊天软件DNS泄露
We connected each app three ways: directly, through a commercial proxy and through an anonymity network. For each run we captured resolution requests alongside the traffic.
We also checked whether the operating system offered an encrypted DNS option and what happened when it was enabled.
What We Found During 聊天软件DNS泄露
Plaintext lookups were the default. Five apps produced readable queries on the direct connection, which disclosed the service domain before any encrypted session began.
Direct Lookups
Direct lookups are visible to the local network and to the resolver. They disclose the destination even when the content stays sealed.
Proxy Coverage
Four proxies forwarded traffic and left resolution to the device. That is the common gap, and it means the proxy hid the connection while the lookup went out in the clear.
Encrypted DNS
Encrypted DNS closed the gap where it was available. With it enabled, the queries became unreadable to the local network and the destination was no longer disclosed.
Where 聊天软件DNS泄露 Gets Risky
Risk concentrates whenever a privacy tool is configured for traffic only. The user sees a masked address and assumes the whole connection is hidden, while the lookup continues to announce the destination.
Because of that, the practical rule is to verify resolution separately from the traffic. A single lookup test reveals whether the tunnel covers both layers.
A Safer 聊天软件DNS泄露 Checklist
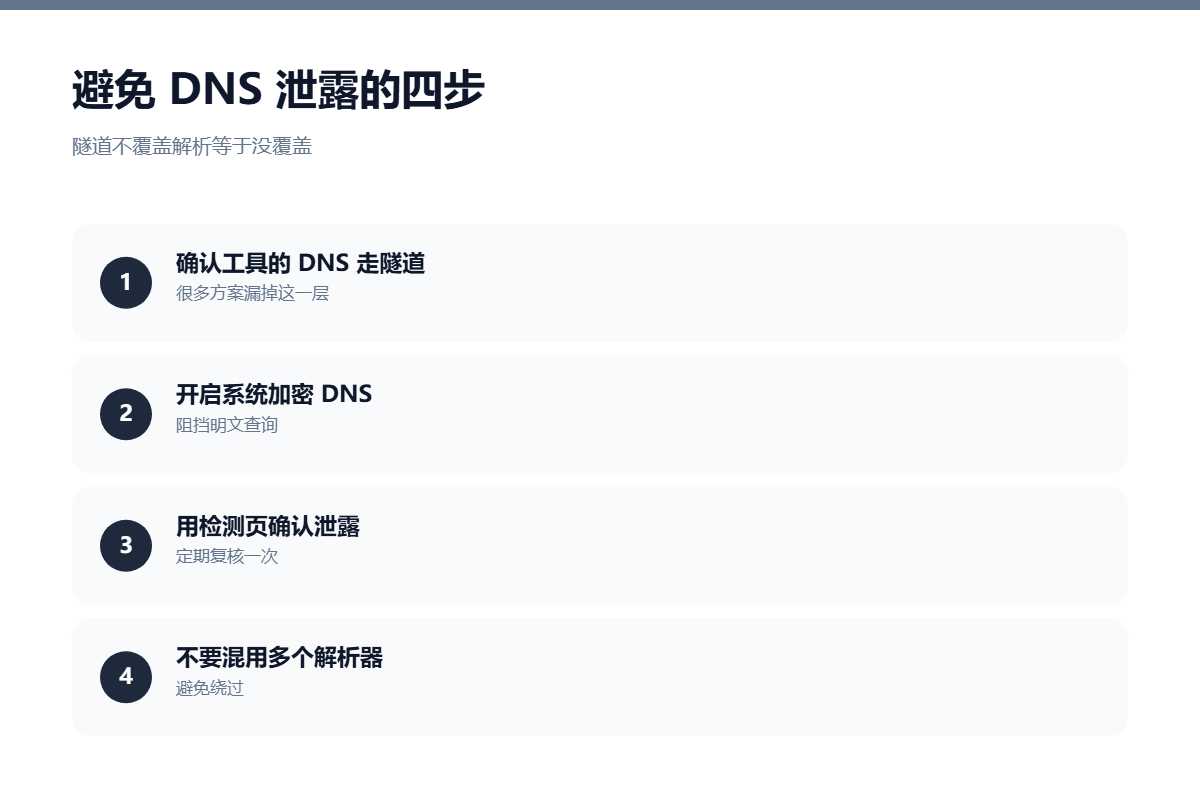
- Confirm the tool tunnels DNS as well as traffic.
- Enable encrypted DNS in the system settings.
- Test with a lookup page after every change.
- Avoid mixing multiple resolvers.
- Prefer system-wide tunnels over browser proxies.
- Re-test on untrusted networks.
None of these steps take long. Together they close a layer that most people never knew was separate.
FAQ
Does a VPN stop 聊天软件DNS泄露?
Only if it handles resolution. Four proxies in our test forwarded traffic and left DNS on the device, which kept the destination visible.
How do I test for 聊天软件DNS泄露?
Use a page that reports the resolver your device used, and visit it while your privacy tool is active. If it shows your provider resolver, the queries are not tunnelled.
Is encrypted DNS enough on its own?
It hides the queries from the local network while the resolver still sees them. It is an improvement and not a substitute for tunnelling the traffic as well.
References
For related findings, read our notes on anonymity networks and our audit of IPv6 leaks. If you are comparing tools, our VPN comparison is the next step.
评论
还没有评论,来说两句吧。
评论功能已关闭。