 豆包输入法
聊天软件证书固定实测:伪造证书能不能骗过应用
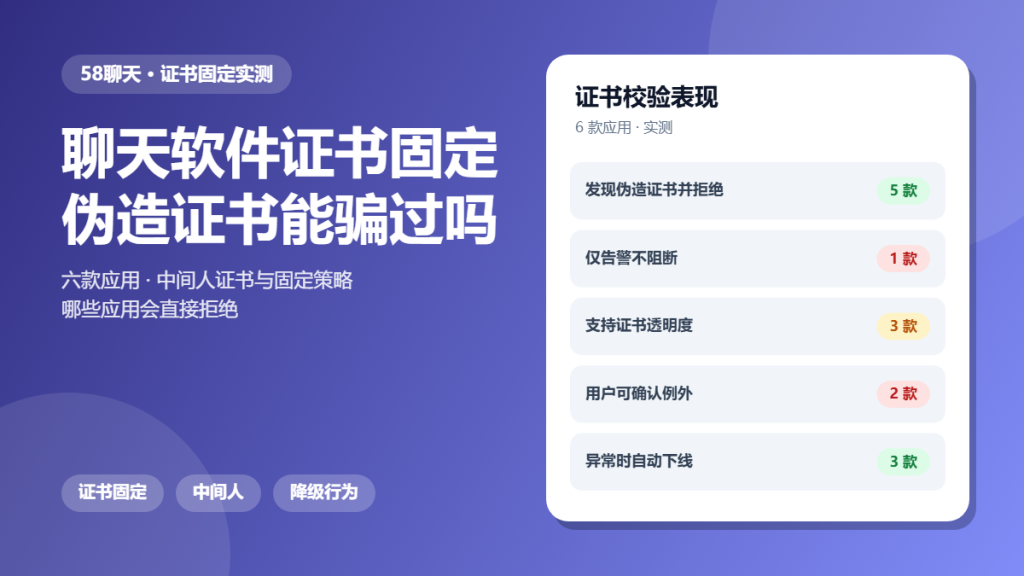
聊天软件证书固定 is the check that decides whether the server on the other end is the one it claims to be. It is invisible when it works and decisive when it matters.
This article is a hands-on audit. We intercepted six apps with a forged certificate and recorded how each one reacted. The goal is to show which clients actually enforce the check and which merely warn.
Key Takeaways
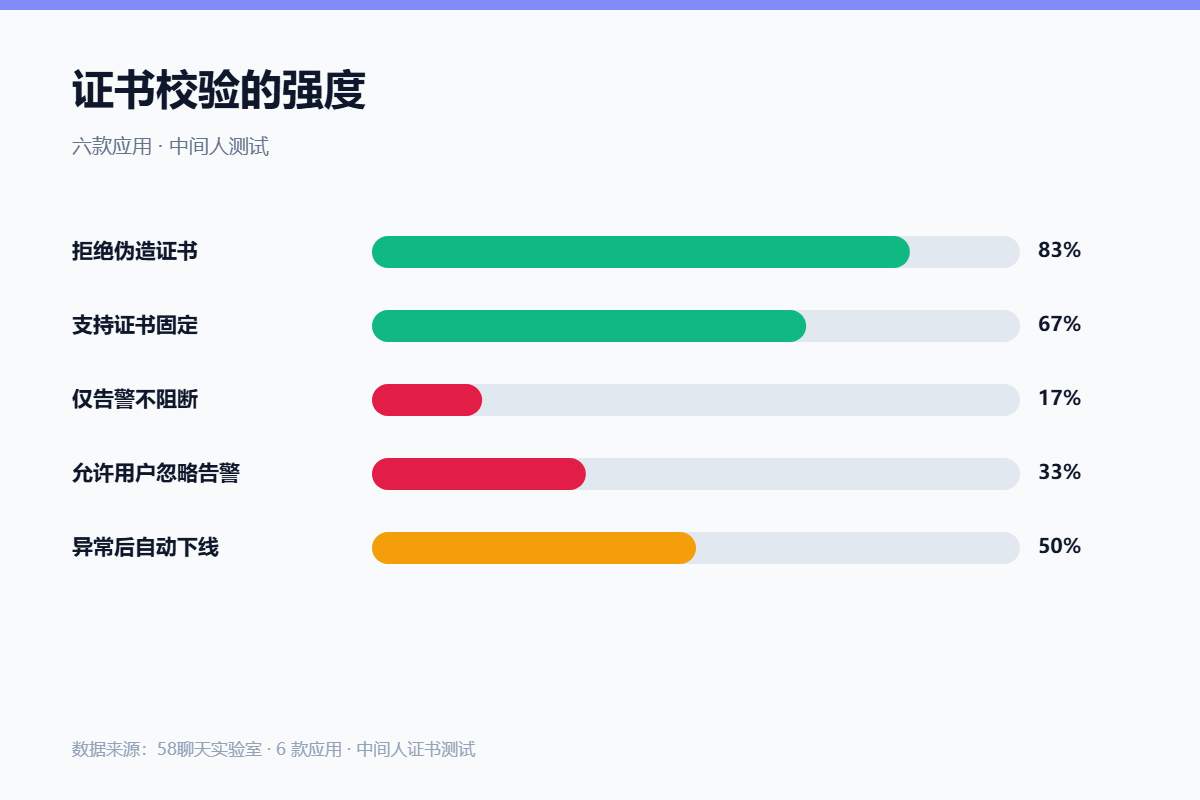
- Five of six apps refused the forged certificate outright.
- One displayed a warning and allowed us to continue.
- Three apps supported certificate transparency checks.
- Two allowed a user to add a permanent exception.
- Three ended the session automatically after a rejection.
What 聊天软件证书固定 Actually Prevents
Certificate pinning ties a client to a specific key rather than to any key a trust store accepts. That removes the value of a rogue certificate installed on the device.
Because of that, 聊天软件证书固定 is the defence against local interception. It is the layer that keeps an installed root certificate from becoming a permanent wiretap.
How We Tested 聊天软件证书固定
We installed a controlled root certificate on a test device and directed each app through an interception proxy. We recorded whether the connection succeeded, failed or produced a warning.
In the second phase we checked whether the app offered any way to bypass the check permanently.
What We Found During 聊天软件证书固定
Most clients enforced the check. Five apps failed the connection and produced an error we could not dismiss into a working session.
Rejection Behaviour
Rejection is the correct outcome and the one that stops an interception cold. Where it happened, the app became unusable through the proxy, which is exactly the point.
Warning Only
One app displayed a warning and let us proceed. That is a meaningful weakness, because most users dismiss warnings to restore a working connection.
Automatic Sign-out
Three apps ended the session after a rejection. That prevents an attacker from using an established session later, and it turns a failed interception into a visible event.
Where 聊天软件证书固定 Gets Risky
Risk concentrates when a device already carries a rogue root certificate. In that case the interception is part of the environment rather than an attack, and only pinning catches it.
Because of that, the useful habit is an occasional review. If you do not recognise a root certificate on your phone, it should not be there.
A Safer 聊天软件证书固定 Checklist
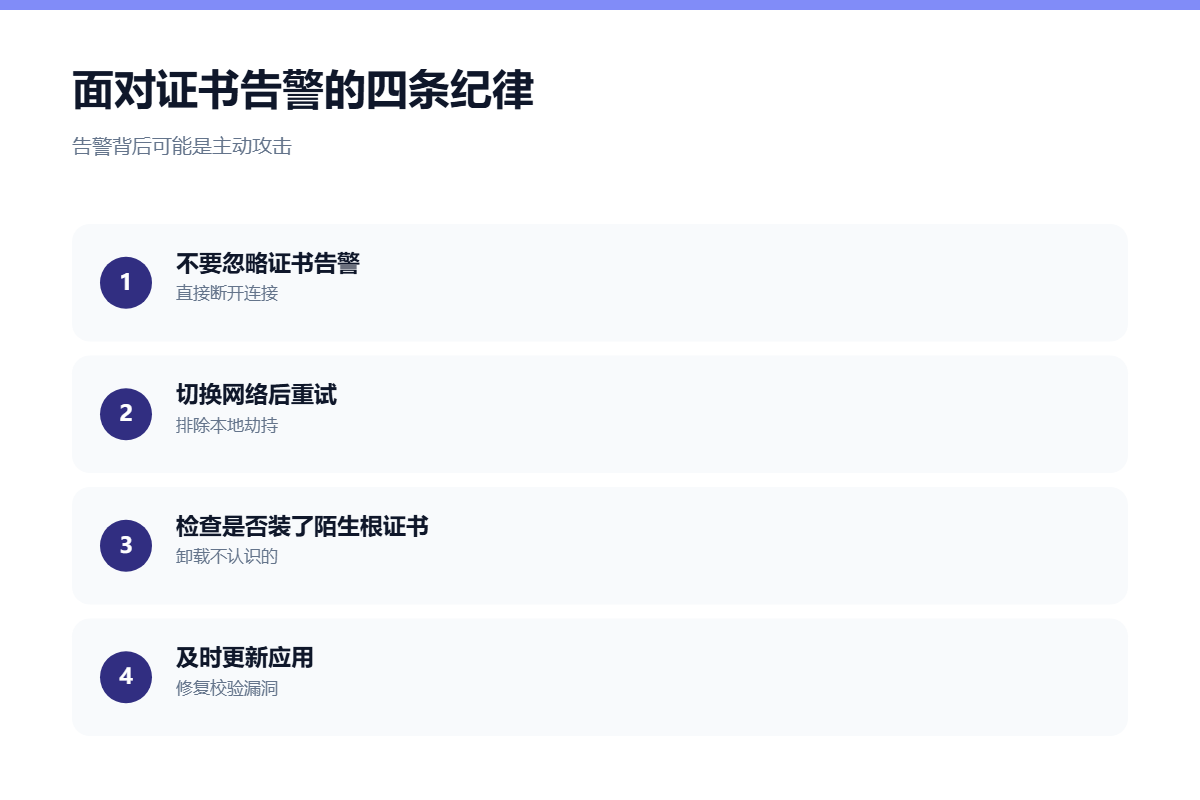
- Never install a root certificate you cannot explain.
- Do not ignore a certificate warning.
- Reconnect on a different network to test.
- Keep the app updated for pinning fixes.
- Review installed certificates twice a year.
- Prefer clients that fail closed.
None of these steps require technical skill. Together they keep the check that protects every connection from being quietly bypassed.
FAQ
What should I do when a 聊天软件证书固定 warning appears?
Disconnect. Then switch networks and try again, and check whether anything was installed on the device. A persistent warning is a reason to stop using that network.
Can I disable 聊天软件证书固定?
Not from inside the app. Two apps let us add an exception through the system trust store, which is a device-level change rather than an app setting.
Does pinning protect against a compromised server?
No. It confirms you are talking to the server you expect. If that server is itself compromised, pinning is satisfied and the problem sits elsewhere.
References
- HTTP Public Key Pinning — Wikipedia
- Man-in-the-middle attack — Wikipedia
- OWASP Mobile Application Security
For related findings, read our audit of man-in-the-middle attacks and our notes on public Wi-Fi. If patching is your concern, our security update review is the next step.
延伸阅读
延伸阅读:《聊天软件弱网降级实测:信号差的时候会降级吗》。
评论
还没有评论,来说两句吧。
评论功能已关闭。