 豆包输入法
聊天软件模拟器实测:在电脑上多开安全吗
聊天软件模拟器风险 is easy to overlook because an emulator feels like a phone. The screen looks the same, and the app rarely says otherwise. Underneath, several of the protections the app depends on are simply absent.
This article is a hands-on audit. We ran six apps inside an emulator and compared what changed relative to a real device. The goal is to describe the trade-off rather than to advise against the practice entirely.
Key Takeaways
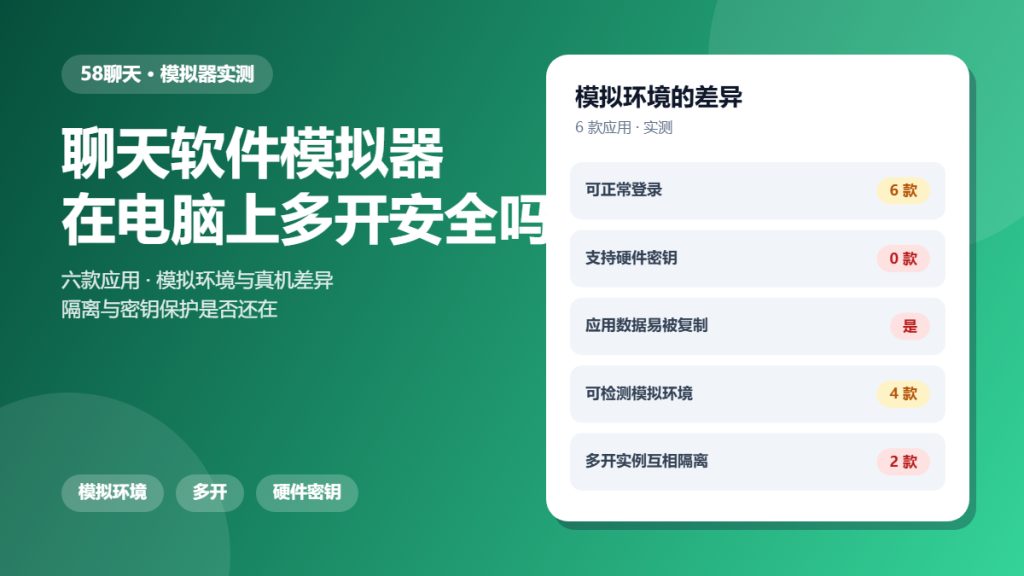
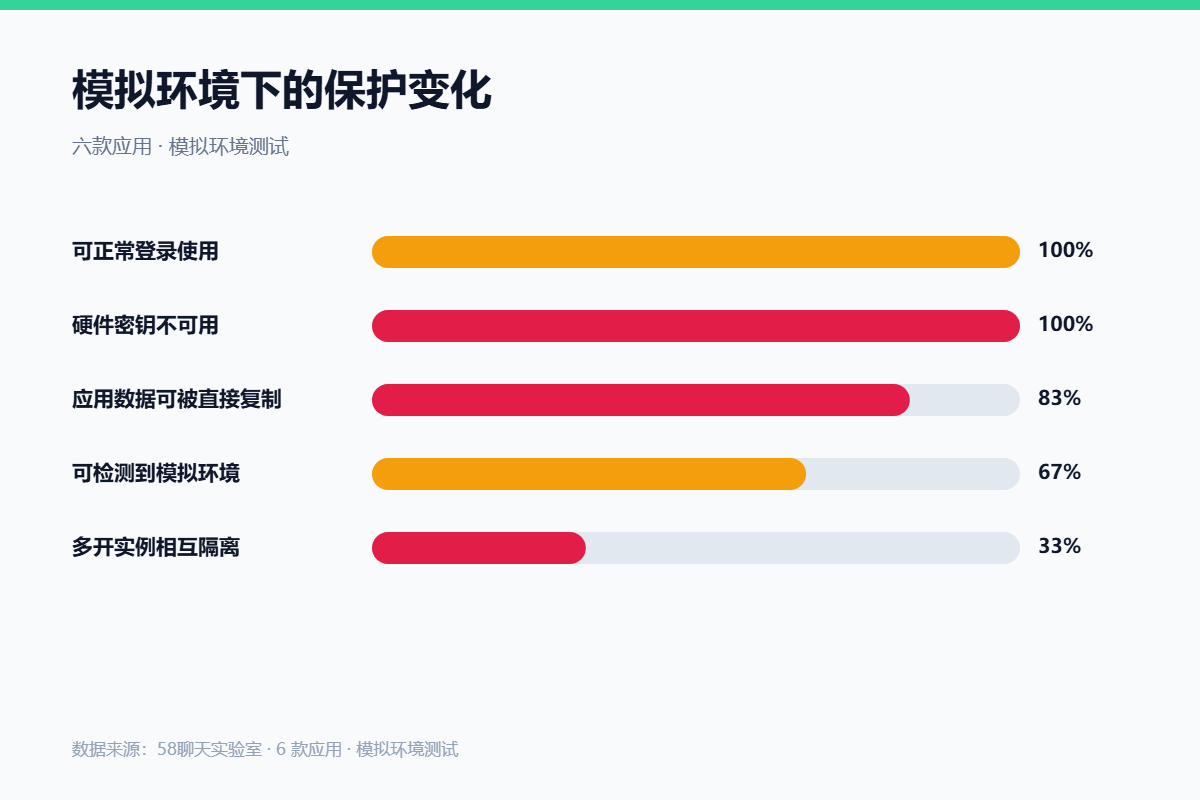
- All six apps could log in from an emulator.
- Hardware-backed key storage was unavailable in every case.
- Four apps detected the emulated environment.
- Two refused to run after detection.
- App data was directly copyable from the emulator image.
What 聊天软件模拟器风险 Actually Means
An emulator is a virtual phone running on a general-purpose computer. It has no secure element, no real device attestation and no meaningful isolation from the host.
Because of that, 聊天软件模拟器风险 is about missing guarantees rather than about a specific attack. The protections are absent, and nothing needs to be exploited for that to matter.
How We Tested 聊天软件模拟器风险
We ran six apps in two popular emulators and used them normally for a week. We recorded launch behaviour, available security features and whether the environment was detected.
We then copied the emulator disk image and searched it for chat data from the host machine.
What We Found During 聊天软件模拟器风险
Logging in was never a problem. Every app accepted the emulated device, and most features worked as they would on a phone.
Hardware Keys
Hardware key storage was unavailable everywhere. That is the most significant loss, because it is the protection that keeps local data unreadable even when the system is compromised.
Data Isolation
Isolation was effectively absent. The emulator image is a file, and a file can be copied. Our host-side search recovered chat databases without any special tooling.
Detection Signals
Detection was partial. Four apps noticed something and either warned us or limited features, and two stopped entirely.
Where 聊天软件模拟器风险 Gets Risky
Risk concentrates around which account you use. An emulator is a reasonable environment for a secondary account used for testing, and a poor one for the account that holds your real conversations.
Because of that, the useful rule is about placement rather than avoidance. Keep sensitive accounts on real hardware and treat emulators as disposable.
A Safer 聊天软件模拟器风险 Checklist
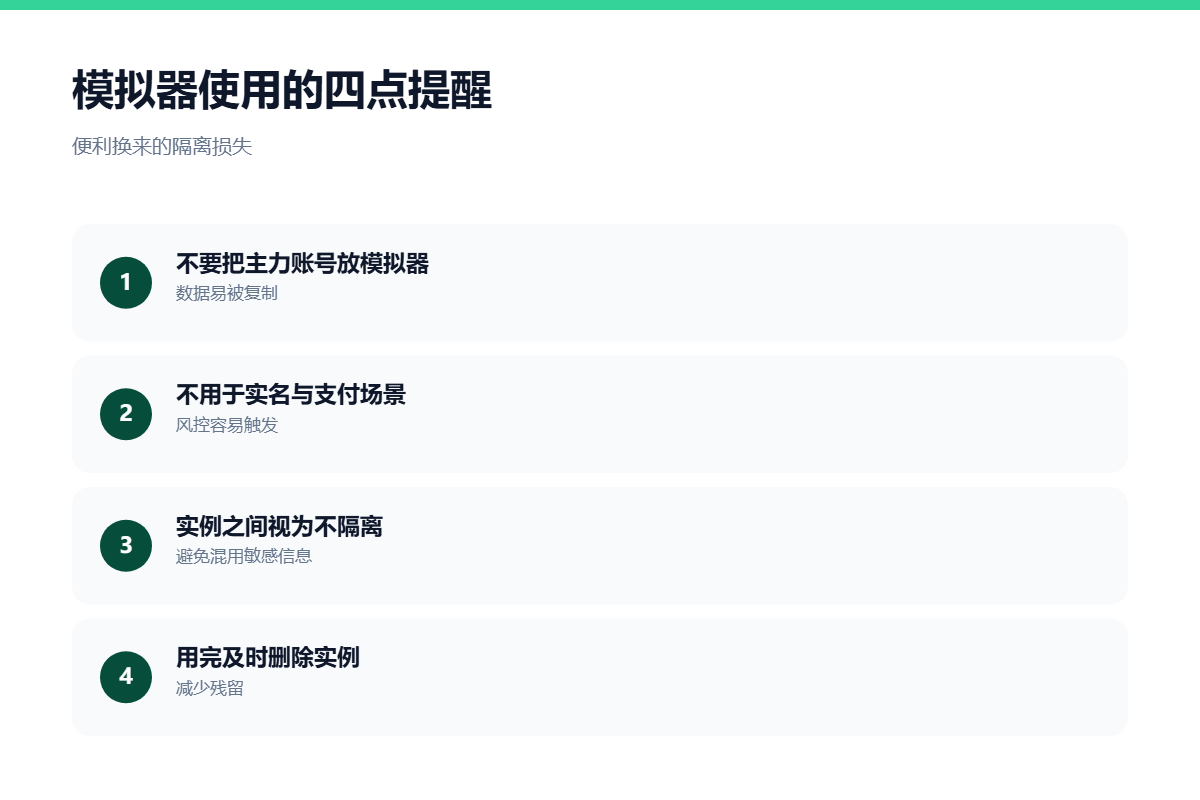
- Keep primary accounts off emulators.
- Avoid verification and payment tasks there.
- Treat instances as fully readable.
- Delete the instance when you finish.
- Do not mix sensitive accounts in one instance.
- Watch for in-app environment warnings.
None of these steps stop you using an emulator. Together they keep a convenience environment from holding the accounts that matter.
FAQ
Does 聊天软件模拟器风险 affect my account?
It affects the data on the emulated device, which is fully readable. The account itself is at risk only if someone obtains the emulator image.
Is 聊天软件模拟器风险 different from rooted phones?
The outcome is similar and the cause is different. Rooting removes isolation on a real device, while an emulator never had it in the first place.
Can I use an emulator for testing safely?
Yes, with a secondary account and no sensitive data. That combination keeps the exposure contained to the test environment.
References
For related findings, read our notes on root detection and our audit of multiple accounts. If you use unofficial builds, our third-party client review is relevant.
评论
还没有评论,来说两句吧。
评论功能已关闭。