 豆包输入法
聊天软件Root检测实测:越狱设备风险在哪
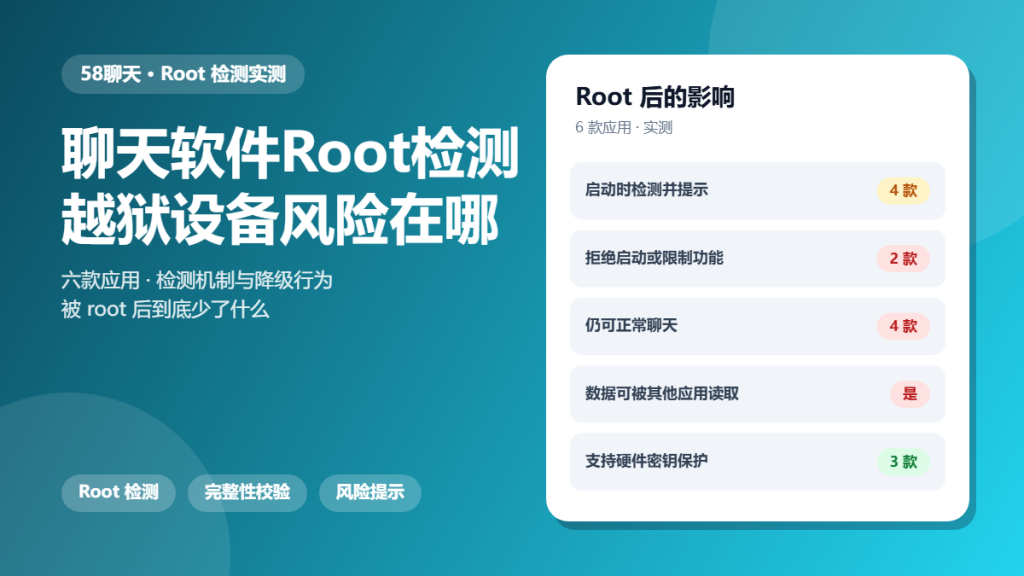
聊天软件Root检测 is the moment an app decides whether to trust the device it is running on. On a rooted phone, that trust is genuinely reduced, and the app knows it.
This article is a hands-on audit. We ran six apps on rooted devices and recorded what survived, what degraded and what the apps did about it. The goal is to explain the trade-off rather than to moralise about rooting.
Key Takeaways
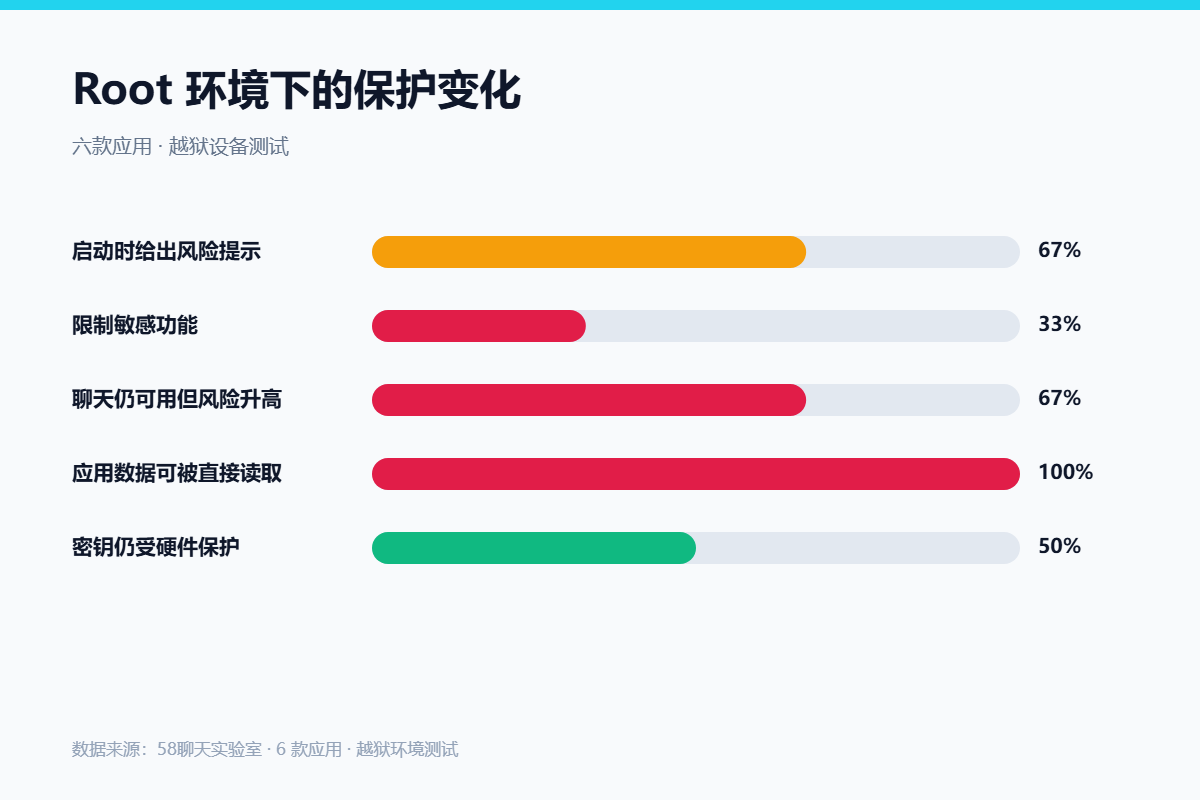
- Four of six apps detected the rooted device and warned us.
- Two refused to start until we restored an unmodified system.
- Hardware-backed keys became unavailable in every app.
- App data was directly readable by other privileged apps.
- Messaging itself kept working in four apps.
What 聊天软件Root检测 Actually Protects
Rooting removes the isolation between apps. Once every app can read every other app’s private storage, encryption at rest stops meaning much.
Because of that, 聊天软件Root检测 is really about sandbox integrity. The app is not checking your intentions, it is checking whether its own protections still hold.
How We Tested 聊天软件Root检测
We used two rooted test devices, one with a standard rooting method and one with a hiding module enabled. For each app we recorded the launch behaviour and the available features.
We then attempted to read app-private data from a separate privileged tool to confirm whether isolation still existed.
What We Found During 聊天软件Root检测
Detection was common and consistent. Four apps identified the environment at launch, and two of them stopped entirely rather than running with reduced guarantees.
Detection Methods
Detection ranged from simple file checks to integrity verification of the system partition. The stronger methods could not be hidden by the modules we tested.
Degraded Protections
Where apps continued, they ran without the guarantees they normally rely on. Message content stayed encrypted in transit, and local storage became readable to anything with root access.
Hardware-backed Keys
Hardware key storage was unavailable in every case. That is the most consequential loss, because it is the one protection that still holds when the operating system cannot be trusted.
Where 聊天软件Root检测 Gets Risky
Risk concentrates around what the device holds. A rooted phone used for casual chat is a modest problem. The same phone holding work conversations and saved credentials is a serious one.
Because of that, the practical advice is separation. Keep sensitive accounts on an unmodified device and treat a rooted phone as a convenience-only environment.
A Safer 聊天软件Root检测 Checklist
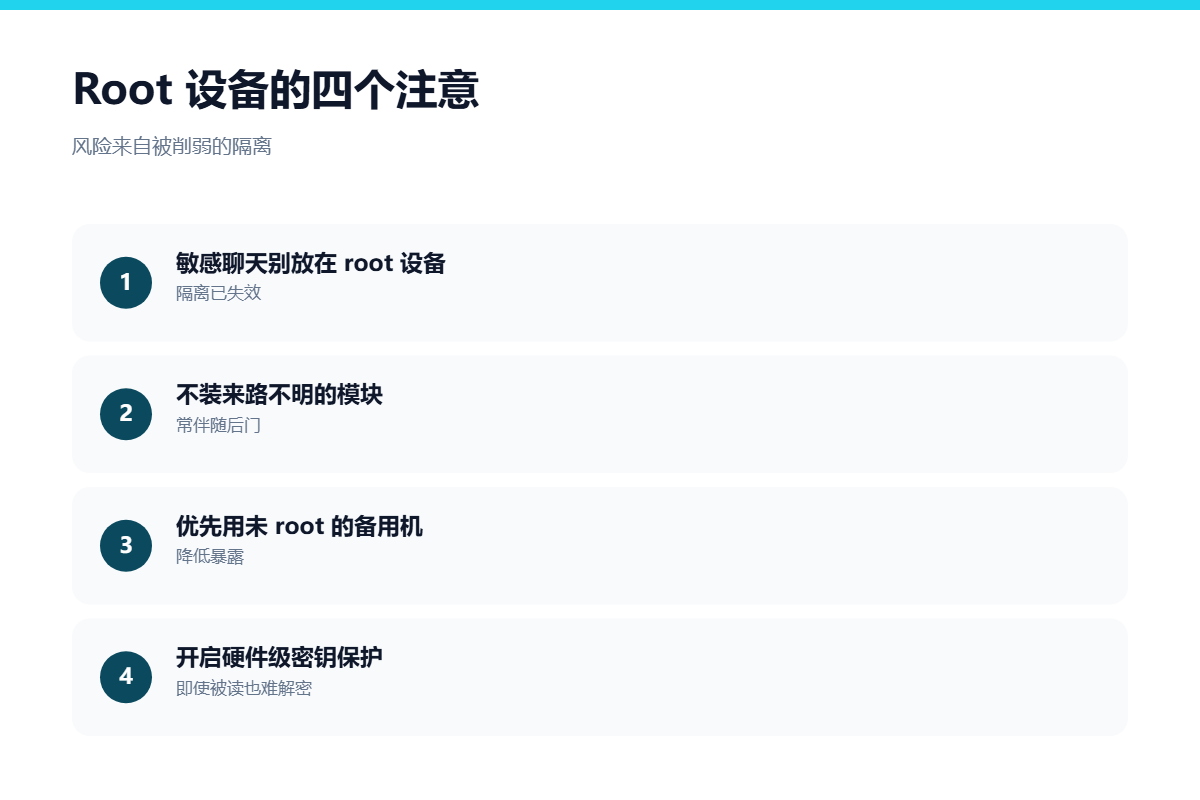
- Keep sensitive accounts off rooted devices.
- Do not install modules from unknown sources.
- Prefer hardware-backed key storage where available.
- Heed the in-app warning rather than dismissing it.
- Use a separate unmodified device for work.
- Restore the stock system before selling the phone.
None of these steps require giving up rooting. Together they keep a modified device from holding the accounts that matter most.
FAQ
Why do apps block 聊天软件Root检测 failures?
Because the protections they depend on are gone. Storage isolation and hardware key storage both stop working, so the app cannot honour the guarantees it advertises.
Is 聊天软件Root检测 a privacy problem?
It can report device state to the server. That is a legitimate signal for risk scoring and also a data point about your device, which is worth knowing.
Can I hide root from these apps?
Partly. Simple checks can be hidden, and integrity verification of the system partition generally cannot. Results in our test matched that pattern.
References
For related findings, read our notes on emulator risk and our audit of biometric locks. If you are hardening device storage, our security settings review is the next step.
延伸阅读
延伸阅读:《聊天软件USB调试实测:连电脑时能被拿走什么》。
评论
还没有评论,来说两句吧。
评论功能已关闭。