 豆包输入法
聊天软件隐私自查实测:三十项检查能发现什么
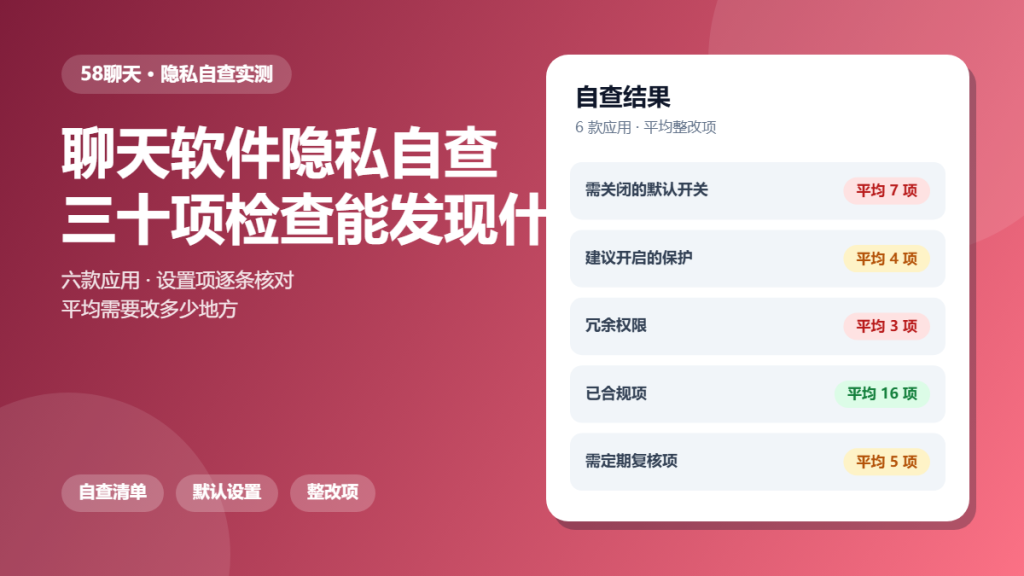
聊天软件隐私自查 is what turns a vague concern into a short list of tasks. Without a list, most people open the settings, feel overwhelmed and close them again.
This article is a hands-on audit. We ran a thirty-point check across six apps and recorded what needed changing. The goal is to show which categories produce the most useful fixes.
Key Takeaways
- An average of seven default switches needed changing.
- Four protections were off by default in every app.
- An average of three redundant permissions needed revoking.
- About half of the thirty points were already correct.
- Five items needed a periodic re-check rather than a one-time fix.
What a 聊天软件隐私自查 Actually Covers
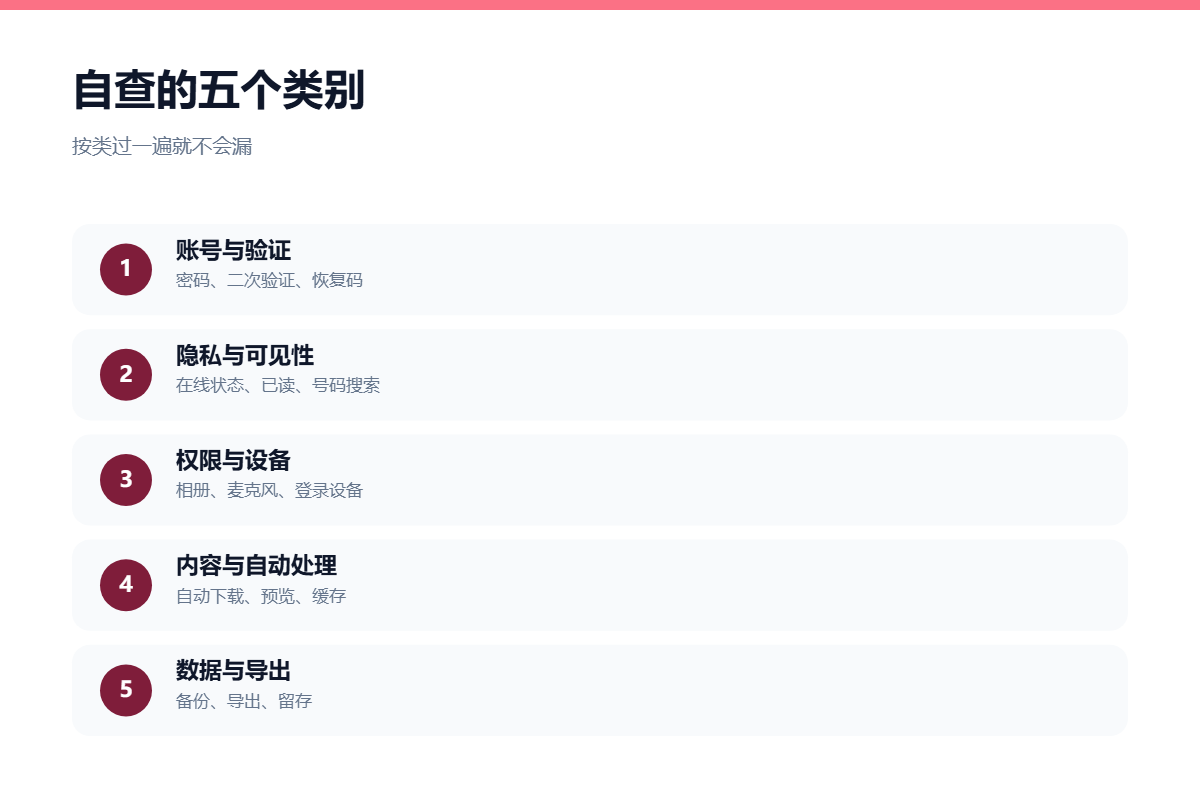
A useful self-audit is grouped by purpose rather than by menu. Account, visibility, permissions, automatic behaviour and stored data cover almost everything that matters.
Because of that, 聊天软件隐私自查 does not require memorising settings. It requires knowing which five groups to walk through.
How We Tested the 聊天软件隐私自查
We installed six apps with default settings and scored each against the same thirty points. Then we applied the fixes and recorded how long the whole process took.
We repeated part of the audit after a major update to see whether settings held.
What We Found During the 聊天软件隐私自查
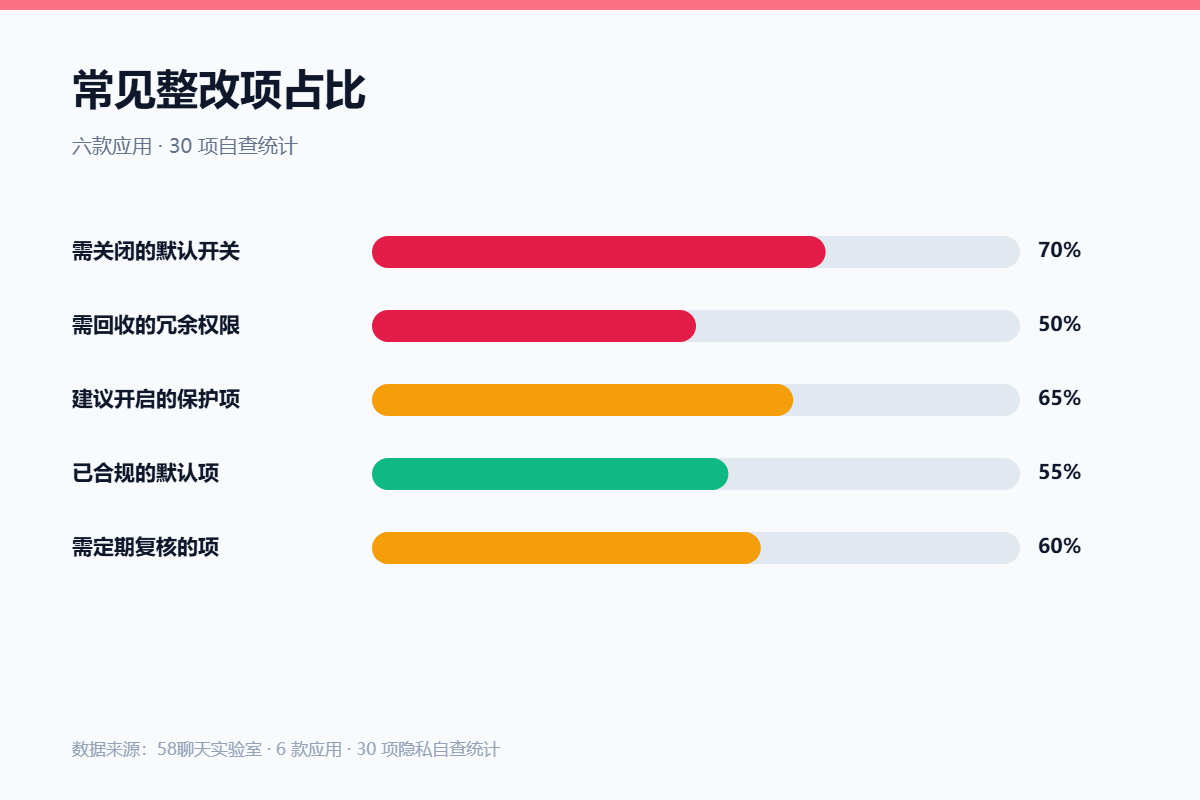
The distribution was consistent across apps. A small number of points produced most of the improvement, and the rest were either already fine or minor.
Account and Verification
This group had the highest value per minute. Enabling a second factor and a login alert addresses the most damaging scenario, which is someone else signing in.
Visibility Settings
Visibility was universally permissive by default. Online status, read receipts and number search were open everywhere, and each one reveals activity or enables discovery.
Permissions and Devices
This group produced the most cleanup. Redundant permissions were common, and the authorised device list usually contained hardware that no longer existed.
Where a 聊天软件隐私自查 Gets Forgotten
The audit decays. Updates reintroduce defaults, new features arrive enabled and a device you added last year is still authorised.
Because of that, the practical approach is a short repeat. A fifteen-minute pass twice a year keeps the audit accurate without turning it into a chore.
A Safer 聊天软件隐私自查 Checklist
- Walk the five groups in the same order every time.
- Fix account protection first.
- Close visibility settings second.
- Revoke permissions nothing uses.
- Clear automatic downloads and previews.
- Re-run the audit after major updates.
None of these steps require technical knowledge. Together they turn a large settings menu into a list you can actually finish.
FAQ
How often should I run a 聊天软件隐私自查?
Twice a year is enough for most people, plus once after any major app update. The whole pass takes about fifteen minutes per app.
What does a 聊天软件隐私自查 miss?
Anything outside your control: how the provider stores data, who it shares with and how long it keeps records. Those belong to the privacy policy rather than the settings.
Is it worth doing on every app?
Prioritise the accounts that hold real conversations and identity documents. Covered accounts matter more than the ones used once for a delivery update.
References
For related findings, read our ten-point security baseline and our audit of app permissions. If retention is your concern, our data retention review is the next step.
评论
还没有评论,来说两句吧。
评论功能已关闭。