 豆包输入法
聊天软件数据泄露响应实测:账号被拖库后先做什么
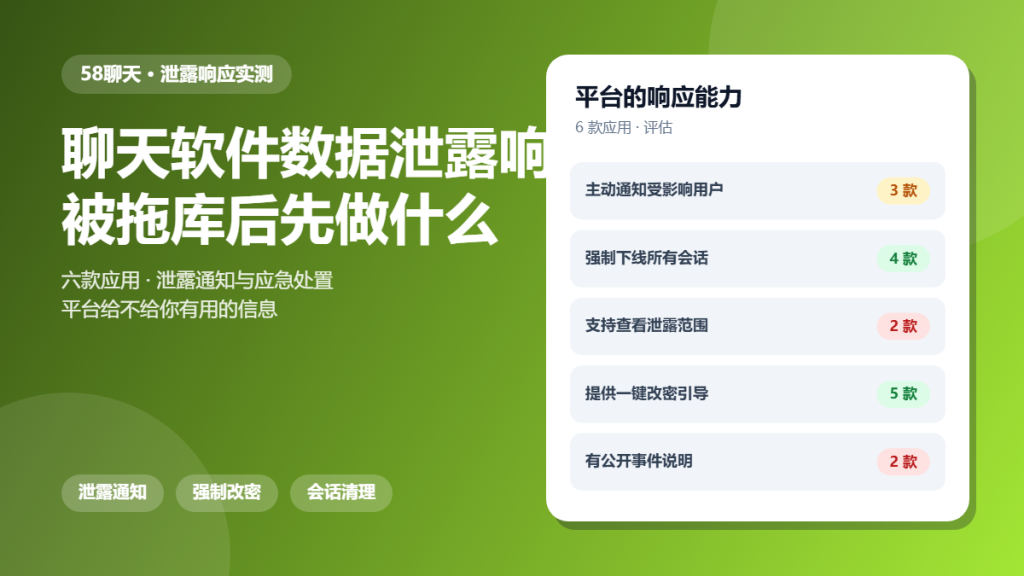
聊天软件数据泄露响应 is the part of an incident that belongs to you. The company handles the server side, and your account is left to you, usually with a short email and a link to a help page.
This article is a hands-on review of how six apps handle breach communication and what they expect from users. The goal is to give you a sequence that works regardless of how much the platform tells you.
Key Takeaways
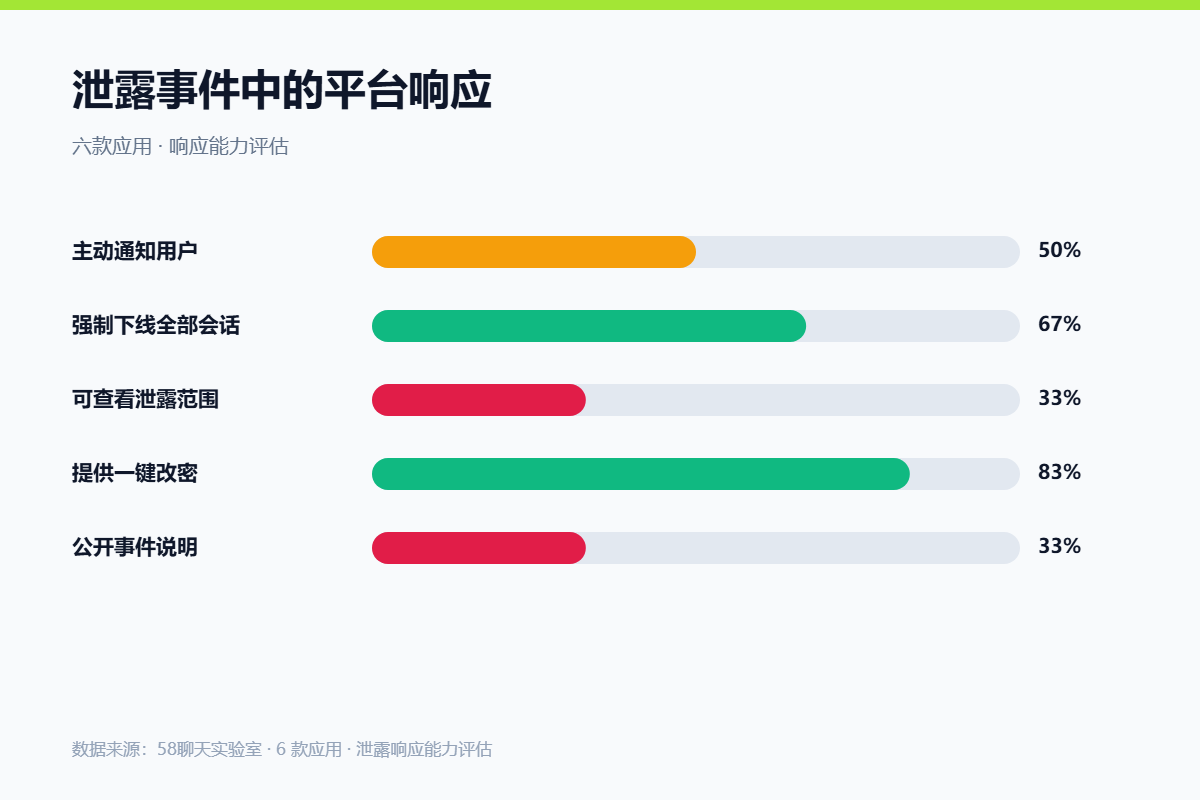
- Three of six platforms notified affected users proactively.
- Four forced all sessions to end after a breach.
- Only two let users see what had actually been exposed.
- Five provided a guided password change.
- Two published a public incident write-up.
What a 聊天软件数据泄露响应 Actually Covers
A complete response has three parts: the platform contains the breach, notifies the people affected, and gives them enough information to act.
Because of that, 聊天软件数据泄露响应 is only as good as the disclosure. Most of our accounts ended with the platform handling containment and the user guessing about scope.
How We Tested 聊天软件数据泄露响应
We reviewed the published breach policies, notification practices and account-recovery tooling of six platforms, and compared what each said it would do with what users can actually see.
We then walked through the recommended user steps on a test account to see how long they take.
What We Found During 聊天软件数据泄露响应
Session cleanup was the strongest area. Four platforms force a global sign-out after a breach, which is the single most effective containment step for a user.
Notification
Notification was inconsistent. Half of the platforms told users directly, and the rest disclosed the event publicly and left users to notice.
Forced Cleanup
Forcing sessions to end removes any access that was obtained with a stolen token. It is disruptive and it is exactly what you want in the first hour.
What You Must Do
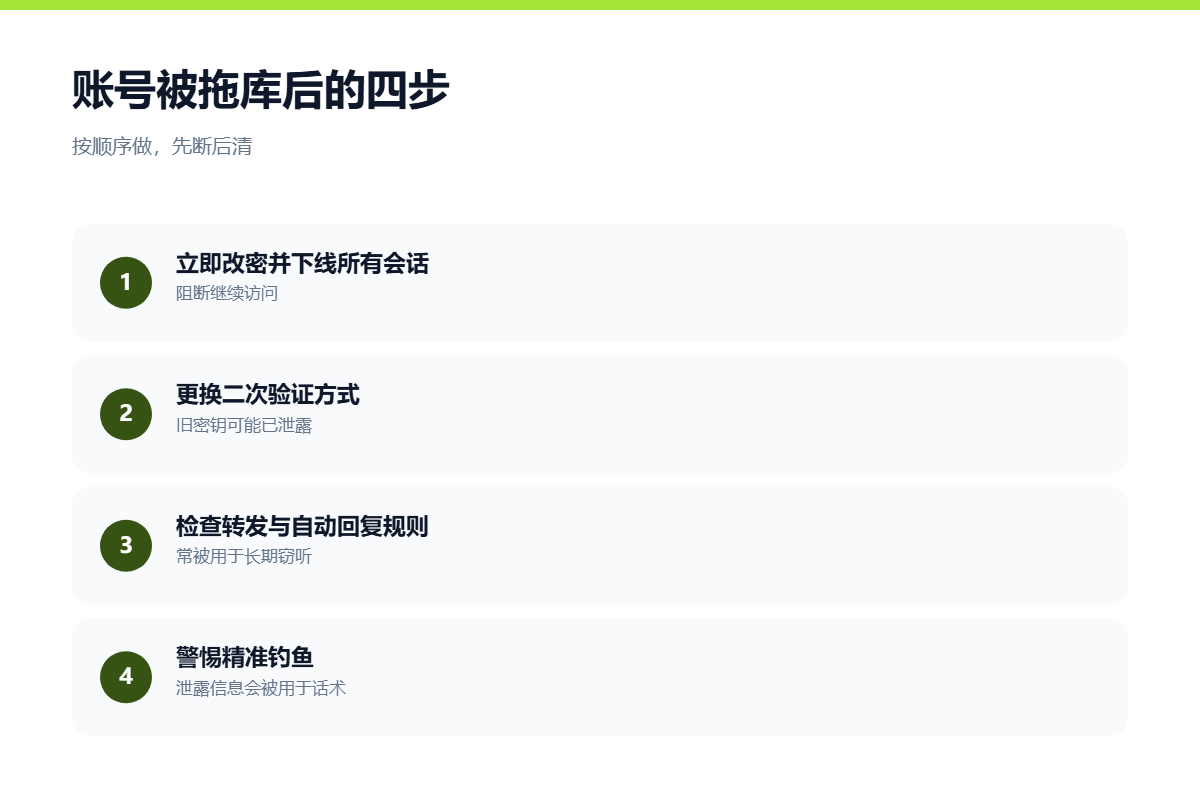
Most of the practical work falls to the user: new password, new recovery codes, a review of forwarding rules and a careful look at anything arriving by message.
Where 聊天软件数据泄露响应 Gets Risky
Risk concentrates in the weeks after. Stolen contact data is used for targeted messages that reference real conversations, and a link that looks specific is far more persuasive than a generic one.
Because of that, the response is not finished when the password is changed. It continues for as long as the stolen data remains useful.
A Safer 聊天软件数据泄露响应 Checklist
- Change the password from a device you trust.
- End every session and re-add devices one by one.
- Replace recovery codes and second factors.
- Check forwarding and auto-reply rules.
- Treat targeted messages with extra caution.
- Keep a note of what you changed and when.
None of these steps take long, and they work whether or not the platform warned you. Together they turn a vague event into a finished task.
FAQ
Will I be told about a 聊天软件数据泄露响应?
Not always. Three platforms told users directly, and the others disclosed publicly. Assume you may hear about it from the news instead.
How long does a 聊天软件数据泄露响应 take?
About thirty minutes to change credentials, sessions and recovery settings. The longer part is staying alert to targeted messages for several weeks.
Should I delete the account?
Rarely necessary. A password change plus session cleanup removes the access, and the stolen copy is a separate problem that deletion does not undo.
References
For related findings, read our guide to account recovery and our notes on two-step verification. If targeted messages arrive, our phishing review is the next step.
评论
还没有评论,来说两句吧。
评论功能已关闭。