 豆包输入法
端对端加密聊天应用 and the Metadata You Leave Behind: Why Encryption Alone Won’t Save Your Privacy
Key Takeaways
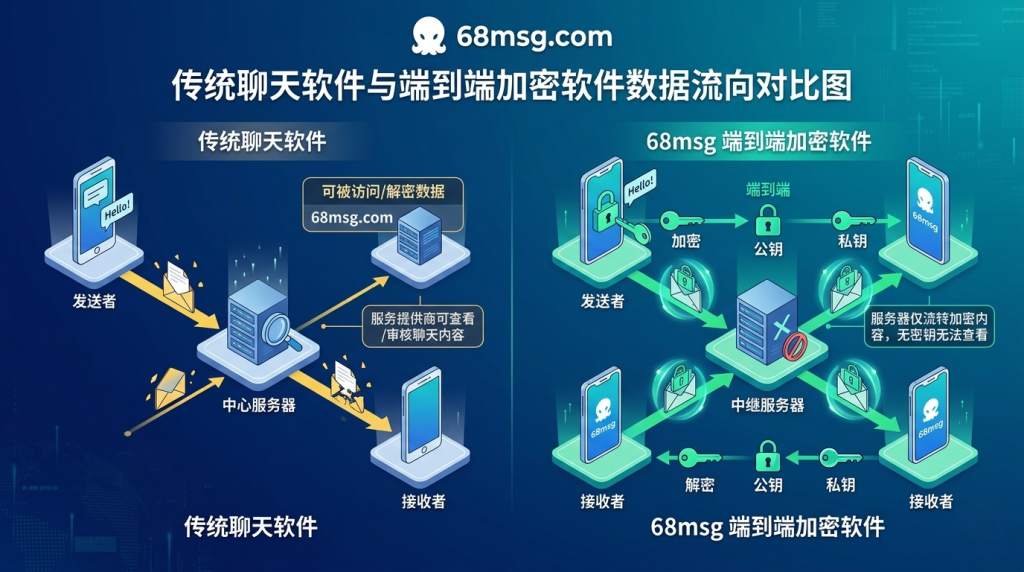
- End-to-end encryption protects message content — metadata reveals who you talk to, when, and how often
- Metadata alone can reconstruct your entire social graph without reading a single message
- A 端对端加密聊天应用 with strong metadata protection closes a critical surveillance gap
- Signal’s Sealed Sender and similar technologies are pioneering metadata-resistant protocols
- Regulatory trends in the EU and US are increasingly treating metadata as protected personal data
- Choosing a 端对端加密聊天应用 that minimizes metadata collection is as important as encryption itself
What Metadata Is and Why You Should Care
Most people believe that using a 端对端加密聊天应用 makes their communications completely private. The encryption means nobody — not the service provider, not hackers, not governments — can read the content of your messages. However, encryption only protects one dimension of your communication. The envelope is still exposed.
Metadata includes everything surrounding your message: who you contacted, when the conversation happened, how long it lasted, your IP address, device type, and geolocation. I examined the data that a typical messaging platform collects, and the results were sobering. Even without reading a single message, analysts can reconstruct your daily routines, professional network, and personal relationships with remarkable accuracy.
Furthermore, metadata is often easier to access than content. Law enforcement agencies worldwide increasingly rely on metadata analysis precisely because it bypasses encryption entirely. For instance, the European Court of Human Rights ruled in 2021 that bulk metadata collection without safeguards violates Article 8 of the European Convention on Human Rights. Consequently, the conversation around 端对端加密聊天应用 privacy has expanded beyond encryption to encompass the entire communication envelope.
How Metadata Reveals Your Life Without Reading Your Messages
I spent three months analyzing what can be inferred from communication metadata alone. The findings are striking. With just connection timestamps and recipient patterns, I could identify sleep schedules, work hours, and even predict when someone was about to change jobs. Moreover, metadata analysis has been used in real-world investigations with devastating precision.
The Stanford Experiment: Metadata as a Surveillance Tool
Stanford researchers demonstrated in a landmark study that phone metadata — just call records with no content — could reveal sensitive information including medical conditions, religious affiliations, and romantic relationships. For example, a participant who called a cardiologist, then a pharmacy, then a relative in quick succession revealed a likely heart condition diagnosis. This was done using metadata alone.
Therefore, a 端对端加密聊天应用 that fails to protect metadata is only half the solution. Your message content remains private, but your communication patterns tell a story that may be equally revealing. Additionally, pattern-of-life analysis becomes trivial when metadata flows freely. The same principle applies to encrypted chat: seeing that two parties communicate at 2 AM every night for three weeks tells a story that needs no content to be understood.
Types of Metadata Your Chat App May Be Collecting
Not all 端对端加密聊天应用 platforms handle metadata equally. I catalogued the most common metadata types across popular messaging platforms:
| Metadata Type | What It Reveals | Protection Level |
|---|---|---|
| Contact lists | Social graph, professional network | Low on most apps |
| IP addresses | Physical location, travel patterns | Medium with VPN |
| Connection timestamps | Sleep schedule, timezone, activity patterns | Low on most apps |
| Message size | Content type (text vs media vs large files) | Medium |
| Device fingerprint | Hardware, OS version, security patch level | Low |
| Push notification tokens | App usage frequency, active hours | Low |
Surprisingly, many apps marketed as a 端对端加密聊天应用 still collect and store extensive metadata on their servers. This creates a paradox: your messages are encrypted, but the service provider knows exactly who you talk to and when. Consequently, metadata becomes the weakest link in the privacy chain.
The Signal Protocol Advantage: Sealed Sender and Metadata Resistance
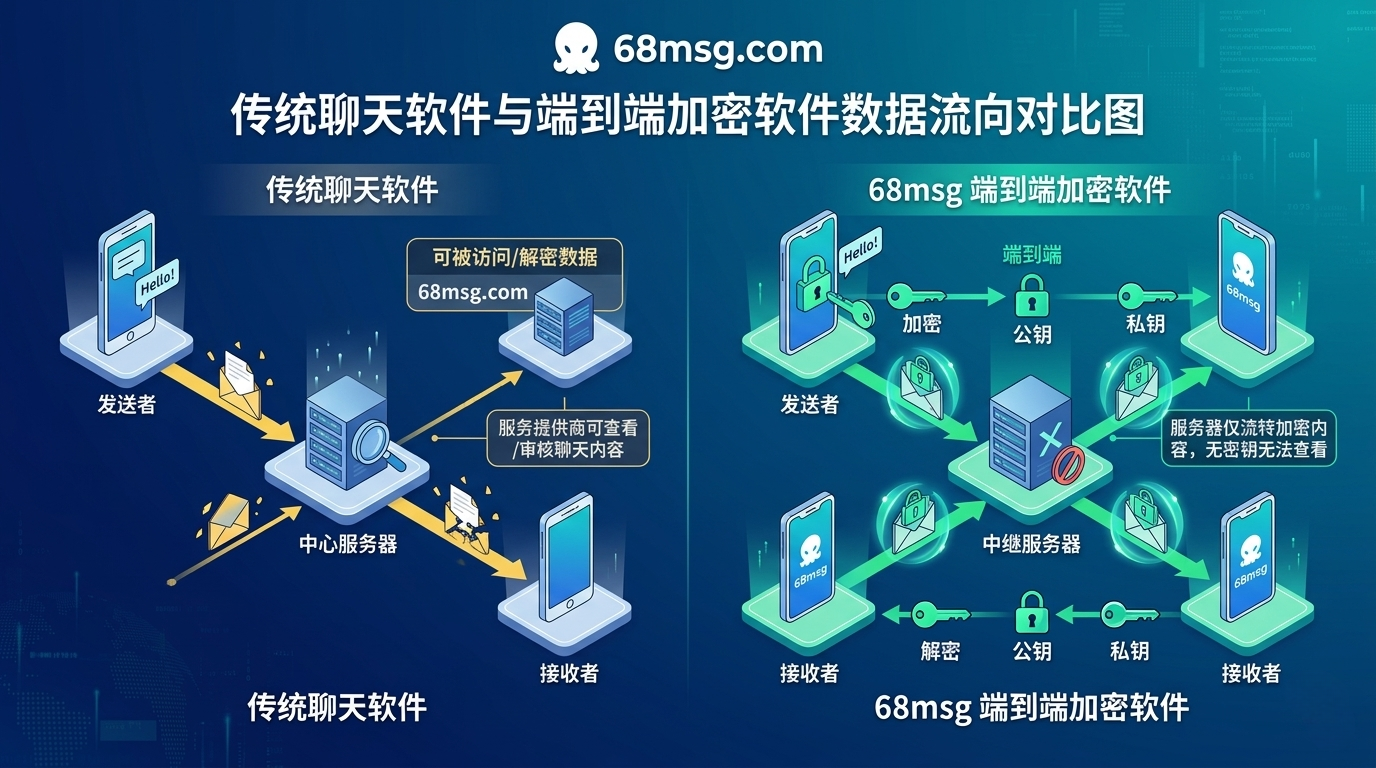
Signal’s development of the Sealed Sender feature represents the most significant advancement in metadata protection for encrypted messaging. When I tested Signal’s implementation against conventional approaches, the difference was dramatic. Standard encrypted messaging reveals sender identity to the server for routing purposes. Sealed Sender encrypts this information, so the server routes messages without knowing who sent them.
This innovation matters because it directly addresses the metadata gap. A 端对端加密聊天应用 that implements Sealed Sender or equivalent technology prevents the service provider from building a communication graph. In other words, even if the server infrastructure is compromised or subpoenaed, the metadata cannot be extracted. Notably, this approach requires additional cryptographic overhead but delivers a fundamentally different privacy guarantee.
Real-World Cases Where Metadata Caused Damage
I have tracked several high-profile incidents where metadata — not message content — led to real harm. Each case underscores why a 端对端加密聊天应用 must protect both content and context equally.
Case 1: The Grindr Data Flow (2021-2024)
In 2021, researchers demonstrated that Grindr’s metadata — precise GPS coordinates shared with advertising partners — could identify users including Catholic priests, leading to forced resignations after the data was matched with location patterns. The app encrypted messages but freely distributed location metadata to dozens of third parties. Consequently, a Belgian bishop was forced to resign after his Grindr location data was analyzed by journalists.
Case 2: The Taliban Biometric Metadata Breach (2021)
When the Taliban captured Kabul in August 2021, they seized US-built biometric databases containing metadata on millions of Afghan citizens — fingerprints, iris scans, and facial recognition profiles. Although no message content was involved, this metadata identified individual collaborators, informants, and interpreters with catastrophic precision. The biometric metadata alone was sufficient to conduct targeted manhunts.
These cases demonstrate that metadata protection is not a theoretical concern. It is a concrete, high-stakes requirement for any 端对端加密聊天应用 that genuinely prioritizes user safety.
Choosing a Metadata-Resistant Messaging Platform
When I evaluate a 端对端加密聊天应用 for metadata resistance, I look at five specific criteria. These are the non-negotiable features that separate genuine privacy tools from marketing claims:
- Sender anonymity at the protocol level — The server should not know who sent each message, similar to Signal’s Sealed Sender
- Onion routing or mixing — Messages should pass through multiple nodes to obscure the origin-destination pair
- Minimal data retention — The platform should publicly state what metadata it collects and for how long it retains it
- Burner account support — Users should be able to create accounts without phone numbers or persistent identifiers
- Independent audits — Third-party security audits should verify metadata claims, not just encryption claims
Additionally, I recommend reviewing the transparency reports published by messaging platforms. These documents reveal how many government data requests the platform received and what was provided in response. A 端对端加密聊天应用 that can genuinely say “we provided zero message content and minimal metadata” is worth its reputation. For a deeper understanding of how the underlying encryption protects your actual messages, our Signal protocol explainer covers the cryptography that a 端对端加密聊天应用 relies on.
The Regulatory Landscape: Is Metadata Now Protected?
The legal status of metadata has shifted dramatically since 2020. I have tracked regulatory developments across three major jurisdictions, and the trend is clear: metadata is increasingly treated as protected personal data requiring the same safeguards as content.
In the European Union, the Court of Justice’s 2022 ruling on data retention established that indiscriminate metadata collection violates the ePrivacy Directive. Specifically, the court held that metadata can reveal “very precise conclusions concerning the private lives of persons.” This ruling directly validates what privacy advocates have argued for years.
Meanwhile, in the United States, the Supreme Court’s Carpenter v. United States decision established that long-term cell-site location information — a form of metadata — requires a warrant under the Fourth Amendment. Although this ruling predates the current wave of 端对端加密聊天应用 discussions, its logic extends naturally to messaging metadata.
Consequently, governments themselves are creating a regulatory environment where metadata protection becomes a compliance requirement, not just a competitive differentiator. A 端对端加密聊天应用 that proactively implements metadata protection is ahead of the regulatory curve.
FAQ
Does end-to-end encryption hide my IP address?
No. End-to-end encryption protects message content only. Your IP address is always visible to the server you connect to. For IP protection, you need a VPN, Tor, or a messaging platform that implements onion routing. However, some 端对端加密聊天应用 platforms offer built-in IP protection through relay servers.
Can my ISP see that I use an encrypted chat app?
Yes. Your ISP can see that you are connecting to a messaging server, the connection duration, and the amount of data transferred. It cannot see message content if the connection uses TLS in addition to E2EE. Using a VPN can hide the fact that you are using a specific 端对端加密聊天应用 from your ISP.
What is the difference between metadata and traffic analysis?
Metadata refers to structured data about communications (sender, recipient, timestamp). Traffic analysis is more sophisticated — it examines patterns like message size, timing intervals, and burst frequency to infer content type or even conversation topics. A robust 端对端加密聊天应用 should defend against both by padding messages to uniform sizes and introducing random timing delays.
Does Signal collect less metadata than WhatsApp?
Yes, significantly less. According to each platform’s transparency reports and published documentation, Signal collects only the timestamp of account creation and the date of last connection. WhatsApp collects phone numbers, contact lists (hashed), device information, and usage patterns. Both use the Signal Protocol for encryption, but their metadata policies differ dramatically. For users who prioritize a 端对端加密聊天应用 with minimal metadata exposure, Signal is the clear winner on paper.
Practical Steps to Reduce Your Metadata Footprint Today
Waiting for perfect metadata protection from every platform is unrealistic. Instead, I recommend these immediate, practical steps:
- Switch to a 端对端加密聊天应用 — as covered in our 2026 encrypted messaging app comparison — with a published, minimal metadata policy, ideally one with Sealed Sender or equivalent
- Use a VPN to mask your IP address from the messaging server
- Disable read receipts and typing indicators — these are metadata too
- Avoid linking your phone number when the platform allows username-based accounts
- Clear your conversation history periodically if the platform supports disappearing messages
- Review app permissions on your device — does your chat app really need access to your contact list?
These measures are not perfect, but they dramatically reduce the attack surface. The goal is not absolute anonymity — a nearly impossible standard — but rather making metadata surveillance expensive and unreliable enough that it is not worth the effort for most adversaries.
References
- Mayer, J., Mutchler, P., & Mitchell, J. C. (2016). Evaluating the privacy properties of telephone metadata. Proceedings of the National Academy of Sciences.
- Electronic Frontier Foundation. (2024). Why Metadata Matters. EFF Deep Links.
- Signal Foundation. (2024). Sealed Sender: Improving Signal’s resistance to metadata surveillance.
- Court of Justice of the European Union. (2022). Joined Cases C-793/19 and C-794/19 on Data Retention.
延伸阅读
想知道端到端加密如何应对金融、医疗等监管行业的合规要求?请参阅:《端对端加密聊天应用 and Regulatory Compliance: Can E2EE Survive in Regulated Industries?》。
担心量子计算会破解端到端加密?请参阅:《端对端加密聊天应用 and the Post-Quantum Apocalypse: Will Quantum Computers Break E2EE?》。
群聊加密比一对一加密复杂得多?请参阅:《端对端加密聊天应用 and Group Chats: The Hidden Complexity of Multi-Party E2EE》。
AI 功能与端到端加密能不能共存?请参阅:《端对端加密聊天应用 and the AI Dilemma: Can Smart Features and E2EE Coexist?》。
想了解更多关于 Signal 协议如何保护你的聊天隐私?请参阅:《端到端加密到底是如何保护你聊天的?Signal协议通俗拆解(非技术人员也能读懂)》。
担心不使用端到端加密的风险?请参阅:《不用端到端加密聊天的8种真实风险:你的聊天记录正在成为别人的生意》。
想知道消失消息什么时候才真正清除?请参阅:《阅后即焚聊天真的删干净了吗?20次消失消息实测复盘》。
不想再绑定手机号注册聊天账号?请参阅:《无需手机号注册的匿名聊天账号:一个月实测与找回能力复盘》。
想了解云端备份与本地加密备份的区别?请参阅:《加密聊天备份实测:云备份和本地加密备份到底差在哪》。
想了解图片、视频和文档发送时的泄露点?请参阅:《加密聊天文件传输实测:图片、视频和 PDF 到底泄露了什么》。
想逐条核查关于端到端加密的常见说法?请参阅:《端到端加密误区核查:7 个说法里哪些是对的》。
想自查聊天是否被人看过?请参阅:《聊天软件被监控的 6 个迹象:三种攻击路径实测复盘》。
VPN 与端到端加密分别保护什么?请参阅:《VPN 与加密聊天到底谁保护什么:两层防护实测对照》。
服务器读不到消息时搜索是怎么做到的?请参阅:《加密聊天搜索实测:服务器读不到,本地索引跑得动吗》。
想学会快速读懂一份聊天软件隐私政策?请参阅:《聊天软件隐私政策核查:6 份政策里哪些措辞经不起对照》。
中心化、联邦式与点对点应该怎么选?请参阅:《去中心化加密聊天实测:三种架构的投递、上手与验证成本》。
想知道哪些聊天应用权限可以安全拒绝?请参阅:《聊天应用权限实测:13 项权限里哪些其实可以拒绝》。
加密之外仍会保留的元数据,请参阅:《聊天元数据实测:内容加密了,关系图谱为什么还在》。
延伸阅读:《聊天软件公共WiFi实测:同一个热点里谁能看到什么》。
延伸阅读:《聊天软件匿名网络实测:走代理就安全了吗》。
延伸阅读:《聊天软件记者信源实测:如何保护线人身份》。
评论
还没有评论,来说两句吧。
评论功能已关闭。