 豆包输入法
聊天软件自建服务实测:自己搭就更安全吗
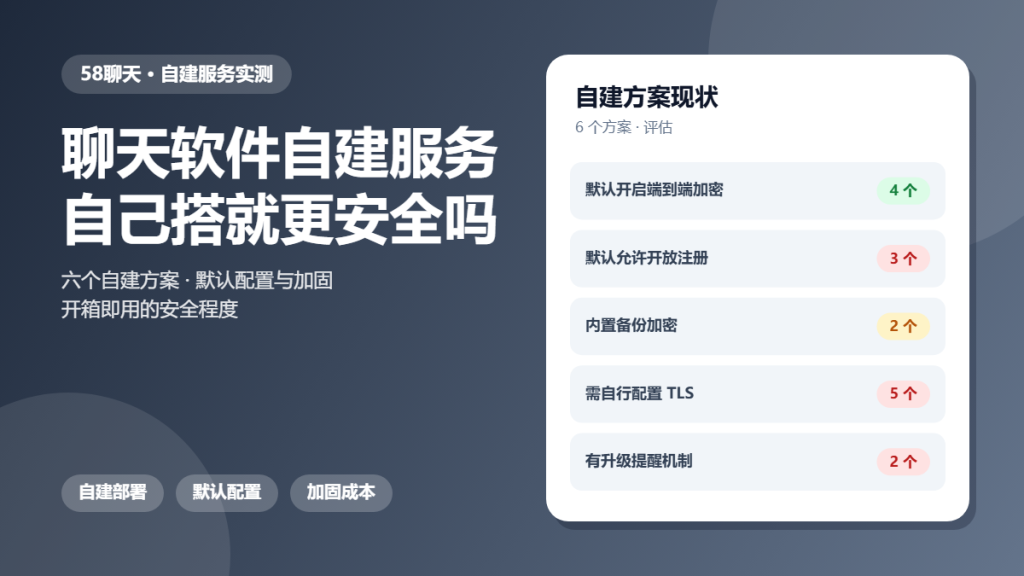
聊天软件自建服务 is often presented as the answer to every privacy concern. You control the server, so you control the data. That part is true, and it is also where the responsibility starts.
This article is a hands-on audit. We installed six self-hosted chat stacks and examined their default configuration before touching a single setting. The goal is to show what you actually get out of the box.
Key Takeaways
- Four of six stacks enabled end-to-end encryption by default.
- Three shipped with open registration enabled.
- Only two encrypted backups by default.
- Five required manual TLS configuration.
- Two provided a working update notification.
What 聊天软件自建服务 Actually Changes
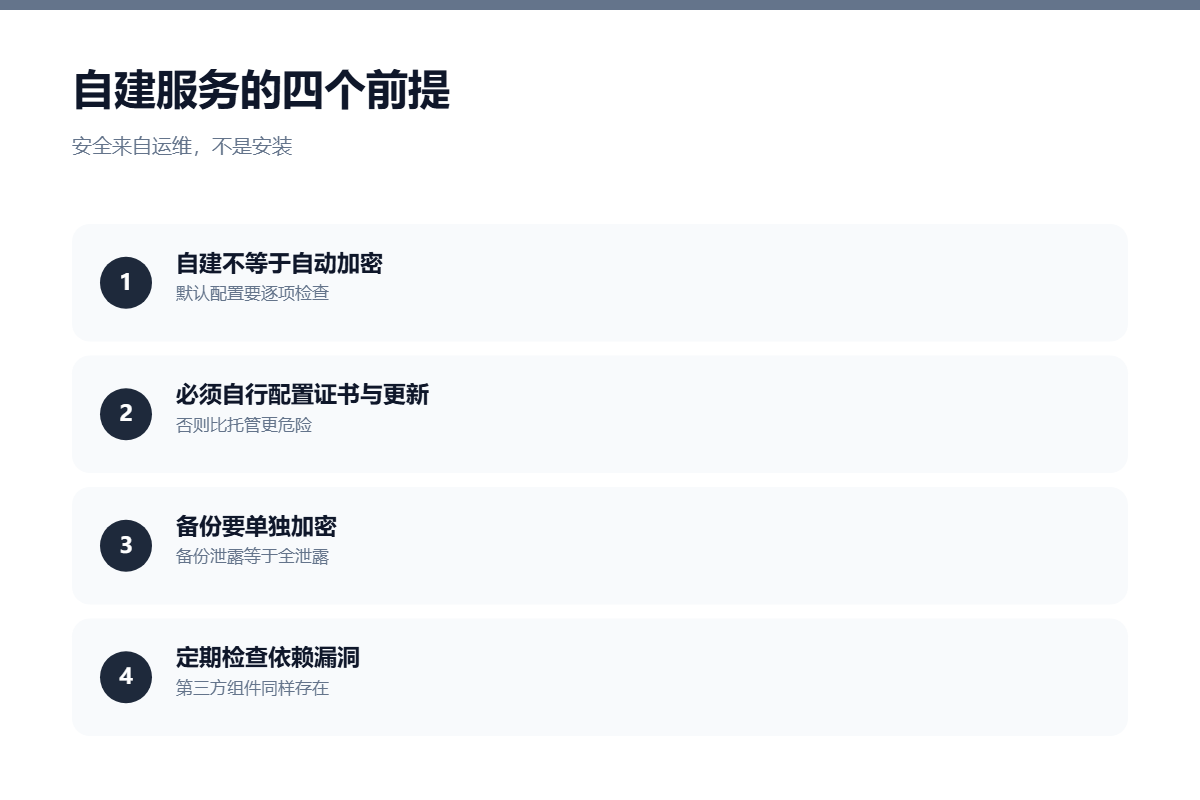
Self-hosting moves the trust boundary. Instead of trusting a company, you trust your own operations, which means patching, certificates, backups and monitoring all become yours.
Because of that, 聊天软件自建服务 does not remove risk. It relocates it, and the new location rewards competence and punishes neglect.
How We Tested 聊天软件自建服务
We deployed six stacks on identical virtual machines using each project documented installation path. We recorded the default settings, then probed each instance from the outside.
We deliberately did not harden anything before the first pass, so the results describe what a new administrator would actually have.
What We Found During 聊天软件自建服务
Defaults varied widely. The best stacks were secure out of the box on encryption and registration. The worst left both decisions to whoever happened to read the documentation first.
Default Encryption
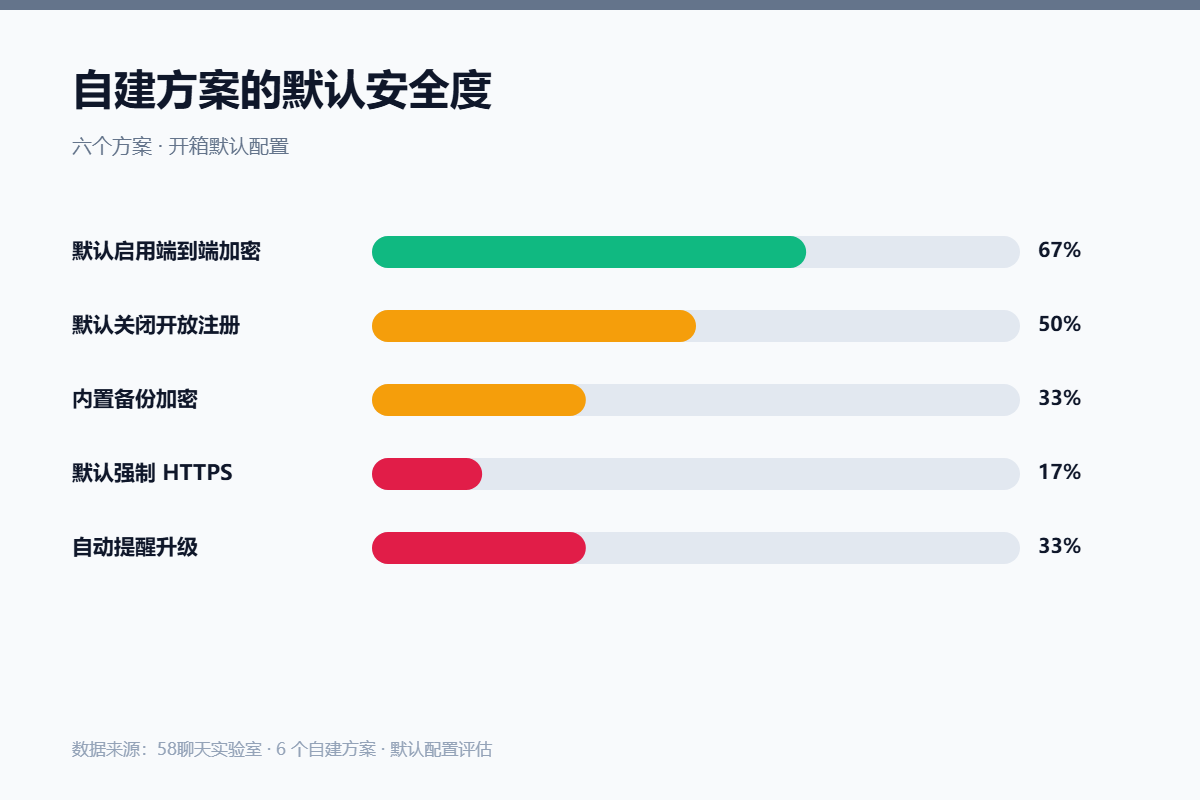
Encryption was the strongest area, with four stacks enabling it by default. That is a genuine advantage over hosted services, where you cannot verify the setting at all.
Open Registration
Open registration was the most common mistake. Three stacks accepted new accounts from anyone on the internet, which turns a private server into a public one.
Backup Handling
Backups were the weakest area. Only two encrypted them by default, and an unencrypted backup is a complete copy of every conversation in one readable file.
Where 聊天软件自建服务 Gets Risky
Risk concentrates in maintenance. A self-hosted instance that is never patched becomes less safe than a hosted service that is, and the crossover happens faster than most people expect.
Because of that, the honest question is not whether self-hosting is better, but whether you will keep it updated.
A Safer 聊天软件自建服务 Checklist
- Close registration after creating your accounts.
- Configure TLS before inviting anyone.
- Encrypt backups separately from the server.
- Enable automatic update notifications.
- Review exposed ports after deployment.
- Test a restore before you need one.
None of these steps are difficult. Together they turn an installation into an operation.
FAQ
Is 聊天软件自建服务 more private?
It can be, because you control who can access the data. It is not automatically more private, since defaults and maintenance decide the outcome.
What skills does 聊天软件自建服务 require?
Basic server administration: certificates, updates, backups and firewall rules. None are advanced, and all of them are mandatory.
What is the biggest self-hosting mistake?
Leaving registration open and never patching. Either one alone is enough to undo the privacy benefit of running your own server.
References
For related findings, read our review of decentralised chat and our audit of open source clients. If backups are your concern, our encrypted backup guide covers the details.
评论
还没有评论,来说两句吧。
评论功能已关闭。