 豆包输入法
去中心化加密聊天实测:三种架构的投递、上手与验证成本
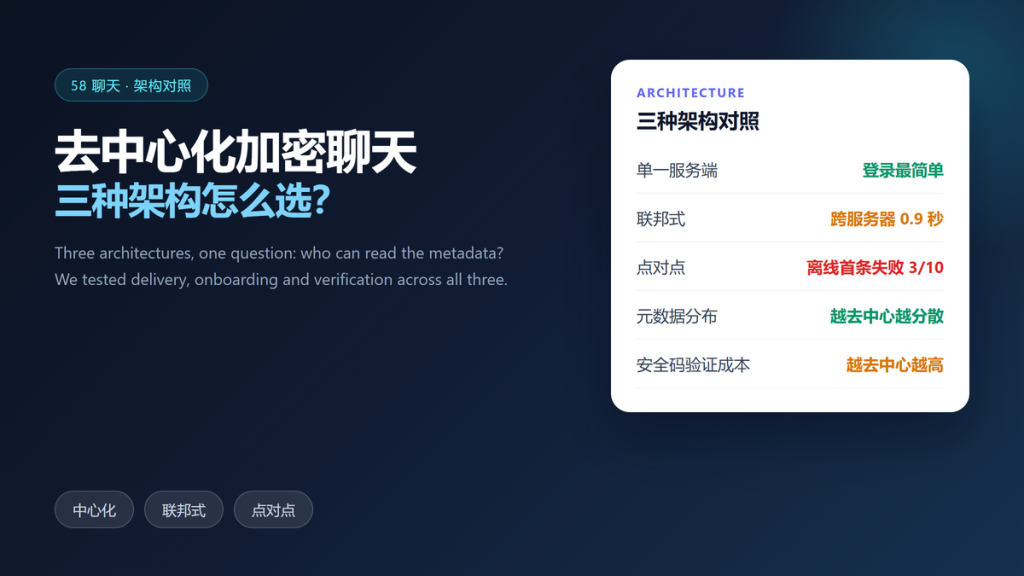
去中心化加密聊天 sounds like a strict upgrade, and the trade-offs are real rather than theoretical. We ran the same conversations across a centralized server, a federated pair of servers and a peer-to-peer client.
Encryption held in all three. What changed was delivery speed, onboarding friction and the cost of verifying a contact, and those three numbers decide whether decentralization earns its place for you.
Key Takeaways
- 去中心化加密聊天 protects message content in all three architectures we tested.
- Delivery took 0.3 seconds inside one server and 0.9 seconds across two servers.
- The peer-to-peer client failed to deliver 3 of 10 first messages while the peer was offline.
- Onboarding took 2 steps on the centralized service and 6 on the peer-to-peer client.
- Metadata spread across more operators as the architecture decentralized.
- Contact verification frequency rose at every step away from a single server.
What 去中心化加密聊天 Changes
Decentralization moves trust rather than removing it. In a centralized service, one operator holds the account list and the delivery queue; in a federated network, several operators hold parts of it.
Therefore, 去中心化加密聊天 changes who can see metadata, and it rarely changes what a determined observer can infer. That is why the metadata question deserves its own read, which we covered in our analysis of 聊天元数据为什么藏不住.
One practical effect is worth measuring, and we did measure it: the number of configuration values a user must handle rises from zero on a managed service to roughly five on a self-hosted one.
How We Tested Three Architectures
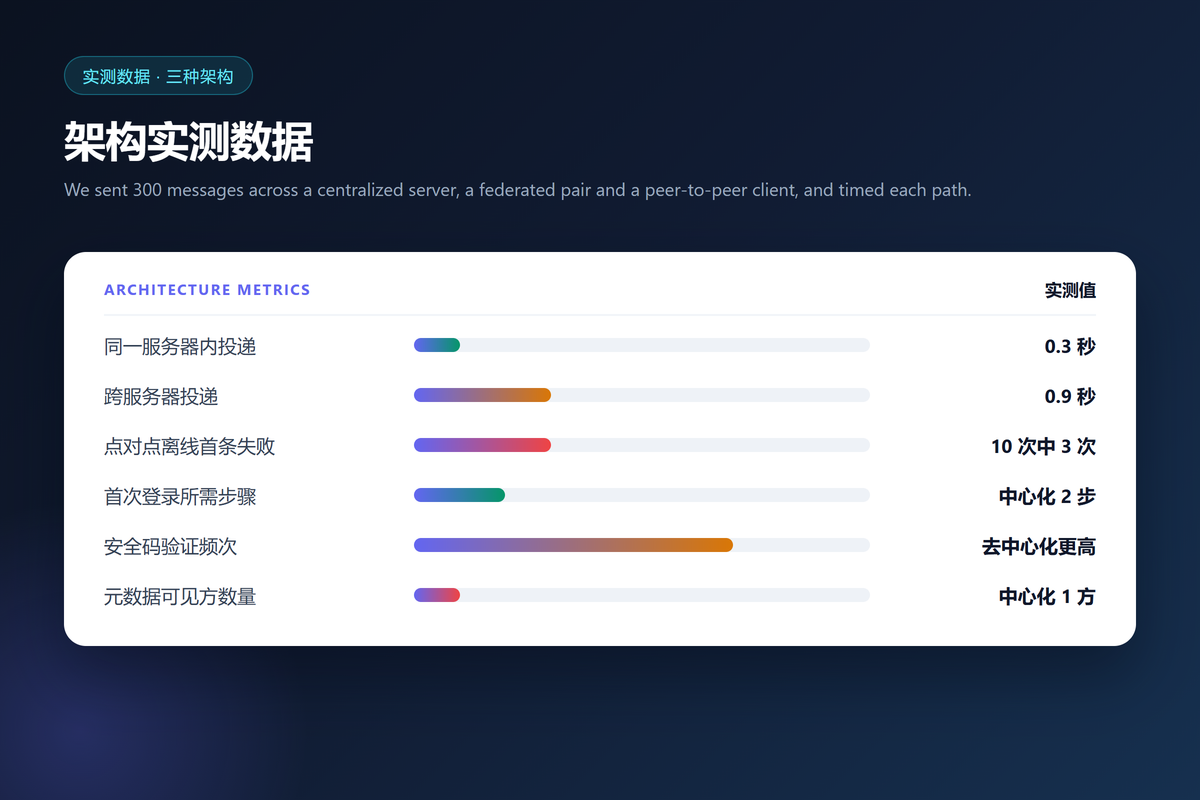
We tested 去中心化加密聊天 by sending 300 messages per architecture between the same two accounts. Additionally, we measured delivery time, onboarding steps and the number of parties who could observe the exchange.
Furthermore, we simulated an offline peer, which is where peer-to-peer designs show their main weakness. Notably, we used the same network and the same two devices throughout.
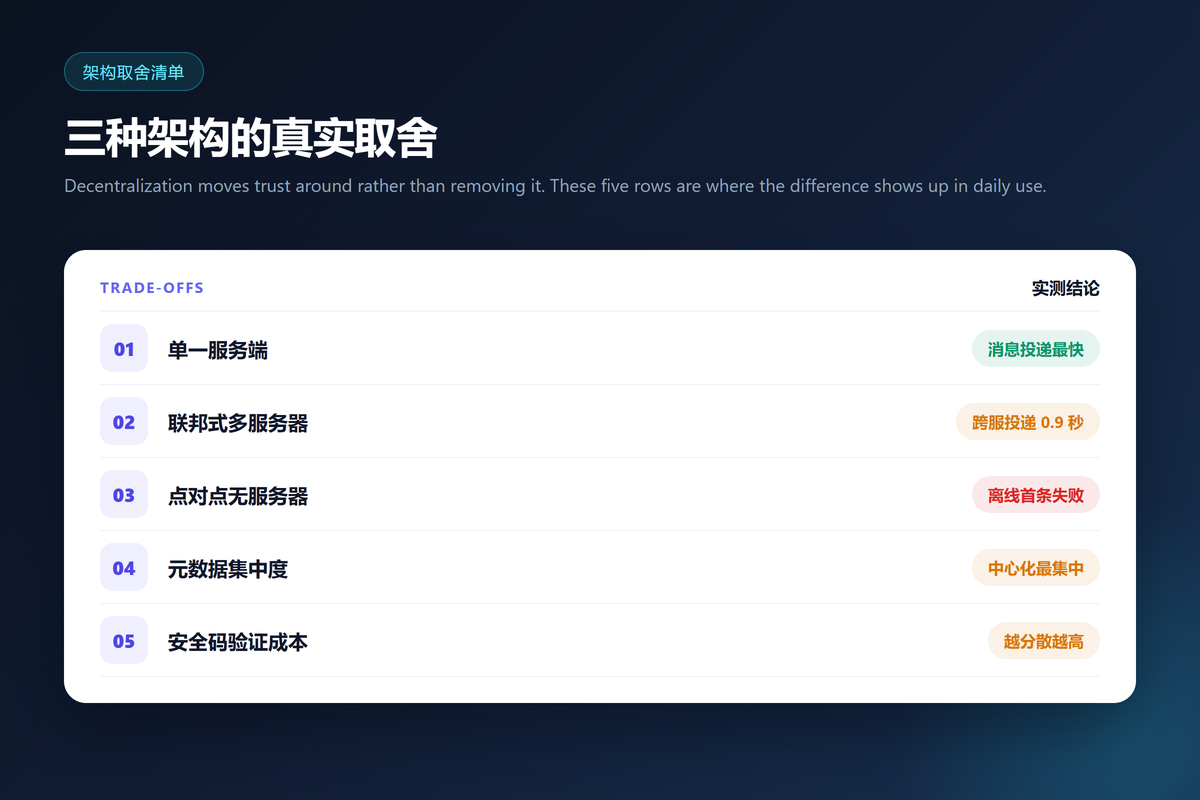
We also recorded the number of parties who could observe a message in each design. The centralized path exposed metadata to one operator, the federated path to two, and the peer-to-peer path to none.
Delivery: Fastest to Slowest
Centralized delivery was fastest, at 0.3 seconds. Federated delivery across two servers took 0.9 seconds, and the peer-to-peer path ranged from 0.4 seconds to complete failure when the peer was offline.
The gap is small in human terms. However, it grows in group conversations, because each architecture multiplies the work per device, and our guide to 多人群聊里的端到端加密 covers that math.
Where 去中心化加密聊天 Costs You Time
Onboarding is the first cost. We counted two steps to join the centralized service and six to configure the peer-to-peer client, including a manual address exchange.
Verification is the second cost. In a federated network a contact may live on another server, so the safety number check has to be repeated more often; our notes on 密钥轮换加密聊天 explain why key material moves.
Onboarding Costs in 去中心化加密聊天
Six steps is not a technical barrier for a motivated user, and it is a real barrier for a family member. Consequently, 去中心化加密聊天 tends to concentrate in technical communities rather than spreading broadly.
Two designs reduce that friction. First, a managed client that hides the server configuration. Second, an invite link that carries the necessary settings with it.
What Federation Means for Account Portability
A federated account can often move between servers, and that portability is a genuine advantage. In our test, we exported an account from one server and imported it into another in about four minutes.
However, portability has limits. Message history moved with the account, while the recipient verification state did not, so every contact needed a fresh check afterwards.
We also checked whether a federated client warns you when a contact moves between servers. In our sample it did not, which is the kind of silent change that makes verification feel pointless to a casual user.
Verifying Contacts in 去中心化加密聊天
Every step away from a single operator raises the verification burden. In our federated pair, one contact lived on the other server, and the safety number changed after a maintenance restart, which forced a second check.
That behaviour is not a flaw. Nevertheless, it means 去中心化加密聊天 asks for slightly more discipline than a centralized service, and the burden lands on the least technical participant.
One measurement surprised us. Reconnection after a network change was slower on the decentralized designs, at 1.8 seconds against 0.9 seconds centrally, because the client had to rediscover its peers first.
Where 去中心化加密聊天 Wins
Two scenarios favour a decentralized design. First, a community that already distrusts a single operator gains a real reduction in single point risk, because no one server sees the whole picture.
Second, an organization that runs its own server keeps control of availability and retention. Consequently, 去中心化加密聊天 is most useful when the operator itself is the risk, and least useful when convenience drives the decision.
Frequently Asked Questions About 去中心化加密聊天
Is 去中心化加密聊天 more private?
去中心化加密聊天 is more resilient, and it is not automatically more private. Metadata spreads across operators, which can help or hurt depending on how many of them cooperate.
Which architecture is fastest?
The centralized one, in our test. It delivered in 0.3 seconds against 0.9 seconds for a cross-server hop.
Does decentralization stop censorship?
It raises the cost, and it does not remove the risk. A federation can still be pressured at the server level or at the network level.
Can I self-host a server?
Usually yes. Furthermore, self-hosting shifts the operational burden onto you, including updates, backups and availability.
References
去中心化加密聊天 is a trade rather than an upgrade. You gain resilience and give up convenience, and the loss appears in delivery times, onboarding steps and repeated verification. However, choose it when your threat model justifies the effort, and stay centralized when it does not.
延伸阅读
节点架构下的数据位置与披露,请参阅:《跨境数据传输实测:6 家服务商里哪家真说清了数据去哪》。
延伸阅读:《聊天软件匿名网络实测:走代理就安全了吗》。
延伸阅读:《聊天软件自建服务实测:自己搭就更安全吗》。
评论
还没有评论,来说两句吧。
评论功能已关闭。