 豆包输入法
聊天软件短信拦截实测:验证码是怎么被截走的
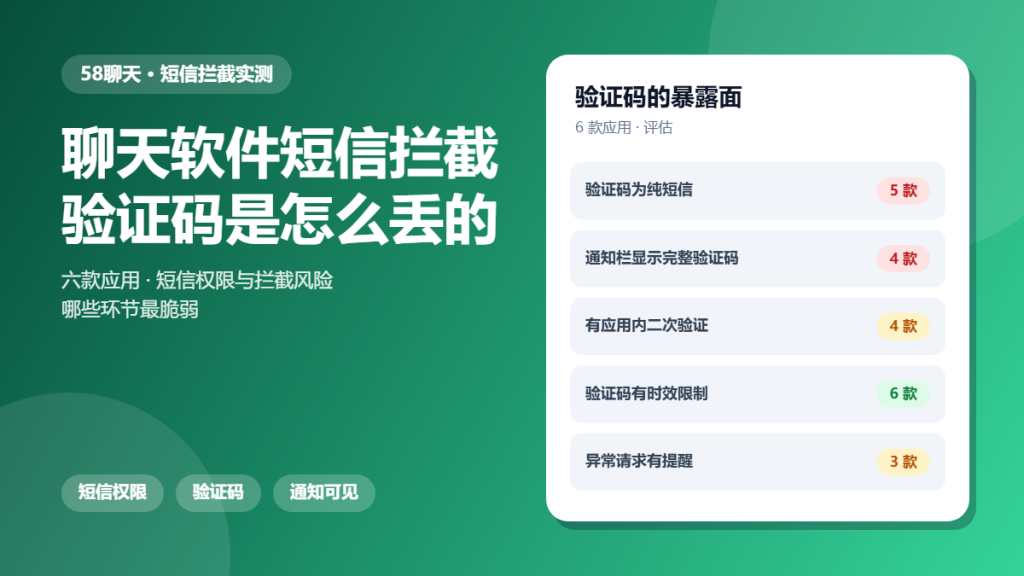
聊天软件短信拦截 is rarely a single dramatic attack. It is usually one weak link in a chain: a code sent by text, shown on a lock screen, or read by something already on the phone.
This article is a hands-on audit. We reviewed six apps for how codes are delivered, how they appear and what alternatives exist. The goal is to show where the weakest link actually sits.
Key Takeaways
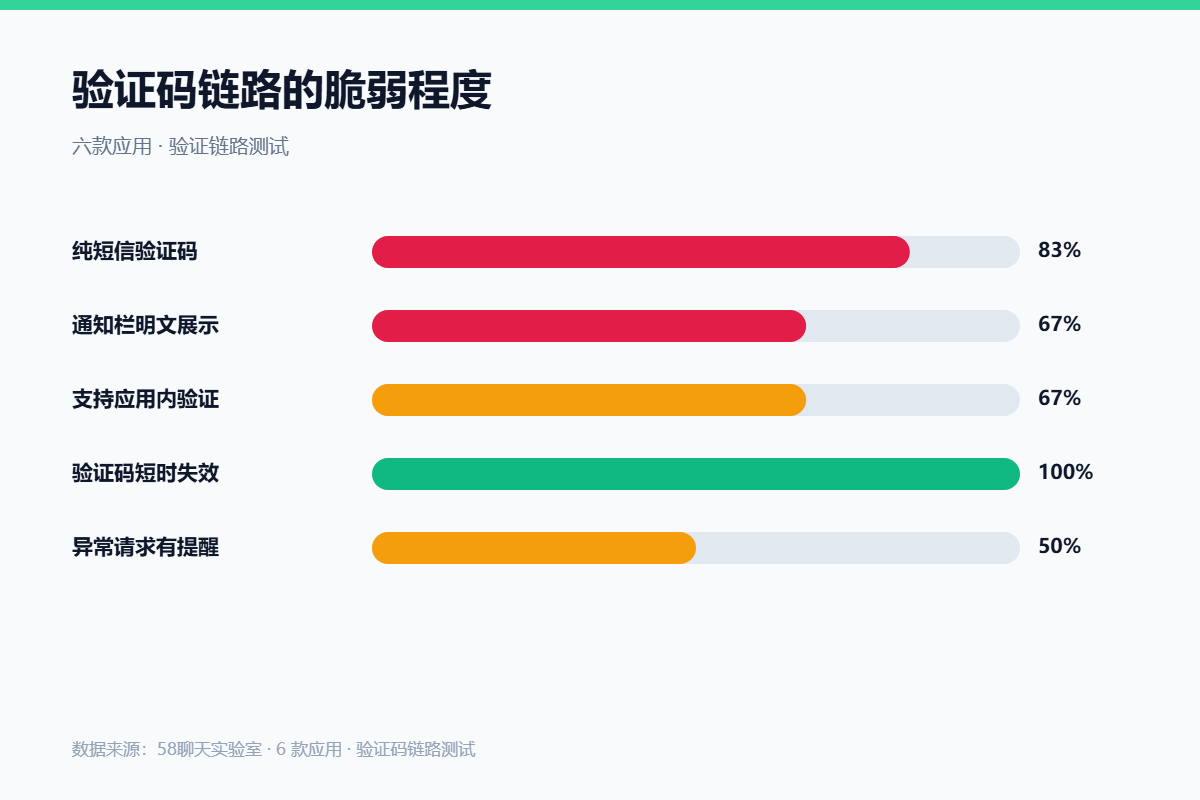
- Five of six apps relied on SMS as the default verification channel.
- Four displayed the full code in a notification.
- Four offered an in-app alternative to SMS.
- Every code expired within a short window.
- Three alerted the user to unexpected verification requests.
What 聊天软件短信拦截 Actually Targets
A verification code is a one-time password. It proves control of a channel, and the value of the code is entirely tied to whether that channel is private.
Because of that, 聊天软件短信拦截 is really a question about channel privacy. A code read from a lock screen has the same effect as a code read from the message itself.
How We Tested 聊天软件短信拦截
We triggered verification flows on six apps and recorded how each code arrived, how long it lasted and whether the app offered a route that did not use SMS.
We also checked what appeared in notifications while the device was locked.
What We Found During 聊天软件短信拦截
Delivery was predictable and exposure was avoidable. Most apps sent a text and simultaneously posted a notification containing the same digits.
Delivery Channel
SMS remains the default because it works everywhere. It is also the least private channel, since the message is readable by the carrier and by anything with SMS access.
Notification Exposure
Notification exposure is the easiest fix and the most commonly ignored. Hiding content on the lock screen removes a code from view without affecting anything else.
Alternative Factors
Four apps offered an in-app confirmation instead of a text. That route never leaves the app, which removes the carrier and the SMS inbox from the chain entirely.
Where 聊天软件短信拦截 Gets Risky
Risk concentrates when the code is the only barrier. If an attacker already knows the password and the code arrives on an exposed channel, nothing else stands in the way.
Because of that, the practical combination is a non-SMS factor plus a hidden lock screen. Together they remove both the channel and the visible copy.
A Safer 聊天软件短信拦截 Checklist
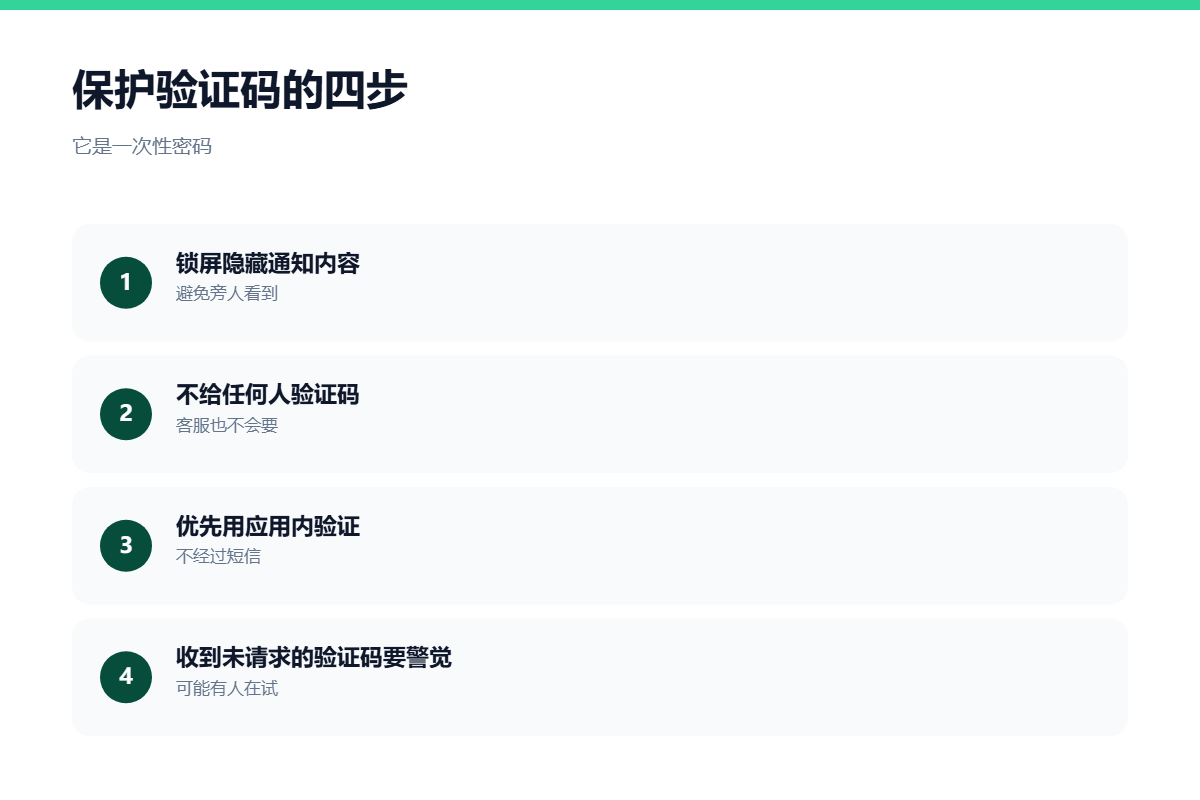
- Hide notification content on the lock screen.
- Choose an in-app factor over SMS.
- Never share a code with anyone.
- Treat an unrequested code as a warning.
- Keep the SMS app free of unknown senders.
- Check for SMS-related permissions in other apps.
None of these steps slow down logging in. Together they close the easiest path to a stolen code.
FAQ
Can malware read my SMS in 聊天软件短信拦截?
It can if it holds SMS permission. On modern systems that permission is restricted, and the notification listener is the more common route, which is why hiding notification content matters.
Do I need SMS for 聊天软件短信拦截 at all?
Not always. Four of six apps offered an in-app alternative, and using it removes the SMS channel from the verification path completely.
Why did I get a code I did not request?
Somebody may be trying to sign in as you. Do not share the code, change your password if it repeats, and check the login device list.
References
For related findings, read our notes on SIM swap attacks and our audit of notification privacy. If a code was already shared, our takeover recovery guide is the next step.
评论
还没有评论,来说两句吧。
评论功能已关闭。