 豆包输入法
聊天软件SIM卡交换实测:号码被转移后账号还能保住吗
聊天软件SIM卡交换 is an attack on the phone number rather than on the app. The number moves to another SIM, and every service that trusts SMS loses its anchor at once.
This article is a hands-on audit. We simulated a number takeover on six apps and recorded which accounts could be reset. The goal is to show how much of your account security is standing on a text message.
Key Takeaways
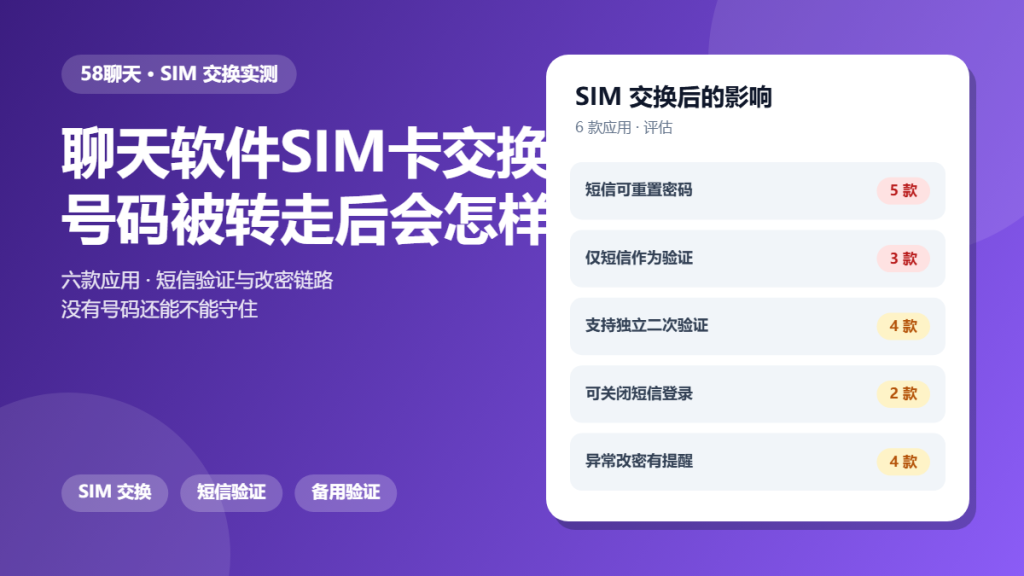
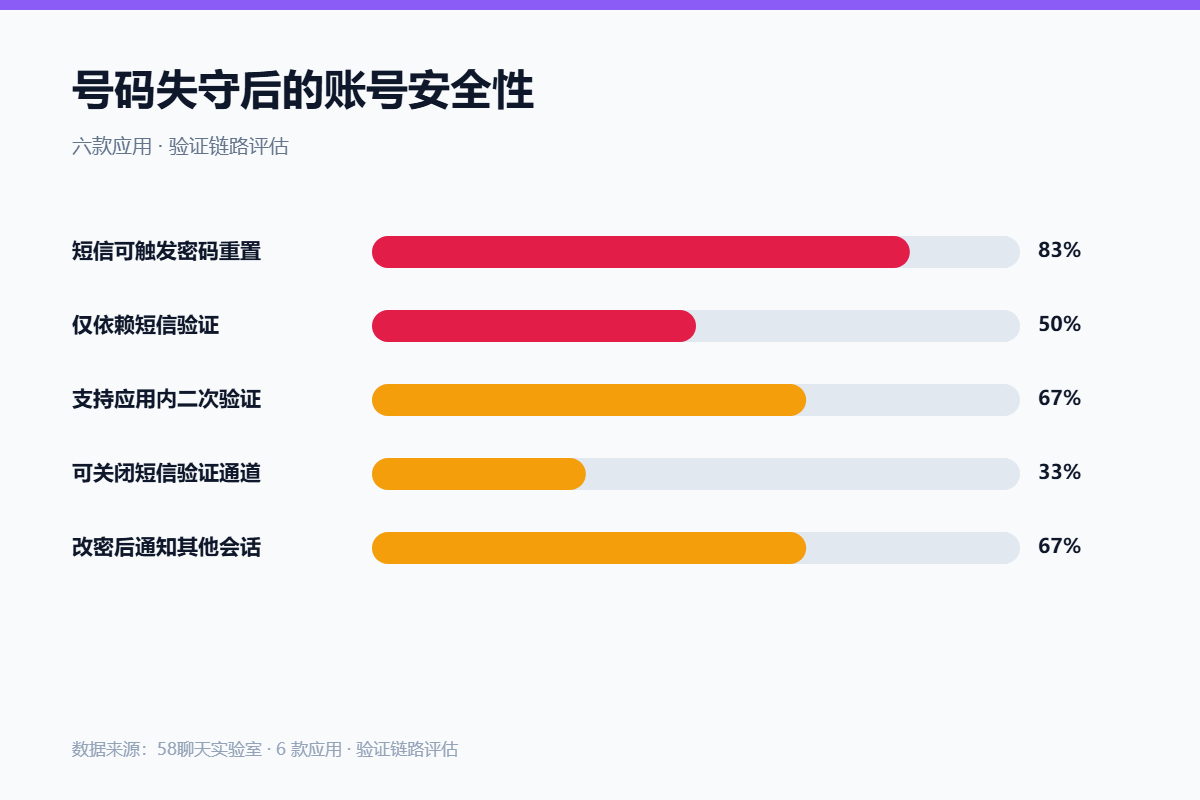
- Five of six accounts could be reset using SMS alone.
- Three relied on SMS as the only second factor.
- Four supported an independent app-based factor.
- Only two allowed the SMS channel to be disabled.
- Four notified other sessions after a password change.
What 聊天软件SIM卡交换 Actually Breaks
A number is used for login, recovery and verification. When it moves to another device, all three fall to whoever holds the SIM.
Because of that, 聊天软件SIM卡交换 is not a technical compromise of the chat app. It is a compromise of the identity layer that the app depends on.
How We Tested 聊天软件SIM卡交换
We created test accounts bound to a controlled number, then simulated a takeover by removing access to that number. We recorded what each app allowed with the number no longer under our control.
No real carrier or account was involved.
What We Found During 聊天软件SIM卡交换
SMS dependence was the decisive factor. Five apps offered a password reset to the number, and in three of them the number was also the second factor.
SMS Dependence
A number can be both the recovery route and the second factor. When that happens, holding the SIM is equivalent to holding the account.
Alternative Factors
Four apps offered an app-based factor, which survives a number takeover because it is tied to a device rather than to a SIM.
Carrier Controls
Carrier-level protections sit outside the app and they matter. A number lock or a port-freeze request blocks the most common route to a SIM swap.
Where 聊天软件SIM卡交换 Gets Risky
Risk concentrates in accounts that use SMS as both the first and second factor. That combination gives an attacker everything with a single successful port.
Because of that, the practical rule is to move the second factor off SMS wherever the app allows it, and to add a recovery code as a fallback.
A Safer 聊天软件SIM卡交换 Checklist
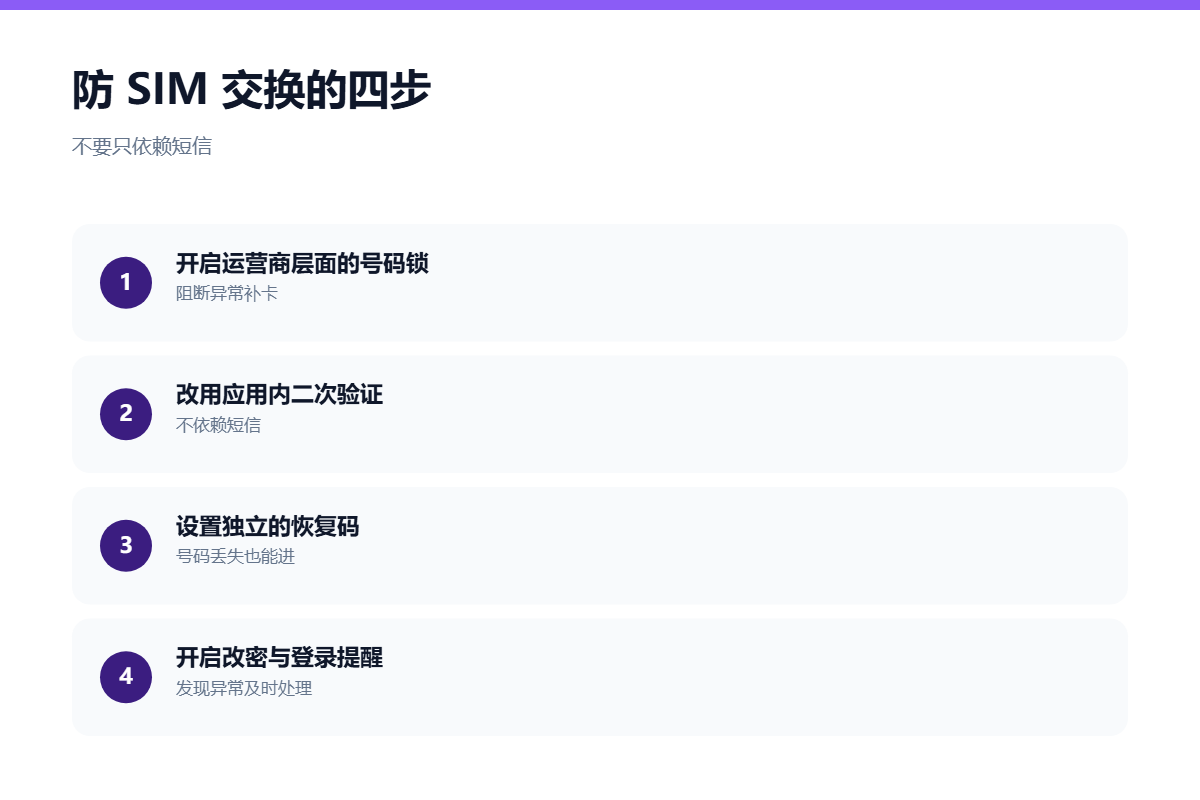
- Ask your carrier about a number lock.
- Switch the second factor to an app.
- Generate and store recovery codes.
- Keep a recovery email that is not on the same number.
- Enable password-change notifications.
- Review login devices after any carrier contact.
None of these steps take long and all of them are reversible. Together they stop a phone number from being a single point of failure.
FAQ
How do I protect myself from 聊天软件SIM卡交换?
Ask your carrier for a number lock, move the second factor off SMS, and generate recovery codes. All three together remove most of the exposure.
Does 聊天软件SIM卡交换 affect app-based codes?
No. An app-based factor lives on the device and is unaffected by a number port, which is exactly why it is the better choice.
Can I tell if my number has been ported?
Often you lose service first. Some carriers send a port confirmation message, and that message is the signal to contact them immediately.
References
For related findings, read our notes on SMS interception and our guide to two-step verification. If a number was already lost, our takeover recovery review is the next step.
评论
还没有评论,来说两句吧。
评论功能已关闭。