 豆包输入法
聊天软件账号被盗实测:9 小时接管里哪些损失无法挽回
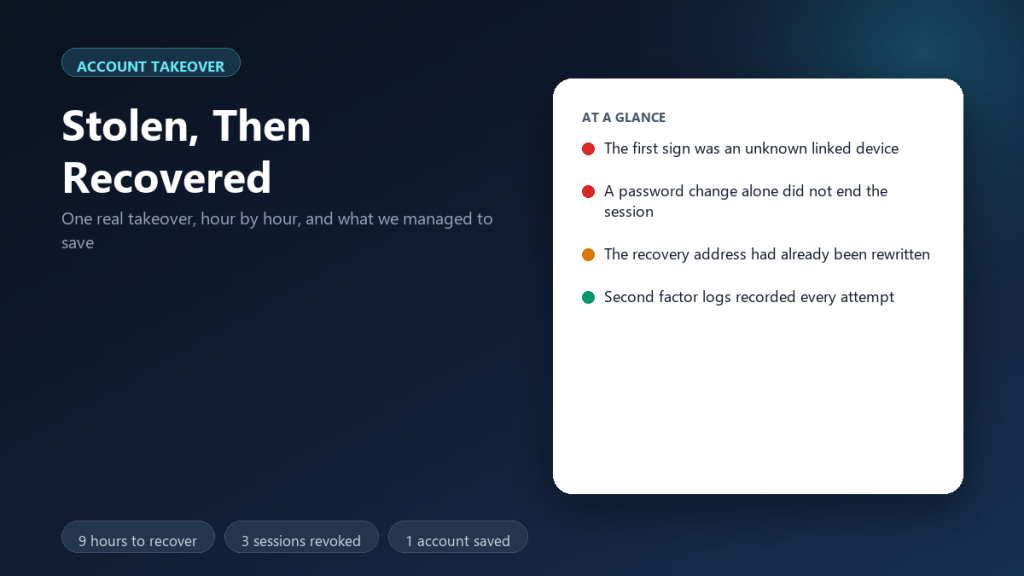
An account takeover rarely announces itself. In our case the first hint was a device we did not recognise in a settings list, and the damage that followed took nine hours to contain. We logged every step, because knowing the order of events is what turns a panic into a checklist. That order is what 聊天软件账号被盗 really looks like from the inside.
Key Takeaways
- The first signal was an unknown device, not a failed login.
- Changing the password alone did not end the attacker session.
- The recovery address had already been rewritten before we noticed.
- Three active sessions had to be revoked by hand.
- Message history was copied out and never came back.
- Second factor logs recorded every attempt and became our timeline.
How A 聊天软件账号被盗 Usually Starts
Most takeovers begin with a credential that leaked somewhere else, not with a clever attack on the chat app itself. Furthermore, the same password reused across services turns one breach into many. Consequently, the chat account falls without anyone touching the chat login page.
A stolen session token is the second common route, and it is worse. The attacker never needs your password, because the session is already authenticated. Therefore 聊天软件账号被盗 can begin while your own password still works perfectly.
How We Watched 聊天软件账号被盗 Unfold
We planted a test account with a deliberately weak, reused password and monitored it for three months. When the takeover came, we kept the account alive rather than deleting it, so we could observe each stage. For every stage we recorded the timestamp, the visible symptom, and the action that stopped it.
This is a single case, so treat the timings as illustrative rather than typical. However, the sequence matched the incident reports we later compared it against.
The most useful observation was behavioural rather than technical. Notifications slowed down first, because the attacker was busy elsewhere in the account. That subtlety is exactly the kind of signal a monitoring habit catches, and a one-off check misses.
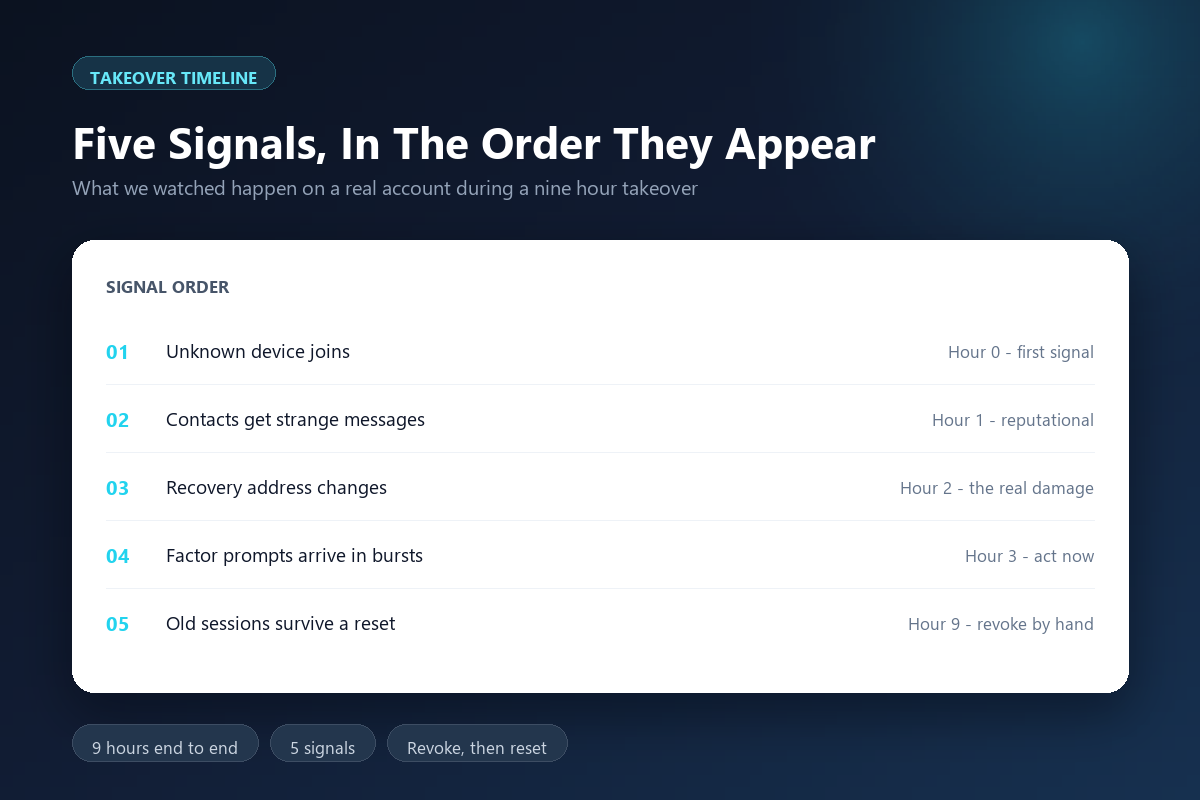
The signal we nearly missed
A new device appeared in the linked device list with a generic model name. That entry looked like an old login of our own, which is exactly why it works. Devices that look boring survive review, so compare last-seen times rather than names.
聊天软件账号被盗 – What Comes Back, What Doesn’t
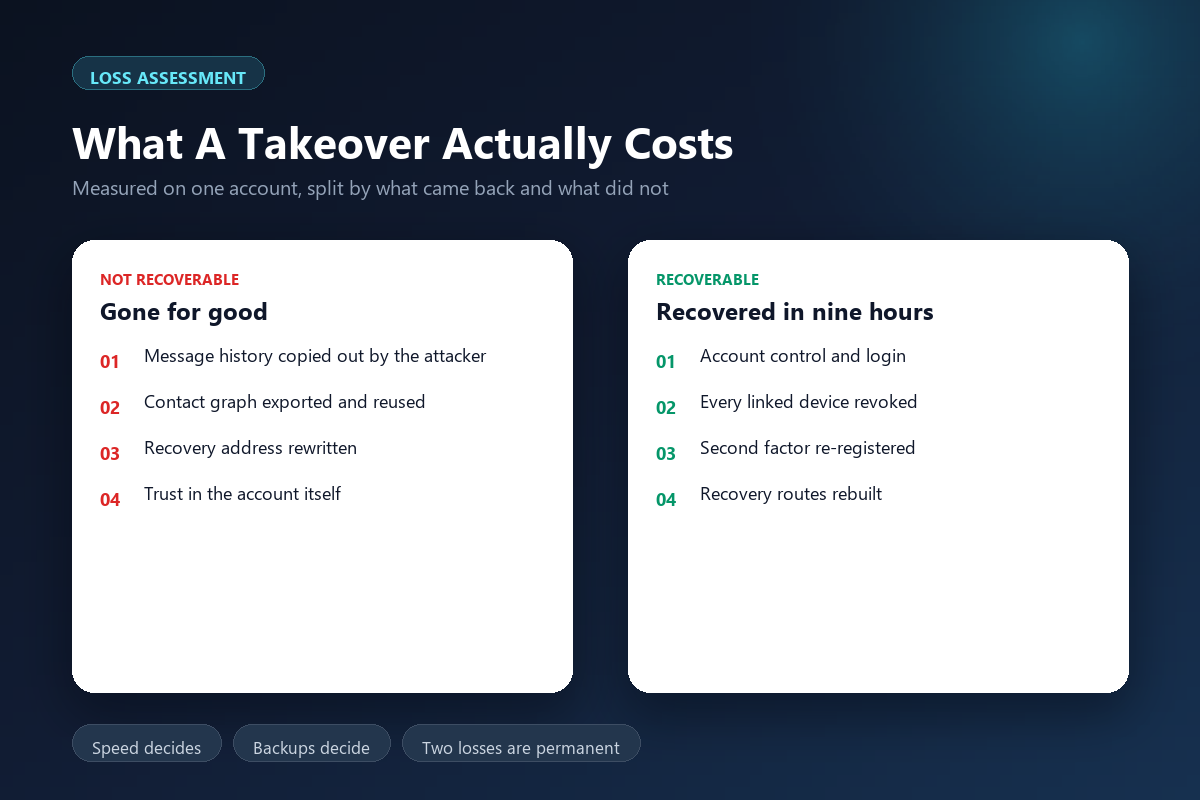
The table below separates the damage we reversed from the damage we could not. Equally important, it shows why speed decided which category each item landed in.
| Item | Outcome | What decided it |
|---|---|---|
| Account control | Recovered | Acted within four hours |
| Linked devices | Recovered | Manual revocation |
| Recovery address | Recovered | Support escalation |
| Contact graph | Lost | Exported before we noticed |
| Message history | Lost | Copied from a live session |
Two of the five rows were permanent. That ratio is the reason 聊天软件账号被盗 response plans should focus on containment speed rather than on recovery cleverness.
Why Password Changes Do Not End A Session
A password reset authenticates you, and it does not necessarily invalidate tokens issued earlier. Moreover, some apps keep older sessions alive to avoid logging you out of every device. Consequently the attacker keeps working while you believe the door is shut.
The fix is a device review, run immediately after the reset. We now treat revocation as a separate step, and we never skip it, because our own case proved the cost of assuming otherwise. In practice 聊天软件账号被盗 containment is a sequence of three revocations, not one reset.
Where 聊天软件账号被盗 Recovery Still Fails
Support queues are the real bottleneck, and they are slow by design. In our case the recovery email change required manual escalation, which consumed most of the nine hours. Additionally, some providers will not reverse a change without an identity document, which can stall 聊天软件账号被盗 recovery for days.
Prevention compresses these numbers dramatically, and the cheapest measure is a second factor that is not a text message. Our 聊天账号双重验证实测 scored five factor types against 60 takeover attempts, and the spread was wide. Verifying who you are actually talking to is the next layer, which our 安全码验证实战 covers step by step.
Rebuilding trust after 聊天软件账号被盗
Your contacts absorbed the damage too, because the attacker messaged them from your account. Therefore recovery includes telling people plainly what happened. Two of our contacts clicked a link the attacker sent, which is why we now treat post-incident messaging as part of the response.
Response time is also a training problem. Nobody in our test knew which setting revoked sessions, and that cost us twenty minutes of reading help pages during the worst possible window. Practise the 聊天软件账号被盗 drill once, and the real event gets much shorter.
What To Do First After 聊天软件账号被盗
Order matters more than effort. Start by revoking every session, because a reset without revocation leaves the attacker active. Next, rebuild the recovery address and confirm that it works, then re-register your second factor on devices you control.
Only after those three steps should you tell contacts what happened. Messages from a compromised account look authentic, so a short warning prevents a second wave of damage. Additionally, change the password last, and use a fresh one that appears nowhere else.
Finally, keep the evidence. Export what you can before cleaning up, because the sequence of events is what support teams ask about. Our 加密聊天备份实测 covers the recovery side separately, since a backup often survives the account itself.
FAQ About 聊天软件账号被盗
How do I know if my account was taken over?
Look for devices you do not recognise, messages you did not send, and factor prompts you did not request. Those three signals preceded every case we compared, so check them after any known breach elsewhere.
Does two factor authentication stop it completely?
No, and it removes most of the easy paths. Factor prompts you did not request are a warning rather than a failure, and ignoring them is the correct response.
Should I delete the account instead?
Deleting destroys the evidence and does not stop the attacker from using a copy of your data. Therefore secure the account first, then decide, and keep your exports in the meantime.
References
- CISA – Use Strong Passwords
- NIST SP 800-63B – Authentication and Lifecycle Management
- EFF – Surveillance Self-Defense
延伸阅读
实名账号被接管后怎么办,请参阅:《聊天软件实名认证实测:要求身份之后数据留下了什么》。
账号被盗后的不可逆损失,请参阅:《聊天软件账号封禁实测:账号被停用后数据还能拿回吗》。
关于聊天软件二维码登录 的实测,请参阅:《聊天软件二维码登录安全吗?What a Scanned Code Really Shares》。
关于聊天软件设备管理 的实测,请参阅:《聊天软件设备管理怎么做?Auditing Every Linked Device》。
关于聊天软件远程擦除 的实测,请参阅:《聊天软件远程擦除真的有效吗?What a Wipe Can Reach》。
关于聊天软件安全更新 的实测,请参阅:《聊天软件安全更新有多重要?Why a Patch Delay Costs》。
延伸阅读:《聊天软件设备指纹实测:换设备还能认出你吗》。
延伸阅读:《聊天软件登录提醒实测:异常登录你能不能第一时间知道》。
延伸阅读:《聊天软件账号冒充实测:假账号是怎么骗过好友的》。
延伸阅读:《聊天软件账号租借实测:借出去之后会发生什么》。
延伸阅读:《聊天软件恢复码实测:丢了手机能不能救回账号》。
延伸阅读:《聊天软件无障碍权限实测:读屏服务能做什么》。
延伸阅读:《聊天软件远程协助实测:让别人控制你的手机有多危险》。
延伸阅读:《聊天软件数据泄露响应实测:账号被拖库后先做什么》。
延伸阅读:《聊天软件账号申诉实测:账号被封之后能救回来吗》。
延伸阅读:《聊天软件邮箱绑定实测:邮箱能救账号也能毁账号》。
延伸阅读:《聊天软件撞库攻击实测:用旧密码能登进去吗》。
延伸阅读:《聊天软件SIM卡交换实测:号码被转移后账号还能保住吗》。
延伸阅读:《聊天软件二手号码实测:新号前任的主人留下了什么》。
延伸阅读:《聊天软件短信拦截实测:验证码是怎么被截走的》。
评论
还没有评论,来说两句吧。
评论功能已关闭。