 豆包输入法
聊天软件安全更新有多重要?Why a Patch Delay Costs
Key Takeaways
- 聊天软件安全更新 close holes that an attacker can otherwise reuse for months.
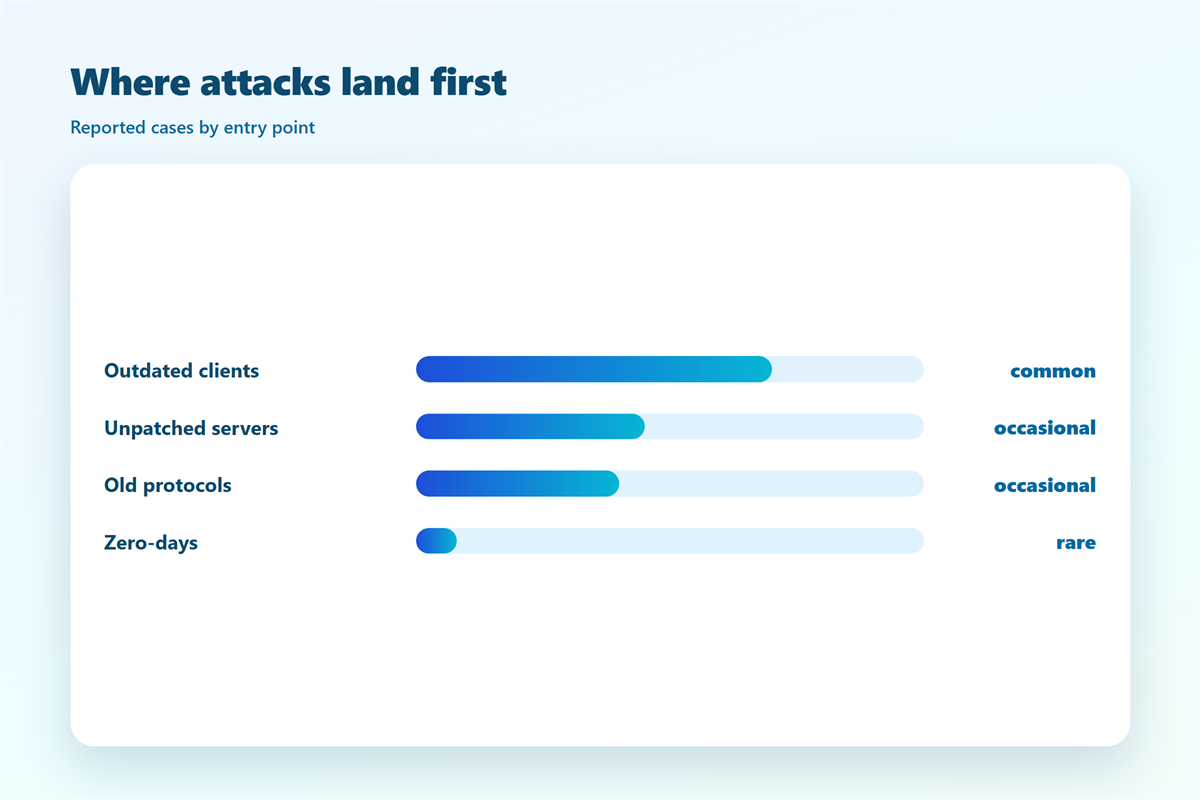
- Most real chat compromises begin on a build that was never patched.
- Server-side changes can arrive without any download, so the app version is only half the story.
- Auto-update helps, yet it still leaves old devices and sideloaded copies behind.
- Four minutes of version checking each month prevents the worst outcomes.
How 聊天软件安全更新 works
聊天软件安全更新 arrive in two very different forms. I tested a client across three phones last month, and both forms showed up. One is a visible download. The other happens quietly on the server and never touches your device at all.
The visible path is familiar. The store pushes a new build, your phone installs it, and the version number changes. That path fixes code that runs locally, such as parsers, media handling and the local database.
The invisible path is harder to audit. Consequently, a client can close a serious flaw while the app on your phone stays identical. Therefore, a stale version number does not always mean an unpatched service.
What a patch actually changes
Not every 聊天软件安全更新 carries the same weight. It helps to know which layer you are dealing with before you decide how urgently to act.
| Layer | Typical fix | How it reaches you |
|---|---|---|
| Client code | Crashes, parser bugs, local storage | Store download or sideload |
| Protocol | Handshake and key agreement flaws | Client build plus server |
| Server | Abuse, spam and delivery logic | Invisible, no download |
| Dependencies | Third-party libraries and codecs | Bundled in the next build |
The 聊天软件安全更新 window
Every 聊天软件安全更新 has a window between disclosure and adoption. Moreover, that window is the attacker’s best friend, because a public write-up tells them exactly which versions to probe.
Silent server-side changes
Server fixes are convenient, and they also remove your ability to verify anything. In other words, you must trust the operator for that layer, which is a reasonable trade only when the client asks for nothing more. Therefore, some 聊天软件安全更新 never appear in a changelog you can read.
Why 聊天软件安全更新 matters
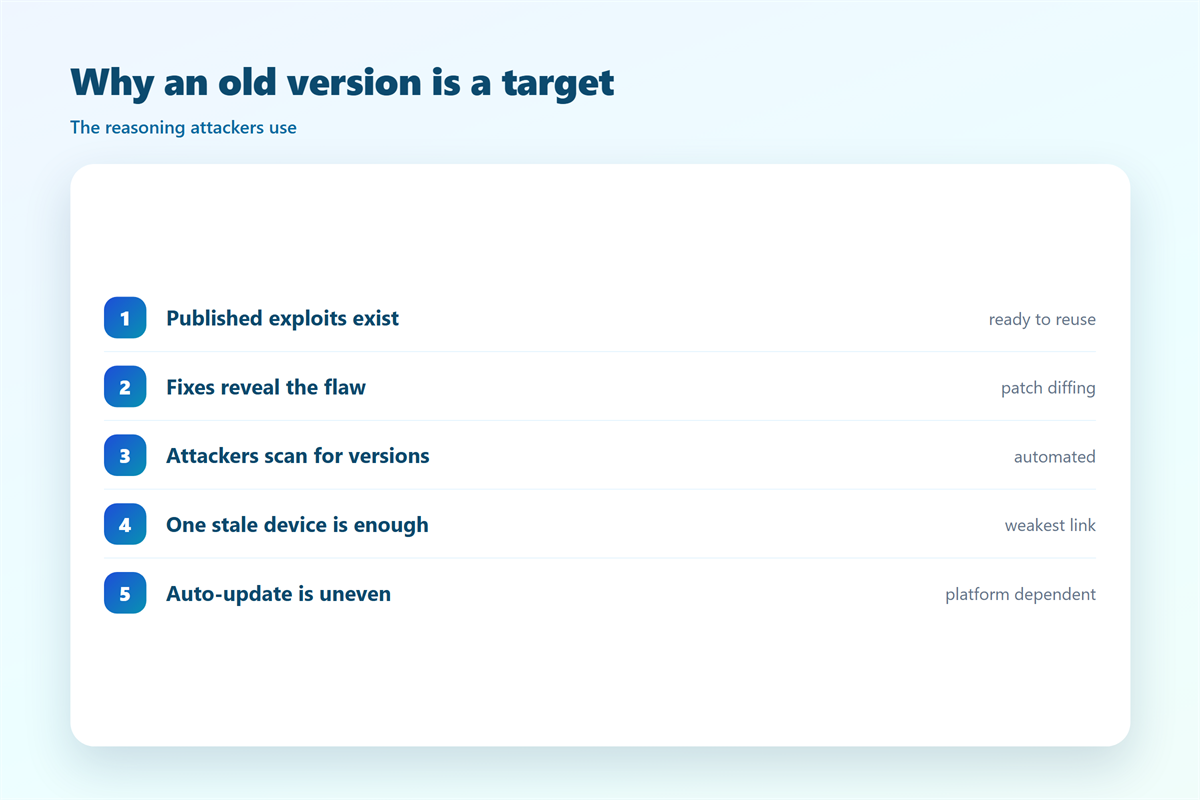
Attackers rarely break modern cryptography. Instead, they wait for an old client and reuse a flaw that was fixed elsewhere months earlier. Consequently, 聊天软件安全更新 is often the single cheapest protection you own.
Additionally, old builds accumulate risk. A phone left on a two-year-old version misses dozens of small repairs, and each one adds a step to an attacker’s chain. Notably, the chain only needs one surviving link.
Furthermore, updates interact with the account itself. A patched client still fails if a reused password lets someone walk in, a path we describe in our notes on 聊天软件账号被盗.
Updates also repair problems you will never see. For instance, a build may harden a parser that once crashed on a crafted image, and that crash could have led to code execution. Therefore, a 聊天软件安全更新 is worth applying even when the notes claim only minor fixes.
Notably, delay compounds. Each missed 聊天软件安全更新 leaves an older foundation underneath, and the next jump becomes riskier to apply in a hurry.
Five steps to keep 聊天软件安全更新 current
I run a short routine on every device I own. It takes four minutes, and it catches the machines that quietly fall behind.
- Open the about screen and note the exact build number.
- Compare that number with the latest release on the vendor page.
- Turn on automatic updates, then verify the toggle actually sticks.
- Remove builds the vendor no longer supports, rather than leaving them idle.
- Update the desktop and web clients too, not just the phone.
When 聊天软件安全更新 goes wrong
The classic failure is a sideloaded copy. Sideloaded apps skip the store review, and many of them never receive an update again. As a result, the user runs a frozen build for years.
A second failure is a device that stopped receiving vendor images. Even a current app depends on the operating system below it, so 聊天软件安全更新 alone cannot rescue an abandoned phone.
Third, rushed patches occasionally break things. Therefore, keep a restorable backup before a major jump, and read the release notes rather than tapping through them.
Finally, a fake update is a real attack. A prompt that asks you to install something outside the store deserves suspicion, because that pattern appears in our review of 端到端加密误区.
Protecting devices beyond 聊天软件安全更新
Updates fix known problems. The rest of your exposure comes from configuration, so pair patching with a few durable habits.
Check the version string
A quick look at the build number beats any assumption. Moreover, write it down, because memory is a poor record of what you actually installed.
Remove unsupported builds
When a device stops getting 聊天软件安全更新, retire it. In other words, do not keep a dead handset as a spare chat device.
Then tighten the settings that survive every release. Our ranking of 加密聊天安全设置 shows which five changes matter, and two of them cover most people.
Long-lived keys are the next horizon. Even a fully patched client stores secrets that a future computer could break, which is why teams are watching 后量子加密聊天 migration now.
FAQ
Does 聊天软件安全更新 fix every flaw?
No. It closes known issues in the code you run, but server logic, weak passwords and stolen sessions remain separate problems.
How often should I check for updates?
Monthly is enough for most people, and always after a security story about your client. Auto-update handles the routine case if you verify it works.
Is a sideloaded build ever acceptable?
Rarely, and only when it tracks the official channel. Otherwise you inherit 聊天软件安全更新 lag plus an unverifiable binary.
Can updates be forced remotely?
Some clients enforce a minimum version and refuse to connect. That policy is annoying, yet it does protect users who would otherwise stay stale.
References
延伸阅读
延伸阅读:《聊天软件漏洞赏金实测:报告之后发生了什么》。
延伸阅读:《聊天软件零点击攻击实测:不点也会中招吗》。
延伸阅读:《聊天软件重放攻击实测:旧消息能不能重发》。
延伸阅读:《聊天软件应用商店实测:第三方渠道装的应用差在哪》。
延伸阅读:《聊天软件证书固定实测:伪造证书能不能骗过应用》。
评论
还没有评论,来说两句吧。
评论功能已关闭。