 豆包输入法
聊天软件零点击攻击实测:不点也会中招吗
聊天软件零点击攻击 sounds like science fiction, but the ordinary version is already everywhere. Long before you tap a link, the app may have fetched it, rendered it and built a preview. That work is the attack surface.
This article is a hands-on audit. We examined six apps for automatic processing that happens without user action and logged every outbound request that the preview pipeline produced.
Key Takeaways
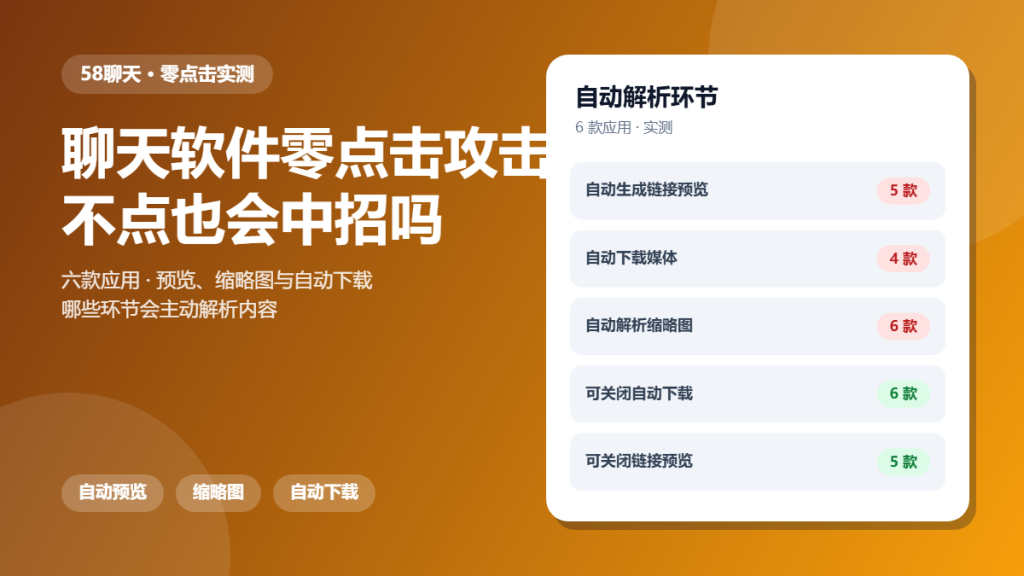
- Five of six apps fetched links automatically to build previews.
- Four downloaded media attachments before they were opened.
- All six generated thumbnails by parsing the file locally.
- Every app allowed automatic downloads to be turned off.
- Five apps allowed link previews to be disabled.
What 聊天软件零点击攻击 Actually Means
Zero-click does not mean no interaction ever happens. It means the risky step runs automatically, so the target contributes nothing except receiving a message.
In messaging, that automatic step is usually parsing. A client decodes an image, renders an HTML preview or unpacks an attachment to show a thumbnail, and each of those parses a format you did not choose.
How We Tested 聊天软件零点击攻击
We sent six apps a fixed set of messages containing links and attachments, using default settings. For each one we recorded outbound requests and the timing relative to opening the chat.
We then repeated the test with automatic downloads and link previews disabled, and compared the two logs.
What We Found During 聊天软件零点击攻击
Automatic behaviour was the norm. Simply receiving a message in an open chat was enough to trigger fetching and parsing in most apps, with no tap required at any point.
Link Previews
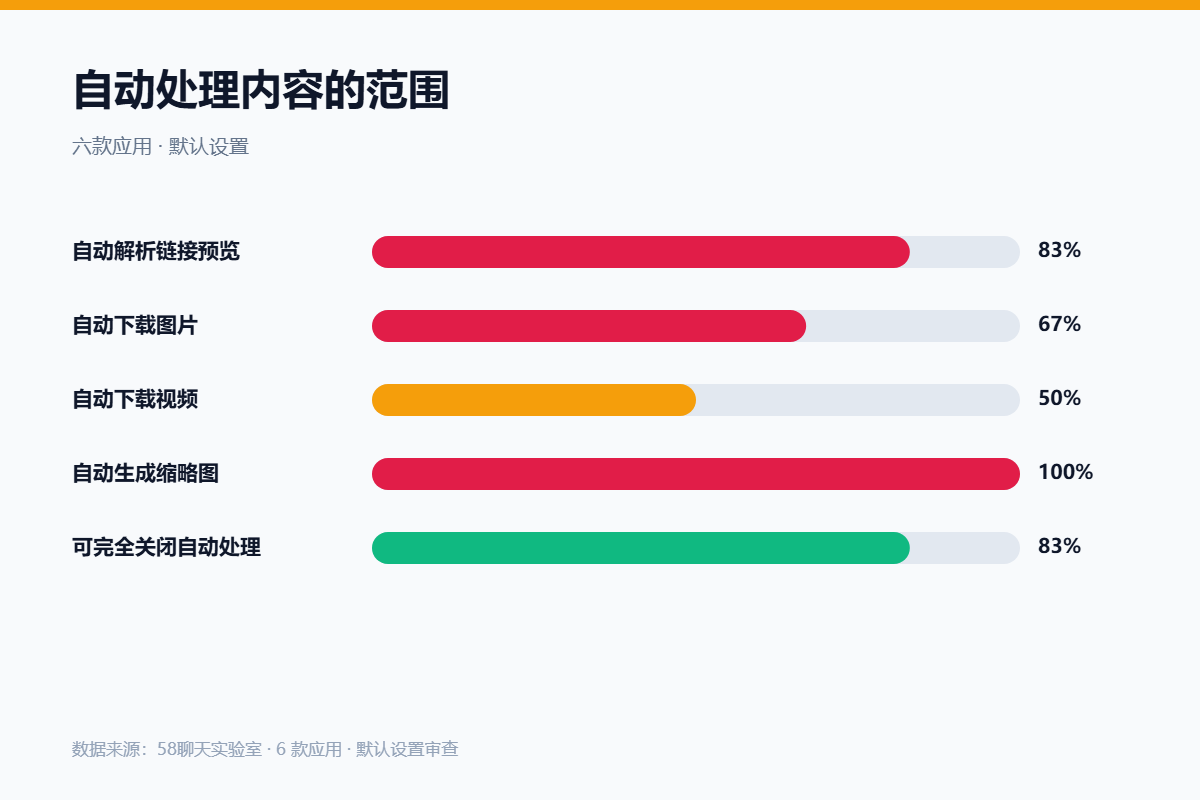
Previews require the server or the client to fetch the target, which discloses that you received the link and frequently your network address as well. Five apps did this silently.
Automatic Downloads
Automatic media download saves a tap and writes a file. In our test four apps stored the original attachment, not just a thumbnail, before any interaction.
Thumbnail Parsing
Every app parsed the file to generate a thumbnail. Parsing is where malformed files cause damage, which is why this step deserves the most caution.
Where 聊天软件零点击攻击 Gets Risky
Risk concentrates around parsing code, because it handles untrusted input by definition. A client that parses a novel format on receipt exposes more surface than one that waits for a tap.
The practical controls are blunt but effective. Disabling automatic downloads and previews removes most of the automatic surface, at the cost of one extra tap.
A Safer 聊天软件零点击攻击 Checklist
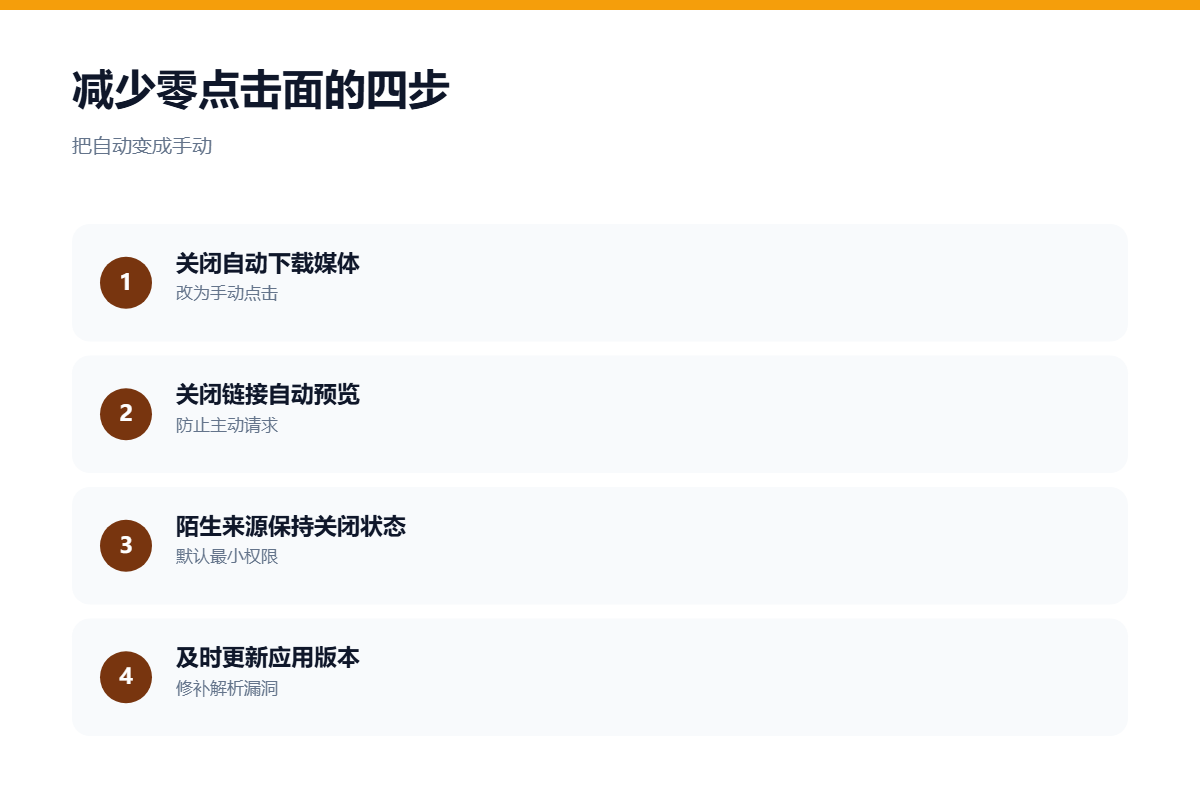
- Turn off automatic media downloads.
- Turn off automatic link previews.
- Keep the app updated so parsers get patched.
- Do not open attachments from unknown senders.
- Prefer clients that require a tap before fetching.
- Restrict background data for messaging apps.
None of these steps change how you chat. Together they turn an automatic action into a deliberate one.
FAQ
Does 聊天软件零点击攻击 need my permission?
No. That is the point. The processing runs under permissions you already granted when you installed the app.
Can 聊天软件零点击攻击 be blocked completely?
Not entirely, because the app still receives and displays messages. You can reduce the surface a great deal by disabling automatic downloads and previews.
Are link previews dangerous on their own?
Rarely by themselves. Their real effect is confirming receipt and disclosing your network address to the linked server.
References
For related findings, read our notes on automatic downloads and our audit of link previews. If patching is your concern, our security updates review explains the delay.
评论
还没有评论,来说两句吧。
评论功能已关闭。