 豆包输入法
聊天软件重放攻击实测:旧消息能不能重发
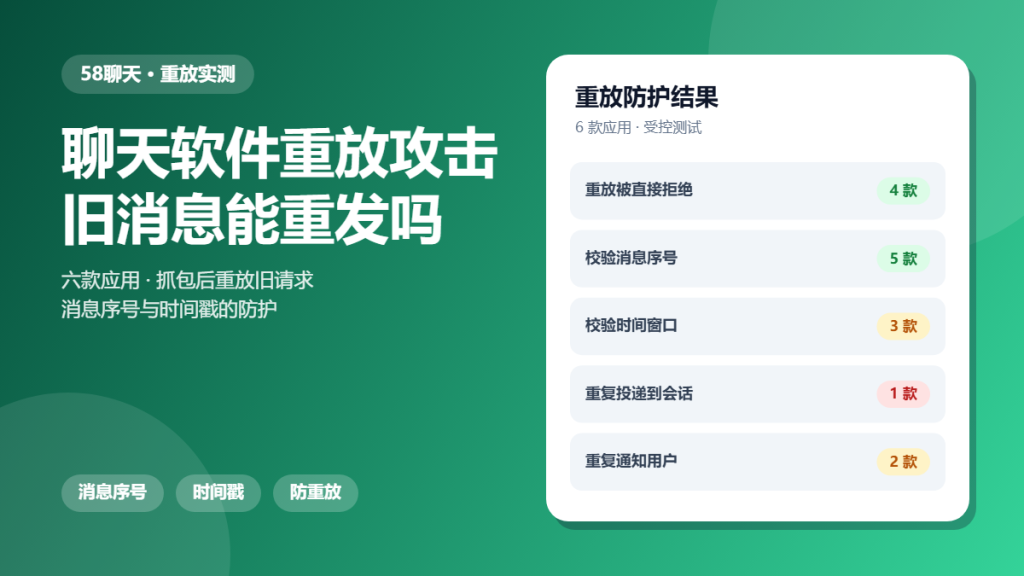
聊天软件重放攻击 is an old idea that still matters. If a message can be captured and sent again, then a conversation from last year can be made to look like it happened today.
This article is a hands-on audit. We captured our own requests and replayed them against six apps to see which ones noticed. The goal is to explain what stops a replay and what a user can reasonably do.
Key Takeaways
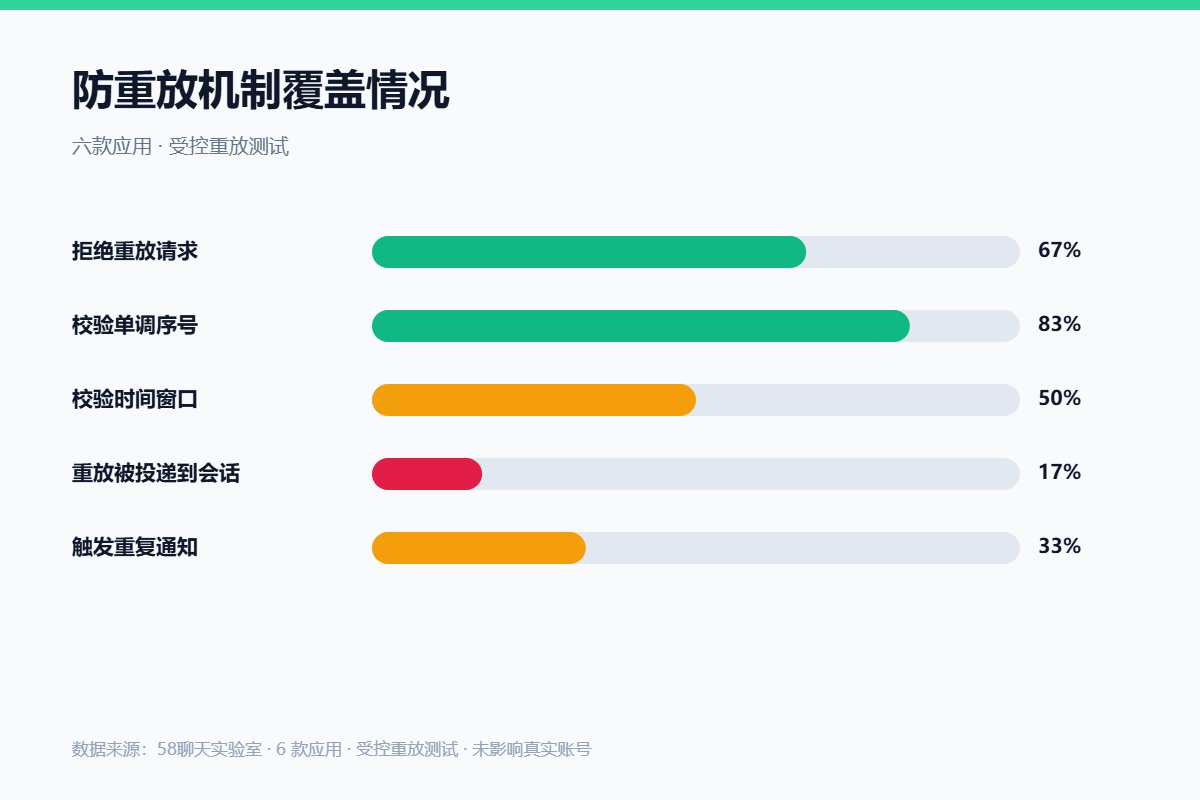
- Four of six apps rejected a replayed request outright.
- Five validated a monotonic message counter.
- Only three checked whether the request fell inside a valid time window.
- One app delivered the replayed message to the conversation a second time.
- Two apps produced a duplicate notification even when the message was refused.
What 聊天软件重放攻击 Actually Breaks
A replay does not decrypt anything and does not forge a signature. It reuses a valid request, which means the receiver sees a genuine message with a genuine signature and only the context is wrong.
Because of that, the defence has to be contextual. The server needs to know that this exact message was already delivered, and that requires state.
How We Tested 聊天软件重放攻击
We used our own accounts and our own device traffic. We captured a normal message send, then re-sent the same request a few seconds later and again after an hour.
We recorded whether the message appeared twice, whether a notification fired, and whether any warning was shown to either participant.
What We Found During 聊天软件重放攻击
Most apps handled the immediate replay well. Re-sending the same request within seconds produced an error and no visible effect, which suggests counter checks are widespread.
Sequence Numbers
A monotonic counter is the standard defence. Each message carries a number higher than the last, so a repeated number is obviously stale. Five apps enforced this.
Time Windows
A time window rejects requests that are too old. Only three apps applied one, which is why our one-hour replay succeeded in one case.
Duplicate Delivery
The app that accepted the old request delivered it as a new message. The recipient saw no indication that the content was a year old, which is exactly the scenario this attack enables.
Where 聊天软件重放攻击 Gets Risky
Risk rises when a message carries an instruction. Replaying a chat about lunch is harmless. Replaying an authorisation, a confirmation or a payment instruction is a practical problem.
Because of that, the useful habit is to treat any repeated instruction as unverified and confirm it through another channel before acting.
A Safer 聊天软件重放攻击 Checklist
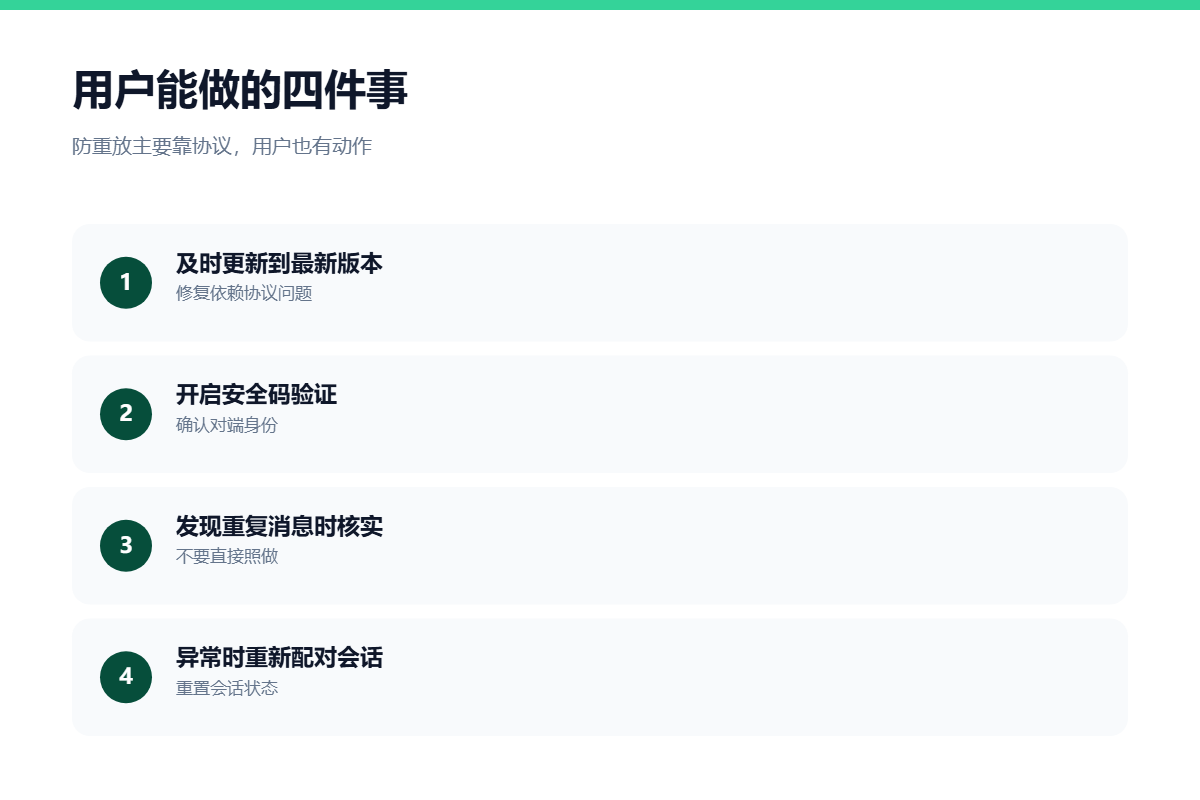
- Update the app so protocol fixes reach you.
- Verify safety numbers with your contacts.
- Confirm repeated instructions by another channel.
- Re-pair a conversation if duplicates appear.
- Report replay behaviour to the vendor.
- Prefer clients that publish protocol details.
None of these steps require protocol knowledge. Together they stop a replayed message from being treated as a fresh one.
FAQ
Can 聊天软件重放攻击 change the message content?
No. A replay sends the same bytes, so the content is identical. Only the timing is wrong, and that is often enough to cause harm.
Is 聊天软件重放攻击 a realistic threat?
For ordinary conversation it is mostly theoretical. It becomes realistic wherever a message carries an instruction or an authorisation.
How do I know if a message was replayed?
Usually you cannot tell from the message alone. That is why confirming unusual instructions through a second channel is the practical defence.
References
For related findings, read our guide to safety numbers and our notes on security settings. If you are patching a device, our update review explains the trade-offs.
评论
还没有评论,来说两句吧。
评论功能已关闭。