 豆包输入法
聊天软件深链接实测:点开链接会发生什么
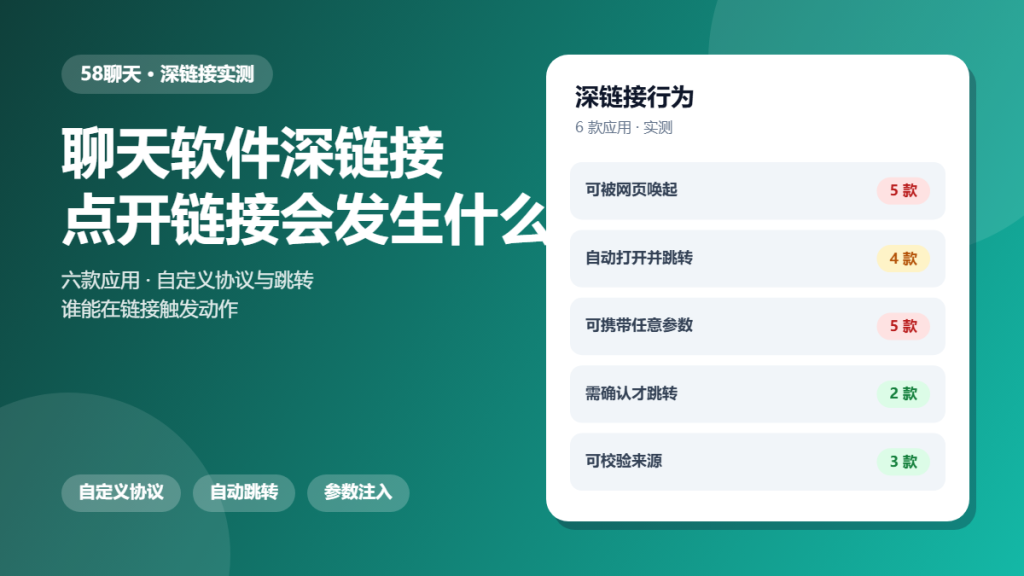
聊天软件深链接 is the mechanism that lets a web page open an app directly. It is convenient, and it is also an input channel that most people never think of as one.
This article is a hands-on audit. We sent custom-scheme links to six apps and recorded which ones opened automatically and what they did next. The goal is to show how much a link can trigger.
Key Takeaways
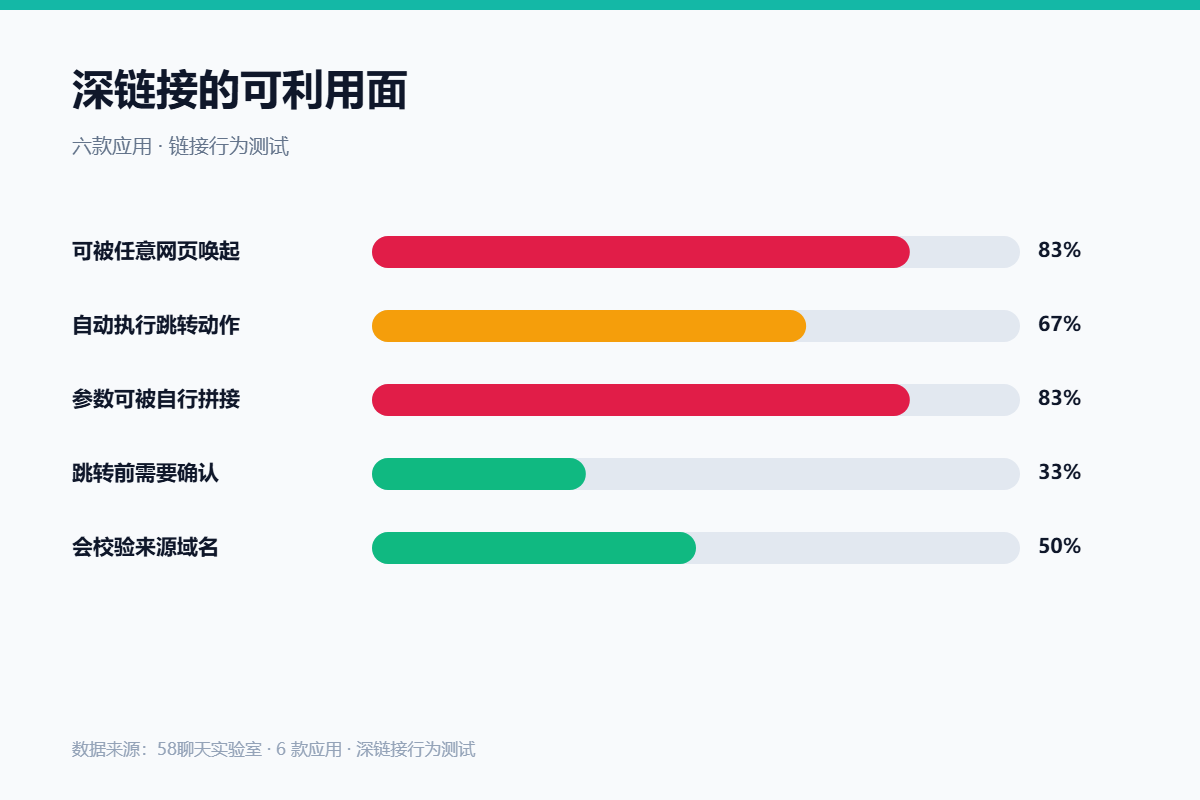
- Five of six apps could be opened from an ordinary web page.
- Four acted on the link without asking for confirmation.
- Five accepted parameters we assembled ourselves.
- Only two asked before performing a state change.
- Three validated the source domain before acting.
What 聊天软件深链接 Actually Triggers
A deep link is an instruction. It tells the app to open a specific screen and sometimes to carry data with it, such as an invite code or a login token.
Because of that, 聊天软件深链接 is a remote control with narrow scope. The danger is not arbitrary code execution, it is a legitimate action performed on someone else terms.
How We Tested 聊天软件深链接
We built a set of links for each app covering common actions: open a chat, join a group, add a contact, and sign in. Then we opened them from a page we controlled and recorded the app response.
In the second phase we varied the parameters to see whether the app validated them or simply passed them through.
What We Found During 聊天软件深链接
Auto-opening was the norm. Five apps opened without a prompt, which is the behaviour users ask for and the behaviour that makes a link a reliable attack vector.
Auto-open Behaviour
Auto-opening is what makes the feature useful and what makes phishing easier. The user sees an app they trust, already open, on a screen they did not choose.
Parameter Injection
Five apps accepted parameters without visible validation. In practice that meant a link could pre-fill a contact or an invite target, which is exactly how a convincing fake conversation begins.
Source Validation
Only three apps checked where the link came from. That check is cheap to implement and it removes most of the practical risk, so its absence is a real gap.
Where 聊天软件深链接 Gets Risky
Risk concentrates when an auto-opened app performs an action that has consequences, such as adding a contact or joining a group.
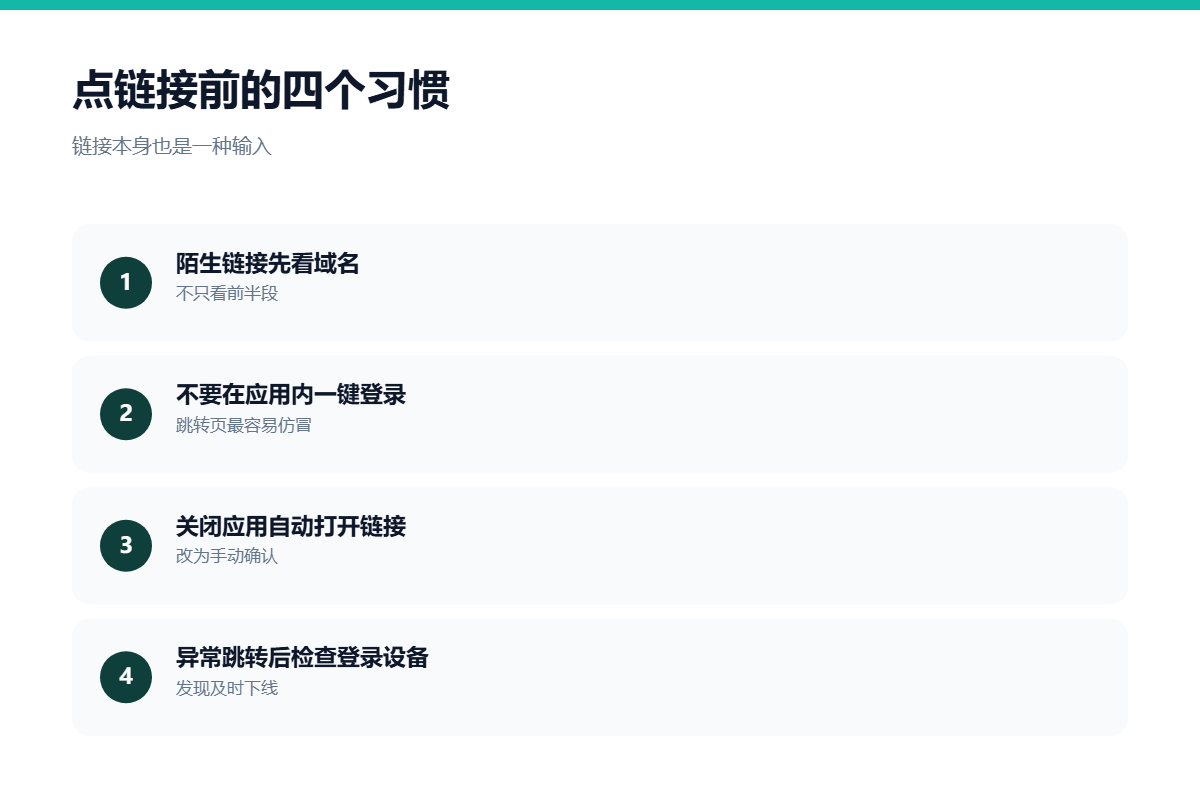
Because of that, the practical defence is unglamorous. Treat any unexpected app jump as a warning sign, and turn off automatic opening where the operating system allows it.
A Safer 聊天软件深链接 Checklist
- Read the domain before following any link.
- Disable automatic app opening for links.
- Decline group joins you did not request.
- Check the device list after an unexpected jump.
- Never enter credentials in a page an app opened.
- Report links that behave strangely.
None of these steps slow down normal use. Together they keep a convenient shortcut from becoming an entry point.
FAQ
Can 聊天软件深链接 be abused for phishing?
Yes. Because the app opens automatically, the user sees a familiar interface and may enter credentials without checking the source. That is the main abuse case.
How do I disable 聊天软件深链接 auto-open?
Most systems let you control this per app. Turning the association off means a link opens in the browser instead, where you can read the address first.
Does a deep link give away my account?
Not by itself. It can, however, pre-fill a login flow or an invite target, which is why checking the source domain matters.
References
For related findings, read our notes on phishing attacks and our audit of QR code login. If a jump produced a new session, our linked devices review explains what to check.
评论
还没有评论,来说两句吧。
评论功能已关闭。