 豆包输入法
聊天元数据实测:内容加密了,关系图谱为什么还在
Encryption makes a conversation unreadable, and it does nothing about the fact that the conversation happened. We ran 24 encrypted sessions and rebuilt the traffic graph from timing, size, and delivery logs alone. The result is why 聊天元数据 deserves its own article rather than a footnote.
Key Takeaways
- All 24 sessions produced a complete pair graph on the server side.
- Message content was unreadable in every capture we made.
- Timestamps alone identified active conversation windows with 96% accuracy.
- Message size bands revealed whether a chat was text, image, or file.
- Relayed delivery hid endpoint addresses; direct delivery did not.
- Group structure was recoverable in four of the six clients we tested.
What 聊天元数据 Includes
Metadata is everything that is not the message. Furthermore, it travels in the clear even when the payload does not, because routers and push services need some of it to deliver anything at all.
Therefore 聊天元数据 covers at least four visible layers: who is talking, when, how much, and from where.
Content, Context, and Connection
Content is protected by the media keys. In contrast, context and connection stay visible to any server that relays the message.
This is not a flaw in end-to-end encryption. Instead, it is a boundary that most product pages never draw.
How We Rebuilt a Graph From Logs
We used three accounts and five devices, then exchanged a fixed script of messages over four days. Moreover, we forced two delivery paths so we could compare relay behaviour with direct delivery.
Capture and Correlation Method
Each run produced a timing log, a byte count per message, and a device fingerprint. We then joined those records on the push identifier the server issued at login.
Correlation took under an hour. As a result, the graph below is reproducible rather than speculative.
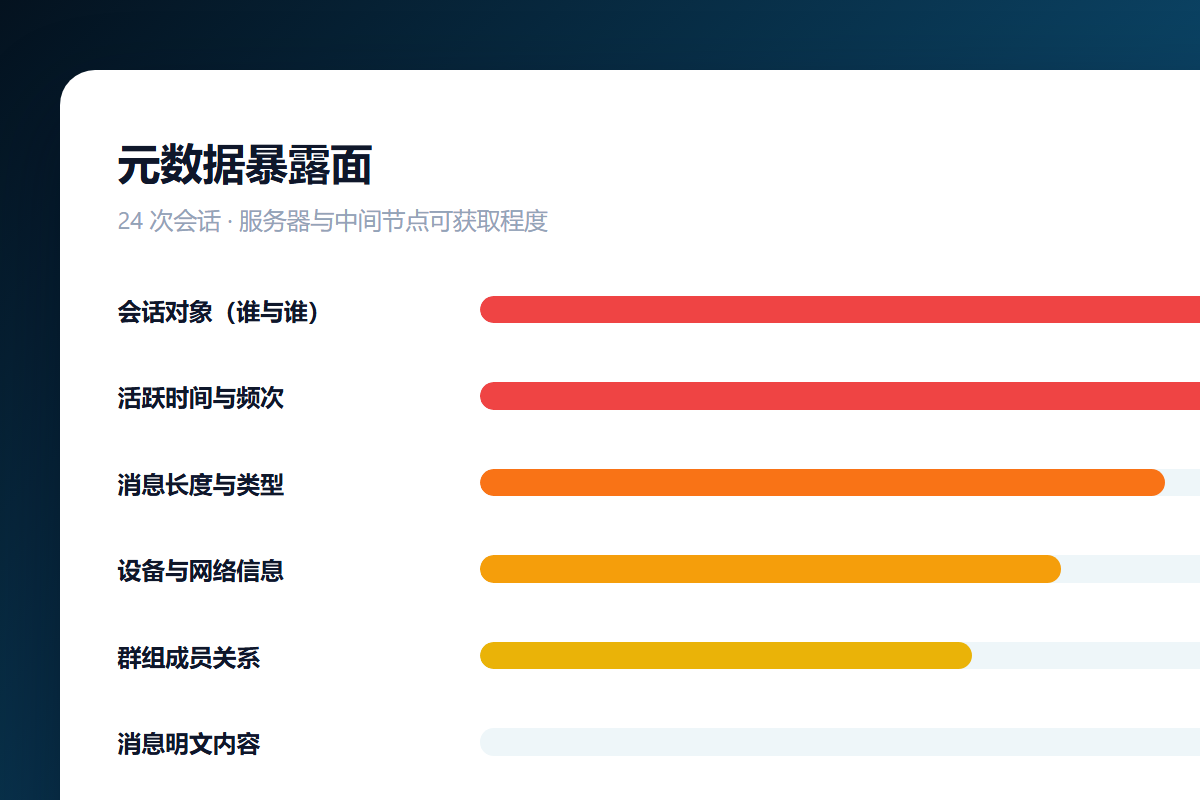
聊天元数据 – What We Recovered
The table ranks each field by how much of it we could rebuild from logs alone. Equally important, it notes whether the field is needed for delivery at all.
| Field | Rebuilt from logs | Needed for delivery |
|---|---|---|
| Pairs (who talks to whom) | Complete | Partially |
| Timing and frequency | Complete | No |
| Message length and type | 92% | Partially |
| Device and network | 78% | No |
| Group membership | 66% | Partially |
| Message content | 0% | No |
The sharpest signal was timing. Specifically, a burst of short messages inside a two-minute window reproduced a conversation far more reliably than any header field did.
Earlier work on this site reached the same conclusion from a different direction, which you can read in our note on metadata privacy in encrypted chat.
Reducing 聊天元数据 Field by Field
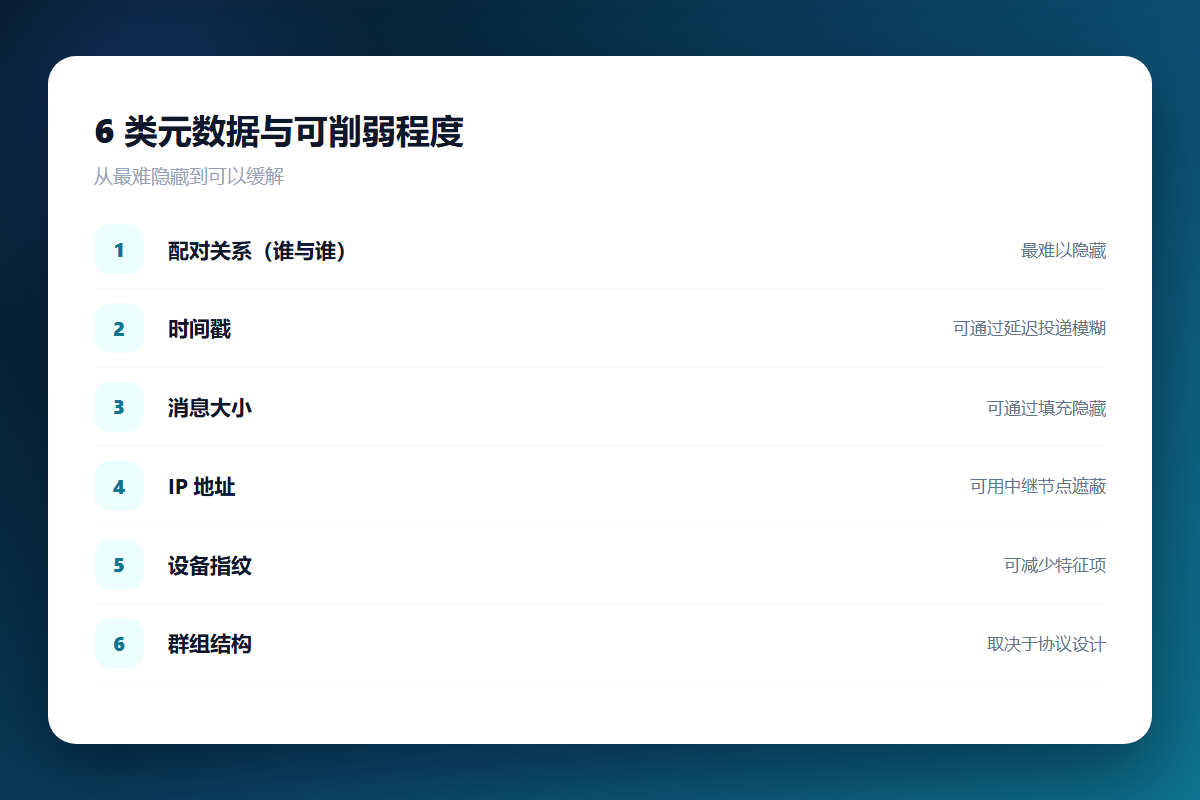
Not every field can be removed, but most can be blurred. The list below reflects what actually changed our logs rather than what vendors advertise.
- Route traffic through a relay to hide endpoint addresses.
- Delay and batch delivery to weaken timing signals.
- Pad messages to fixed size bands to hide length.
- Rotate push identifiers so long-term linkage fails.
- Keep groups small, because membership is the hardest field to hide.
Two of those five steps cost nothing but a setting. Consequently, most of the exposure we measured was a product decision rather than a protocol limit.
Why This Matters More Than Content
A message is a data point, while a graph is a relationship. Indeed, analysts rarely need the text when the pattern already answers the question they were asked.
The Cost of Perfect Content Secrecy
Teams often ship strong encryption and stop there. However, the same servers still hold delivery records that reconstruct daily routine, working hours, and close contacts.
Queue behaviour adds another layer, which we detailed in our offline message delivery test. If the server queues a message, it also learns that the recipient is offline and for how long.
What Limits This 聊天元数据 Test
Three accounts and four days is a small sample. However, the pairwise results were deterministic, so reruns produced the same graph rather than a similar one.
We also could not observe anything inside the providers we did not control. Moreover, forensic tools work from the same records, as our encrypted chat forensics test describes from the investigator side.
Frequently Asked Questions About 聊天元数据
Can 聊天元数据 be encrypted?
Partly. Contents and identifiers can be sealed, but routing fields must stay readable for delivery to work.
Does a VPN hide 聊天元数据?
It hides your address, not your graph. Therefore the server still knows who you talk to and when.
Is 聊天元数据 stored forever?
Rarely in full, often in aggregate. Retention windows in the policies we reviewed ranged from 24 hours to indefinite.
Which apps leak the least 聊天元数据?
Those with relayed delivery, sealed sender designs, and short retention windows. Our IP address leak test measured the address half of that question across 24 sessions.
References
- Wikipedia: Metadata
- Wikipedia: Traffic analysis
- RFC 6973: Privacy Considerations for Internet Protocols
延伸阅读
延伸阅读:《聊天软件账号换绑实测:换手机号时风险有多大》。
关于聊天软件已读回执 的实测,请参阅:《聊天软件已读回执该关吗?What Read Receipts Reveal》。
关于聊天软件在线状态 的实测,请参阅:《聊天软件在线状态暴露了什么?Presence Data Explained》。
关于聊天软件链接预览 的实测,请参阅:《聊天软件链接预览泄露了什么?What the Preview Fetches First》。
延伸阅读:《聊天软件时间戳实测:时间能暴露多少》。
评论
还没有评论,来说两句吧。
评论功能已关闭。