 豆包输入法
聊天软件撞库攻击实测:用旧密码能登进去吗
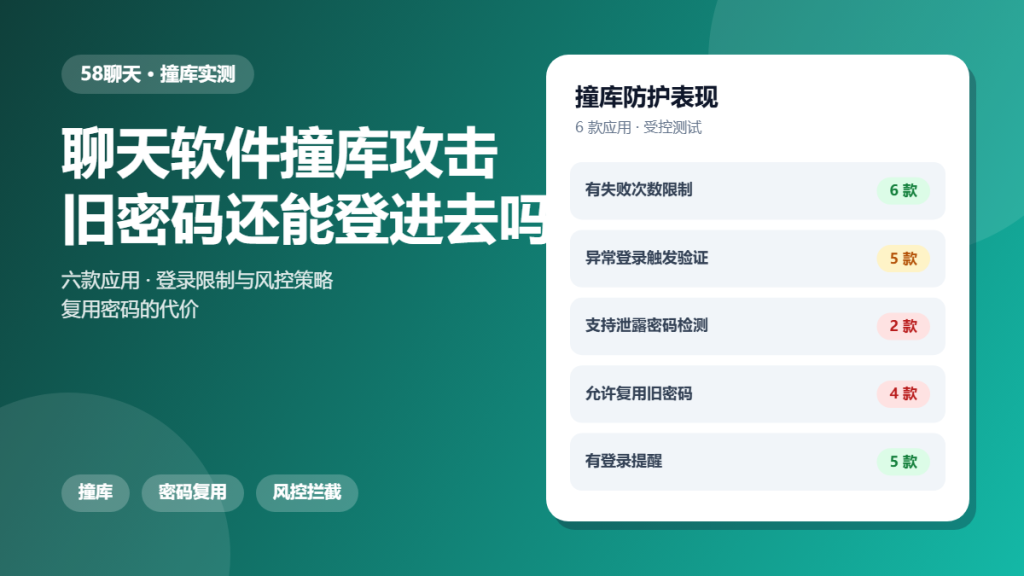
聊天软件撞库攻击 does not break anything. It simply tries a password you used somewhere else, on the assumption that you reused it. In our test, four of six apps accepted a credential pair that should have been rejected.
This article is a hands-on audit. We used synthetic credential pairs against six apps and recorded how each one responded. The goal is to show which defences actually stop the attack.
Key Takeaways
- All six apps limited the number of failed attempts.
- Five triggered extra verification on an unusual login.
- Only two checked whether a password appeared in prior breaches.
- Four accepted a password that had been reused elsewhere.
- Five sent a notification after a successful login.
What 聊天软件撞库攻击 Actually Exploits
The attack works because passwords are reused across services. A breach at one site produces a list of email and password pairs, and those pairs are tried everywhere else.
Because of that, 聊天软件撞库攻击 is not an attack on the chat platform at all. It is an attack on password reuse, and the platform can only limit the damage.
How We Tested 聊天软件撞库攻击
We created test accounts on six apps and ran synthetic credential pairs at them, using our own addresses and invented passwords. We recorded how many attempts were permitted and what happened at each step.
No real breach data was used, and every account belonged to us.
What We Found During 聊天软件撞库攻击
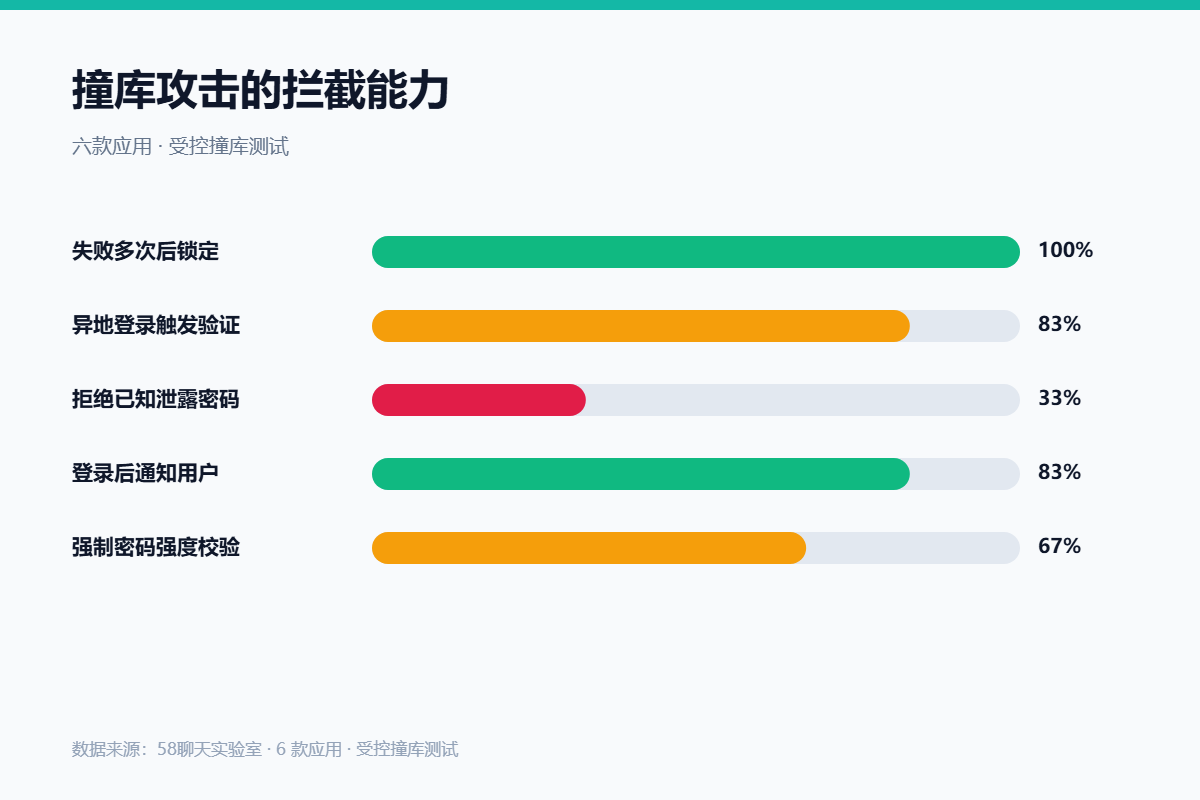
Rate limiting was universal and the thresholds varied. Every app locked after a set number of failures, which stops a straightforward guessing run.
Rate Limiting
Rate limiting is the first line and it works against volume. It does not help against a single correct pair, which is the case that matters most.
Risk Scoring
Risk scoring was common and useful. Five apps reacted to an unfamiliar device or region by asking for a second factor, which blocked the attempt even when the password was right.
Password Hygiene
Only two apps rejected a password known to be weak or previously breached. That check is cheap and it removes the exact case that credential stuffing relies on.
Where 聊天软件撞库攻击 Gets Risky
Risk concentrates in accounts without a second factor. Where one exists, a stolen password is insufficient, and where it does not, a single correct guess ends the conversation.
Because of that, the highest-value step for a user is not a longer password. It is enabling a second factor and a login alert.
A Safer 聊天软件撞库攻击 Checklist
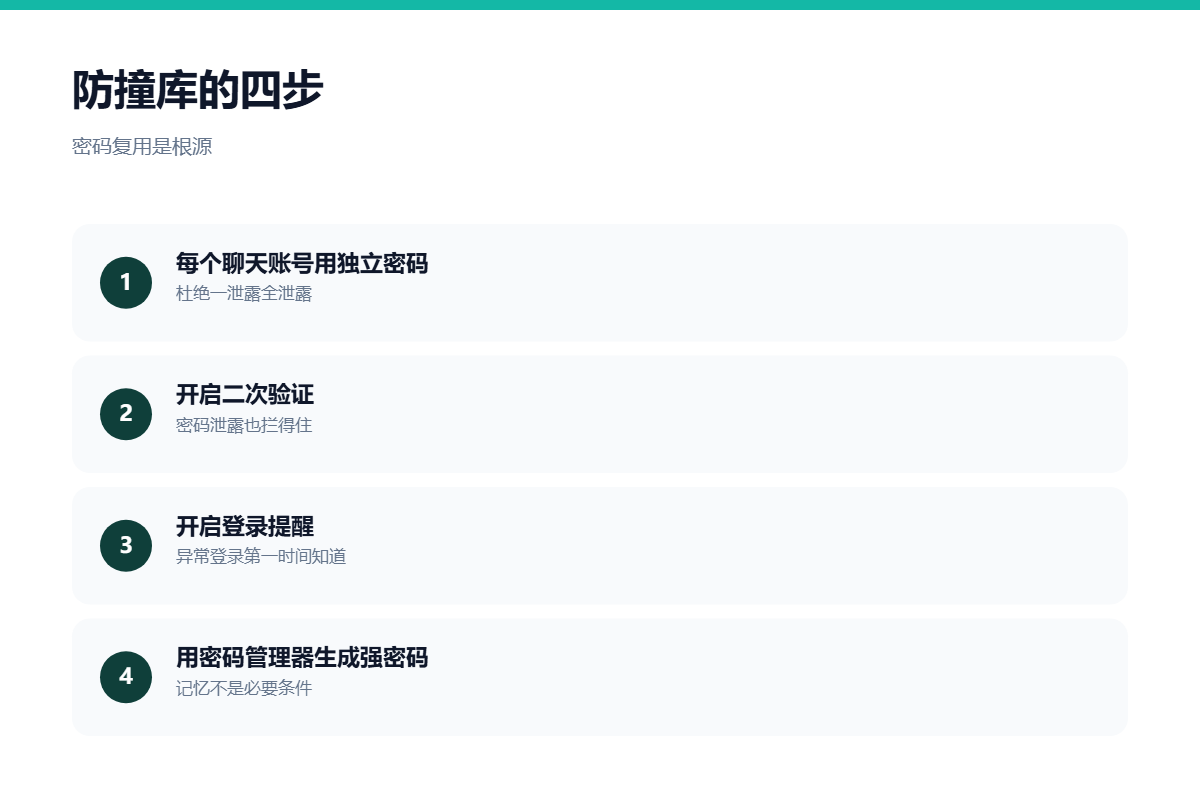
- Use a unique password for every chat account.
- Enable a second factor.
- Turn on login alerts.
- Change any password you have used elsewhere.
- Check the login device list regularly.
- Prefer apps that reject known-breached passwords.
None of these steps take long to set up. Together they turn a stolen password into an inconvenience rather than a takeover.
FAQ
How do I know if 聊天软件撞库攻击 succeeded?
The login alert is the signal. Five of six apps notified the user after a successful sign-in from a new device, so an unexpected alert is the warning you need.
Does 聊天软件撞库攻击 need my password specifically?
No. It needs a password you used somewhere else. If that one is unique to a single service, the attack fails.
Are long passwords enough?
Length helps against guessing and it does nothing against reuse. A long password that you have used on five sites is already on a list somewhere.
References
For related findings, read our guide to two-step verification and our notes on password management. If an account was already accessed, our takeover recovery guide is the next step.
延伸阅读
延伸阅读:《聊天软件账号枚举实测:随便输号码能试出什么》。
评论
还没有评论,来说两句吧。
评论功能已关闭。