 豆包输入法
聊天软件记者信源实测:如何保护线人身份
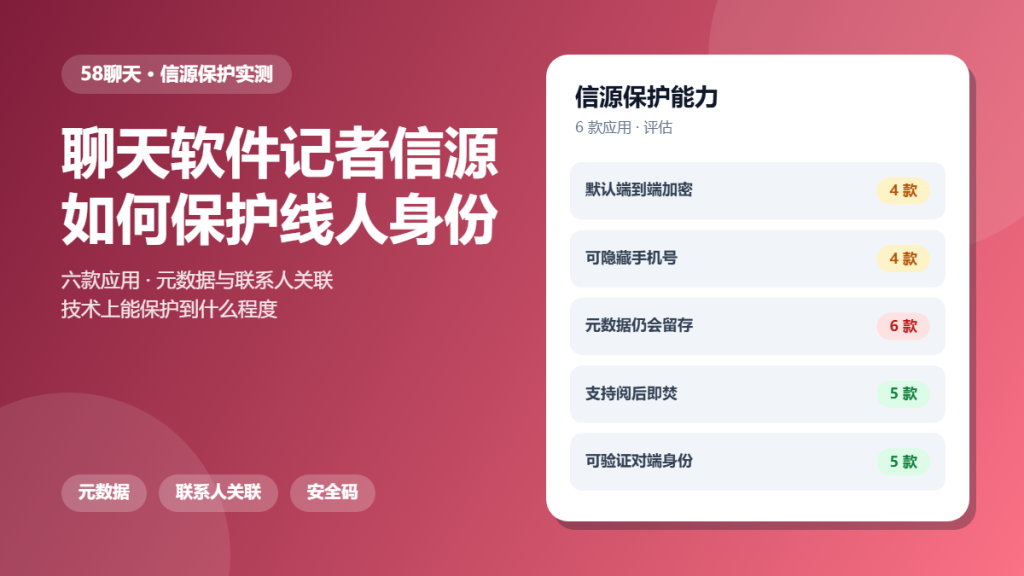
聊天软件记者信源 protection is often reduced to a choice of app. That choice matters and it is only one part of a much larger problem.
This article is a hands-on assessment of six apps from a source-protection perspective. We looked at encryption, metadata and what remains on the platform. The goal is to describe the technical boundary honestly.
Key Takeaways
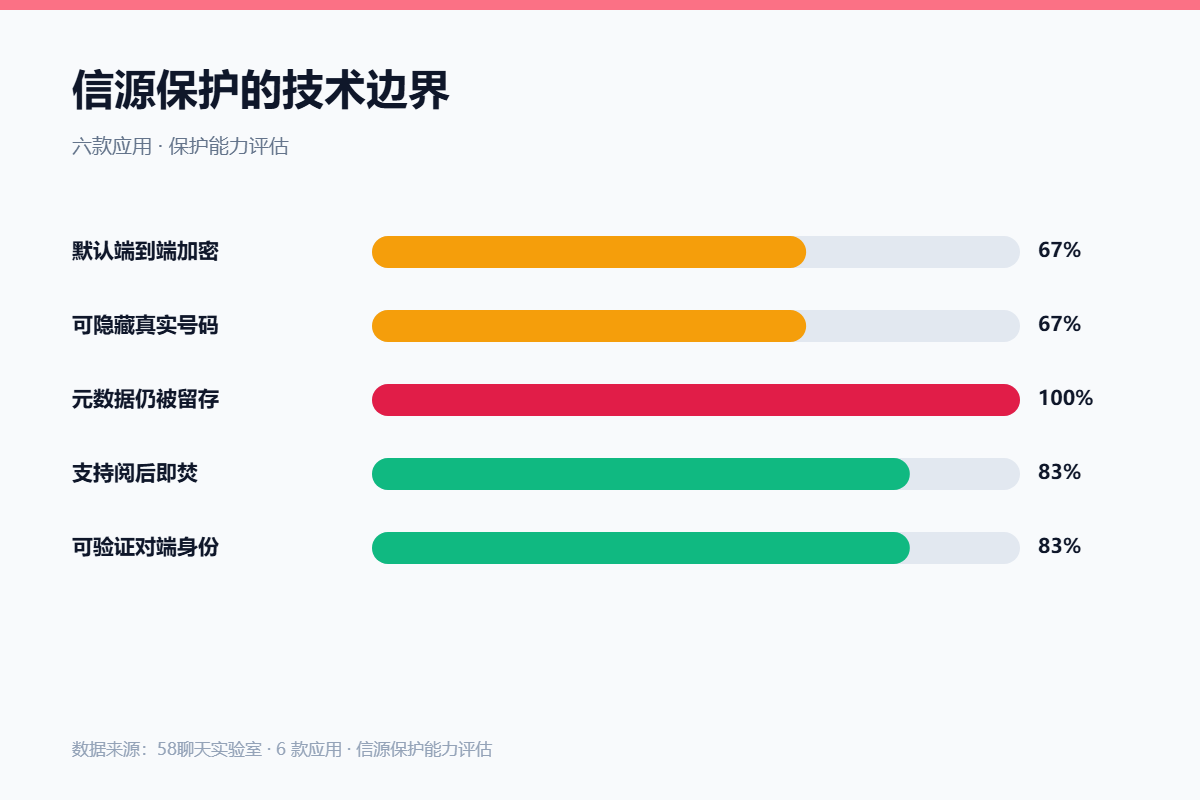
- Four of six apps enabled end-to-end encryption by default.
- All six retained metadata the platform can see.
- Five supported expiring messages.
- Five offered a way to verify the other party identity.
- None could hide the fact that two accounts communicated.
What 聊天软件记者信源 Protection Actually Requires
Protecting a source needs three things at once: the content must stay secret, the identity must not be linkable, and the fact of contact must not be provable.
Because of that, 聊天软件记者信源 protection is a system rather than a setting. An app can deliver the first, and the second and third depend on habits.
How We Tested 聊天软件记者信源
We assessed six apps on encryption defaults, metadata retention, identity separation and verification tools. We recorded what the platform can see and what the counterpart can see.
We did not attempt to access any platform data, and all findings come from documented behaviour and our own controlled accounts.
What We Found During 聊天软件记者信源
Content protection was strong, and the social graph was not. Every app retained the fact that two accounts exchanged messages, along with timing and frequency.
Encryption Defaults
Encryption defaults were good in most apps. Four enabled end-to-end encryption without asking, which is the correct default for this use case.
Metadata Exposure
Metadata was universal. The platform knows who talked to whom and when, and that record is the practical risk in most source-protection failures.
Identity Separation
Separation is the user-side work. A dedicated device with a dedicated account and no overlapping contacts is far more effective than any single app feature.
Where 聊天软件记者信源 Gets Risky
Risk concentrates in the connection between identities. A source who messages from a personal number and a journalist who calls from a work phone have already linked the two, whatever the app encrypts.
Because of that, the discipline is operational: separate devices, separate accounts and no cross-over in contacts, payment or timing.
A Safer 聊天软件记者信源 Checklist
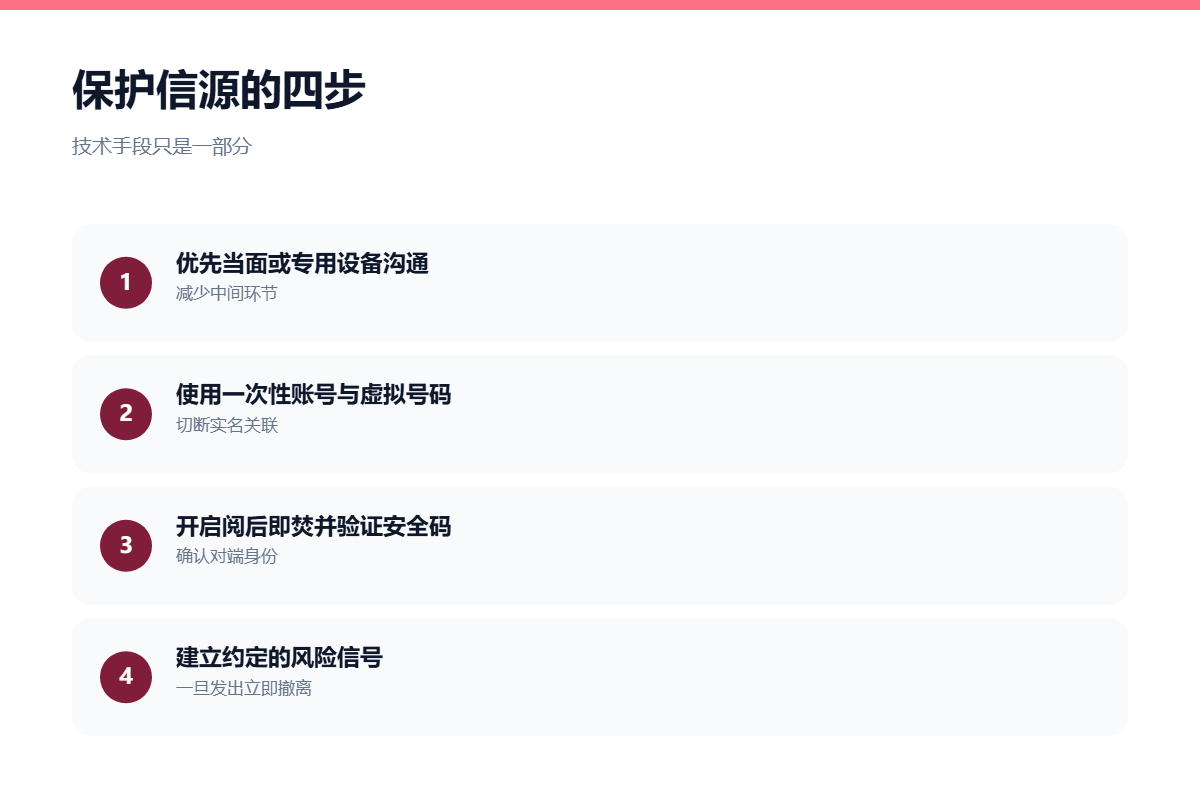
- Use a dedicated device and account.
- Never mix personal and professional identifiers.
- Enable expiring messages for sensitive exchanges.
- Verify the counterpart identity before talking.
- Agree a risk signal in advance.
- Assume the fact of contact is visible.
None of these steps make contact invisible. Together they reduce what a platform, a network or a third party can conclude.
FAQ
Is 聊天软件记者信源 protection ever complete?
Not with a normal consumer app. The content can be protected, and the fact of communication usually cannot, which is why operational separation matters.
What is the biggest risk to 聊天软件记者信源?
Linking identities. A shared device, a reused number or an overlapping contact list defeats encryption entirely, and it is the most common failure.
Do expiring messages help?
They reduce what remains on both devices and they do not remove what the platform recorded. Treat them as one layer rather than a solution.
References
- Source protection — Wikipedia
- End-to-end encryption — Wikipedia
- Privacy — Electronic Frontier Foundation
For related findings, read our notes on metadata privacy and our audit of expiring messages. If identity separation is your concern, our registration review is relevant.
评论
还没有评论,来说两句吧。
评论功能已关闭。