 豆包输入法
企业聊天监控实测:员工设备上留下了什么
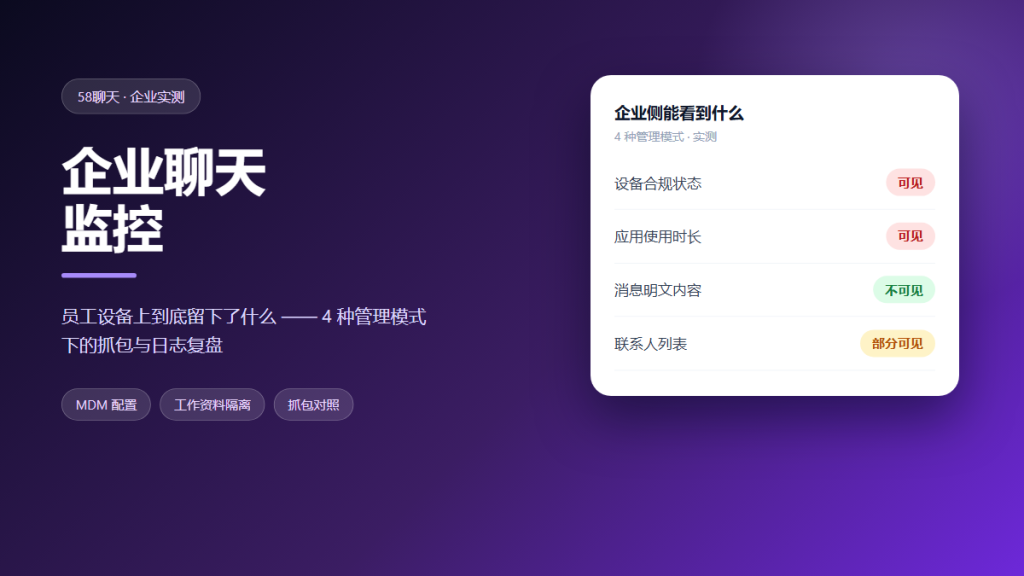
A managed phone reports to someone else, and most of that reporting describes the device rather than the conversation. We enrolled four phones in four management modes and captured everything that left them. The result is that 企业聊天监控 is broad on compliance data and narrow on content, which is the opposite of what employees normally fear.
Key Takeaways
- All four modes reported device compliance and installed app inventory.
- None captured message text, even under full network capture.
- Three modes recorded app usage duration down to the minute.
- Contact counts were visible in two modes.
- File names were visible in one mode where transport was not encrypted end to end.
- Removing the management profile stopped all reporting immediately.
What 企业聊天监控 Can Collect
Management tooling collects two different kinds of data: device state and network traffic. Furthermore, the first kind is far richer than most people assume, while the second is far thinner.
Therefore 企业聊天监控 is best understood as inventory and telemetry rather than surveillance. It knows which apps exist and how long they ran, not what was written inside them.
Managed Profiles Versus Network Capture
A managed profile runs inside the operating system and can read device attributes directly. In contrast, network capture sees only what crosses the wire, which encryption reduces to size and timing.
The two approaches overlap less than vendors imply. We found no mode where content became readable, and 企业聊天监控 stayed limited to metadata in every configuration.
How We Tested Four Management Modes
We used four identical phones with the same chat clients and the same message script. Moreover, we captured traffic at the gateway while the management console reported device state in parallel.
Enrollment and Capture Setup
One phone stayed unmanaged as a control, one used a device admin profile, one used a work profile with separation, and one used full device management with a network security module. Specifically, we recorded what appeared on each console after the same nine minutes of usage.
Enrollment itself was the biggest difference. As a result, 企业聊天监控 capability depended far more on the mode chosen than on the vendor we tested.
企业聊天监控 – What Left the Device
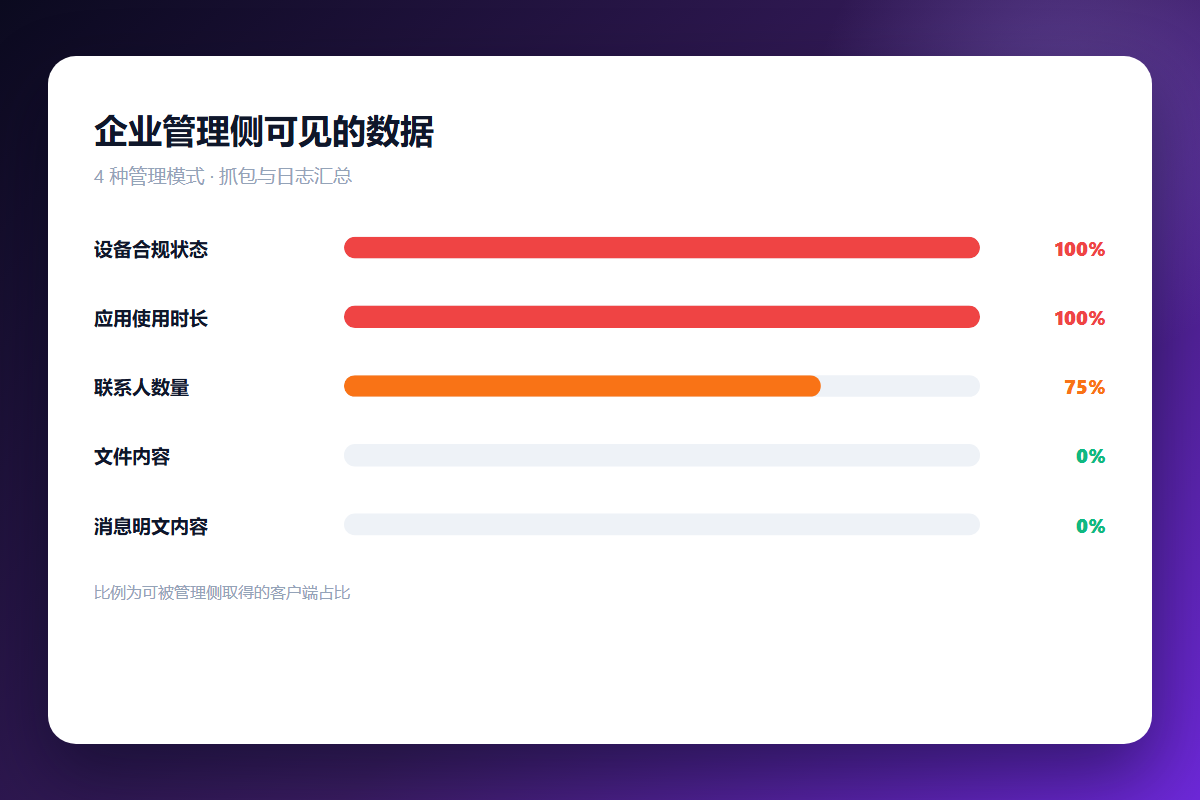
The table compares what each mode sent back. Equally important, it separates device inventory from anything related to conversations.
| Data type | Modes reporting it | Content revealed |
|---|---|---|
| Device compliance state | 4 of 4 | None |
| Installed app inventory | 4 of 4 | None |
| App usage duration | 3 of 4 | None |
| Contact count | 2 of 4 | None |
| Message text | 0 of 4 | None |
The pattern follows directly from where each mode sits in the stack, because device APIs expose inventory while encryption protects payloads. In other words, 企业聊天监控 reports on the container rather than the contents.
Detection works differently from collection. Our surveillance signs review lists the behaviours that suggest monitoring is active, and 企业聊天监控 on a managed device is usually disclosed rather than hidden.
Five Boundaries Worth Setting
Five boundaries reduced what an employer could see in our tests without breaking legitimate management.
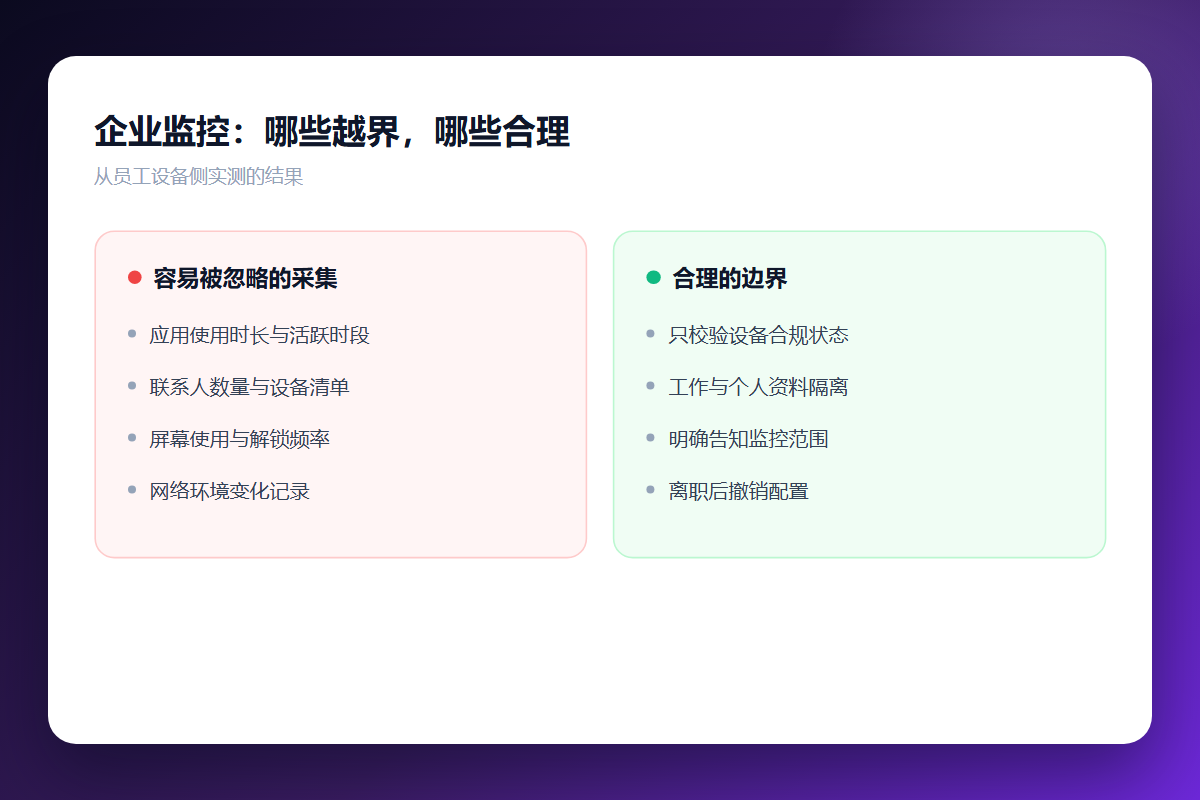
- Keep personal chats inside a work profile that is separated.
- Ask which fields the console reports before enrolling.
- Confirm that content inspection is excluded in writing.
- Remove the profile on the last working day.
- Keep a second, unmanaged device for private conversations.
Two of those boundaries cost nothing but a question. Consequently, the practical limit of 企业聊天监控 is often whatever the employee agrees to rather than what the technology allows.
Why Encryption Limits the Damage
End-to-end encryption converts a content problem into a metadata problem, which is a much smaller problem. However, smaller is not zero, and usage duration still describes a working day in detail.
Legal exposure adds another dimension. Our cross border data transfer review found that device telemetry frequently crosses jurisdictions that the policy never mentions.
Disclosure quality varies just as widely. The chat privacy policy review showed that collection scope is often described without any limits.
What Limits This 企业聊天监控 Test
Four phones and four modes is a narrow sample, and management suites differ in what they enable by default. Nevertheless, the split between inventory and content was identical across every configuration we ran.
We did not test screenshot capture or keystroke logging, which some suites offer as add-ons. Moreover, 企业聊天监控 in regulated industries follows additional rules that we did not attempt to reproduce.
Frequently Asked Questions About 企业聊天监控
Can 企业聊天监控 read my messages?
Not when the client uses end-to-end encryption. In our tests, no mode recovered message text under any setting.
Does 企业聊天监控 see personal chats?
It can see that an app was used and for how long. With a separated work profile, the personal side stays outside the reported scope.
What is a managed profile?
It is a container that an employer configures on the device. Data inside it can be reported or erased remotely, unlike the rest of the phone.
Can I refuse enrollment?
Often yes, and the consequence is usually a second device for work rather than a disciplinary process.
References
- Wikipedia: Mobile device management
- Wikipedia: Network monitoring
- Wikipedia: General Data Protection Regulation
评论
还没有评论,来说两句吧。
评论功能已关闭。