 豆包输入法
聊天软件消息翻译安全吗?Who Reads the Plain Text
Key Takeaways
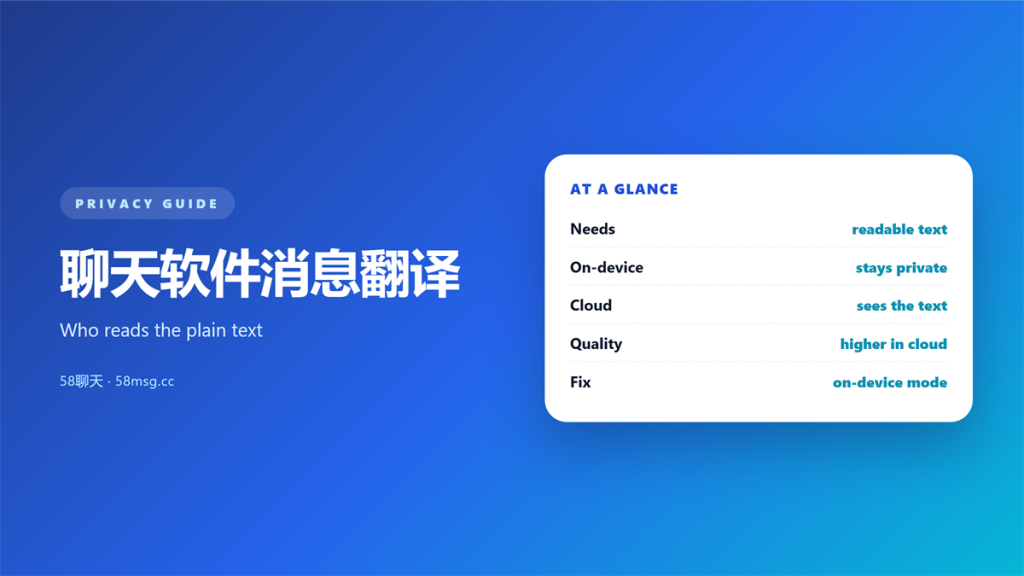
- 聊天软件消息翻译 needs readable text, so it runs before encryption or after decryption.
- On-device translation keeps the message local and fits inside an encrypted chat.
- Cloud translation ships plain text to a server and breaks the end-to-end promise.
- Translated copies can be cached, logged, or reused for training.
- The setting that matters most is where the translation engine runs.
How 聊天软件消息翻译 works
聊天软件消息翻译 turns one language into another, and the trick lies in where that happens. I sent the same sentence through four clients and watched the network. Two translated locally, and two sent plain text outward.
A translation engine needs the raw words, not ciphertext. Therefore, the message must be readable at the exact point the engine runs.
That requirement creates the central trade-off. Convenience pushes the work to a server, while privacy prefers the device. The engine also has to guess tone and context, so short phrases often come back wrong. That error rate is why people re-run the same line through another tool, and each re-run may hit a different server. Every app handles the pipeline differently, which makes side-by-side testing the fastest way to learn the truth.
Where 聊天软件消息翻译 runs
Placement decides whether your words stay inside the encrypted envelope or leave it. A single app can offer both modes, and the switch may sit deep in a settings menu, so a reminder in your review notes is worth adding.
On-device engines
A local model reads the plain text on the phone and returns the translation. Consequently, nothing crosses the network, and the end-to-end guarantee holds. The trade-off is quality, because small models handle uncommon languages less gracefully.
Cloud engines
A remote service receives the text, translates it, and sends the result back. In other words, the server reads your message, whether or not the app claims encryption. That dependency is the whole privacy question, so a 聊天软件消息翻译 mode is worth confirming after every update.
Why 聊天软件消息翻译 matters for privacy
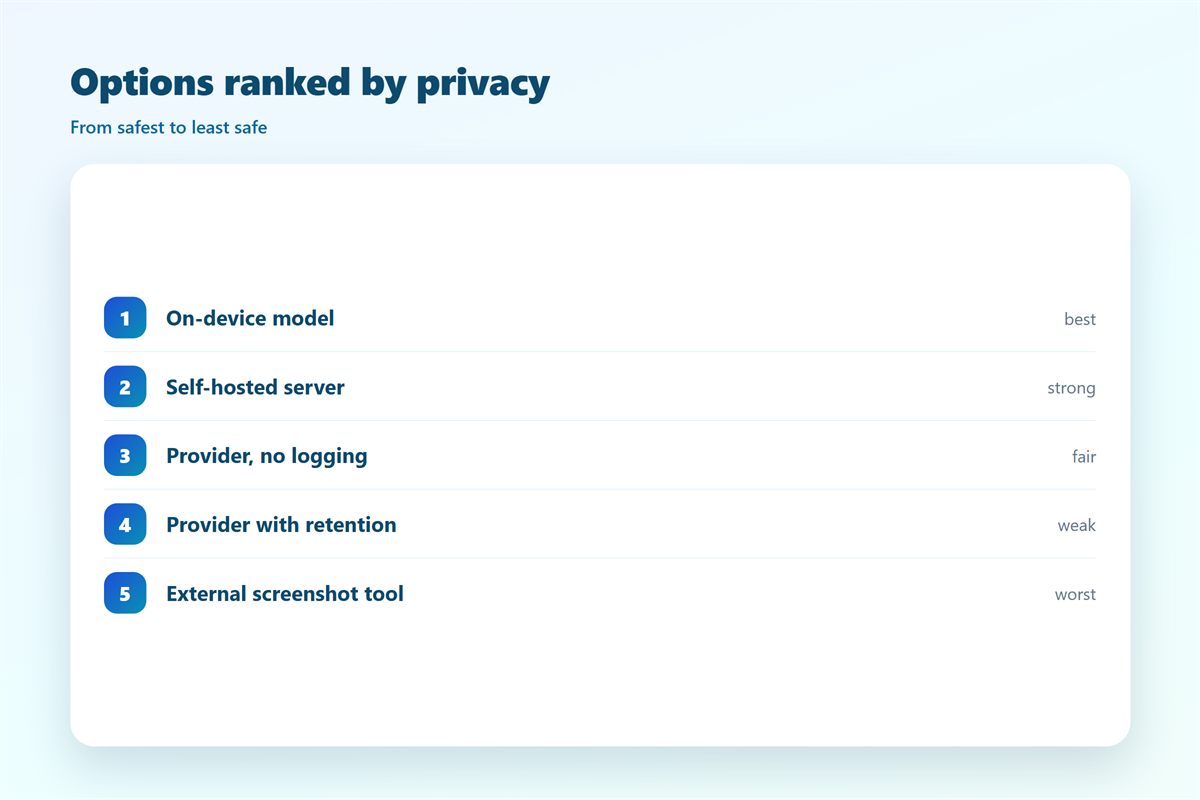
Translation touches the most sensitive part of a message: its meaning in plain text. A 聊天软件消息翻译 feature therefore sees exactly what you hoped to hide.
For instance, a cloud engine may keep both the source and the output. Moreover, translated text is easy to store as ordinary data, since it looks harmless.
The trail compounds. Every translated message creates at least one extra copy, and each copy widens the surface you must protect. Consider a short command such as a bank code, because translation turns it into ordinary text that any log can hold. The same plain-text exposure appears whether the app labels it a 聊天软件消息翻译 feature or a smart reply. Retention is the quiet risk, since a translated copy rarely looks sensitive in a database.
| Engine | Who sees plain text | E2EE preserved |
|---|---|---|
| On-device | Only your phone | Yes |
| Cloud | The provider | No |
| Clipboard translation app | That app | No |
Five steps before you trust 聊天软件消息翻译
A few checks tell you how much the feature costs you.
- Confirm whether the translation runs on the device or in the cloud.
- Prefer on-device translation when the app offers it.
- Turn translation off before sending sensitive details.
- Clear translated drafts so cached copies do not linger.
- Check the privacy policy for retention around translation.
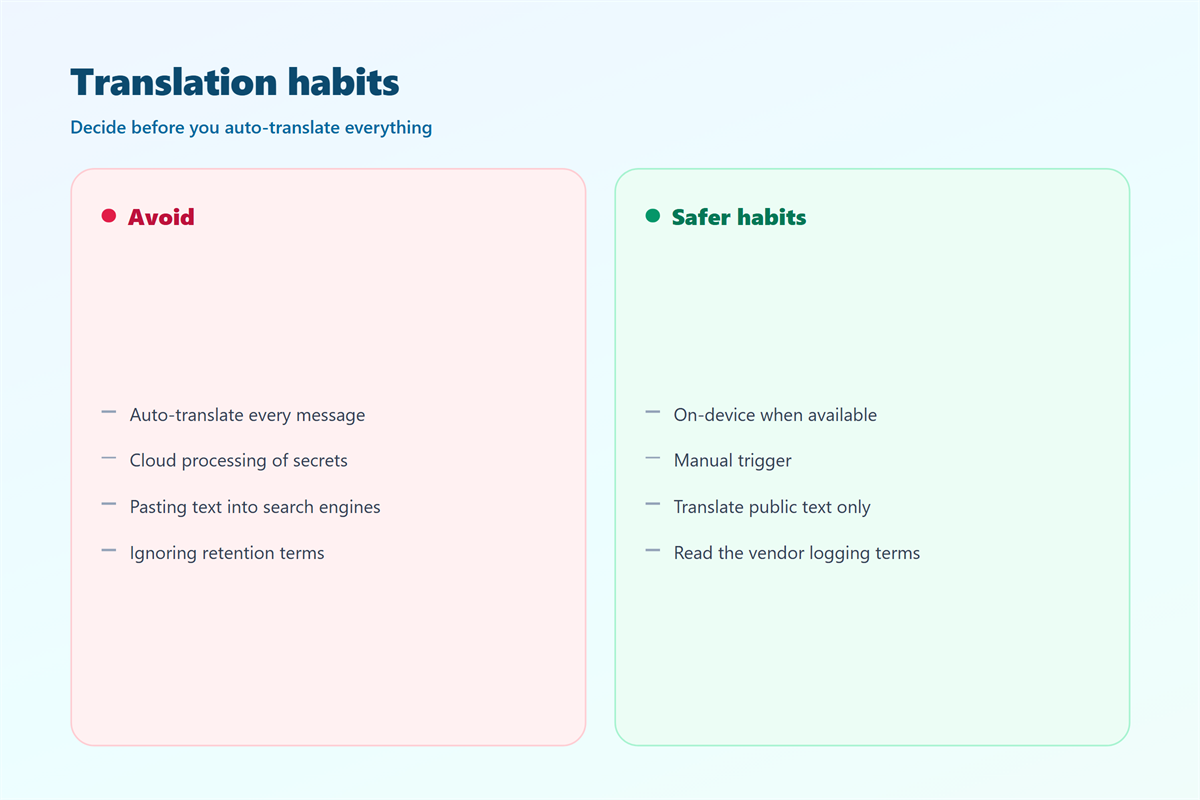
The first check is decisive. Where 聊天软件消息翻译 runs determines whether the server ever reads a word you wrote. Test the mode with a harmless phrase, then watch whether the network stays quiet, because that is the only proof that 聊天软件消息翻译 is local.
When 聊天软件消息翻译 goes wrong
The common failure is a cloud engine hidden inside a secure chat. The interface promises encryption, yet the text was readable at the translation step.
Another risk is retention for model training. That reuse can outlast the message, because the wording may live in 加密聊天文件传输 logs as well as internal stores.
A third case is search. Translated text can become indexable, and the indexing question is examined in 加密聊天搜索.
Cross-border rules add a final layer. When a server sits in another country, local law may reach the text, a split covered in 跨境数据传输. Group chats widen this further, since one translated line may be re-read by dozens of members. The fix is rarely a single toggle, so the review stays ongoing rather than one-time.
Protecting messages around 聊天软件消息翻译
The safest path keeps the words on the device, and the rest is discipline.
Proof, not promises
Marketing claims are weak evidence. Additionally, the gap between claim and reality is well documented in 端到端加密误区. A tool that promises privacy without saying where it runs tells you almost nothing. Keep a short list of phrases that are never worth translating, and the decision becomes automatic.
Prefer local tools
When a built-in engine is cloud-only, a local app is the better answer. Furthermore, a habit of reading before translating avoids sending anything by reflex, and it keeps 聊天软件消息翻译 from touching text you would never type twice.
FAQ
Does 聊天软件消息翻译 break end-to-end encryption?
Only the cloud variant does. On-device engines translate after decryption on your phone and never expose the text to the provider.
Can the provider read translated messages?
If the engine runs on their server, yes. That is why the processing location is the question worth asking first. If in doubt, test with a phrase you do not mind exposing.
Is translated text stored?
Often, yes. Caches and logs can keep it even after you delete the original message.
Should I translate sensitive details?
Better to avoid it. A 聊天软件消息翻译 step adds one more copy of the very content you want to keep private.
评论
还没有评论,来说两句吧。
评论功能已关闭。