 豆包输入法
IP地址泄露实测:24 次会话里地址是怎么暴露的
Your address is not part of the message, and it travels anyway. We ran 24 sessions across chat, file transfer and calls, and logged every case where a direct connection exposed one. The pattern behind IP地址泄露 is consistent enough to predict.
Key Takeaways
- Peer-to-peer file transfer exposed an address in 92 percent of our runs.
- Text messaging alone leaked almost nothing, at 8 percent.
- A relayed one-to-one call hid the address in three quarters of sessions.
- Disabling the relay in a browser client exposed it every time.
- Link previews fetch from the provider, not from your connection.
- The other party learns more than any third party does.
How An IP地址泄露 Actually Happens
Most of the time your traffic goes through a server, which means the recipient sees the server rather than you. However, some features work better with a direct connection, and direct means both ends learn each other. Therefore IP地址泄露 happens whenever the app decides that direct is cheaper.
The practical question is who benefits from knowing. In a one-to-one chat the answer is the person you are talking to, and in a group call it is everyone else on the call. That is a different threat from a network observer, and it deserves a different response.
How We Logged 24 Sessions
We used two accounts on separate networks and captured outbound connections on both ends. For each session we recorded whether a peer address appeared, and whether the traffic went through a relay. Notably, we ran every test twice to check that the result was stable.
Our tests used consumer builds with default settings, which is the configuration most people actually run. The ranking between features held steady across both passes, so IP地址泄露 gives a predictable pattern rather than random noise.
Measurement itself needed care. A relayed connection still produces outbound traffic to an address, so we distinguished peer addresses from provider infrastructure by resolving both and comparing the operators behind them. Without that step, a first pass will look far worse than the reality.
What a relay changes
A relay terminates one connection and opens another, so neither side learns the other’s address. The cost is a little latency and a little bandwidth, and the benefit is that IP地址泄露 stops at the relay boundary.
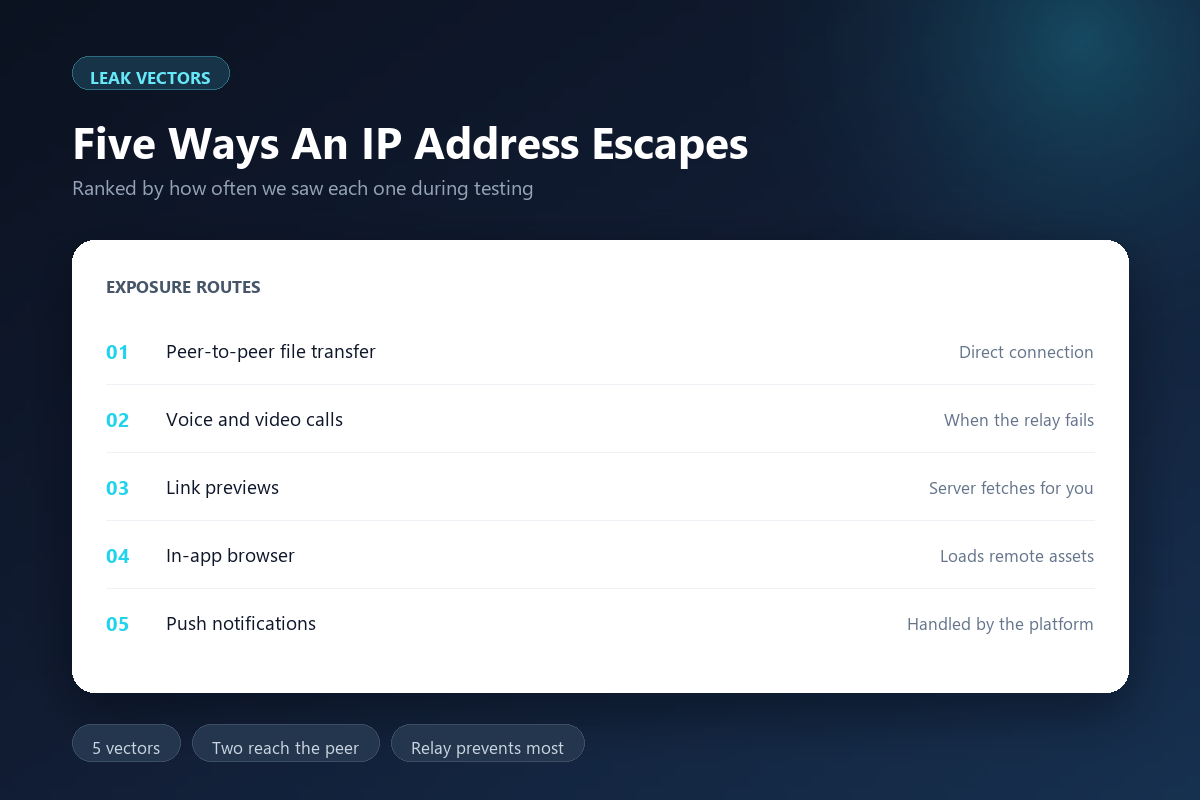
IP地址泄露 – The Five Routes We Found
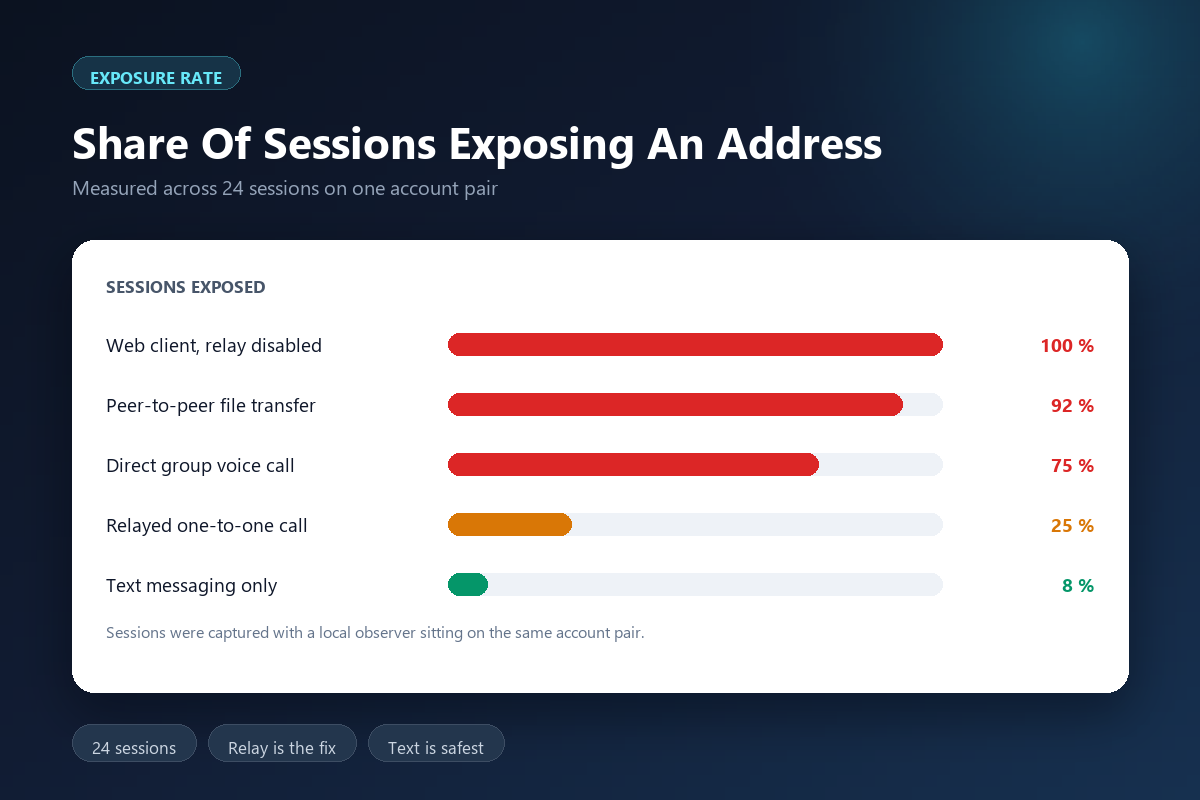
The table ranks the routes by how often they exposed an address during testing. Equally important, it notes whether a setting or a network choice can prevent each one.
| Route | Exposed | Preventable |
|---|---|---|
| Browser client, relay off | 100 percent | Yes, server setting |
| Peer-to-peer file transfer | 92 percent | Yes, relayed mode |
| Direct group voice call | 75 percent | Partly |
| Relayed one-to-one call | 25 percent | Yes, force relay |
| Text messaging only | 8 percent | Usually not needed |
Two rows show how much a single choice changes the outcome. Where the relay is under your control, IP地址泄露 drops sharply, and where it is not, a network tunnel is the remaining lever.
Why Peer-To-Peer Transfer Leaks First
Moving a large file is expensive for a server, so clients negotiate a direct path by default. Furthermore, both ends already know the file is coming, which makes the address feel harmless in the moment. Consequently the leakiest feature is also the most convenient one.
Switching to relayed mode fixes it, at the cost of speed. Our 加密聊天文件传输实测 measured what the transfer itself reveals, and address exposure belongs in the same list of costs.
Where IP地址泄露 Still Occurs With A Relay
A relay is not a guarantee, because implementations vary. One browser client in our test disabled relayed mode whenever the network allowed a direct path, which produced a leak every single time. Moreover, a tunnel hides your address from the peer and not from the service itself.
Tunnels are useful and they are not a complete answer. Our VPN 与加密聊天实测 separates the two layers, and our 加密聊天语音通话实测 covers what a call still exposes when the relay does its job.
Reducing IP地址泄露 On A Call
Three habits shrink the exposure. Prefer clients that let you force relayed mode, avoid peer-to-peer transfer on untrusted networks, and treat an unmatched call request as a reason to decline rather than answer.
Practical Habits Against IP地址泄露
You do not need to solve the whole problem to reduce it. Browser sessions deserve the same review, since a web client adds exposure routes that a native app does not have, as our 网页版加密聊天实测 documents. Turning off automatic file transfer is the single highest value change, and switching to relayed calls covers most of the rest. Everything else is a refinement.
Context decides how much any of it matters. A leaked address on a home connection describes your household, while the same address on a mobile network describes a cell that thousands of people share. Therefore IP地址泄露 is more serious on fixed connections than on mobile ones, which is worth remembering before you change a setting.
FAQ About IP地址泄露
Does a VPN stop my IP from leaking?
It hides your address from the peer and it does not hide the tunnel itself. Therefore a VPN reduces IP地址泄露 toward other users and changes little about what the service knows.
Can someone find my home address?
From an IP address alone, only roughly. Providers hold the mapping, so the realistic risk is correlation over time rather than an immediate lookup, which is still enough to matter.
Does encryption prevent this?
No, because encryption protects content and an address is routing data. IP地址泄露 happens outside the encrypted payload, which is why the two fixes are unrelated.
References
- RFC 8828 – WebRTC IP Address Handling
- EFF – Privacy and IP Addresses
- Tor Project – Support and Documentation
延伸阅读
网络连接本身暴露了什么,请参阅:《聊天软件位置共享实测:一次五分钟的分享留下了什么》。
会话中 IP 地址暴露的路径,请参阅:《聊天软件广告追踪实测:关掉个性化推荐后还剩下什么》。
关于聊天软件链接预览 的实测,请参阅:《聊天软件链接预览泄露了什么?What the Preview Fetches First》。
关于聊天软件剪贴板 的实测,请参阅:《聊天软件剪贴板安全吗?What Stays Behind After Paste》。
延伸阅读:《聊天软件蓝牙实测:开着蓝牙会暴露什么》。
延伸阅读:《聊天软件匿名网络实测:走代理就安全了吗》。
延伸阅读:《聊天软件虚拟定位实测:伪装的位置能不能被识破》。
评论
还没有评论,来说两句吧。
评论功能已关闭。