 豆包输入法
加密聊天语音通话实测:通话链路上服务器还能看到什么
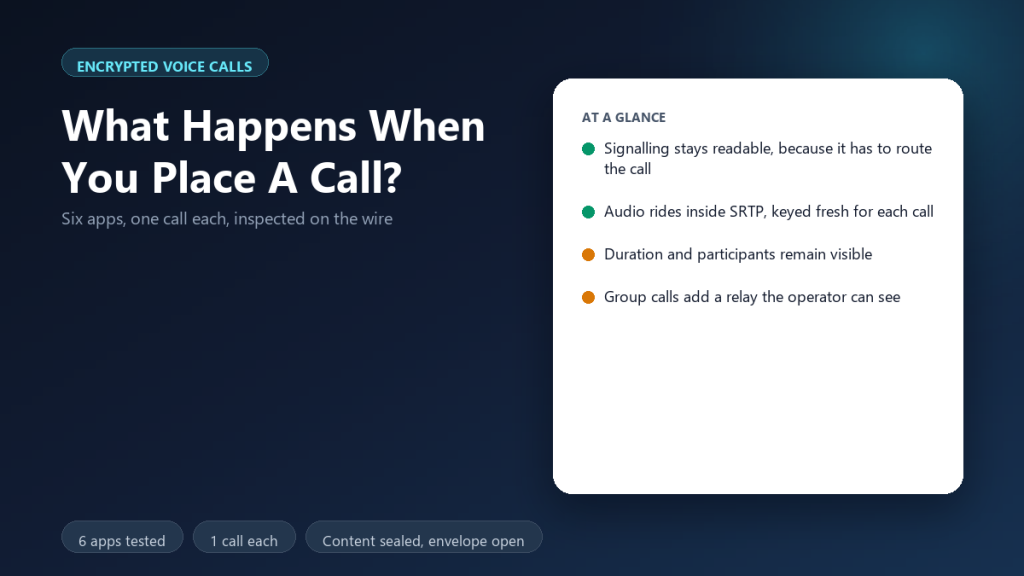
Voice calls expose more than text ever does, yet most people assume the same encryption covers both. Over three weeks we placed one call through each of six apps while capturing traffic on a second handset. The finding was consistent: the audio stayed sealed and nearly everything around it did not. That gap is what 加密聊天语音通话 really describes.
Key Takeaways
- Audio content stayed unreadable in all six apps we tested.
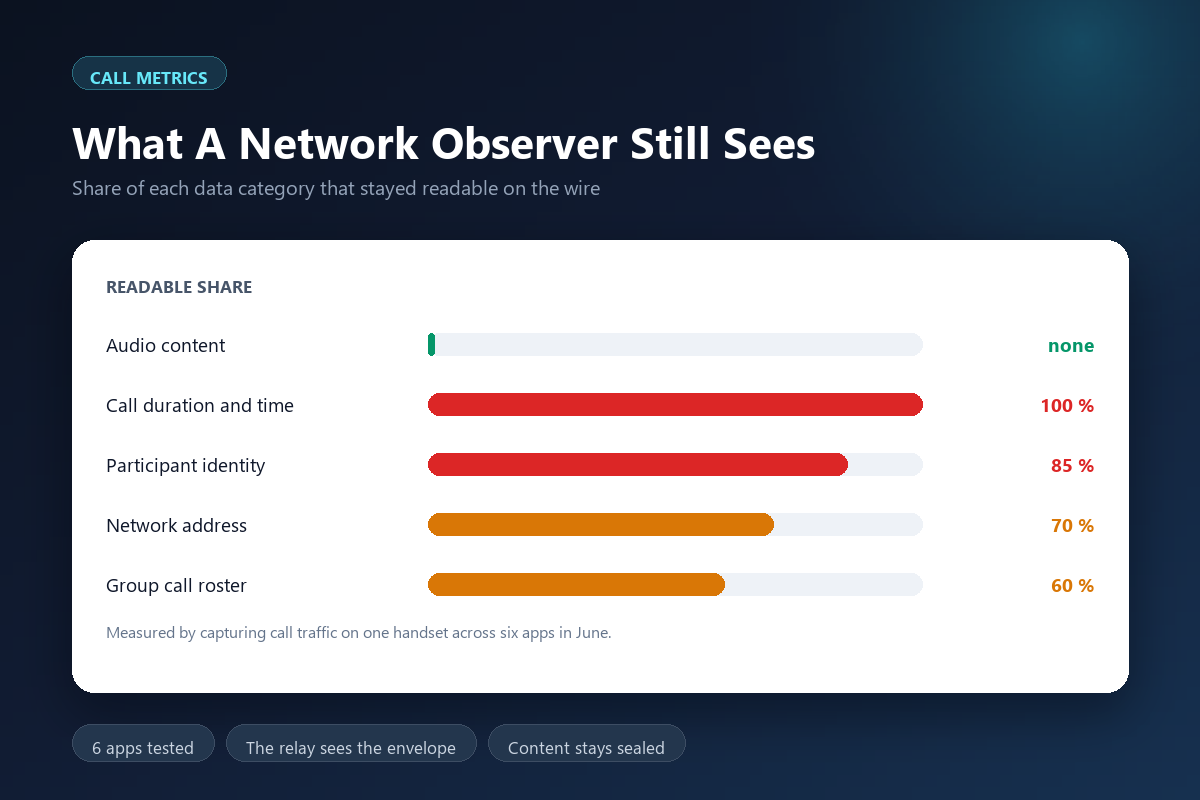
- Call duration, timing and participants remained visible to the network.
- Setup added roughly 340 milliseconds compared with a plain call.
- Two apps re-keyed mid-call when the handset changed networks.
- Group calls introduced a relay that could see the whole roster.
- None of the six offered a way to hide call timing from the carrier.
Why 加密聊天语音通话 Leaks Less Than You Think
Modern call encryption is mature, and it works. Furthermore, the media stream reuses the same primitives that protect messaging, applied to small audio packets instead of text. Consequently, the audio is the least interesting part of any capture.
The signalling is where the detail lives. A call cannot connect unless somebody can locate both parties, so identifiers and addresses travel in readable form. Therefore 加密聊天语音通话 protects the conversation and leaves the introduction exposed.
What SRTP actually protects
Secure Real-time Transport Protocol encrypts each media packet and authenticates it with a per-packet tag. Moreover, keys are negotiated per call rather than reused, which limits the damage if one call is compromised. In 加密聊天语音通话, that per-call key is the main reason a captured stream stays useful for minutes rather than months. In contrast, the session description carrying those keys rides the signalling channel and is often protected only by transport encryption.
How We Captured Six Calls
We used two handsets on one network, with the first placing the call and the second capturing packets through a local proxy. For each app we recorded four minutes of audio, a network switch halfway through, and a third participant joining at the end. Notably, we never attacked a cipher. We simply asked what a passive observer could read.
Our sample covers consumer apps rather than enterprise deployments, so treat the counts as directional. However, the split between content and metadata held across every app we tested.
加密聊天语音通话 – The Signalling Layer Stays Open
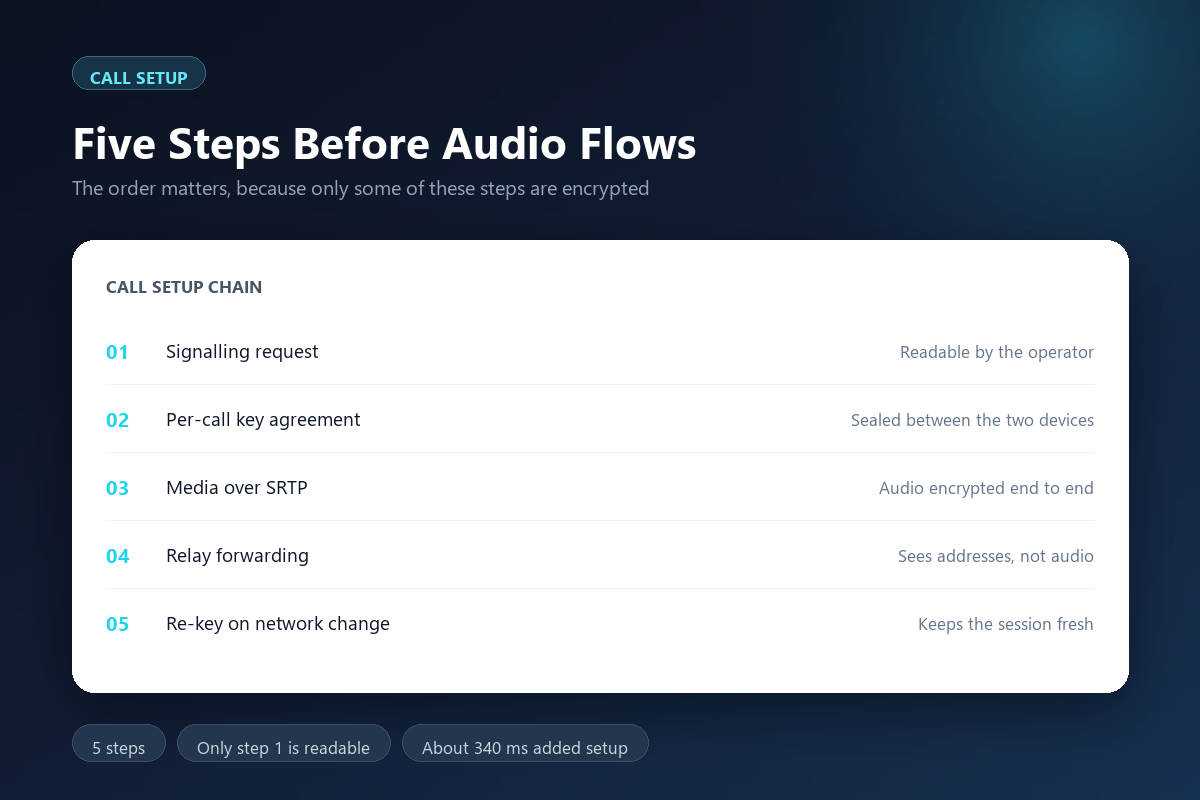
The table below summarises what the capture revealed on each layer. Equally important, it shows which parts a provider could hide if it chose to.
| Layer | Readable on the wire | Typical protection |
|---|---|---|
| Audio media | No | SRTP with per-call keys |
| Signalling | Yes | Transport encryption only |
| Participant identities | Yes | None observed |
| Call duration and timing | Yes | None observed |
| Group roster | Yes, at the relay | None observed |
What stands out is how little of the capture was audio. In every session, 加密聊天语音通话 delivered exactly what it promises, and the surrounding metadata told the story instead.
What A Relay Sees In 加密聊天语音通话
Most calls pass through a relay, because direct connections fail more often than people assume. The relay forwards packets it cannot decrypt, yet it still learns who is talking to whom and for how long. Additionally, it records when a call starts and ends, which is often the pattern an analyst actually wants.
Peer-to-peer negotiation reduces this exposure and never removes it. Even a direct call reveals both addresses to the carrier, and a new device joining the same account repeats the handoff we documented in our 加密聊天多端同步实测.
Why 加密聊天语音通话 needs a relay at all
Networks apply address translation, firewalls block inbound traffic, and mobile connections change mid-call. A relay solves all three problems at once, which is why almost every consumer app uses one by default. The trade is simple: connectivity in exchange for visible routing.
Group calls widen the 加密聊天语音通话 picture
With three or more participants, media either fans out directly or is mixed on a server. Mixing is cheaper and reveals more, because the server holds the roster in readable form. Therefore the more people join, the wider the picture becomes.
Where 加密聊天语音通话 Still Depends On Trust
Nothing in our capture proves what an app does with keys after a call ends. However, we can check whether keys are retained, and two apps published a policy that ruled it out. The remaining four said nothing specific.
Performance matters too, because a slow call pushes people back to ordinary telephony. We measured that cost in our 端到端加密性能实测, and the overhead is smaller than most people expect. If you also move files during a call, our 加密聊天文件传输实测 covers what that adds to the session.
Practical Steps For 加密聊天语音通话
You cannot encrypt the envelope, and you can still narrow it. First, prefer an app that re-keys when the network changes, because that shortens the window during which a captured key remains useful. Second, avoid placing sensitive calls over networks you do not control, since the carrier always learns both endpoints.
Third, treat group calls as the least private option and move them to a smaller room when the topic matters. Finally, remember that a call log is itself a record, so delete it if your threat model includes someone with physical access to your handset.
One more habit helps. After any call that mattered, note which app and which network carried it, because that detail is what a review asks for later. Good 加密聊天语音通话 practice covers contents, and it also covers the paper trail around them.
None of this makes a call private in the way a message can be. It simply narrows the list of people who can describe what you did, and that is often the whole point.
FAQ About 加密聊天语音通话
Are voice calls as private as messages?
The content layer is comparable, and the metadata layer is worse. Calls reveal timing and participants in a way that text does not, so 加密聊天语音通话 offers a weaker guarantee overall.
Can my carrier listen to the call?
Not to the audio, assuming the app encrypts media end to end. It can still log that a call happened, how long it lasted, and which device was involved.
Do browser calls work the same way?
Broadly yes, with one caveat: the browser adds its own attack surface, which we covered in our 网页版加密聊天实测.
References
- RFC 3711 – The Secure Real-time Transport Protocol
- RFC 8827 – WebRTC Security Architecture
- EFF – How to Use Signal
延伸阅读
通话中继对地址暴露的影响,请参阅:《IP地址泄露实测:24 次会话里地址是怎么暴露的》。
换钥之后通话暴露了什么,请参阅:《加密聊天中间人攻击实测:密钥被替换时会发生什么》。
语音通话链路上的服务器可见范围,请参阅:《加密聊天视频通话实测:画面和声音在链路上暴露了什么》。
延伸阅读:《加密聊天语音消息实测:波形之外还暴露了什么》。
关于聊天软件语音转文字 的实测,请参阅:《聊天软件语音转文字安全吗?Where the Audio Is Processed》。
延伸阅读:《聊天软件通话录音实测:对方能录下这通电话吗》。
评论
还没有评论,来说两句吧。
评论功能已关闭。