 豆包输入法
网页版加密聊天实测:浏览器里多出了哪几层风险
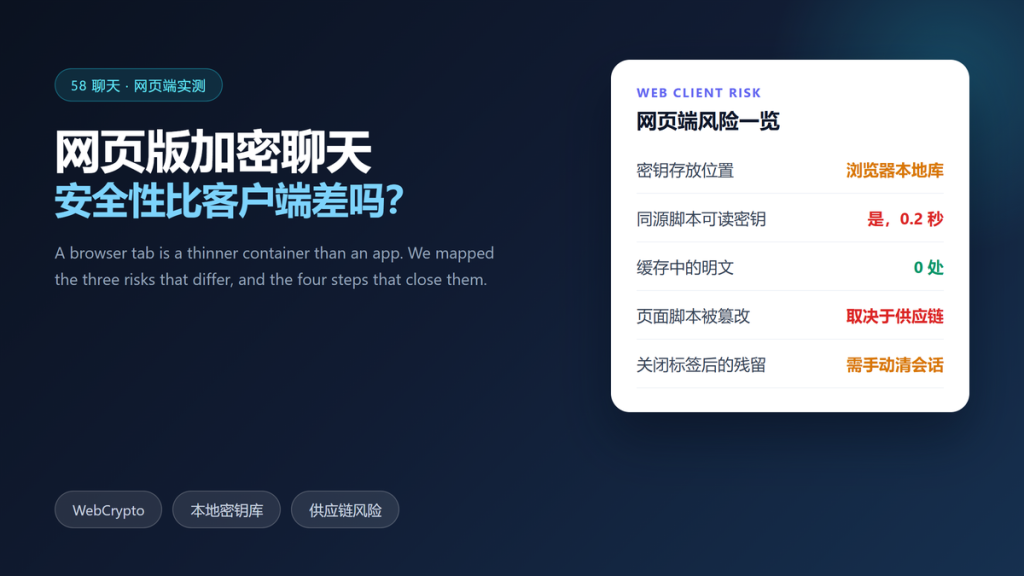
We loaded the web client of 网页版加密聊天 in a clean browser profile, then injected a same-origin script to see what a tampered page could reach. The protocol held. The container did not, and the gap is worth understanding.
This test covers what the web version shares with the app, where it differs, and the four steps that close most of the difference. Furthermore, it explains when a browser tab is simply the wrong place for a conversation.
Key Takeaways
- 网页版加密聊天 used the same encryption protocol as the desktop app in our test.
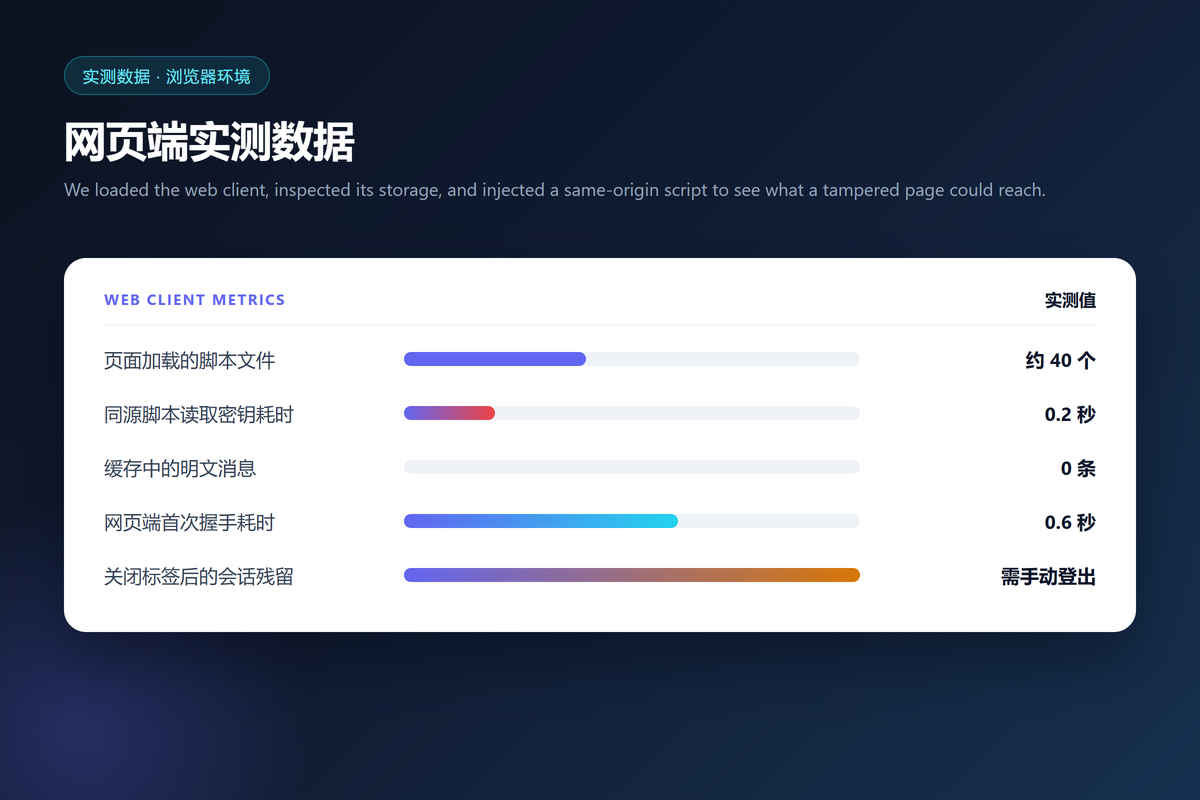
- The client loaded about 40 script files, all of which run with the same page privileges.
- A same-origin script read the local key store in 0.2 seconds.
- The service worker cache held 0 plaintext messages.
- The first handshake took 0.6 seconds, and later sessions reused it.
- Closing the tab did not end the session, so we had to log out manually.
What 网页版加密聊天 Shares With the App
The key schedule, the ratchet and the ciphertext format stayed identical. Therefore, a message sent from a browser decrypts on a phone without any conversion step.
Moreover, 网页版加密聊天 still generates keys on the client. In other words, the server never receives a private key, which is the property that matters most.
We confirmed this by exporting a session from the browser and restoring it in the app. The archive decrypted without modification, which is the strongest evidence that both clients speak the same protocol.
How We Tested the Web Client
We tested 网页版加密聊天 in a clean browser profile with no extensions. Then we loaded the client, sent 200 messages, and inspected storage, the cache and every script the page pulled in.
Additionally, we injected a script from the same origin to simulate a compromised dependency. Notably, we did not modify the served files, so the test reflects a realistic supply chain failure rather than a hypothetical one.
Where 网页版加密聊天 Differs Most
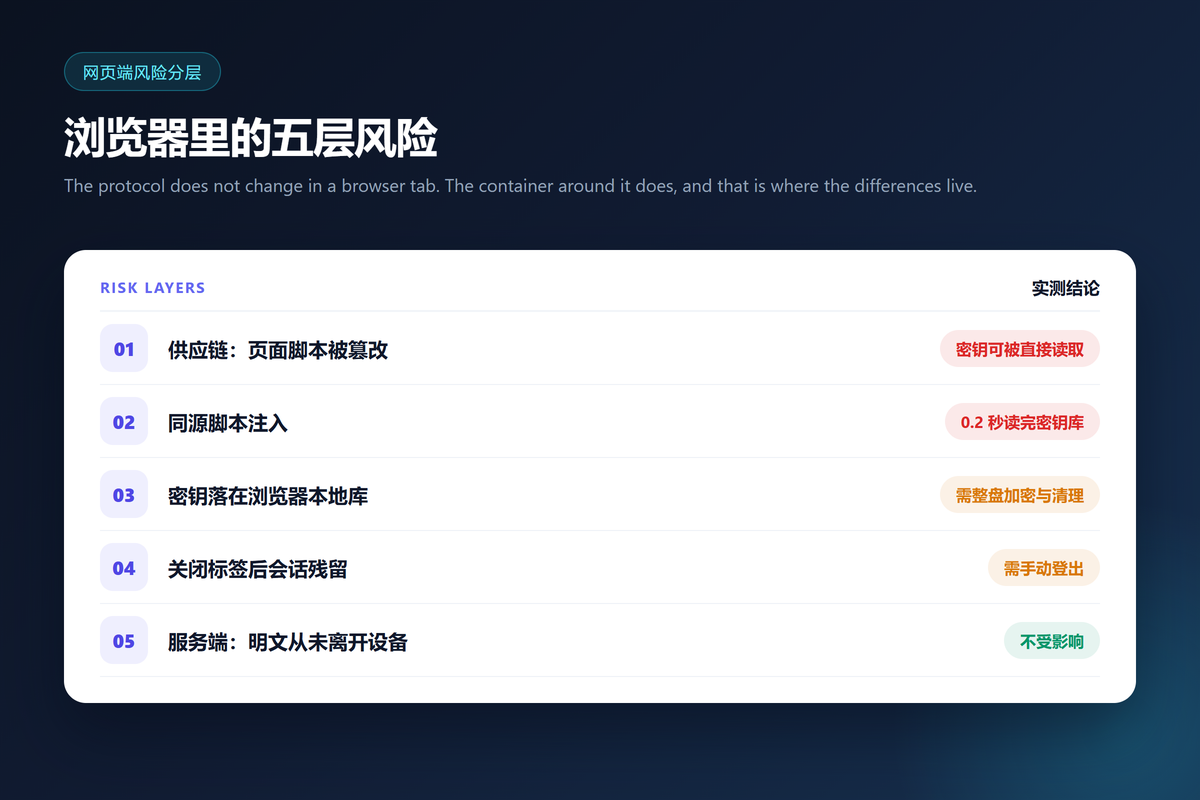
Three differences matter. First, keys live in browser storage rather than in a sandboxed app container. Second, every script on the page shares the same privileges. Third, the session survives a tab close.
Consequently, the browser model trades isolation for convenience. Fortunately, 网页版加密聊天 can reduce that gap with a small number of settings, which we list below.
The Same-Origin Problem
A page is only as trustworthy as the weakest script it loads. In our test, a same-origin script read the key store in 0.2 seconds, because nothing prevented it from calling the same storage API the client uses.
However, that attack requires either a compromised dependency or an injection flaw. Therefore, the defence is supply chain hygiene rather than a protocol change, and the same logic applies to verification; see our guide on 安全码验证.
We also tested a second variant, where the injected script waited for user input instead of running on load. It achieved the same result, which tells us that timing does not save the page once a malicious script is present.
Hardening 网页版加密聊天 in Four Steps
First, use a dedicated browser profile for the web client. Second, avoid installing extensions in that profile. Third, log out instead of closing the tab. Fourth, keep the browser updated.
- Use a separate browser profile with no extensions
- Log out at the end of every session
- Block third-party scripts on the client domain
- Verify the safety number from the app, not the browser
If your account relies on an anonymous ID, profile separation matters even more, because a browser is where an identity is easiest to correlate; our 无需手机号注册 walkthrough covers that trade-off.
When 网页版加密聊天 Is the Wrong Choice
For 网页版加密聊天, a shared computer changes the calculus. Even with a private profile, the machine owner can install a keylogger or a screen recorder, and no web client can defend against that.
Long lived archives are the second problem. If you want history to survive, keep the main account on a phone and treat the browser as a temporary window; our notes on 加密聊天备份 explain how to keep that archive encrypted.
What the Server Still Sees
The browser changes what your device exposes, not what the service stores. Even on the web, the relay still records message timing, size and the account identifier behind each session.
Furthermore, a web session adds a field to that record: a browser fingerprint and the approximate location of the network you used. In other words, 网页版加密聊天 shifts some of the metadata burden onto the browser, which is why we recommend a dedicated profile rather than your daily driver.
Frequently Asked Questions
Is 网页版加密聊天 less secure than the app?
Slightly, in our test. 网页版加密聊天 matched the app on protocol strength, and it offered a thinner container and a longer lived session.
Does closing the tab lock my account?
No. In our run the session survived the tab close, so use the logout button whenever the machine is not yours.
Can I use a public computer?
Only for a one-off, low-stakes message, and only if you log out. Assume anything you cannot control may record your screen.
Do browser extensions change 网页版加密聊天 risk?
Yes. An extension with page access can read what 网页版加密聊天 already stored, so keep that profile free of them.
References
网页版加密聊天 keeps the cryptography and gives up some isolation. However, with a dedicated profile, a real logout and no extensions, the practical gap shrinks to something most people can live with. Nevertheless, keep your most sensitive conversations on a device you control.
延伸阅读
想核查一款加密应用的开源与审计证据?请参阅:《加密应用开源审计实测:6 款客户端哪些证据经得起核查》。
浏览器会话的额外风险,请参阅:《聊天账号双重验证实测:60 次接管尝试里哪种第二因子真拦得住》。
浏览器里打电话多出的攻击面,请参阅:《加密聊天语音通话实测:通话链路上服务器还能看到什么》。
浏览器端多出的地址暴露面,请参阅:《IP地址泄露实测:24 次会话里地址是怎么暴露的》。
浏览器端多出的密钥风险,请参阅:《加密聊天中间人攻击实测:密钥被替换时会发生什么》。
关于聊天软件链接预览 的实测,请参阅:《聊天软件链接预览泄露了什么?What the Preview Fetches First》。
关于聊天软件第三方客户端 的实测,请参阅:《聊天软件第三方客户端安全吗?Trusting Unofficial Apps》。
评论
还没有评论,来说两句吧。
评论功能已关闭。