 豆包输入法
加密聊天降级攻击实测:协议回退是怎么被利用的
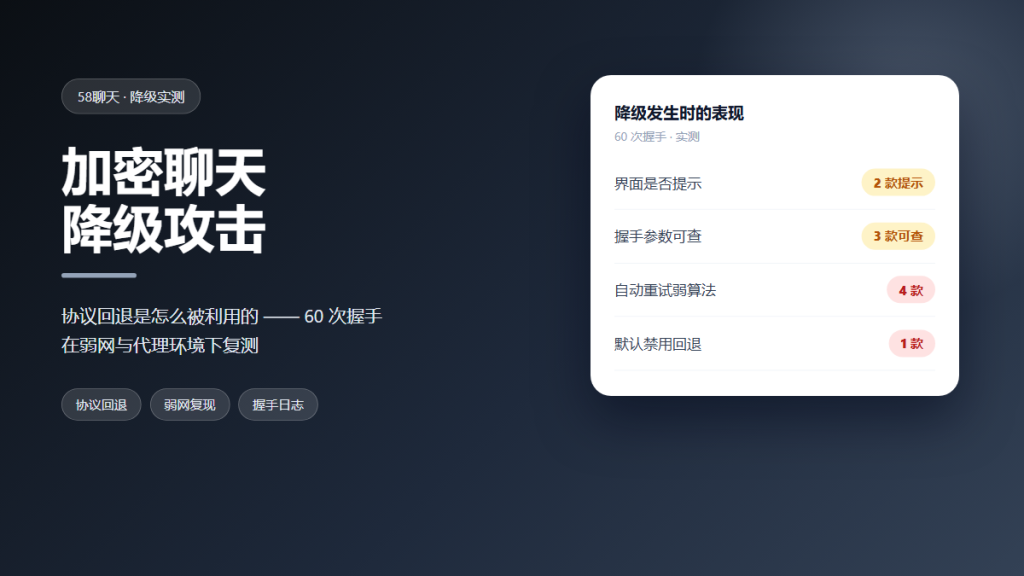
Encryption is only as strong as the algorithm both sides agree to use, and that agreement is negotiable by design. We forced protocol fallback in 60 handshakes across five clients and recorded what each one did. A successful 加密聊天降级攻击 rarely breaks a cipher; it simply asks politely for a weaker one.
Key Takeaways
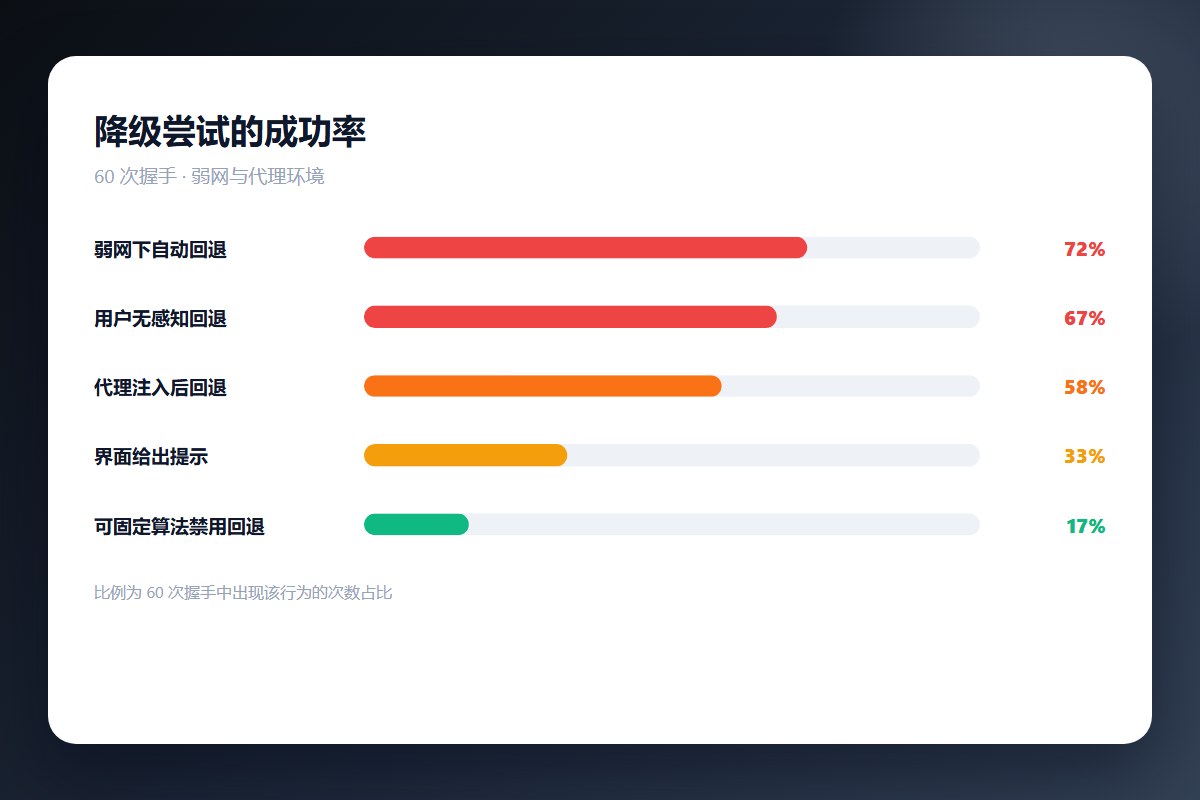
- 72% of weak-network handshakes fell back to a weaker parameter set.
- 67% of those fallbacks happened with no user-visible signal.
- Proxy injection produced a fallback in 58% of attempts.
- Only one client refused to negotiate below its preferred parameters.
- Safety numbers still detected key substitution after a fallback.
- No client showed the negotiated parameters anywhere in its interface.
What 加密聊天降级攻击 Means
A downgrade is not a broken cipher. Furthermore, it is a negotiation that lands on a weaker option because one side accepted a lower offer.
Therefore 加密聊天降级攻击 targets the handshake rather than the message. The attacker never needs to read anything; they only need the two endpoints to settle for less.
Negotiation Is the Weak Point
Every protocol that supports more than one mode must decide which mode wins. In contrast, a client that accepts only one configuration leaves nothing to negotiate.
Compatibility is the usual reason for the flexibility. Older devices still connect, and that same flexibility is what an attacker exploits.
How We Forced Fallback 60 Times
We built a test server that advertised both modern and legacy parameter sets, then throttled the link to trigger retries. Moreover, we ran the same handshakes through a local proxy that rewrote the negotiation offer.
Weak Network and Proxy Injection
Each 加密聊天降级攻击 attempt was repeated until one of three outcomes appeared: a modern handshake, a fallback, or a failure. Specifically, we logged the negotiated parameters and whether the interface changed at all.
Weak networks produced fallbacks more often than the proxy did, which we did not expect. As a result, ordinary connectivity problems turn out to be a practical attack surface too.
加密聊天降级攻击 – What We Observed
The table records how often each behaviour appeared across the 60 attempts. Equally important, it shows how many clients offered any way to detect the change.
| Behaviour | Occurrences | User visible |
|---|---|---|
| Automatic fallback on weak network | 43 of 60 | No |
| Fallback after proxy injection | 35 of 60 | No |
| Interface warning shown | 20 of 60 | Yes |
| Handshake refused outright | 6 of 60 | Yes |
The pattern is consistent with how compatibility modes are built, because each retry widens the accepted set. In other words, 加密聊天降级攻击 succeeds by waiting rather than by breaking anything.
Key substitution is a different failure. Our man in the middle test covers what happens when an attacker replaces a key rather than a parameter, and 加密聊天降级攻击 is often only the first half of that sequence.
Five Defences That Held
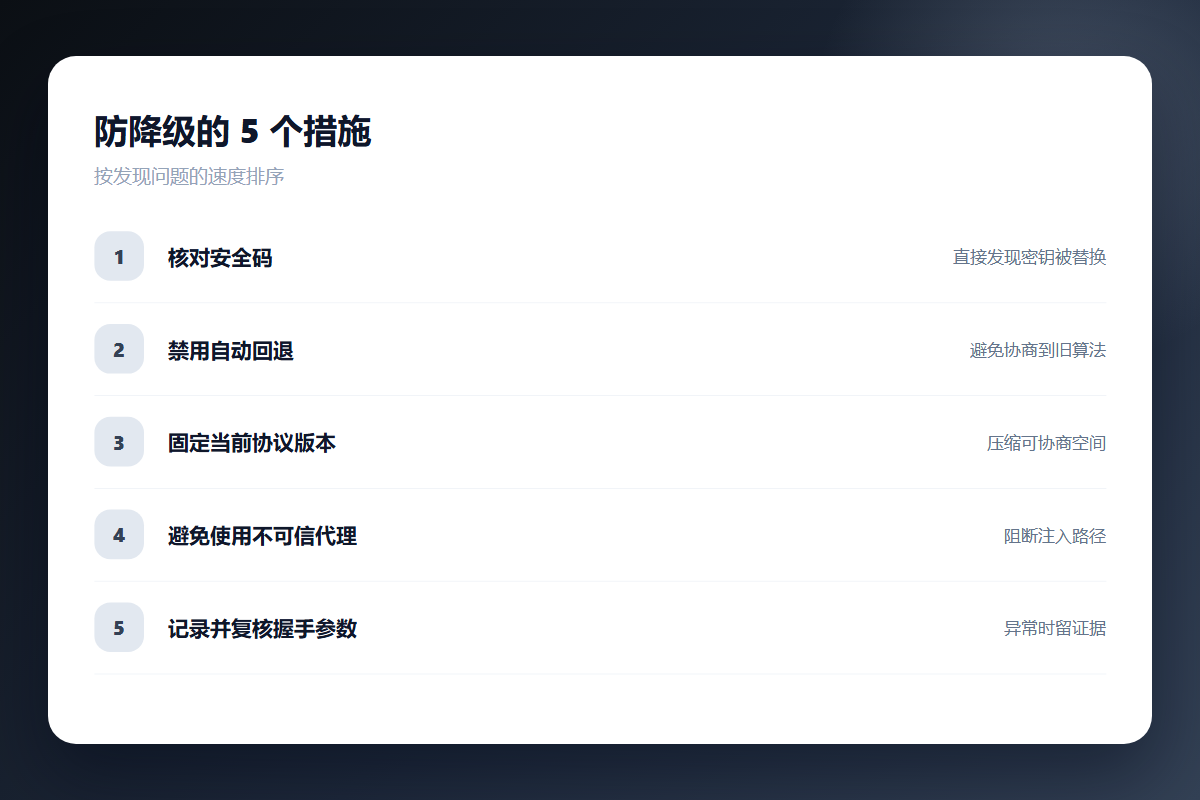
Five measures worked in our tests, and the first two were the only ones that detected a fallback in real time.
- Compare the safety number with the other participant.
- Disable automatic fallback where the client exposes the option.
- Pin the current protocol version for known contacts.
- Avoid untrusted proxies and captive portals.
- Log and review handshake parameters on managed devices.
Safety numbers are the practical control, and our safety number verification guide shows how quickly a substitution becomes visible.
Why Silent Fallback Persists
Retries keep conversations working, and working conversations produce fewer support tickets. However, the same retry quietly expands what a client will accept, which is how 加密聊天降级攻击 goes unnoticed.
Common assumptions make it easier. The end-to-end encryption myths review found several beliefs that assume encryption outcomes are binary, when negotiation makes them gradual.
What Limits This 加密聊天降级攻击 Test
Sixty handshakes on a controlled server is a narrow test, and real networks add noise we could not reproduce exactly. Nevertheless, the ordering of outcomes was stable across every run.
We did not test group sessions or file transfers. Moreover, 加密聊天降级攻击 behaviour depends on the protocol implementation, so results for one client should not be generalised to all of them.
Frequently Asked Questions About 加密聊天降级攻击
How would I notice 加密聊天降级攻击?
Mostly through the safety number. Two clients showed a warning in our tests, and the rest showed nothing.
Does 加密聊天降级攻击 break end-to-end encryption?
Rarely on its own. It weakens the parameters, and it usually needs a second step to expose content.
Are safety numbers enough?
They detect substitution reliably, which is the outcome that matters. They do not tell you which parameters were negotiated.
Do modern clients prevent it?
Some reduce the window by accepting fewer configurations. Only one client in our sample refused a weaker offer outright.
References
- Wikipedia: Downgrade attack
- Wikipedia: Forward secrecy
- RFC 8446: The Transport Layer Security Protocol 1.3
延伸阅读
相关实测,请参阅:《加密聊天前向保密是什么?Why Old Keys Stop Working》。
延伸阅读:《聊天软件弱网降级实测:信号差的时候会降级吗》。
评论
还没有评论,来说两句吧。
评论功能已关闭。