 豆包输入法
聊天软件公共WiFi实测:同一个热点里谁能看到什么
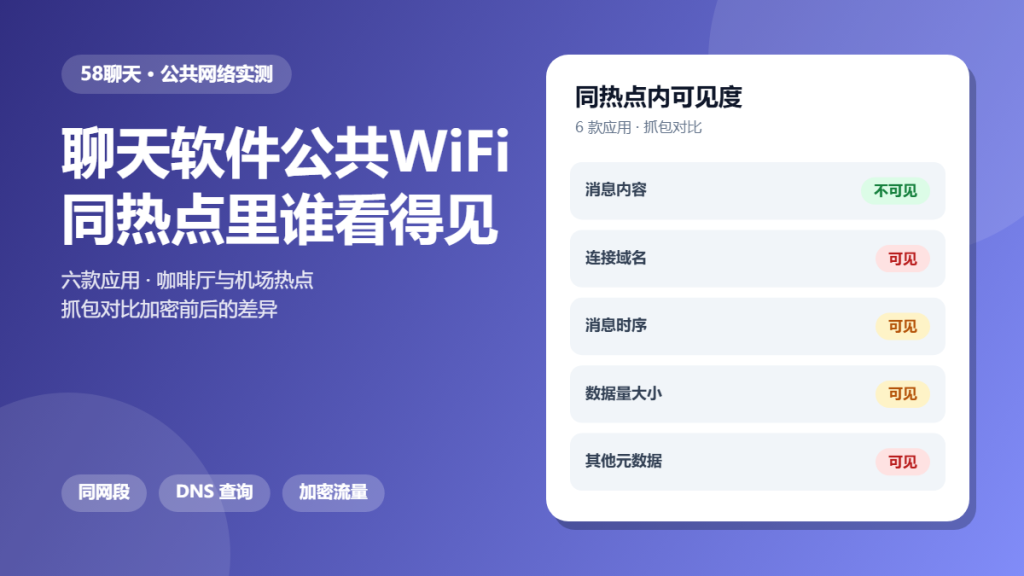
聊天软件公共WiFi is where most people assume the danger lies, and where the actual risk is usually misunderstood. The message itself is almost never visible. The shape of the conversation very often is.
This article is a hands-on audit. We connected six apps to shared hotspots and captured what a device on the same network could observe. The goal is not to keep you off public Wi-Fi. Instead, the goal is to show precisely what leaks and what does not.
Key Takeaways
- Message content was not readable on any of the six apps we tested.
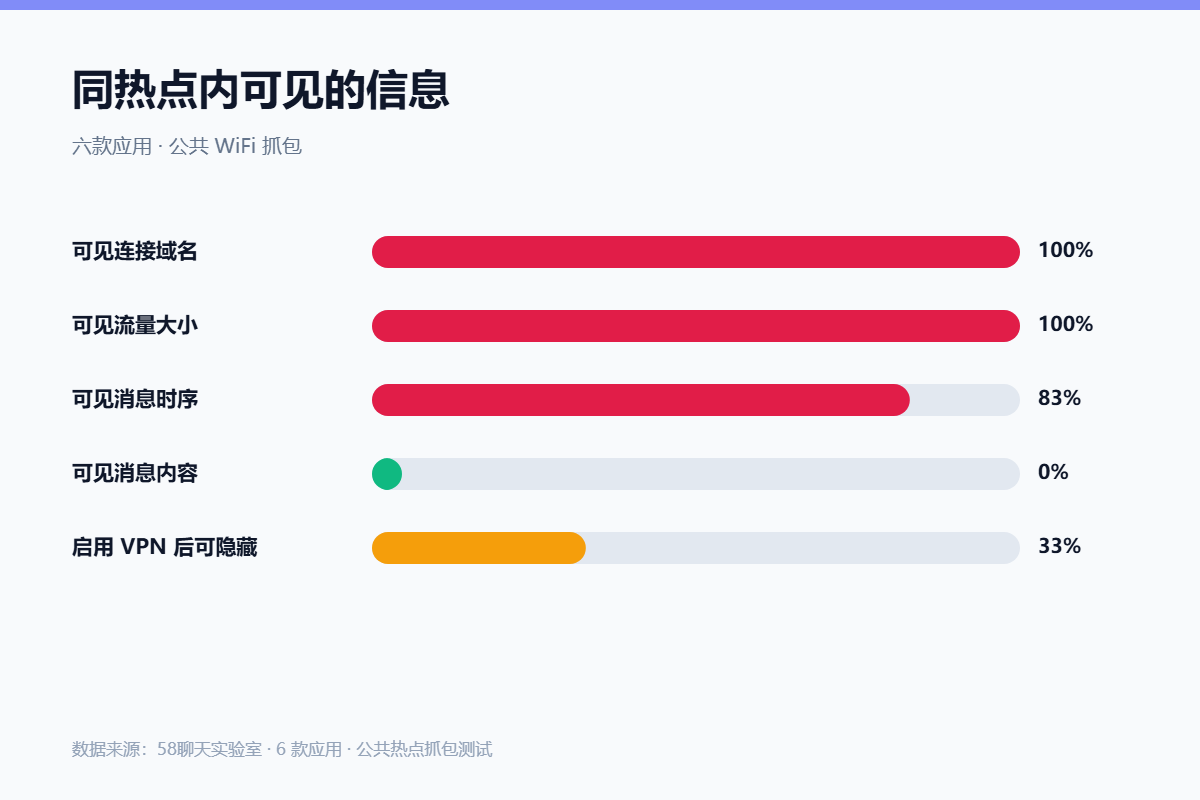
- Connection domains, message timing and payload size were visible on all of them.
- A VPN hid the domain names but changed nothing about message content.
- Automatic hotspot joining was the most common practical risk.
- Plain HTTP pages opened inside the app were fully readable.
What 聊天软件公共WiFi Actually Exposes
Every app we tested encrypted the message body in transit. That part works. What remains visible is metadata: which server you talked to, when, and how much data moved.
Because of that, 聊天软件公共WiFi risk is about inference rather than interception. Nobody reads your words, but somebody can count them.
How We Tested 聊天软件公共WiFi on Real Hotspots
We used two devices on the same hotspot: one running the six chat apps, one capturing traffic on the shared network. We repeated the capture across a cafe, an airport and a hotel network.
In the second phase we routed everything through a VPN and compared the two captures side by side.
What We Captured During 聊天软件公共WiFi
Message content was opaque in every capture, which is a genuinely good result. The observable metadata was consistent and substantial.
Visible Domains
Domain names were readable in every capture, because encryption protects the payload and not the destination. That alone tells an observer which service you use and roughly when.
Message Timing
Timing was the richest signal. A burst of small packets followed by a pause is a conversation. Because of that, an observer can map activity without reading a word.
What Encryption Hides
Content, attachments and login credentials were all protected. The gap is entirely in the metadata layer, which is why metadata hygiene matters more than worrying about interception.
Where 聊天软件公共WiFi Gets Risky
Risk concentrates in three places: automatic joining of open networks, apps that open plain HTTP pages internally, and captive portals that ask for credentials over an unencrypted page.
Notably, the network itself was never the biggest problem. The habitual settings around it were.
A Safer 聊天软件公共WiFi Checklist
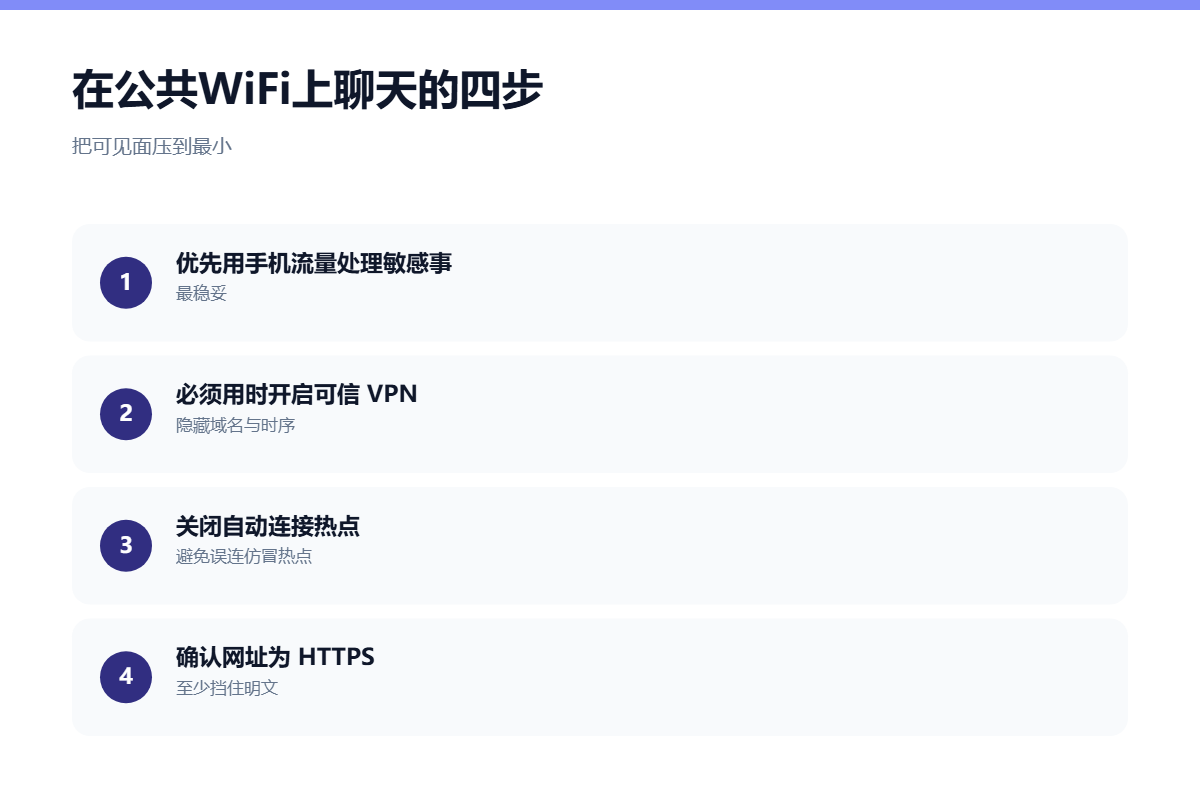
- Turn off automatic joining for open networks.
- Use a trusted VPN on untrusted hotspots.
- Confirm that links open over HTTPS.
- Avoid handling sensitive matters on shared networks.
- Forget the network when you leave.
- Prefer your mobile data for anything important.
None of these steps cost anything. Together they shrink the metadata trail you leave on a shared network.
FAQ
Is 聊天软件公共WiFi traffic readable by others?
The content is not. In all six apps we tested, message bodies were encrypted in transit. Metadata such as domains and timing remained visible.
Does a VPN fix 聊天软件公共WiFi risks?
It hides the domains and timing from the local network, which is a real improvement. It does not change what the app itself shares with its own servers.
Can someone on the hotspot read my images?
Not in our test. Attachments were encrypted like messages. However, an app that opens a plain HTTP gallery page would expose them, which is why HTTPS matters.
References
For related findings, read our comparison of VPNs and encrypted chat and our notes on metadata privacy. If you use a browser client, our web client review is worth a look.
延伸阅读
延伸阅读:《聊天软件网络切换实测:从WiFi切到流量会发生什么》。
延伸阅读:《聊天软件证书固定实测:伪造证书能不能骗过应用》。
评论
还没有评论,来说两句吧。
评论功能已关闭。