 豆包输入法
聊天软件第三方客户端安全吗?Trusting Unofficial Apps
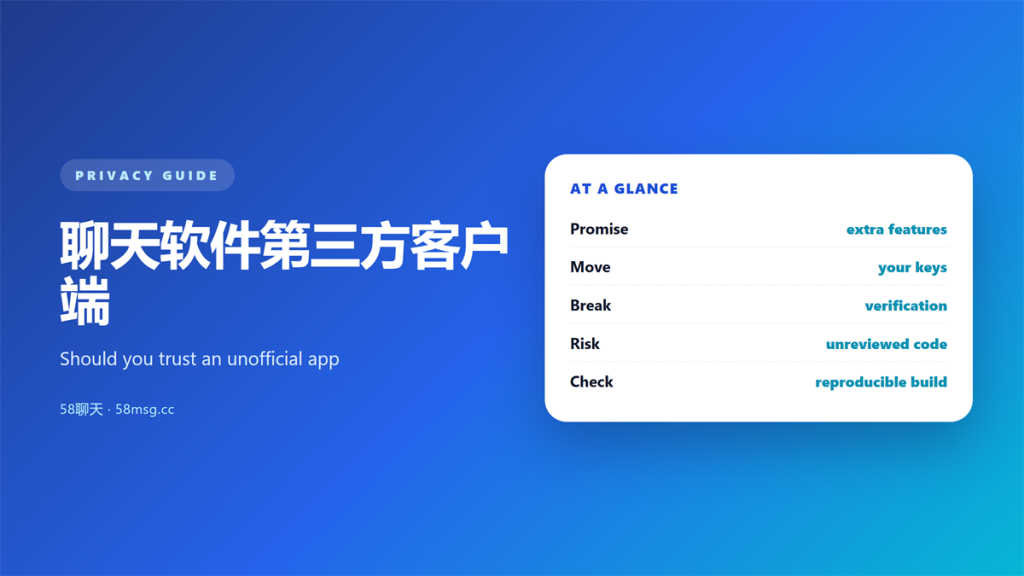
Key Takeaways
- 聊天软件第三方客户端 promise extra features while asking for the keys that guard your messages.
- Most forks reuse the official protocol, so the risk sits in the code around it.
- A client you cannot audit is a client you are trusting on faith.
- Update channels matter as much as the first release you installed.
- Comparing the safety number catches a swapped key in seconds.
How 聊天软件第三方客户端 differ from official apps
聊天软件第三方客户端 usually start as a friendly experiment. I installed one last month and the extra themes were genuinely pleasant. However, the moment it asked to link my account, the trust question arrived with it.
The reason is simple. Linking a device hands over key material. Consequently, a fork inherits everything the official client could do, plus whatever its own authors added.
In other words, 聊天软件第三方客户端 are not automatically hostile. They are simply unvetted, and unvetted code deserves a different level of caution.
The differences are not always visible, either. A fork can look identical to the official app on the surface, yet change how it talks to the server underneath. Therefore, 聊天软件第三方客户端 deserve a closer look than a screenshot can give.
What a fork can change
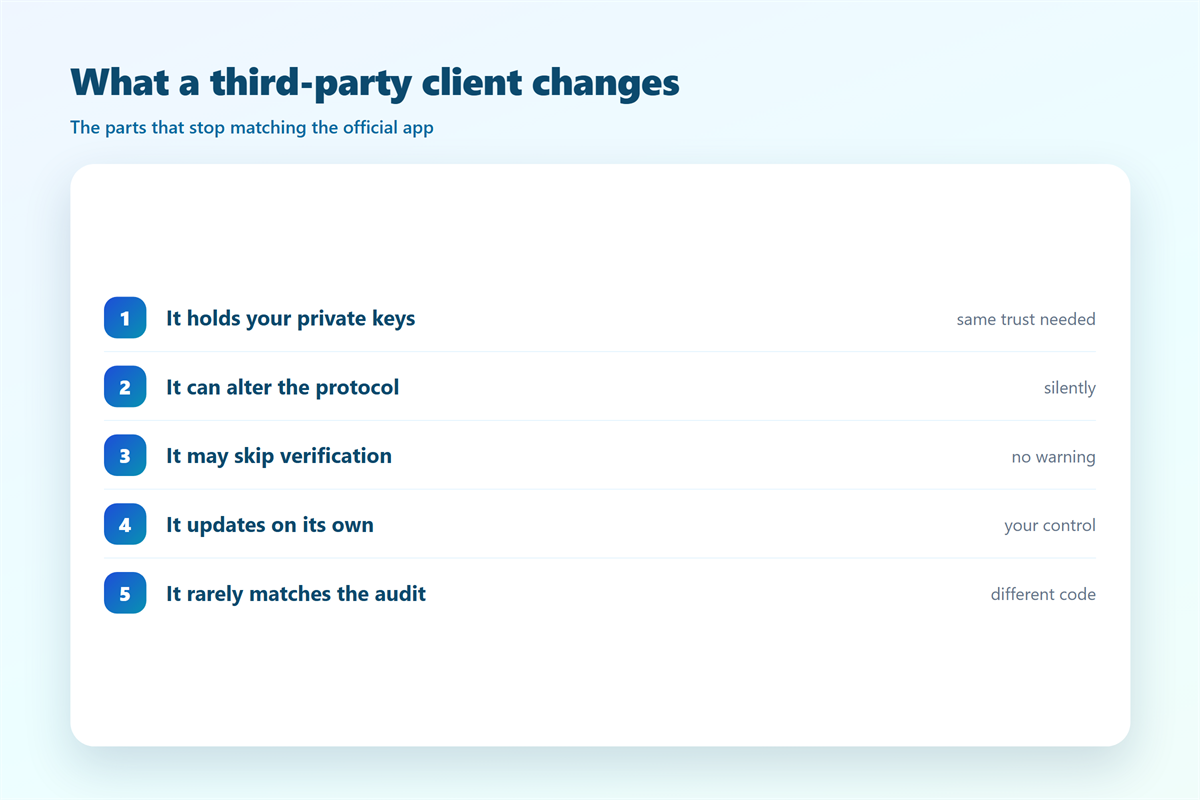
A fork can alter far more than an icon. The table below lists the parts I check first, because each one touches security.
| Component | What a fork may change | Why it matters |
|---|---|---|
| Key storage | Where private keys are written | A plaintext store is easy to copy |
| Network layer | Endpoints and proxies | A hidden relay can read metadata |
| Update path | Who signs new builds | A rogue channel can push anything |
| Crypto library | Which primitives are called | Subtle swaps weaken the handshake |
Key handling
The first thing I inspect is key storage. Moreover, a fork that keeps private keys in a readable file has already told me how much it values them.
Update channel
The second is the update path. Notably, a build is only as trustworthy as the signature that authorises the next one.
Why 聊天软件第三方客户端 attract risk
Popularity creates temptation. Attackers watch obscure builds, and they know maintainers are tired. Therefore, 聊天软件第三方客户端 can become a soft target precisely because nobody reviews them.
A second driver is funding. Volunteers rarely run audits, and a single compromised dependency can slip through unnoticed. Consequently, the code you downloaded last year may not be the code you are running today.
Additionally, some forks ask for broad permissions. That topic is covered in our review of 网页版加密聊天, where the browser adds its own layers of exposure.
Notably, the update problem is the sharpest one. Many 聊天软件第三方客户端 have no signed update channel at all, so users download a fresh build by hand and never verify it. As a result, the safest-looking fork can drift into an unsafe one without a single warning.
Five checks before installing 聊天软件第三方客户端
I do not reject forks outright. Instead, I run five checks, and most candidates fail at least one.
- Confirm the source repository is public and recently active.
- Look for an independent audit, not just a promise of one.
- Verify the download matches the published hash.
- Check whether the build signs its own updates.
- Read how it stores keys before you link an account.
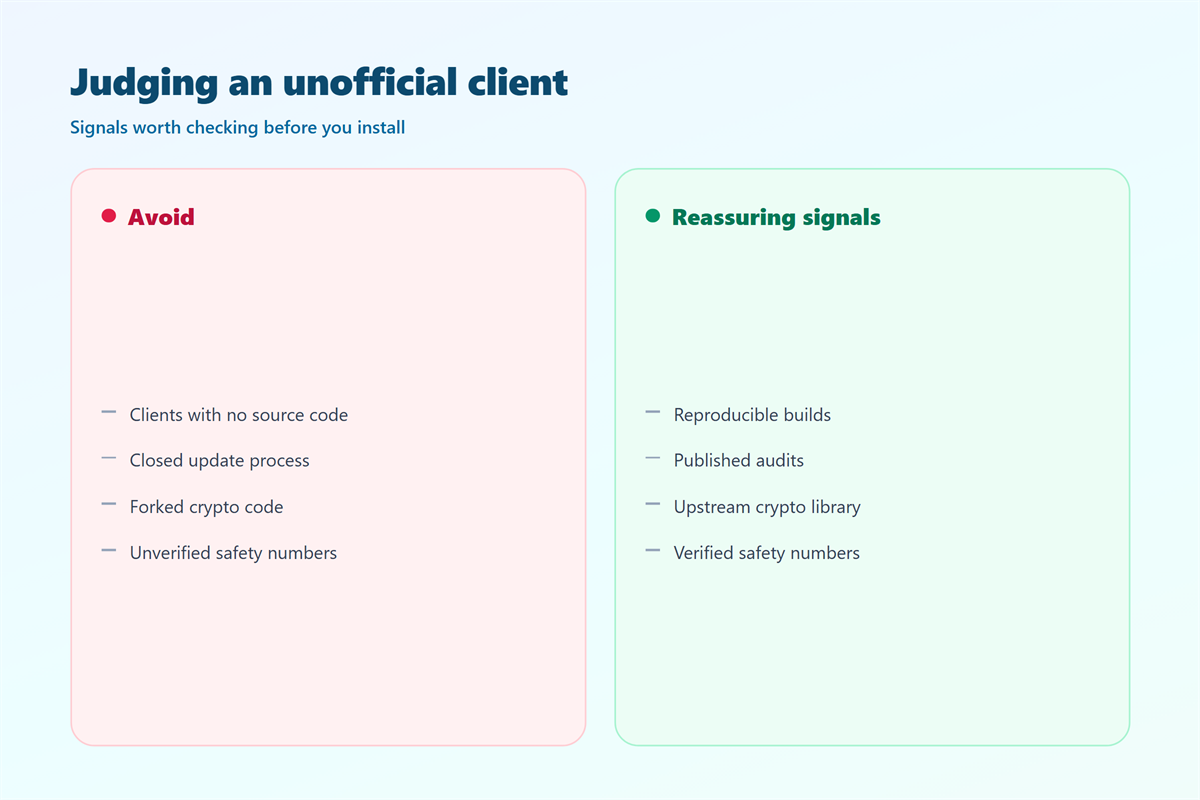
Most candidates fail the hash check first, and that single failure is reason enough to walk away. However, a clean hash plus a public audit is a genuinely good sign, so the routine rewards patience.
When 聊天软件第三方客户端 goes wrong
The obvious failure is malware with a chat icon. Less obvious is a fork that works fine for months and changes behaviour in a later build. Because users rarely re-check, that quiet change can persist.
A fourth case is harder to spot. A 聊天软件第三方客户端 may ship a slightly weakened encryption library, and the difference only shows when two devices compare numbers. Consequently, routine verification is the only reliable detector.
Another failure is a swapped key. A modified client can present its own key during setup, and the official server will never notice. This is the classic pattern we break down in 加密聊天中间人攻击.
Therefore, the defence is verification rather than blind trust. Even a suspicious build has trouble hiding when two devices compare their numbers.
Verifying a client beyond 聊天软件第三方客户端
Trust should rest on evidence, not vibes. Two habits make that practical, and both work with any client you choose.
Compare the safety number
Read the digits aloud and check them on both devices. Moreover, our walkthrough of 安全码验证 shows how a mismatch appears in seconds.
Sandbox the 聊天软件第三方客户端 build
Run a new 聊天软件第三方客户端 on a spare device first. In other words, let it fail somewhere that holds nothing you care about. Keep that test phone away from your real contacts.
Finally, prefer projects with a public audit trail. The evidence that separates serious work from guesswork is compared in 加密应用开源审计, and the pattern is consistent.
FAQ
Are 聊天软件第三方客户端 always unsafe?
No. Some forks are transparent and well maintained. However, the burden of proof sits with the client, not with you.
Can 聊天软件第三方客户端 break end-to-end encryption?
They cannot read traffic they never receive, but they can leak keys or inject their own. That is enough to defeat the guarantee in practice.
Is an unofficial client ever faster?
Sometimes, and speed is rarely the point. A lighter build may cut features that quietly protect you.
How do I check a client hash?
Download the file, run a checksum, and compare it with the value the project publishes. A mismatch means you stop.
References
- Wikipedia: Fork (software development)
- OWASP: Man-in-the-middle attack
- EFF: Trust and software security
延伸阅读
延伸阅读:《聊天软件漏洞赏金实测:报告之后发生了什么》。
延伸阅读:《聊天软件供应链攻击实测:第三方组件带来的风险》。
延伸阅读:《聊天软件模拟器实测:在电脑上多开安全吗》。
评论
还没有评论,来说两句吧。
评论功能已关闭。