 豆包输入法
聊天机器人安全吗?Risks of Bots Inside a Private Chat
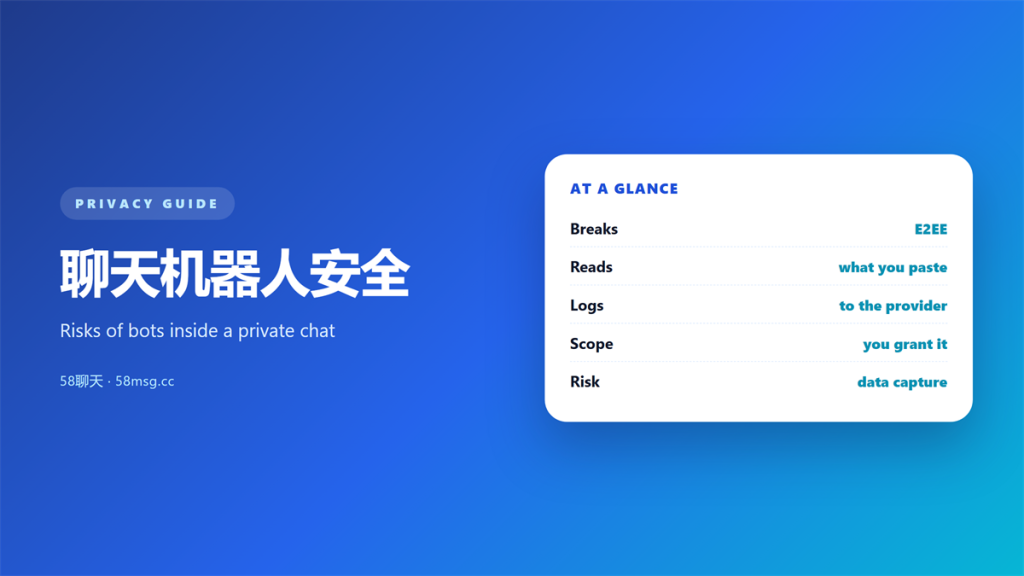
Key Takeaways
- 聊天机器人安全 is a shared responsibility between the user and whoever built the bot.
- A bot sits inside the conversation, so it reads plaintext before any encryption applies.
- Permissions decide whether a bot can read history or only the current thread.
- Every message you paste into a helper becomes part of someone else’s log.
- The safest bots run locally, or with the smallest useful set of permissions.
How 聊天机器人安全 changes a private chat
I added the same assistant bot to three chat clients this year, and the 聊天机器人安全 profile differed in each one. The bot lived inside the thread. It saw every message the moment it arrived.
That placement is the whole issue. End-to-end encryption protects a message between two people. A bot is a third participant, so the guarantee changes shape.
Not every bot is a server. Some run on your own device and never send data out. Others are thin clients that forward everything to a remote service. That single difference decides where your plaintext ends up.
What a bot can read and log
The answer depends on permissions rather than on encryption. I check three things before I trust any integration, and the differences between them are large.
| Capability | What it allows | Risk level |
|---|---|---|
| Read current thread | Sees new replies | Moderate |
| Read history | Sees old messages | High |
| Send messages | Posts as the bot | Moderate |
| Access files | Reads shared media | High |
Bot permissions
Permissions are the real control surface. A summariser that only needs the current conversation should not hold history access. Furthermore, a bot that can send messages can also impersonate a help desk. Therefore, I grant the smallest set that still makes the tool useful, and I review it again after every update.
Third-party bridges
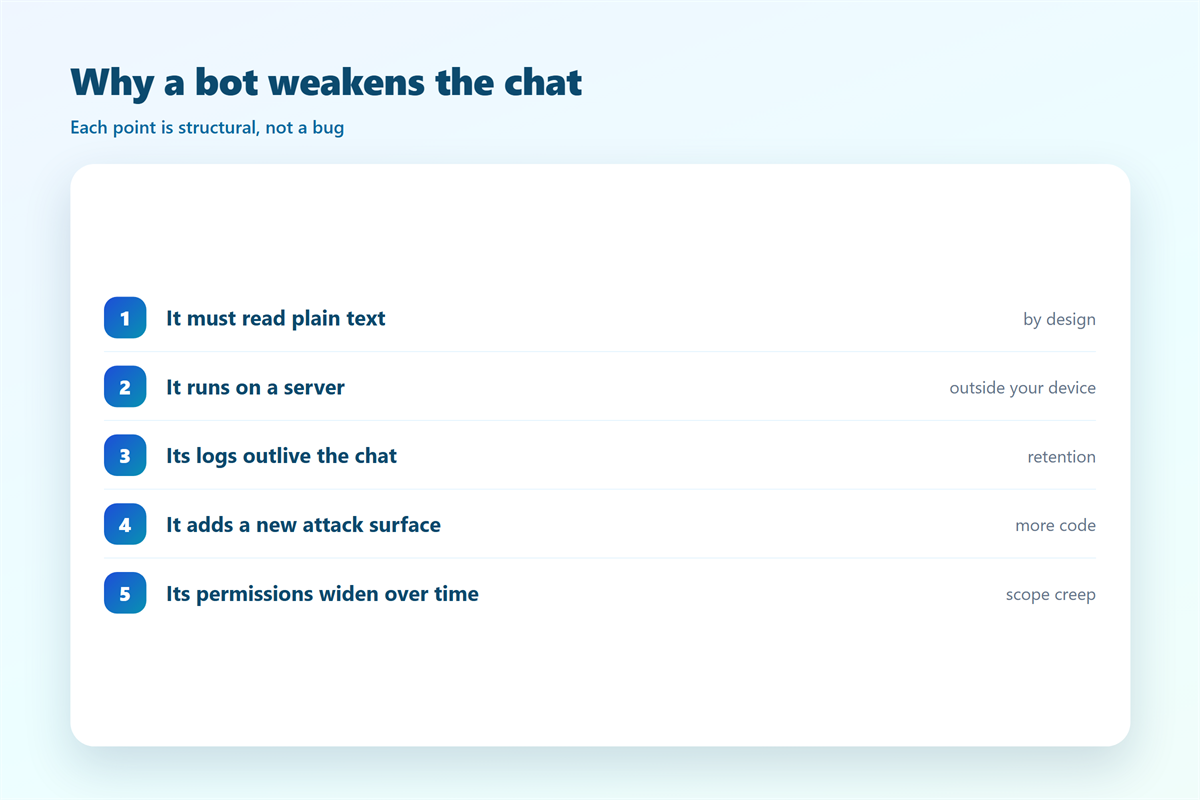
Many bots are bridges to another service. They decrypt on one side and re-encrypt on the other, which means plaintext exists in the middle for a moment. Consequently, the end-to-end path quietly ends at the bridge, and 聊天机器人安全 becomes the bridge operator’s problem.
Why 聊天机器人安全 matters inside encrypted chats
Encryption creates a feeling of safety, and a bot can quietly puncture it. That gap is why the topic belongs beside general chat privacy rather than outside it. Users rarely notice the change, because the interface looks exactly the same.
Consider a translation helper. It reads your private message and returns a converted version, and in most designs the original text passes through a server. Therefore, 聊天机器人安全 often matters more than the cipher protecting the thread.
Malicious integrations are the sharp edge. A bot that reads history can be turned against users, and the pattern resembles classic 聊天钓鱼攻击 in disguise.
The trust model also breaks a common assumption. Many people believe encryption covers every participant, and our review of 端到端加密误区 explains why that belief fails once a bot joins.
Five checks for 聊天机器人安全 before you add a bot
聊天机器人安全 improves quickly once you ask a few blunt questions. I run these checks before I approve any integration.
- Confirm whether the bot runs locally or on a remote server.
- List the permissions it requests and reject the unused ones.
- Check who operates it and where their servers sit.
- Test it in a throwaway chat with dummy text first.
- Review what the bot is allowed to remember.
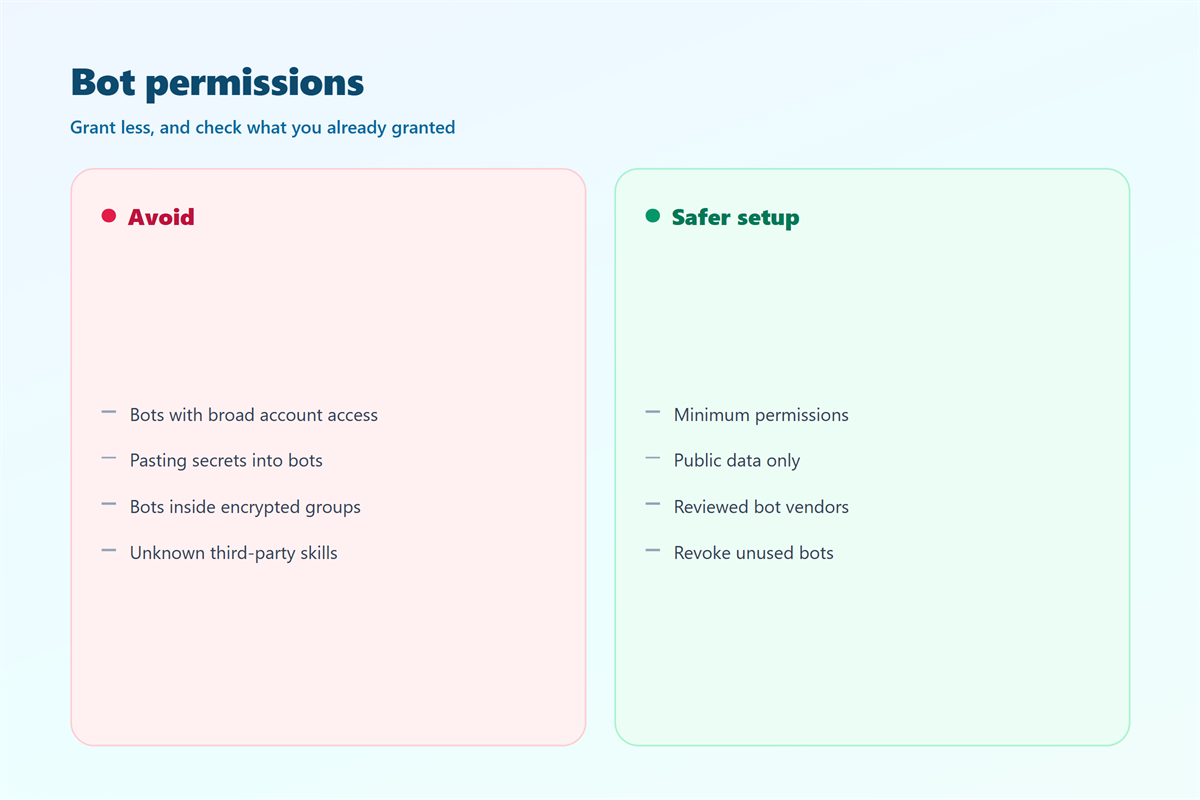
That first check is the most revealing. A local tool keeps your words on the device, while a hosted bot cannot promise the same.
When 聊天机器人安全 goes wrong
聊天机器人安全 fails in quiet ways. A typical case is a helper that stores conversation logs indefinitely, long after the chat itself was cleared.
Another case is over-broad permissions. The bot asked for history access for context, and the feature later shipped with that access still switched on.
A third case is a compromised vendor. The host updates the bot, and the new version starts forwarding data to a third party. Nothing looks different on your screen.
Each failure shares a theme that is easy to overlook. The bot sits inside the trust boundary, yet it answers to a different owner. That mismatch is exactly what a man in the middle exploits, as outlined in 加密聊天中间人攻击.
Protecting a chat that relies on 聊天机器人安全
You rarely need to remove every bot. For 聊天机器人安全, you need to keep the ones you use on a short leash.
Limit what you paste
I treat every bot like a public form. Passwords, recovery codes and personal documents never go in. For 聊天机器人安全, that habit matters more than any feature the tool advertises.
Review installed bots
Old integrations linger for years. I open the bot list monthly and remove anything I cannot explain. A forgotten bot keeps its access even after you stop using it. That habit belongs with the wider audit in 聊天应用权限.
FAQ
Does 聊天机器人安全 break end-to-end encryption?
It can, at least for the messages the bot handles. A bot is another endpoint, so messages are decrypted for it. If the bot is remote, plaintext leaves your device even though the thread was encrypted.
Are local bots safer?
Usually yes, because they process data on your device and skip the round trip. The gain depends on the code being honest and on the app sandboxing it properly.
Can I run a bot without giving it history?
Yes. On most platforms you can grant access to the current thread only, and the bot still works. That single restriction removes a large share of the risk without much inconvenience.
What should I never send to a bot?
Recovery codes, passwords, identity documents and anything you would not post in a group. 聊天机器人安全 depends on assuming the log exists somewhere you cannot see.
References
- Wikipedia: Chatbot
- Wikipedia: Principle of least privilege
- OWASP: Top 10 web application security risks
延伸阅读
延伸阅读:《聊天软件开放接口实测:机器人能拿到多少数据》。
评论
还没有评论,来说两句吧。
评论功能已关闭。