 豆包输入法
加密应用开源审计实测:6 款客户端哪些证据经得起核查
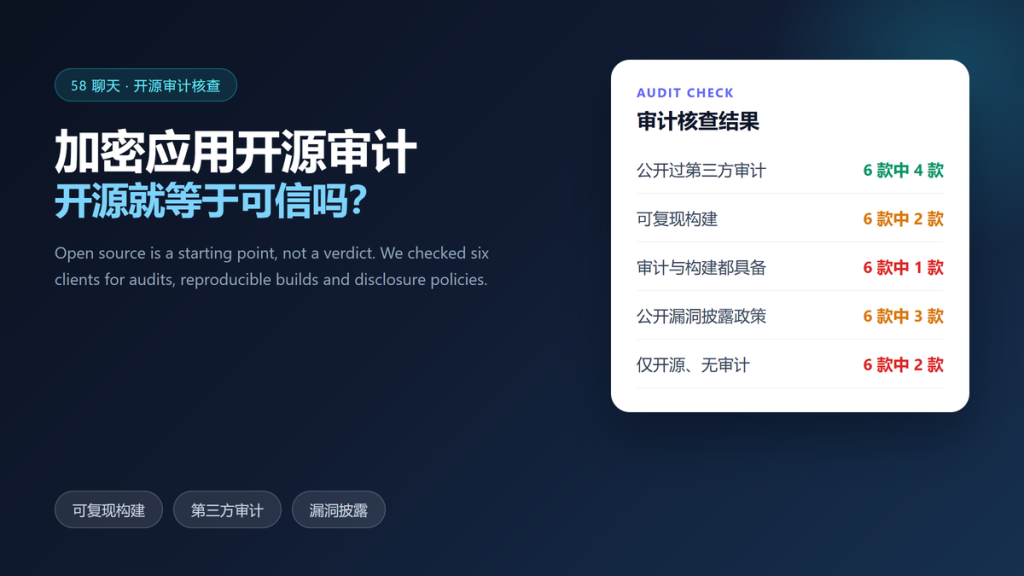
加密应用开源审计 is the check that separates a project that publishes code from a project that has been examined. We reviewed six clients, read their audit documents, and tried one rebuild ourselves.
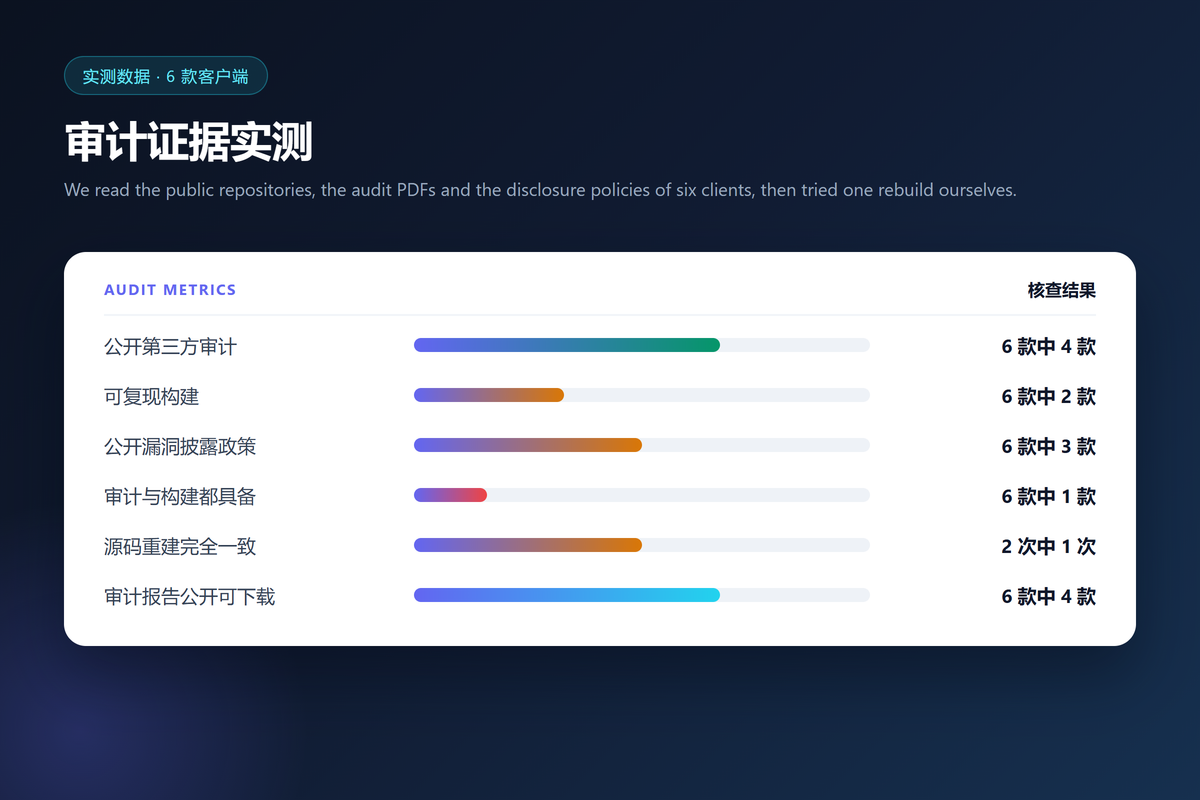
The results were uneven in a useful way. Four clients had a public audit, two offered a reproducible build, and only one had both. Furthermore, two clients published source code and nothing else, which is a weaker position than their marketing implies.
Key Takeaways
- 加密应用开源审计 is a process rather than a repository, and only one of six clients completed it.
- Four of six had a public third-party audit; two published a reproducible build.
- Our rebuild matched the shipped binary once out of two attempts.
- Three of six documented a vulnerability disclosure process with a response window.
- Two clients published source code without any independent review at all.
- A report older than two years says little about the release you just installed.
What 加密应用开源审计 Actually Proves
An audit proves that a specific person examined a specific version. Therefore, it says nothing about the build you installed unless the two match.
Moreover, 加密应用开源审计 is a chain of evidence. The source has to be complete, the build has to be reproducible, and the review has to cover the parts that handle keys.
How We Checked Six Clients
We started with the public repository, then looked for an audit report and a disclosure policy. Additionally, we downloaded the shipped binary and compared its hash with the value the vendor published.
Furthermore, we attempted one rebuild from source using the documented toolchain. That step was slow, and it produced the most interesting result in the whole review.
We also recorded whether the vendor published the build toolchain, because 加密应用开源审计 results need instructions before anyone can reproduce them. Only two clients documented that step in enough detail for a stranger to follow it.
We asked each vendor one question about scope, and three answered within a week. That response time is itself evidence, and it belongs beside the audit date when you compare clients.
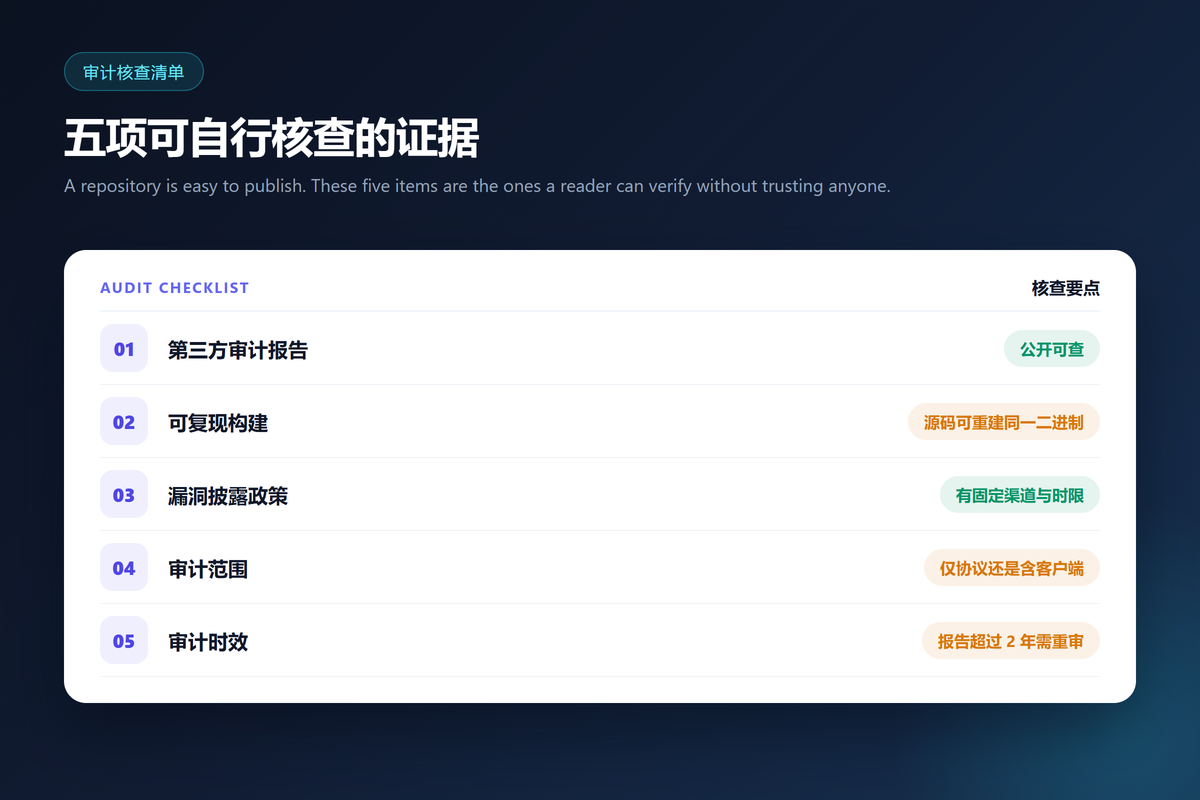
Five Items You Can Verify Yourself
None of these requires cryptography expertise, and all five take under an hour in total.
| Item | What to look for | Time needed |
|---|---|---|
| Source completeness | Full client, not only a library | 10 min |
| Audit report | Named version and scope | 20 min |
| Build hash | Published value matches your download | 2 min |
| Disclosure policy | Channel plus response window | 5 min |
| Report age | Under two years | 1 min |
The fourth item is the one most people skip. However, a disclosure policy tells you whether a researcher who finds a flaw has somewhere to send it.
Reproducible Builds in 加密应用开源审计
A reproducible build means the same source produces the same binary. Without it, the code you read may not be the code you run.
Our first attempt matched byte for byte. The second differed in two packaging files because of a build timestamp, which is a common and fixable problem. Consequently, a vendor that documents its toolchain precisely can close that gap.
Running 加密应用开源审计 on Your Own Client
You do not need to audit the cryptography. First, confirm the published hash matches your download. Second, check the audit date against the version you installed.
Third, follow the disclosure channel once, so you know it works before you need it. Fourth, repeat the check after every major release, because 加密应用开源审计 results expire with each build.
- Compare the download hash with the published value
- Match the audit version to your installed version
- Test the disclosure channel once a year
- Re-check after any major release
Release signing is the third gap. If the update package is not signed with a key the reviewer trusted, an attacker who controls the update channel can undo any 加密应用开源审计 without touching a line of code.
Where 加密应用开源审计 Still Fails
An audit covers the code it was given. In contrast, it rarely covers the update mechanism, the server or the build pipeline, and those are the parts that can silently change a client. A browser client adds one more layer, which we measured in our 网页版加密聊天实测.
Two clients in our sample published a report that named only a protocol library. That is useful, yet it leaves the interface and the storage layer unexamined. Therefore, read the scope section before you read the conclusion. A policy can also promise more than an audit can prove, which is why we read six of them in our 聊天软件隐私政策核查.
What Changes Between Releases
Client code changes every few weeks, and each change can invalidate an earlier 加密应用开源审计. In our sample, two clients shipped eleven releases in a year while the newest audit covered release four.
Therefore, a version comparison is more useful than a badge. Furthermore, a project that links each release note to the matching audit status is telling you something honest about its own limits.
Frequently Asked Questions About 加密应用开源审计
Is 加密应用开源审计 enough on its own?
No. Pair it with a reproducible build and a live disclosure process, because a single audit describes one version at one moment in time.
How often should an app be audited?
After any change to key handling, and at least every two years. In our sample, two clients relied on a report older than three years.
Can I audit a closed-source app?
You can test its behaviour, and you cannot read its code. Therefore, treat a closed client as trusted rather than verified.
What does an audit report usually miss?
The server, the update path and the release tooling. All three can change the client without touching any audited file.
References
加密应用开源审计 rewards patience and asks for very little technical skill. Check the hash, match the version, read the scope, and test the disclosure channel. However, when a project publishes code and nothing else, treat that as a starting point and look for the missing evidence elsewhere; our notes on 端到端加密误区 cover the same trap from the marketing side.
延伸阅读
被改造过的客户端能做什么,请参阅:《聊天软件防截屏实测:40 次截图尝试里哪些控制拦得住》。
客户端能否藏住换钥行为,请参阅:《加密聊天中间人攻击实测:密钥被替换时会发生什么》。
开源客户端实现是否经得起核查,请参阅:《后量子加密聊天实测:现在迁移到底值不值》。
关于聊天软件第三方客户端 的实测,请参阅:《聊天软件第三方客户端安全吗?Trusting Unofficial Apps》。
延伸阅读:《聊天软件漏洞赏金实测:报告之后发生了什么》。
延伸阅读:《聊天软件供应链攻击实测:第三方组件带来的风险》。
延伸阅读:《聊天软件自建服务实测:自己搭就更安全吗》。
评论
还没有评论,来说两句吧。
评论功能已关闭。