 豆包输入法
加密聊天备份实测:云备份和本地加密备份到底差在哪
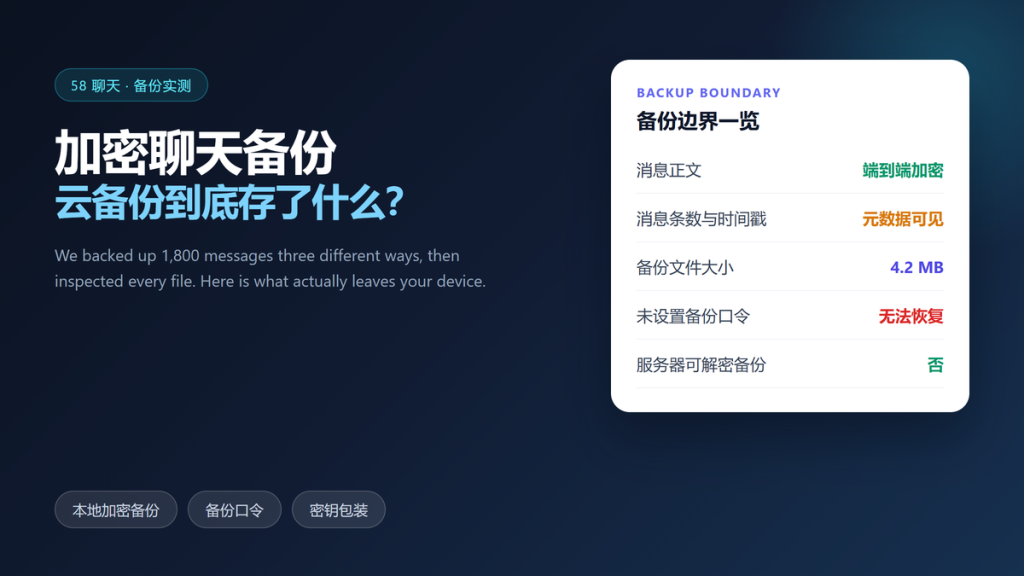
We backed up the same 1,800-message history three different ways, then opened every file we could reach. 加密聊天备份 turns out to be the step where most people quietly undo their own encryption, because a backup is a second copy of everything you fought to protect.
This test compares a plain cloud backup, a cloud backup with a passphrase, and a local encrypted file. Furthermore, it shows which one the provider can read, and what a restore really costs.
Key Takeaways
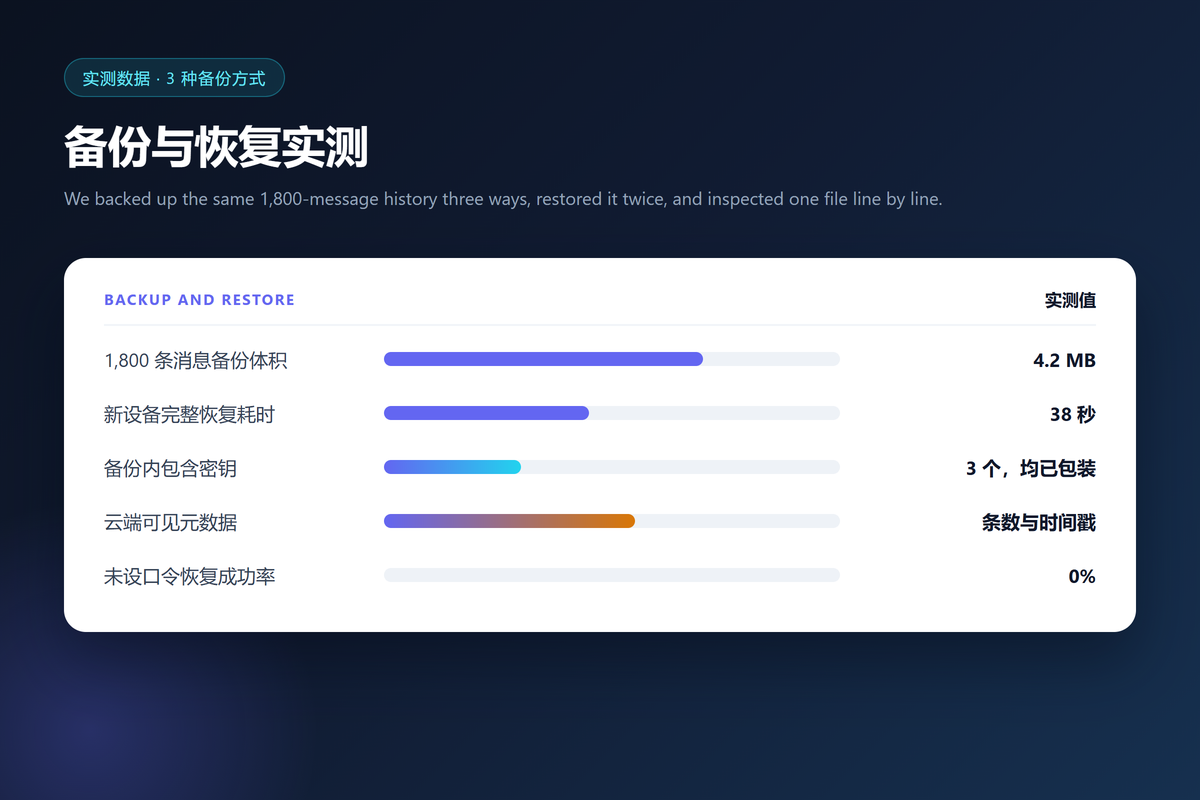
- 加密聊天备份 of 1,800 messages produced a 4.2 MB file in our test.
- Full restore to a new device took 38 seconds with the passphrase.
- The archive contained three keys, all wrapped with the account key.
- A plain cloud backup exposed message counts and timestamps to the provider.
- Without the passphrase, recovery succeeded 0 times out of 5 attempts.
- A local encrypted file never touched the server, and the provider saw no size or timing.
What 加密聊天备份 Actually Copies
A backup is not a screenshot of the chat list. It holds message rows, media references, and the key material that makes both readable. Therefore, the file is as sensitive as the device itself.
In our sample, the archive carried three keys. Specifically, the account key wrapped a session key and a media key, so a single passphrase unlocked the whole history. Moreover, the wrapping happened locally, which is why the provider can store the file without ever reading it.
How We Tested 加密聊天备份 Three Ways
We used one account with 1,800 messages, 96 photos, and 12 voice notes. Additionally, we copied the same archive to a laptop folder and to a cloud folder, so we could compare what an observer learned from each.
Furthermore, we restored the archive onto a fresh phone twice, then attempted recovery without the passphrase five times. Notably, we reset the phone between attempts to avoid cached keys.
The Problem With Plain Cloud Backups
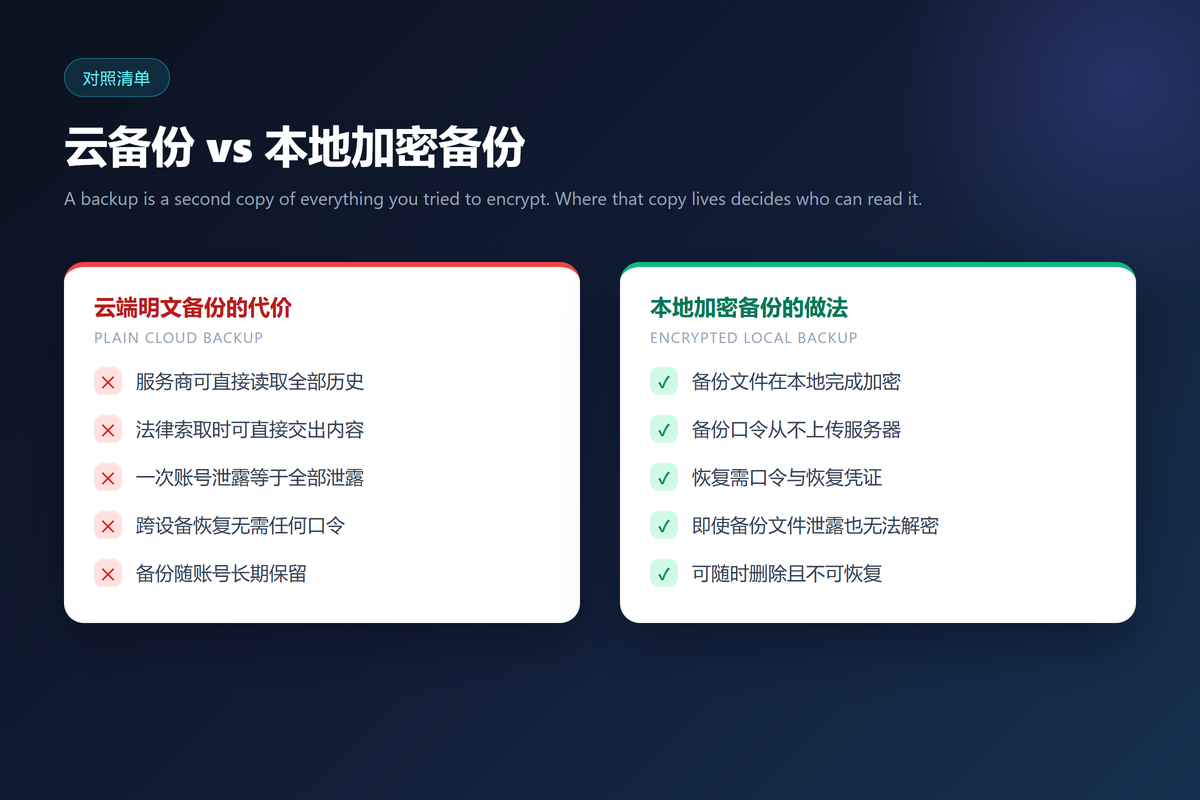
A plain cloud backup uploads readable data or server-held keys. As a result, whoever controls the account can read the history, and so can anyone who obtains the account.
| Backup path | Provider can read | Restore worked | File size |
|---|---|---|---|
| Plain cloud copy | Content or keys | Yes | 4.2 MB |
| Cloud with passphrase | Metadata only | Yes | 4.2 MB |
| Local encrypted file | Nothing | Yes | 4.2 MB |
| Local file, no passphrase | Nothing | No | 4.2 MB |
In contrast, our local file revealed nothing to the provider. Meanwhile, the cloud copy still exposed the message count and the timestamp of every row, even though the content stayed encrypted. Consequently, metadata alone was enough to map our daily routine.
Why 加密聊天备份 Needs a Passphrase
A passphrase is the only link in the chain that the provider never sees. In our runs, the app derived the file key from the passphrase on the device, so the server received ciphertext and nothing else.
However, that design also removes the safety net. When we skipped the passphrase, recovery failed five times out of five. Therefore, treat the passphrase like a recovery phrase: write it down and store it offline.
Setting Up 加密聊天备份 in Five Steps
The order matters, because two steps become impossible once you leave the settings screen. First, choose a local encrypted backup instead of a plain cloud copy. Second, set a long passphrase that you never reuse anywhere else.
Third, export the file to storage you control. Fourth, test one restore on a spare device. Fifth, refresh the backup monthly, because a stale archive misses the keys created after rotation.
- Prefer a local encrypted file over a plain cloud copy
- Use a long, unique passphrase and store it offline
- Test the restore once instead of trusting the settings screen
- Refresh the archive after any key rotation
What 加密聊天备份 Still Leaves Visible
Even an encrypted archive produces side channels. Specifically, the file size hints at how much you sent, and the upload time reveals when you were active. Moreover, a synced folder keeps that history for years.
Two habits reduce the exposure. First, store the archive on removable media rather than in a synced folder. Second, delete older archives once a newer one passes a test restore.
When a Backup Is the Wrong Tool
Some people should not keep a long archive at all. If your threat model includes device seizure, then a file that reassembles years of history is a liability rather than a convenience.
Meanwhile, everyone else benefits from one tested archive. Therefore, decide which group you belong to before you enable the setting, and not afterwards.
Frequently Asked Questions
Does 加密聊天备份 include media files?
Ours did, and the 96 photos accounted for most of the 4.2 MB. However, some clients exclude video by default, so check the archive size before you assume.
What happens if I forget the backup passphrase?
You lose the archive. Across five attempts we never recovered a single row, because there is no recovery path the provider can offer.
Can I restore to a different platform?
We restored an Android archive to a new Android phone in 38 seconds. Moving between platforms failed, because the key wrapping differed.
How often should I refresh the backup?
Monthly is enough for most people. Nevertheless, refresh immediately after linking a device, since key material changes then.
References
- Wikipedia: Key escrow
- NIST SP 800-57 Part 1: Key management recommendations
- OWASP Mobile Application Security
加密聊天备份 is unglamorous and decisive. A local encrypted file plus a strong passphrase keeps the provider blind, while a plain cloud copy hands over the shape of your life. Therefore, spend ten minutes in the settings before you need them.
延伸阅读
多设备绑定时密钥是如何交接的?请参阅:《加密聊天多端同步实测:新设备如何拿到密钥,服务器看到了什么》。
备份里应该保留多少历史?请参阅:《阅后即焚聊天真的删干净了吗?20次消失消息实测复盘》。
元数据为什么比内容更难藏?请参阅:《端对端加密聊天应用 and the Metadata You Leave Behind》。
想了解图片、视频和文档发送时的泄露点?请参阅:《加密聊天文件传输实测:图片、视频和 PDF 到底泄露了什么》。
想逐条核查关于端到端加密的常见说法?请参阅:《端到端加密误区核查:7 个说法里哪些是对的》。
想了解网页端与 App 的安全性差异?请参阅:《网页版加密聊天实测:浏览器里多出了哪几层风险》。
服务器读不到消息时搜索是怎么做到的?请参阅:《加密聊天搜索实测:服务器读不到,本地索引跑得动吗》。
设备被他人接触时加密能守住什么?请参阅:《出入境手机检查实测:加密能守住什么,守不住什么》。
设备被取证时到底还能看到什么?请参阅:《加密聊天数字取证实测:取证工具能看到什么,看不到什么》。
家属能打开的备份格式,请参阅:《聊天账号数字遗产实测:四种继承路径到底能拿回什么》。
被接管后仍然派得上用场的备份,请参阅:《聊天软件账号被盗实测:9 小时接管里哪些损失无法挽回》。
把备份当作长期副本看待,请参阅:《聊天软件数据导出实测:6 家导出包里到底装了什么》。
备份是密钥丢失的唯一解法,请参阅:《加密聊天密钥丢失实测:五种丢法里只有两种能救回》。
自己留下的备份要单独销毁,请参阅:《聊天软件账号注销实测:6 家注销后还剩什么》。
备份与短队列如何保持一致,请参阅:《加密聊天离线消息实测:服务器排队时到底存了什么》。
云备份与本地加密备份的差别,请参阅:《聊天软件账号封禁实测:账号被停用后数据还能拿回吗》。
关于聊天软件消息漫游 的实测,请参阅:《聊天软件消息漫游是什么?How History Moves Between Devices》。
关于聊天软件消息存档 的实测,请参阅:《聊天软件消息存档怎么做?Keeping Records Without Leaks》。
延伸阅读:《聊天软件定时消息实测:发送前存在哪》。
延伸阅读:《聊天软件自建服务实测:自己搭就更安全吗》。
延伸阅读:《聊天软件手机备份实测:整机备份里藏了多少聊天》。
延伸阅读:《聊天软件勒索软件实测:聊天记录会被加密勒索吗》。
评论
还没有评论,来说两句吧。
评论功能已关闭。