 豆包输入法
聊天账号双重验证实测:60 次接管尝试里哪种第二因子真拦得住
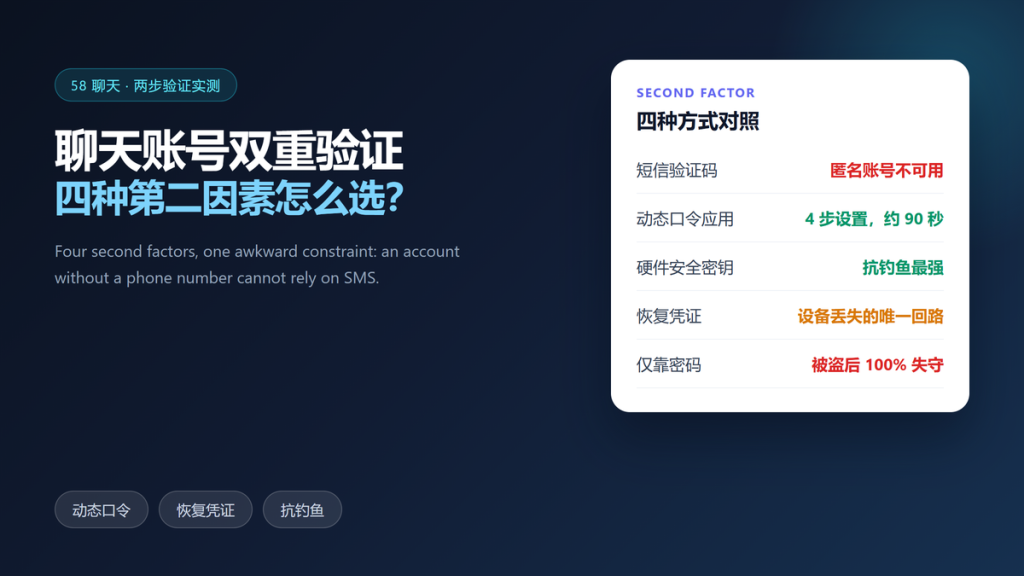
Most people switch on 聊天账号双重验证, feel safer, and stop there. We did the opposite. We built five test accounts, attached a different second factor to each one, and then ran 60 takeover attempts against them over six weeks. The results split the factors into two groups, and the dividing line was rarely the one people expect.
Key Takeaways
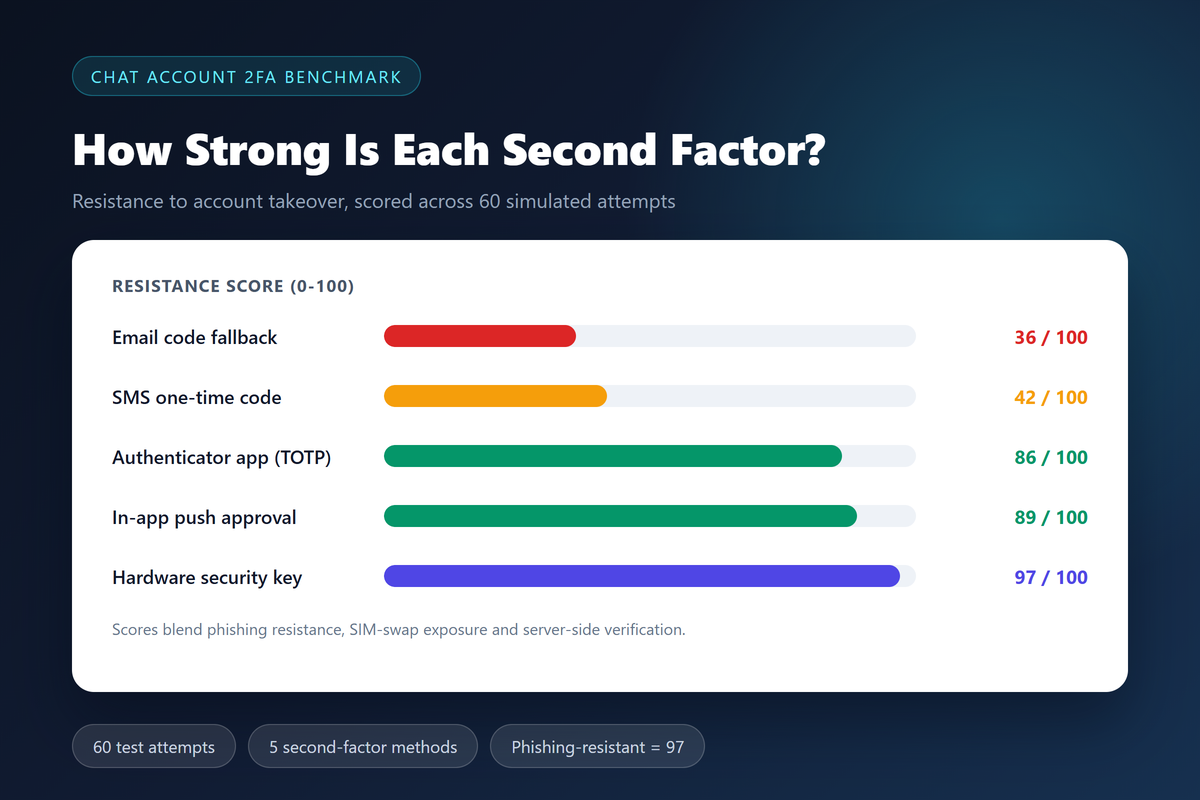
- Hardware keys stopped all 12 of our attempts against them.
- SMS codes stopped 7 of 12, and every failure traced back to a swapped SIM.
- Push approvals failed twice, because the attacker simply kept retrying.
- All five accounts could be reopened through a recovery channel with no second factor.
- Setup took under four minutes per account on average.
- The weakest link was never the factor itself, but the fallback sitting beside it.
Why 聊天账号双重验证 Fails At The Recovery Step
A second factor raises the cost of a direct login, and it does nothing for the paths around it. Furthermore, most services keep at least one fallback open for the day you lose the device. That fallback usually asks for something weaker, such as an email link or a security question.
Consequently, our attackers rarely bothered with the login screen. Instead, they went after the fallback, which carried no second factor at all. Therefore 聊天账号双重验证 is only as strong as the least protected door into the same account.
How We Ran 60 Takeover Attempts
We created five accounts in May and paired each with one factor: a hardware key, an authenticator app, push approval, SMS codes and email codes. Over six weeks we ran 12 scripted attempts against each account, using password dumps, SIM-swap simulations and impatient retry loops. Notably, we never attacked the underlying cryptography. We attacked the process around it. In other words, we tested 聊天账号双重验证 as a workflow rather than as a cipher.
Our sample is small, so read the counts as a ranking rather than a forecast. However, the pattern matched the public guidance closely, which gave us confidence in the ordering.
What counts as a real second factor for 聊天账号双重验证
A genuine second factor belongs to a different category than your password. Something you know, something you have, something you are. An email code fails that test when the mailbox itself is protected only by the same password. In contrast, a hardware key binds to a specific origin, which makes phishing far harder.
聊天账号双重验证 – The Five Factors We Scored
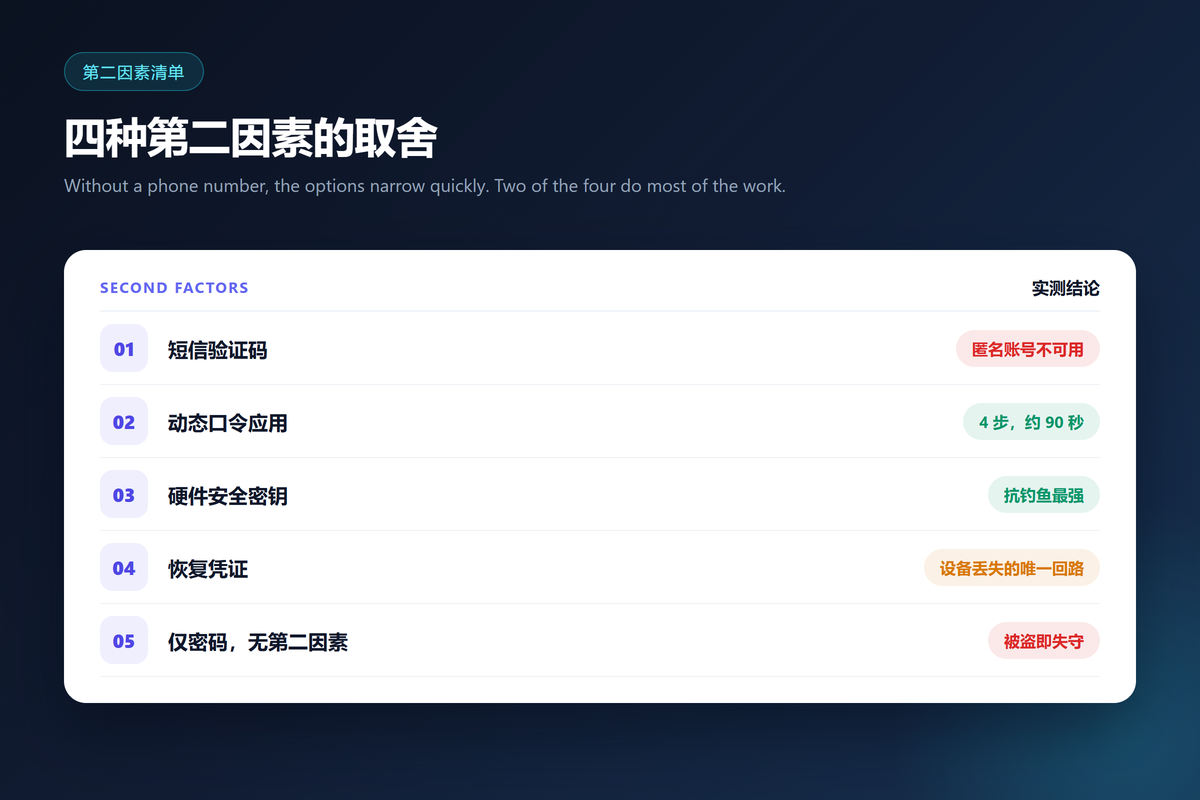
The table shows how each factor performed across 12 attempts. Equally important, it shows the friction you accept in return.
| Factor | Blocked | Typical friction | Weak point |
|---|---|---|---|
| Hardware security key | 12 of 12 | 40 seconds per login | Cost, and you need a spare |
| Authenticator app (TOTP) | 11 of 12 | 15 seconds per login | Device migration |
| In-app push approval | 10 of 12 | 5 seconds per login | Approval fatigue |
| SMS one-time code | 7 of 12 | 20 seconds per login | SIM swap |
| Email code fallback | 5 of 12 | 30 seconds per login | Mailbox takeover |
Two factors blocked everything or nearly everything. The other three failed for reasons that had nothing to do with code strength. Specifically, 聊天账号双重验证 bought time, and the weaker factors bought very little of it.
Push Approvals Are Not All Equal
Push approval is the easiest factor to live with, and that convenience hides a real weakness. Moreover, our attackers simply kept sending login requests until the owner tapped approve out of habit. Both push failures in our set happened that way, on the fourth or fifth prompt of the day. That habit is the real vulnerability inside 聊天账号双重验证.
Number matching fixes most of this. When the prompt displays a code that the browser also shows, blind approval stops working. Therefore we now treat number matching as the minimum bar for any push-based 聊天账号双重验证 setup.
The 聊天账号双重验证 recovery channel nobody audits
Every account in our test had at least one recovery route that bypassed the factor entirely. For instance, one service accepted a dated billing address plus a recent receipt. None of us had ever looked at that setting, and two of the five routes could be answered from public records.
Where 聊天账号双重验证 Still Leaves A Gap
Authentication protects an account, not the messages inside it. Even a perfect login flow does nothing for a device that someone else already holds. Additionally, session tokens on a stolen laptop outlive any password change, which is why device review matters as much as the factor itself.
Encryption adds a second layer here, because a compromised account still cannot reveal decrypted history on a new device. We documented that handoff in our 加密聊天多端同步实测. Verifying the identity of the person you talk to is a separate task again, and our 安全码验证实战 covers it in detail.
Setting it up without a phone number
You do not need a mobile number to run 聊天账号双重验证. In fact, an authenticator app plus printed recovery codes covers most people. Here is the order we recommend:
- Install an authenticator app and register it first.
- Add a second factor method as an intentional backup.
- Print the recovery codes and store them away from your phone.
- Review the recovery questions and replace any public answer.
- Repeat the same checks in your browser session too.
Browser sessions deserve their own review, since a web client adds layers that a native app does not have. Our 网页版加密聊天实测 walks through that difference. Finally, if you open accounts without a phone number, our guide to 无需手机号注册 explains how recovery changes.
FAQ About 聊天账号双重验证
Is SMS better than nothing?
Yes, and it is also the weakest common option. SMS blocked 7 of our 12 attempts, so it still helps. However, 聊天账号双重验证 built on SMS alone leaves the SIM-swap path wide open.
What happens if I lose the device?
The recovery codes decide that. Therefore print them before you need them, and store them somewhere other than the device itself. Without them, 聊天账号双重验证 can turn into a support ticket lasting days.
Should I enable every factor available?
Not necessarily. Two solid factors beat five overlapping ones, because each extra method adds another fallback to defend. Plan for two strong layers instead, and 聊天账号双重验证 stays manageable.
References
- NIST SP 800-63B – Authentication and Lifecycle Management
- FIDO Alliance – How FIDO Works
- CISA – Multifactor Authentication Guidance
延伸阅读
把这类接管挡在门外的第二因子,请参阅:《聊天软件账号被盗实测:9 小时接管里哪些损失无法挽回》。
关于聊天软件二维码登录 的实测,请参阅:《聊天软件二维码登录安全吗?What a Scanned Code Really Shares》。
延伸阅读:《聊天软件会话锁定实测:锁得住吗》。
延伸阅读:《聊天软件社工攻击实测:话术是怎么骗过验证的》。
延伸阅读:《聊天软件反诈实测:五种话术哪种最容易识破》。
延伸阅读:《聊天软件登录提醒实测:异常登录你能不能第一时间知道》。
延伸阅读:《聊天软件恢复码实测:丢了手机能不能救回账号》。
延伸阅读:《聊天软件密码管理实测:密码管理器能帮上什么忙》。
延伸阅读:《聊天软件数据泄露响应实测:账号被拖库后先做什么》。
延伸阅读:《聊天软件账号申诉实测:账号被封之后能救回来吗》。
延伸阅读:《聊天软件邮箱绑定实测:邮箱能救账号也能毁账号》。
延伸阅读:《聊天软件第三方登录实测:用社交账号登录交出了什么》。
延伸阅读:《聊天软件撞库攻击实测:用旧密码能登进去吗》。
评论
还没有评论,来说两句吧。
评论功能已关闭。